
CVE-2026-48907
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
exploitationpayload-developmentpenetration-testing+6
noname-elv/cve-2026-48907Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
 cyberalp0/smartermail-cve-2026-24423
Exploit for CVE-2026-24423 — a critical unauthenticated RCE in SmarterMail's ConnectToHub API. Affects all builds prior to 9511.
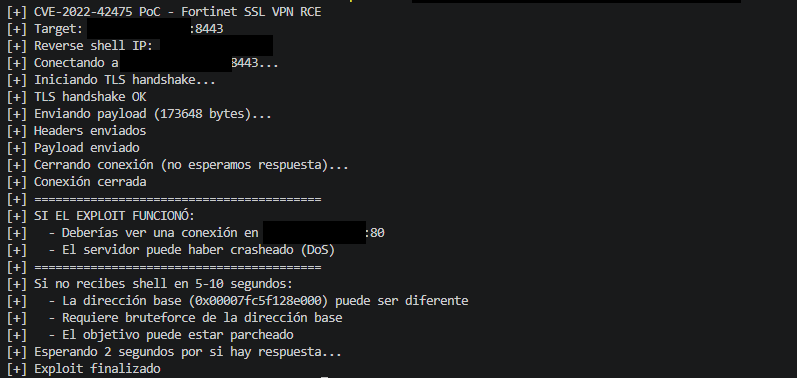 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 gagaltotal/cve-2026-44825-apache-solr-scanner
Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.
 goultarde/cve-2022-42889-text4shell
Proof of Concept (PoC) for CVE-2022-42889 (Text4Shell) targeting Apache Commons Text versions prior to 1.10.0. This script automates Remote Code…
 k3ystr0k3r/cve-2022-0543
PoC for CVE-2022-0543 – Redis Remote Code Execution (RCE)
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 joaoaugustom/ipfire_2.25_rce_authenticated
This exploit is based on CVE-2021-33393 and was built upon the original exploit by Mücahit Saratar, extending it to achieve a reverse shell with root…
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 tryj/cve-2012-1823---php-cgi---rce
Python-based exploit for CVE-2012-1823 enabling remote code execution on vulnerable PHP-CGI servers by injecting command-line arguments via the query…
 r4vl1t0/cve-2019-0232
Exploit based in /jaiguptanick/CVE-2019-0232
 ninjazan420/cve-2025-52691-poc-smartermail-authentication-bypass-exploit-wt-2026-0001
CVE-2025-52691 PoC: Based on watchtowr's article WT-2026-0001 about an authentication bypass exploit, this one is a functional Python attack script.
 abdulrkb/n8n-rce
Proof of Concept (PoC) Script for Remote Code Execution via n8n Workflows (Based on CVE-2025-68613)
 yz9yt/react2shell-ctf
A CTF challenge based on CVE-2025-55182 Vulnerability
 d3ltaformation/cve-2024-28397-js2py-rce
This repository contains a Proof of Concept (PoC) for CVE-2024-28397, a vulnerability in the js2py library allowing a sandbox escape to achieve…
 alm6no5/cve-2025-32756-poc
Proof-of-concept exploit for a critical stack-based buffer overflow in Fortinet products, enabling unauthenticated remote code execution via the…