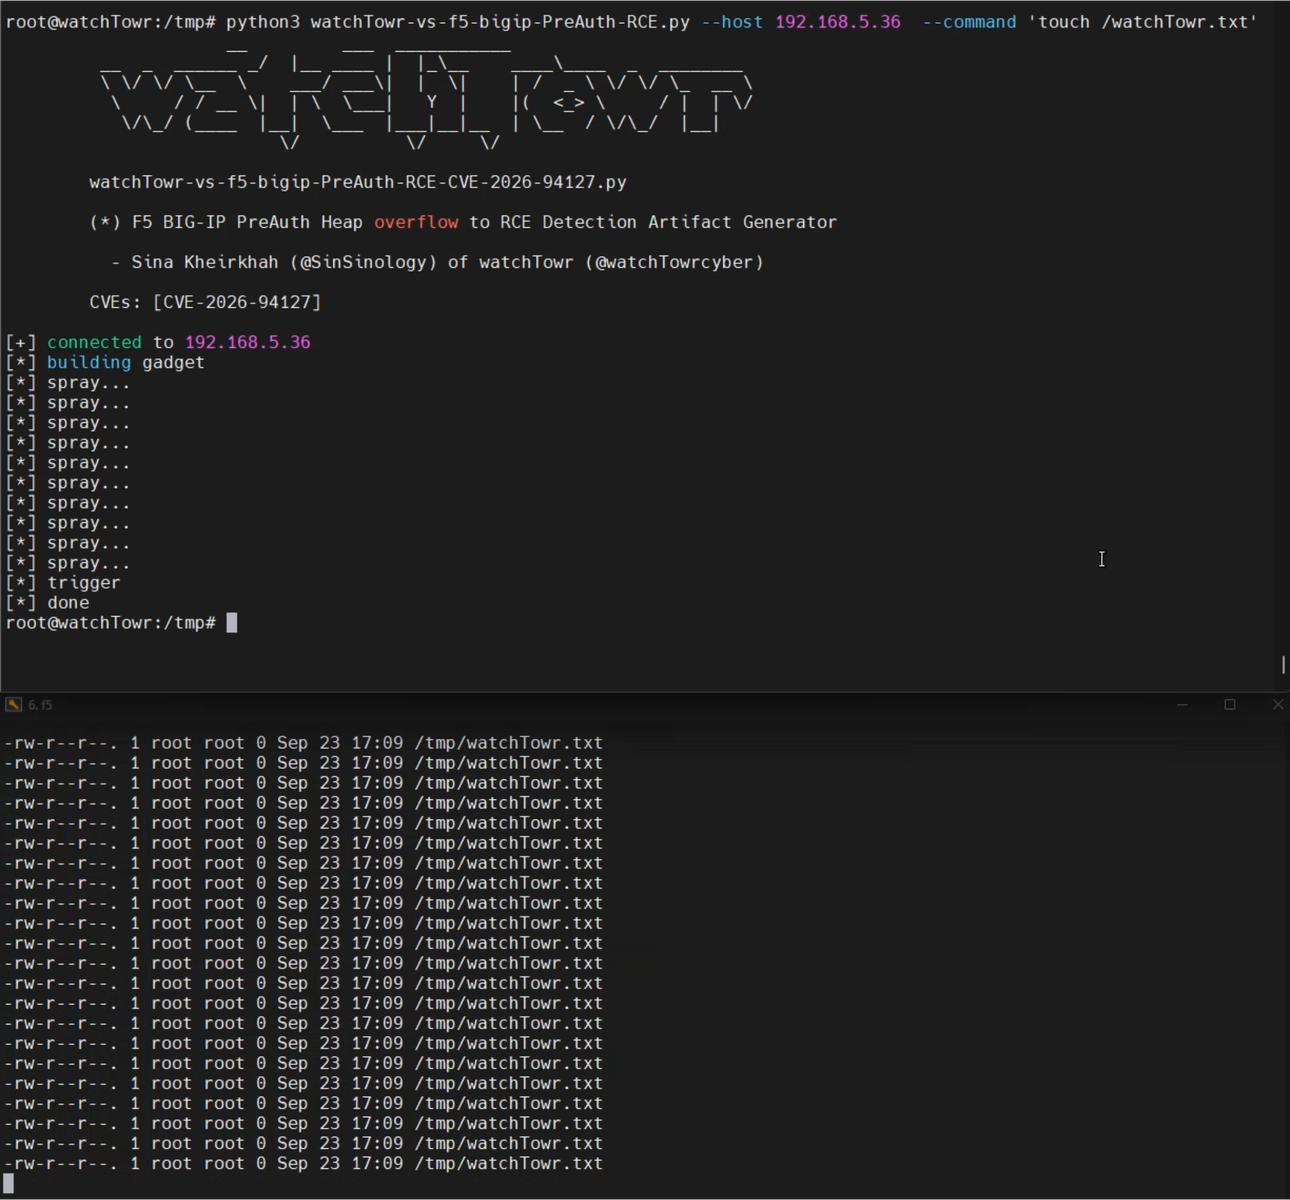
watchTowr-vs-f5-bigip-PreAuth-RCE-CVE-2026-94127

Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…

Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Python PoC for CVE-2026-12793 in JetFormBuilder <= 3.6.2: unauthenticated privilege escalation leading to plugin upload and remote code execution,…

Python PoC exploiting CVE-2025-24813, an Apache Tomcat partial PUT deserialization RCE. Auto-detects vulnerable variants, supports blind command…

Python exploit for CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii2 __class injection, with command execution and reverse shell support.

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…

Marimo exploit prior to 0.23.0. Pre-Auth RCE vulnerability via websocket endpoint : /terminal/ws.

Proof of Concept (PoC) for CVE-2022-42889 (Text4Shell) targeting Apache Commons Text versions prior to 1.10.0. This script automates Remote Code…

OpenSTAManager RCE Exploit (CVE-2026-38751)

CVE-2023-46604-RCE exploit with Linux reverse shell payload

python 2.7

CVE-2025-55182 Exploit Tool – Python 2.7 exploit for Next.js prototype pollution leading to RCE

PoC exploit for CVE-2023-34468 — RCE via H2 RUNSCRIPT in Apache NiFi <= 1.21.0

Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.

Python PoC for unauthenticated remote code execution in Fuel CMS 1.4.1 via the `filter` parameter, providing an interactive shell for command…

CVE-2019–11043: PHP-FPM Nginx Remote Code Execution Vulnerability

Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload (CVE-2026-3891) PoC