
cloudflared
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
api-securitycloud-infrastructure-securitycloud-security+3
15.9k
cloudflare/cloudflaredClient for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 nakagami/grdpwasm
A web-based RDP client
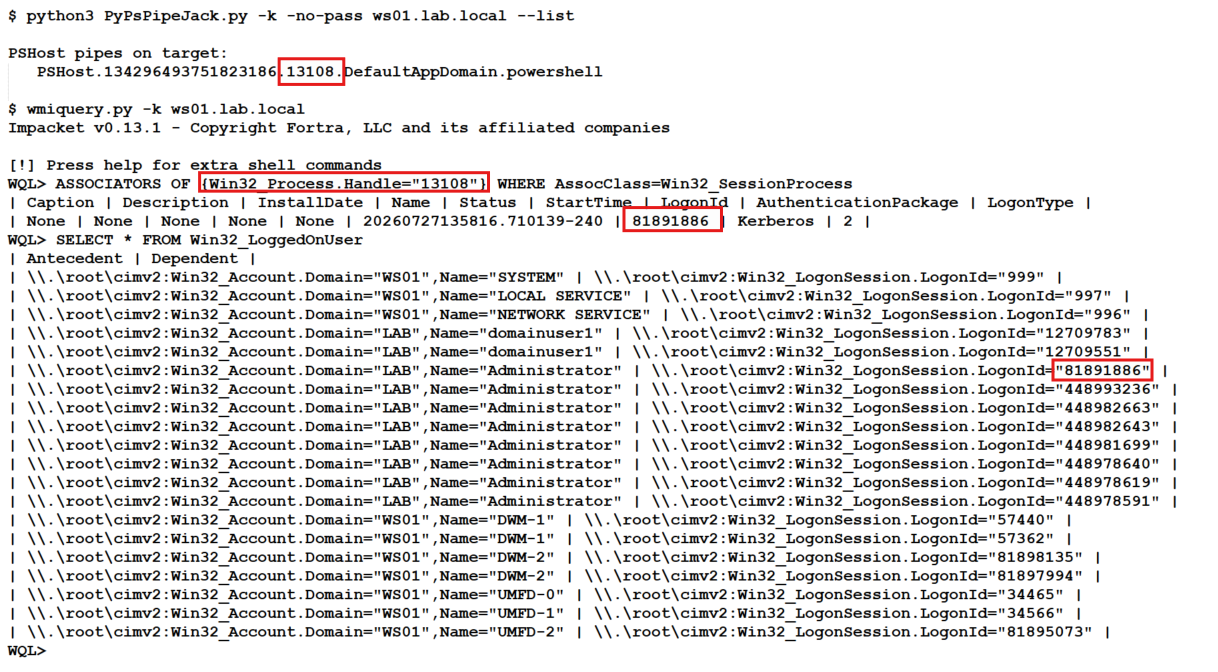 e-fin/pypspipejack
Python implementation of OpenPsPipeJack
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 jackalkarlos/evilahenk
CVE-2026-6508 LiderAhenk Merkezi Yönetim Sistemi mimarisinde, uç birimler (agents) arası tüm istemcilerin birbirleri üzerinde 'root' yetkisiyle kod…
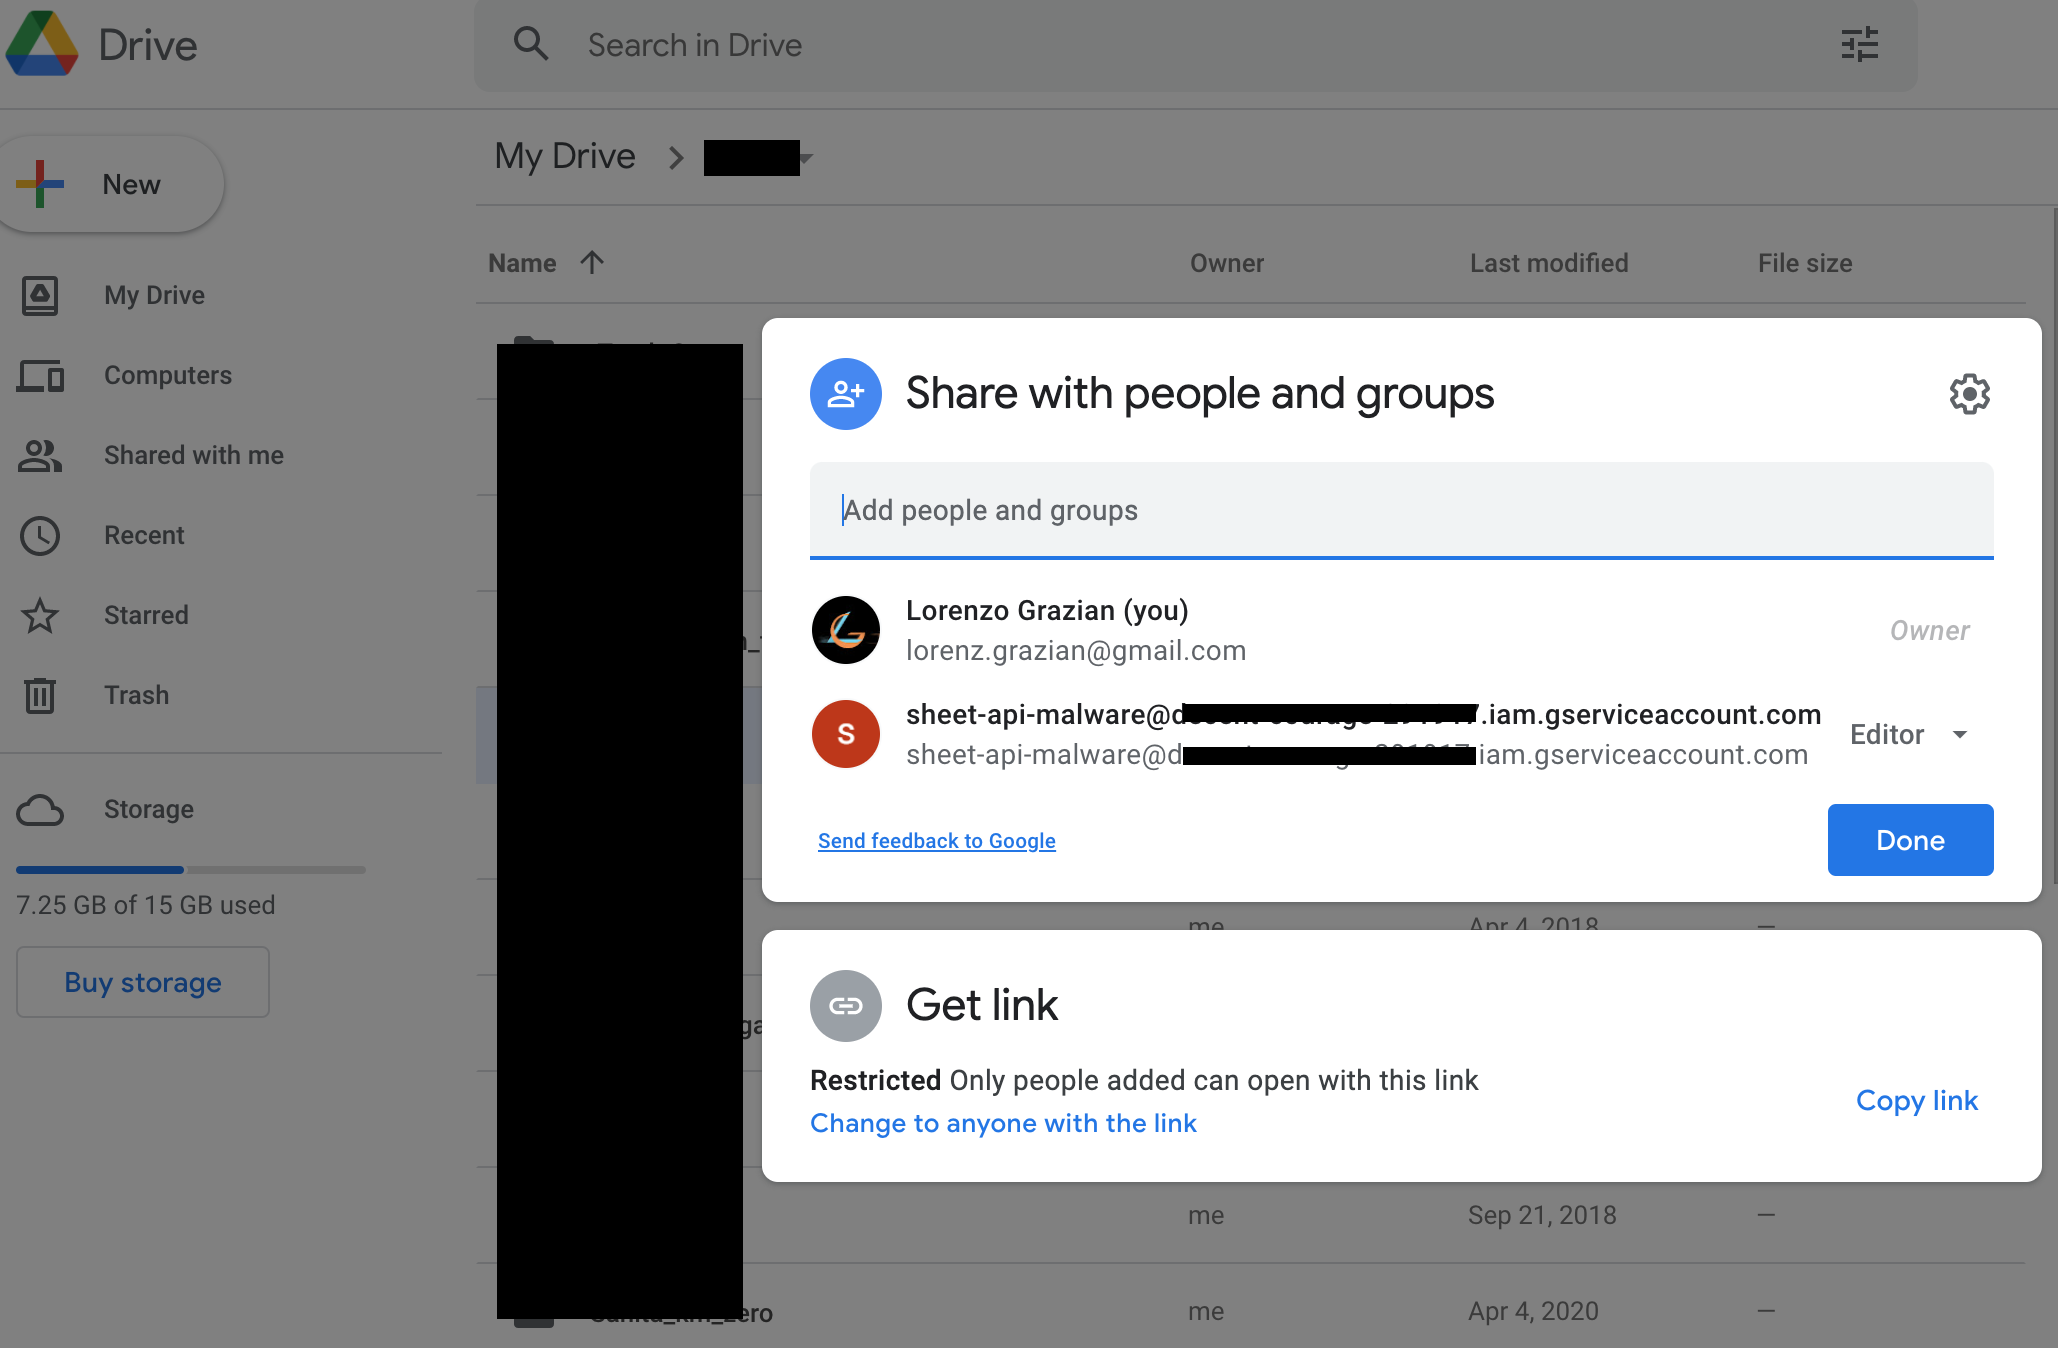 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 hnytgl/cve-2026-41089
CVE-2026-41089 是 Windows Netlogon 服务中一个关键的远程代码执行漏洞,单包即可崩溃 lsass.exe,导致域控制器在约 30-60 秒内重启。此期间该 DC 的所有域认证将失败。
 synacktiv/dcomillusionist
DCOM in memory and fileless lateral movement techniques through .Net deserilization
 aperocky/bepr
A minimal authenticated reverse shell framework for reaching hosts with outbound internet access.
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 johanneslks/cve-2025-14558
FreeBSD rtsold DNSSL Command Injection (RCE)
 fcjaviergarcia/cve-2026-23744-poc
Proof of Concept (PoC) exploit for CVE-2026-23744, a vulnerability affecting MCPJam Inspector that allows remote command execution (RCE) through…
 cypher-21/cve-2026-23520
Proof-of-concept exploit for CVE-2026-23520, a command injection vulnerability in Arcane's updater service, enabling remote code execution via…
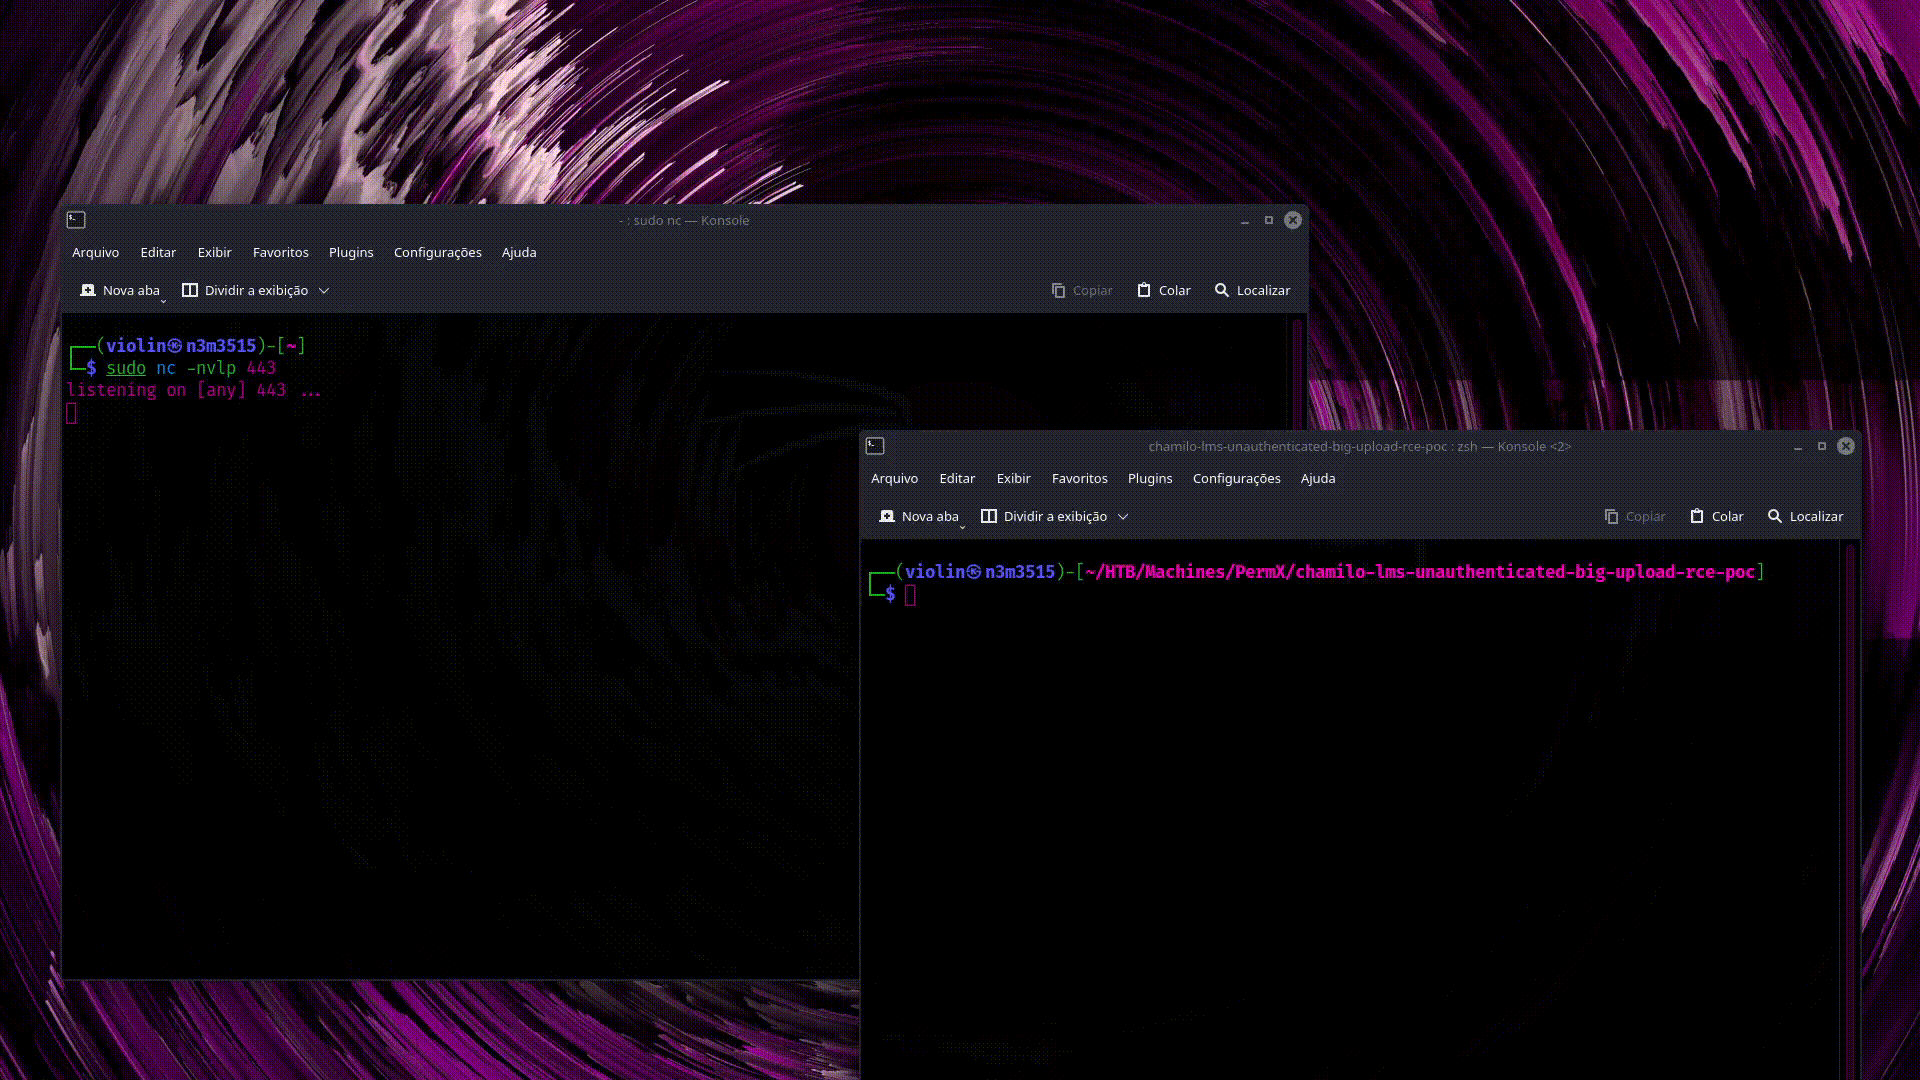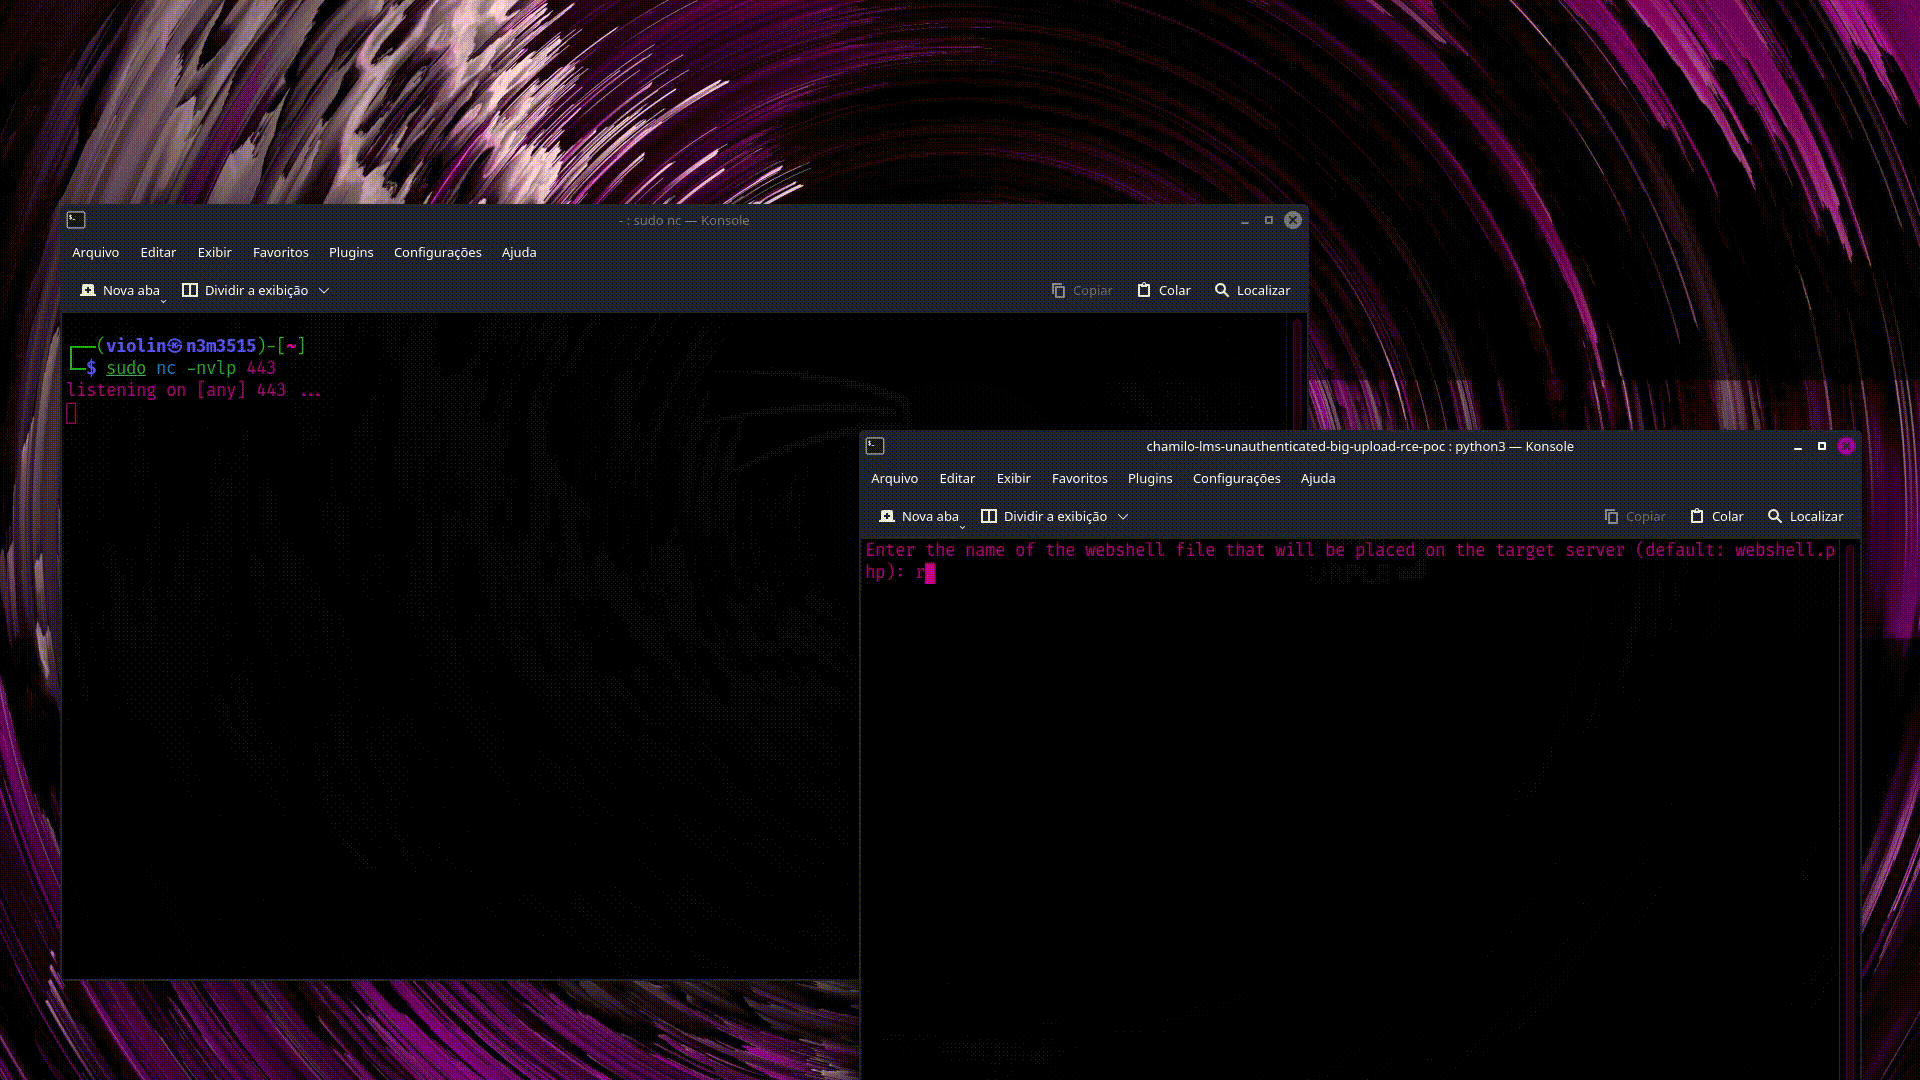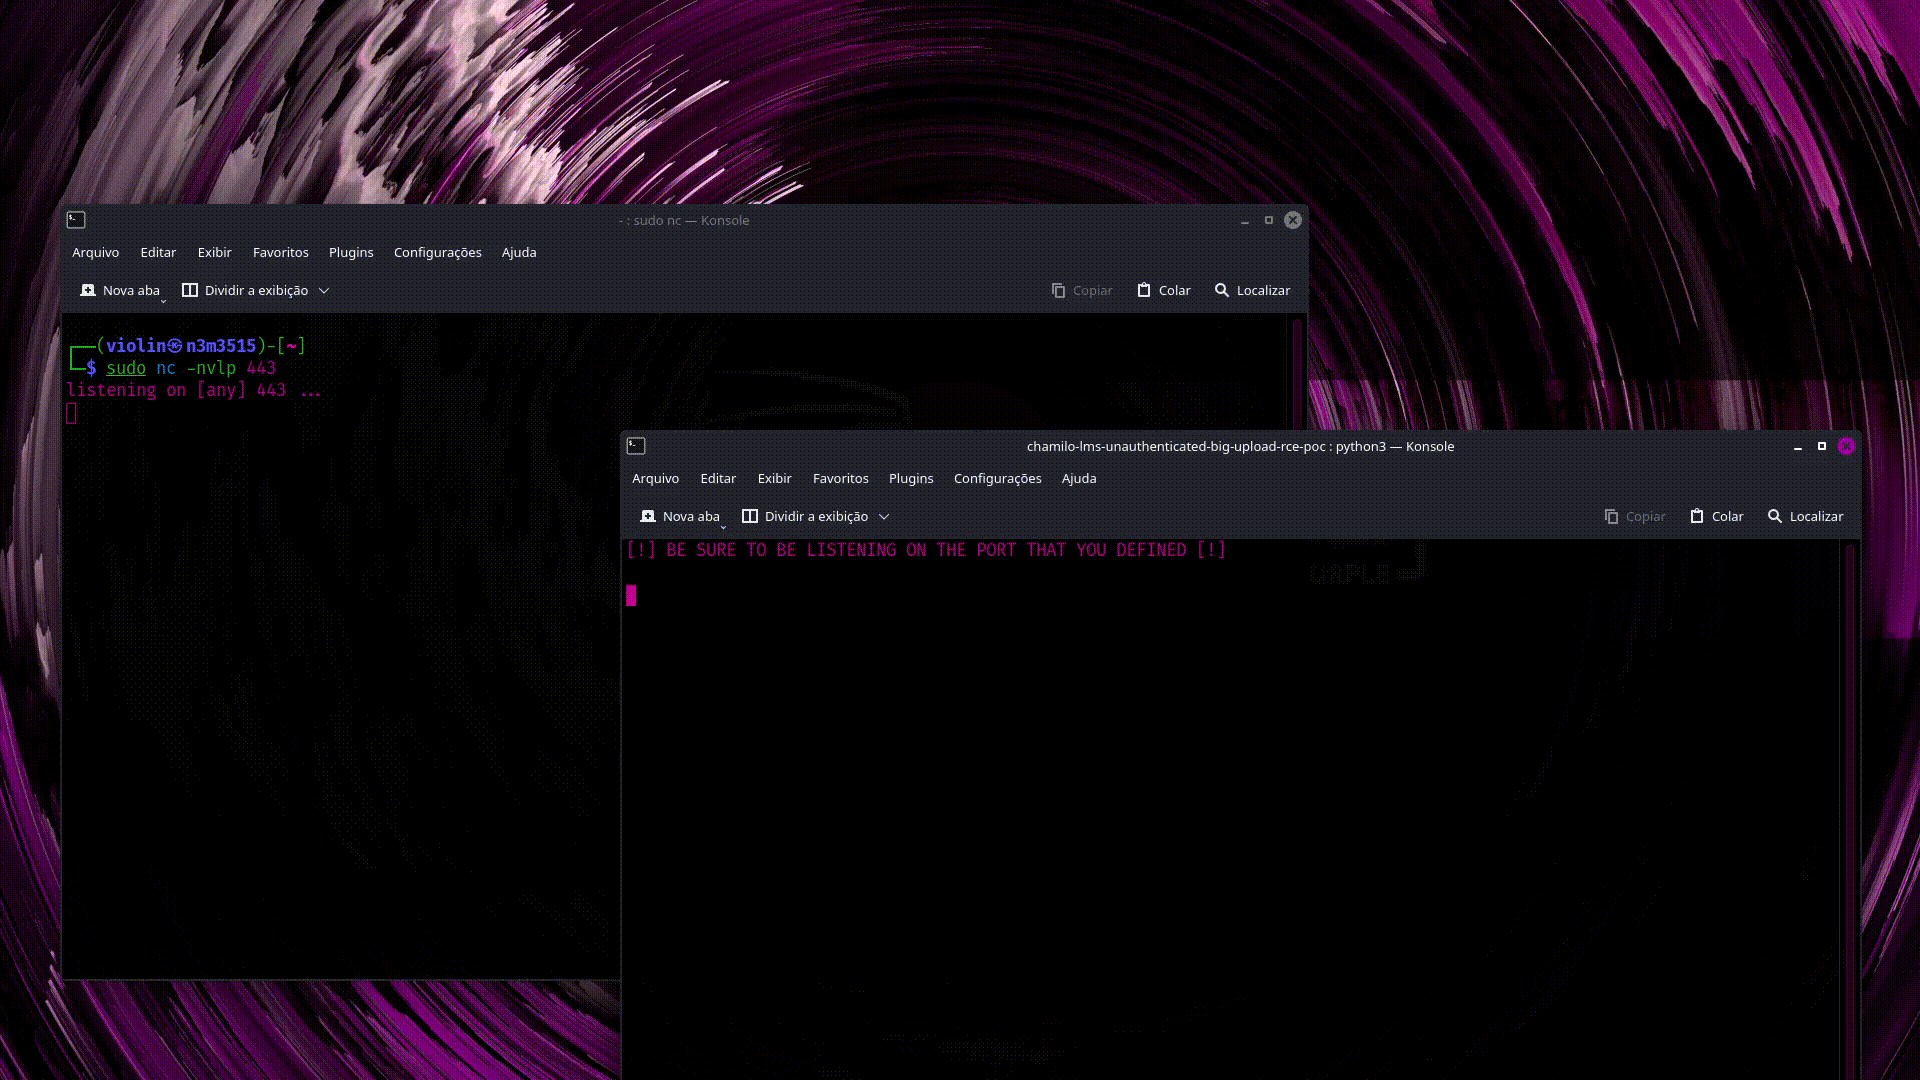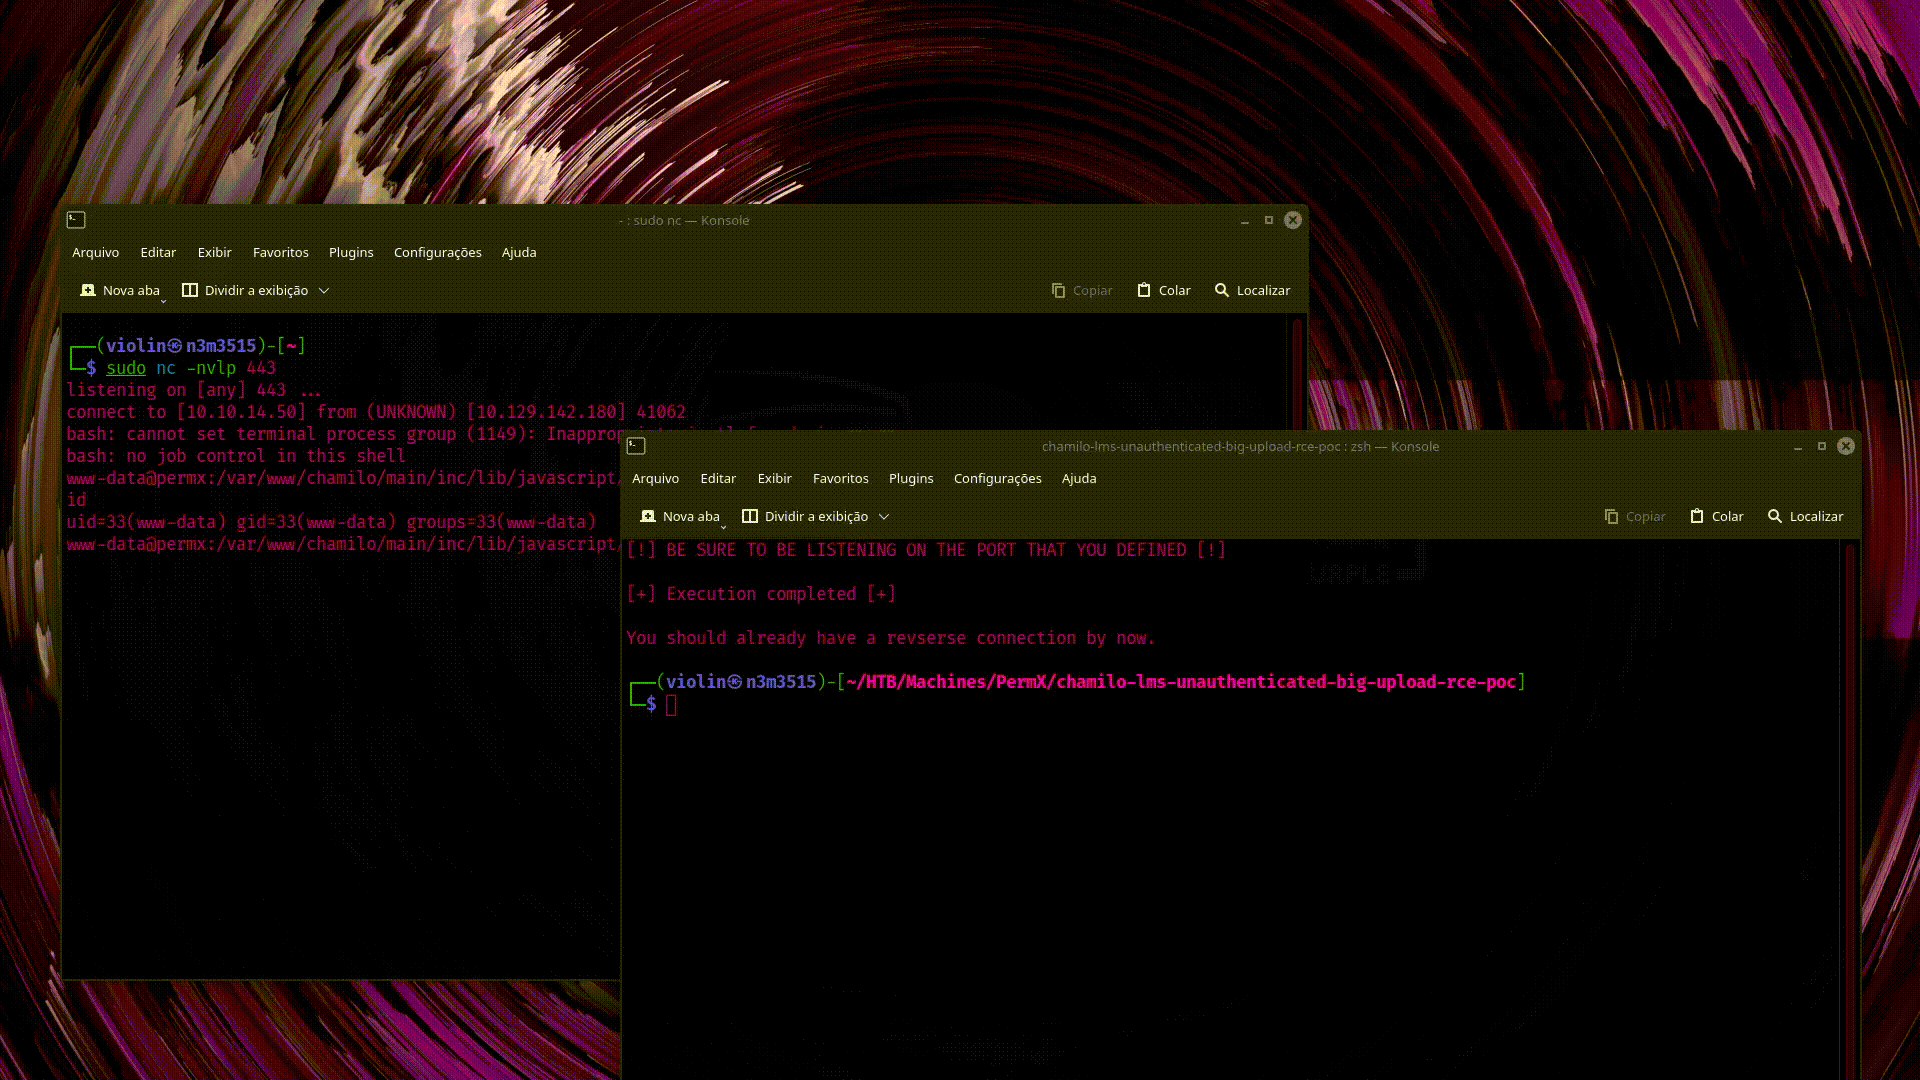 rai2en/cve-2023-4220-chamilo-lms
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 shadowroot97/react2shell-cve-2025-55182
POC React2Shell-CVE-2025-55182