
CVE-2026-87930
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
exploitationpayload-generationpenetration-testing+7
1
winrarzipsexploit/cve-2026-87930Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 mindflarex/cve-2025-61882-poc
Exploit for CVE-2025-61882, a critical pre-auth RCE in Oracle E-Business Suite. Combines SSRF, CRLF injection, HTTP smuggling, and XSLT injection for…
 blacknon/lssh
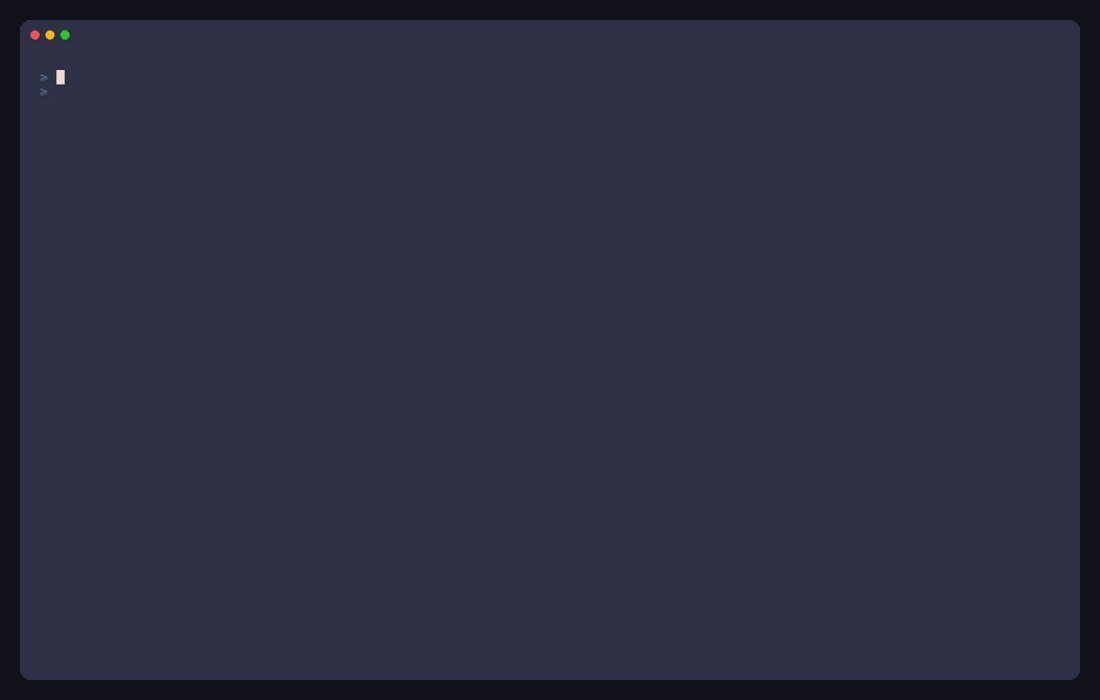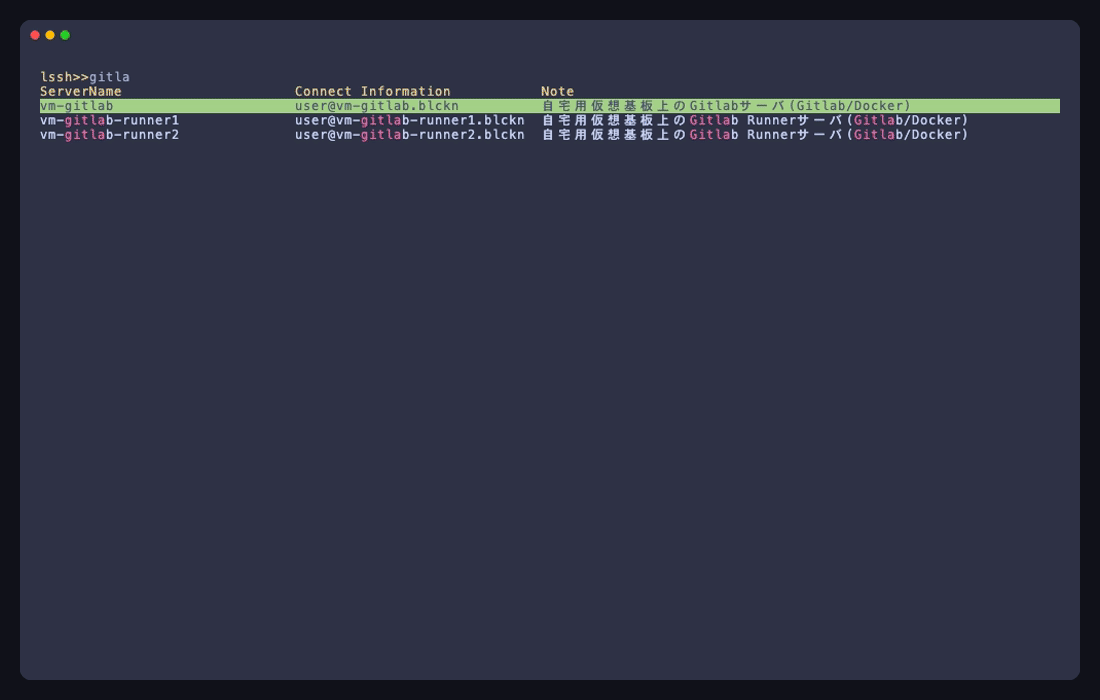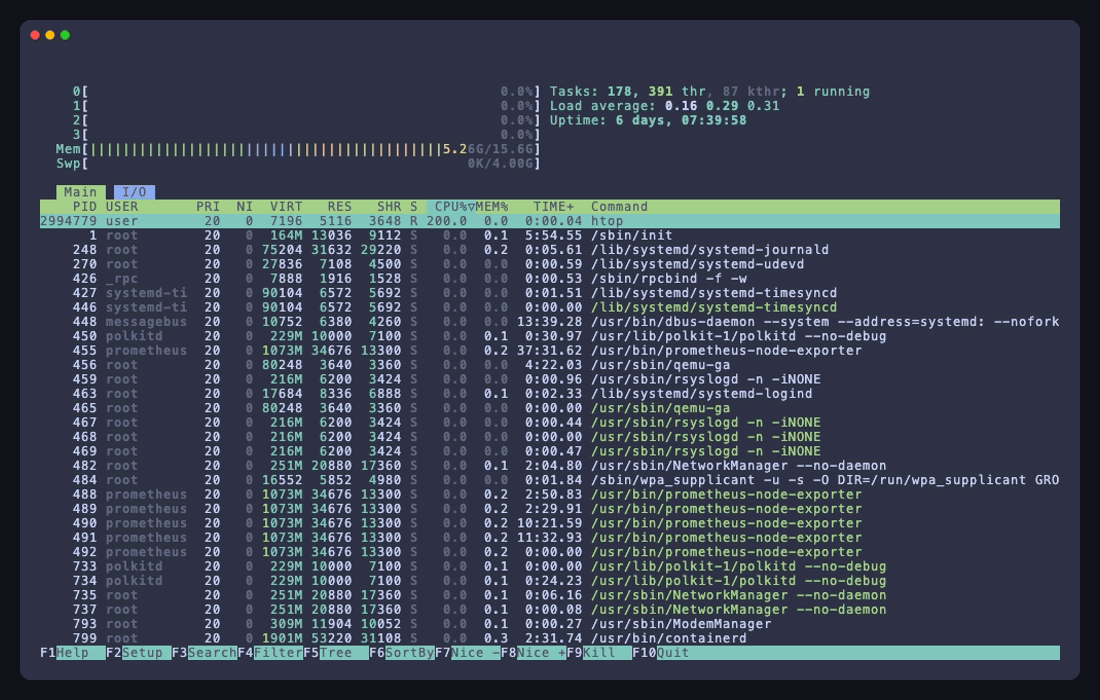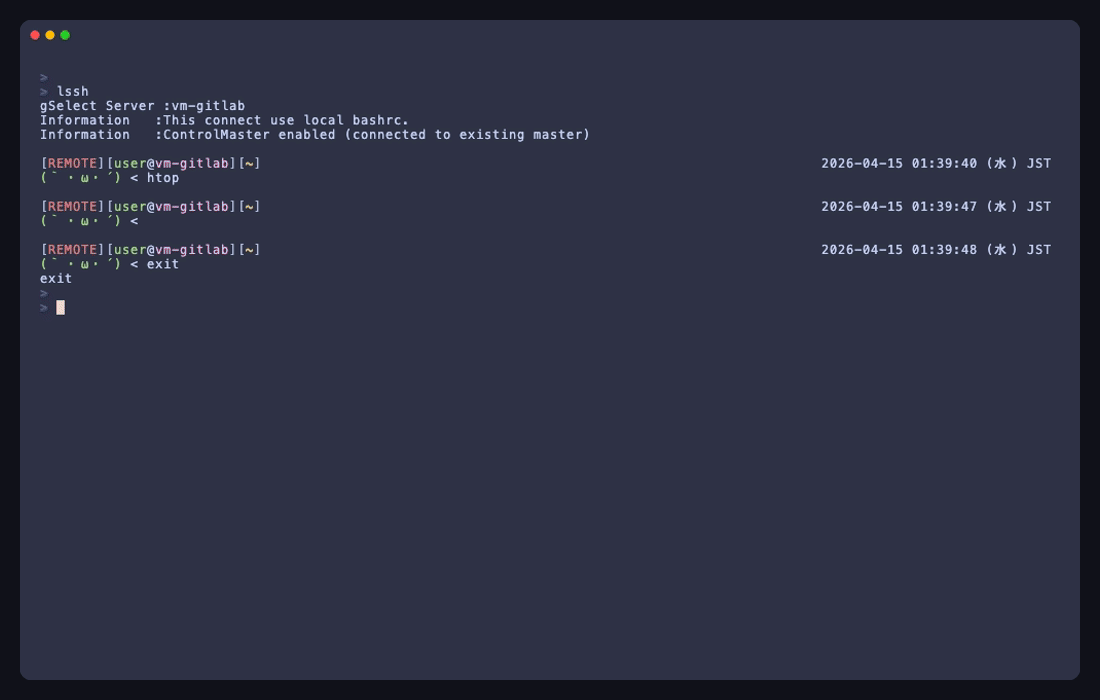
A terminal-native remote access suite for SSH, cloud inventories, provider-backed connectors, parallel commands, mux workspaces, file transfer, and…
 flozz/p0wny-shell
Single-file PHP shell
 note0577/cve-2019-12840-nodejs-exploit
Authenticated Remote Command Execution - Webmin <= 1.910
 touchmycrazyredhat/cve-2022-27925-revshell
Python exploit for CVE-2022-27925 targeting Zimbra Collaboration Suite, enabling unauthenticated remote code execution and reverse shell delivery.
 huahuatzt/cve-2022-27925
Unauthenticated remote code execution exploit for Zimbra Collaboration Suite (CVE-2022-27925). Delivers a reverse shell payload to compromise…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell