
CVE-2026-48907
 noname-elv/cve-2026-48907
Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
exploitationpayload-developmentpenetration-testing+6
1
noname-elv/cve-2026-48907Python CLI that exploits CVE-2026-48907 in Joomla JCE via profile-import upload, verifies shell paths, and opens an interactive command channel on…
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
 cyberalp0/smartermail-cve-2026-24423
Exploit for CVE-2026-24423 — a critical unauthenticated RCE in SmarterMail's ConnectToHub API. Affects all builds prior to 9511.
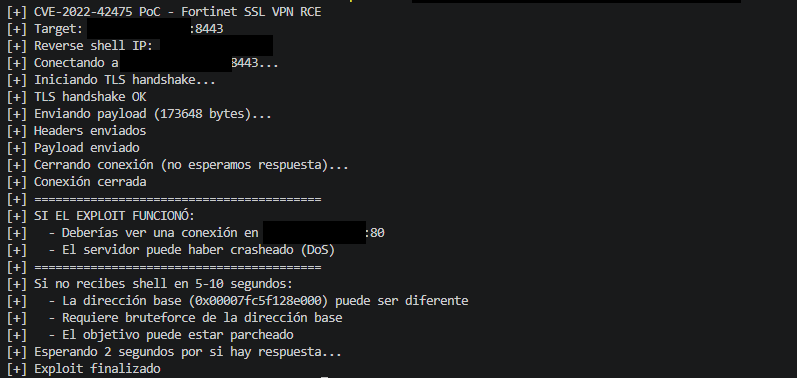 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 nakagami/grdpwasm
A web-based RDP client
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers
 razureink/cve-2024-38077-madlicense_reproduction
CVE Reproduction: cve-2024-38077-madlicense_reproduction
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
 gagaltotal/cve-2026-44825-apache-solr-scanner
Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.
 goultarde/cve-2022-42889-text4shell
Proof of Concept (PoC) for CVE-2022-42889 (Text4Shell) targeting Apache Commons Text versions prior to 1.10.0. This script automates Remote Code…
 hnytgl/cve-2026-41089
CVE-2026-41089 是 Windows Netlogon 服务中一个关键的远程代码执行漏洞,单包即可崩溃 lsass.exe,导致域控制器在约 30-60 秒内重启。此期间该 DC 的所有域认证将失败。
 k3ystr0k3r/cve-2022-0543
PoC for CVE-2022-0543 – Redis Remote Code Execution (RCE)
 chuzoux/cve-2025-32433-exploit-edited
Based on the original version:https://github.com/vulhub/vulhub/blob/master/erlang/CVE-2025-32433/exploit.py Replace Unicode checkmark with ASCII…
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
 joaoaugustom/ipfire_2.25_rce_authenticated
This exploit is based on CVE-2021-33393 and was built upon the original exploit by Mücahit Saratar, extending it to achieve a reverse shell with root…
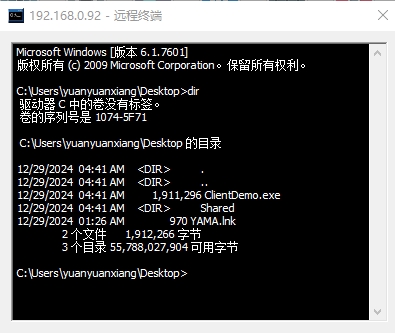 yuanyuanxiang/simpleremoter
A remote control program based on Gh0st: 实现了终端管理、进程管理、窗口管理、远程桌面、文件管理、语音管理、视频管理、服务管理、注册表管理等功能,优化全部代码及整理排版,修复内存泄漏缺陷,程序运行稳定。项目代码仅限于学习和交流用途。
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
 damariion/cve-2015-8522.rce
Exploit for CVE-2015-8522 targeting Tivoli FastBack Server with stack-based buffer overflow, ASLR/DEP bypass, and automated reverse-shell…