
CVE-2019-3929
 xfox64x/cve-2019-3929
Crestron/Barco/Extron/InFocus/TeqAV Remote Command Injection (CVE-2019-3929) Metasploit Module
command-and-controlexploit-frameworkspenetration-testing+3
5
xfox64x/cve-2019-3929Crestron/Barco/Extron/InFocus/TeqAV Remote Command Injection (CVE-2019-3929) Metasploit Module
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…
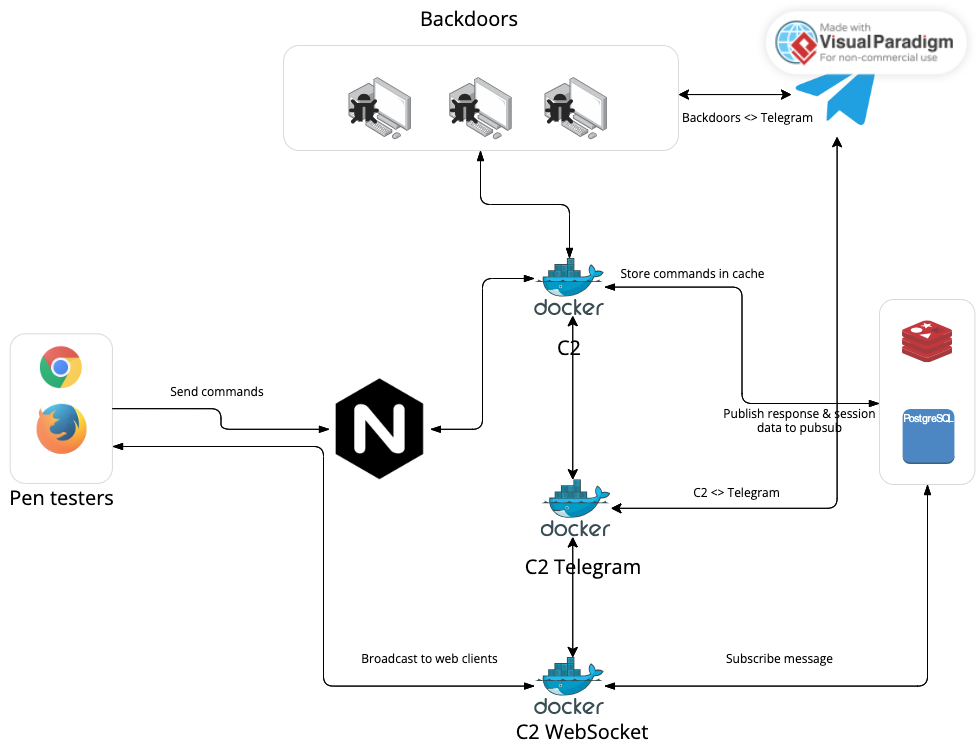 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 enkomio/alanframework
A C2 post-exploitation framework