CVE-2026-28326-check

Non-destructive patch-state checker for SolarWinds ARM CVE-2026-28326 that probes the gRPC listener on TCP 55555 to report VULNERABLE, PATCHED, or…

Non-destructive patch-state checker for SolarWinds ARM CVE-2026-28326 that probes the gRPC listener on TCP 55555 to report VULNERABLE, PATCHED, or…

Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…

Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…

Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…

Exploits CouchDB CVE-2017-12635/12636 for privilege escalation and RCE, then provides an interactive shell with command execution, database browsing,…

Asynchronous RDP client for Python (headless)

Modern tactical exploitation toolkit.

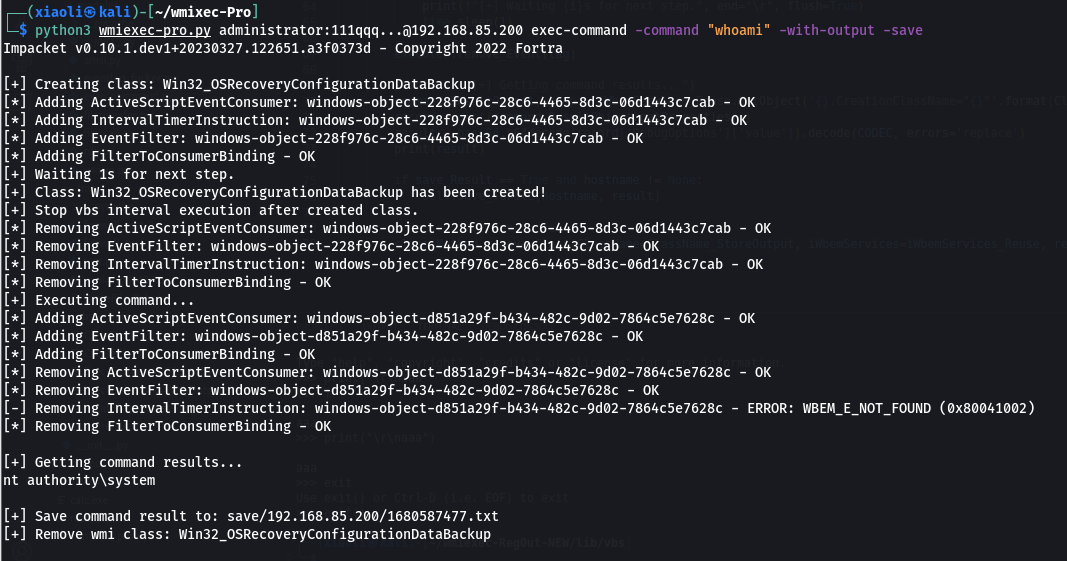
New generation of wmiexec.py

Hooked browser communication over MQTT

A command shell wrapper using only WMI for Microsoft Windows

Intranet penetration tools

marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability

CVE-2026-57827 — RSFiles! Joomla Component Unauthenticated File Upload RCE. Split-controller upload bypass. CVSS 9.8 | CWE-434 | com_rsfiles < 1.17.12

Work in Progress. RAT written in C++ using wxWidgets

This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…