

TornadoRevC2
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
command-and-controlinformation-gatheringlateral-movement+8
24
kamalx06/tornadorevc2Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 0xcyp1337/cve-2026-44402
Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
 cyberalp0/smartermail-cve-2026-24423
Exploit for CVE-2026-24423 — a critical unauthenticated RCE in SmarterMail's ConnectToHub API. Affects all builds prior to 9511.
 ahseven/cve-2026-33017-poc-reverse-shell
Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow, enabling reverse shell via malicious CustomComponent payload.
 gabrielunknown/cve-2026-73570
Zimbra SNMP Notification OS Command Injection — Unauthenticated RCE via SMTP exploit (Poc)
 puzzlepeaches/log4jhorizon
Exploiting CVE-2021-44228 in VMWare Horizon for remote code execution and more.
 bfdfhdsfdd-crypto/cve-2026-22444
Exploit for Apache Solr CVE-2026-22444, leveraging UNC path injection and SMB server to achieve remote code execution via malicious configset and…
 lincolino/lab-annie
Automates exploitation of CVE-2020-13160, a critical remote code execution vulnerability in AnyDesk 5.5.2, enabling penetration testers to validate…
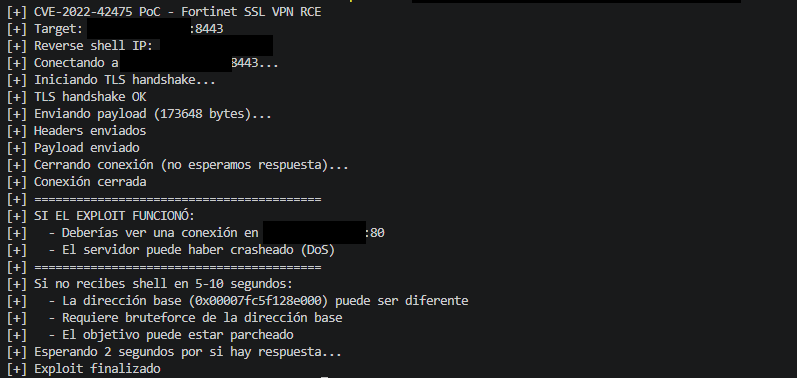 ull0a/cve-2022-42475-poc
Proof of Concept (PoC) for research and controlled laboratory validation of CVE-2022-42475, a critical heap-based buffer overflow vulnerability…
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
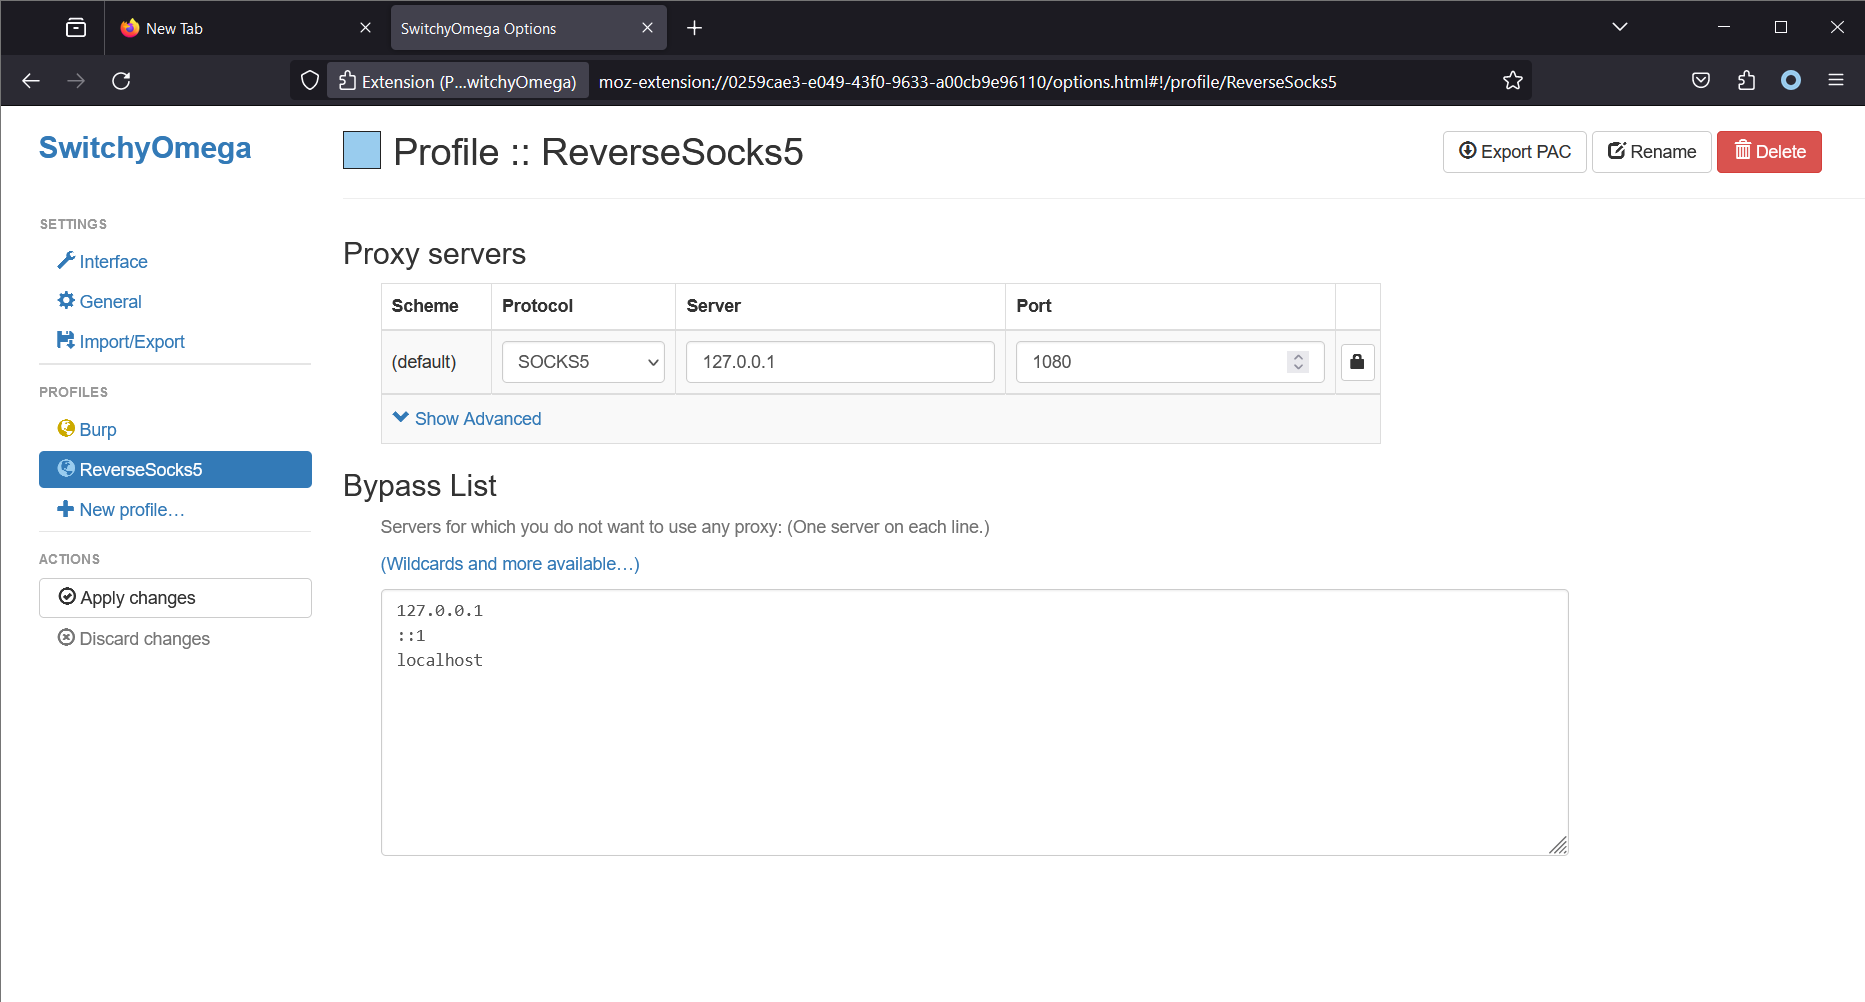 acebond/reversesocks5
Single executable reverse SOCKS5 proxy written in Golang.
 hackerhouse-opensource/offensivelua
Offensive Lua.
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 mbadanoiu/java-servlets-shell
JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
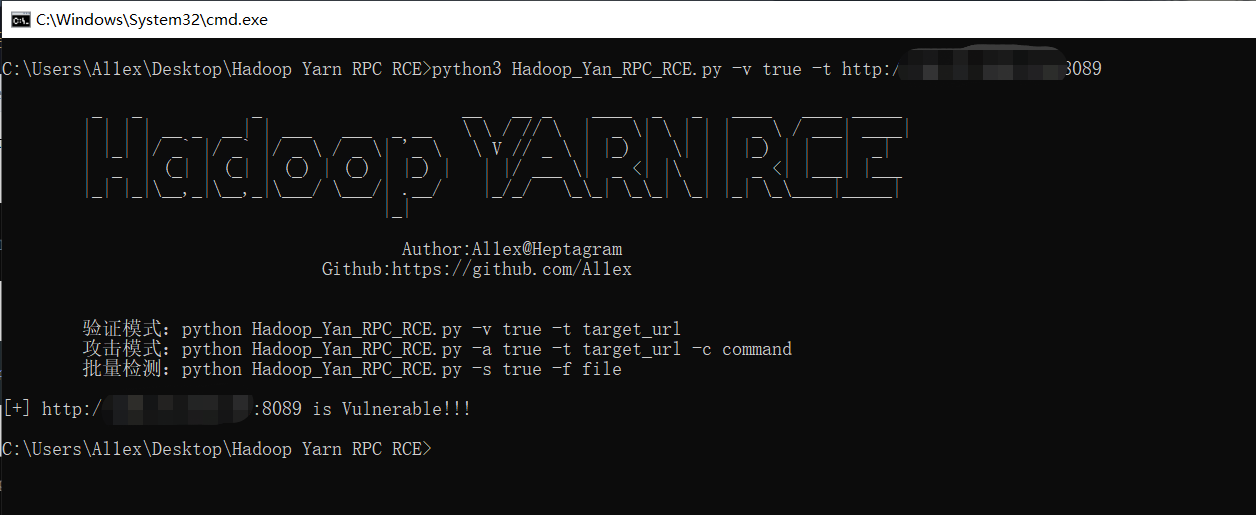 al1ex/hadoop-yarn-resourcemanager-rce
Hadoop Yan ResourceManager unauthorized RCE
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 flast101/php-8.1.0-dev-backdoor-rce
PHP 8.1.0-dev Backdoor System Shell Script