
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
RingReaper preview

RingReaper

GitHubmatheuzsecurity/ringreaper

Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
adversarial-attackcommand-and-controldata-exfiltration+5
3871 year ago
mqxss preview

mqxss

GitHubgrampae/mqxss

Hooked browser communication over MQTT
command-and-controlinformation-gatheringpayload-generation+4
82 years ago
ReverseHttp preview

ReverseHttp

GitHubd4vinci/reversehttp

Python backdoor that uses http post/get requests to communicate
command-and-controlpayload-developmentpenetration-testing+3
4210 years ago
dicerosbicornis preview

dicerosbicornis

GitHubmaldevel/dicerosbicornis

A fully featured Windows backdoor that uses email as a C&C server
command-and-controldata-exfiltrationencryption-decryption-tools+5
169 years ago
vsFTP-2.3.4-Remote-Root-Shell-Exploit preview

vsFTP-2.3.4-Remote-Root-Shell-Exploit

GitHubgill-singh-a/vsftp-2.3.4-remote-root-shell-exploit

A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4
command-and-controlexploitationpayload-development+3
22 years ago
Log4Shell-CVE-2021-44228-PoC preview

Log4Shell-CVE-2021-44228-PoC

GitHubpierpaolosestito-dev/log4shell-cve-2021-44228-poc

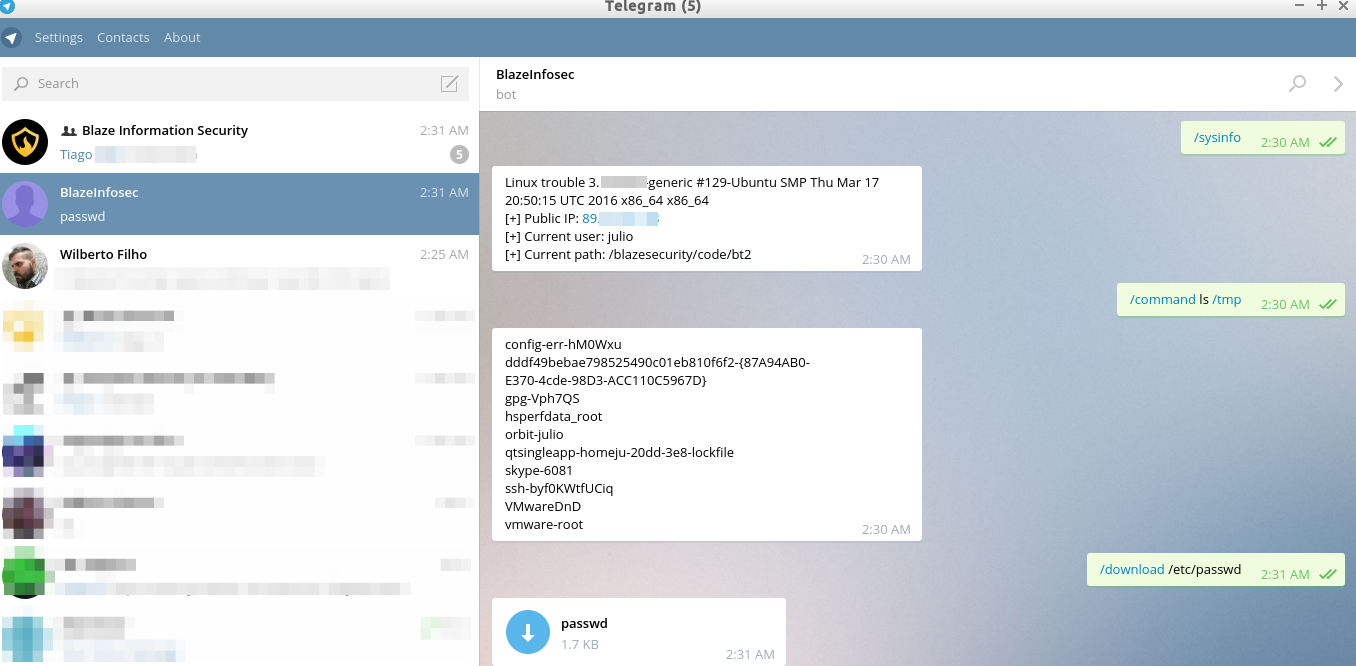
CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.
command-and-controlexploitationpayload-development+3
13 years ago
bt2 preview

bt2

GitHubblazeinfosec/bt2

Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C

command-and-controlpayload-developmentpenetration-testing+3
20610 years ago
browser-backdoor preview

browser-backdoor

GitHubimcpwn/browser-backdoor

BrowserBackdoor is an Electron Application with a JavaScript WebSocket Backdoor and a Ruby Command-Line Listener

command-and-controldata-exfiltrationpayload-generation+4
3418 years ago
twittor preview

twittor

GitHubpaulsec/twittor

A fully featured backdoor that uses Twitter as a C&C server

command-and-controlexploitationpayload-development+4
81111 years ago
Reverse_DNS_Shell preview

Reverse_DNS_Shell

GitHubahhh/reverse_dns_shell

A python reverse shell that uses DNS as the c2 channel
command-and-controldns-analysispayload-generation+2
50710 years ago
canisrufus preview

canisrufus

GitHubmaldevel/canisrufus

A stealthy Python based Windows backdoor that uses Github as a command and control server
command-and-controlpayload-generationpost-exploitation+2
2659 years ago
gdog preview

gdog

GitHubmaldevel/gdog

A fully featured Windows backdoor that uses Gmail as a C&C server

command-and-controlpayload-generationpost-exploitation+2
5089 years ago
PingRAT preview

PingRAT

GitHubumutcamliyurt/pingrat

ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.

command-and-controlpenetration-testingred-teaming+1
4744 months ago
TeamsImplant preview

TeamsImplant

GitHuballevon412/teamsimplant

Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…

command-and-controlexploit-frameworkspayload-development+5
2074 years ago