Weblogic_CVE-2020-14645

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

Proof of concept for CVE-2026-33439, an unauthenticated RCE in OpenAM via Java deserialization

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool

Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…

JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz

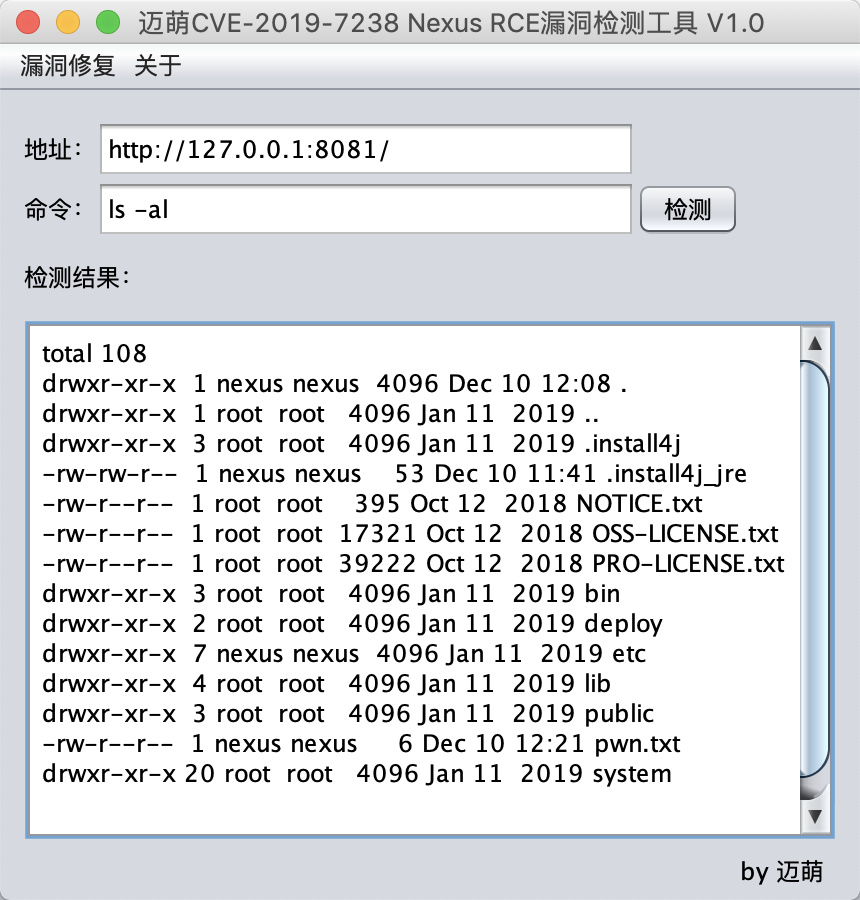
CVE-2019-7238 Nexus RCE漏洞图形化一键检测工具。CVE-2019-7238 Nexus RCE Vul POC Tool.

fork of the popular jsch library

CVE-2018-3191 反弹shell

ActiveMQ_CVE-2015-5254

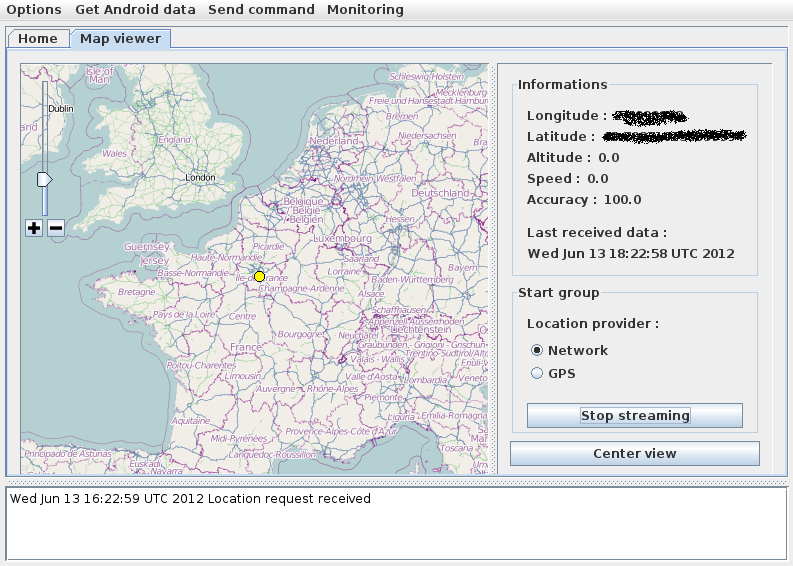
Remote Administration Tool for Android devices

[WIP]RemoteAssistance like TeamViewer(C++)

AndroRAT | Remote Administrator Tool for Android OS Hacking

Unauthenticated remote command execution in Papercut service allows an attacker to execute commands due to improper access controls in the…

Proof-of-concept exploit for CVE-2025-30065 demonstrating remote class instantiation and SSRF via malicious Parquet files in Java applications.

Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…

Demo of CVE-2021-44228 Log4Shell.