
flipper-mcp
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
ai-securitybluetooth-securitycommand-and-control+9
22
roostercoopllc/flipper-mcpAI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 d6fault/cve-2026-95675
Python PoC exploiting CVE-2026-95675, an unauthenticated root command injection in D-Link DAP-1360 RevB firmware via a hardcoded auth-bypass and the…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 exdev994/cve-2026-90817
Python PoC for CVE-2026-90817, an unauthenticated REDCap RCE via survey passthrough routing and file-path injection, with a Docker lab and…
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…
 k3ystr0k3r/cve-2026-32604
Proof-of-concept exploit for CVE-2026-32604, a command injection RCE in Spinnaker's GitRepo artifact handling via the version field.
 ustr/cve-2026-25057
PoC for Zip Slip in MarkUs Assignment Configuration Uploads
 e5dfdd568a75282b712b6d93a7a18e12/cve-2025-32432
Python exploit for CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii2 __class injection, with command execution and reverse shell support.
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
 dmonst3r/cve-2015-8562
Joomla 1.5 - 3.4.5 Object Injection RCE X-Forwarded-For header
 khashayarnzk/cve-2025-2945-pgadmin-rce
PoC for CVE-2025-2945 — pgAdmin 4 authenticated eval() injection RCE, CVSS 9.9
 gabrielunknown/cve-2026-73570
Zimbra SNMP Notification OS Command Injection — Unauthenticated RCE via SMTP exploit (Poc)
 cypher-21/cve-2026-23520
Proof-of-concept exploit for CVE-2026-23520, a command injection vulnerability in Arcane's updater service, enabling remote code execution via…
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.
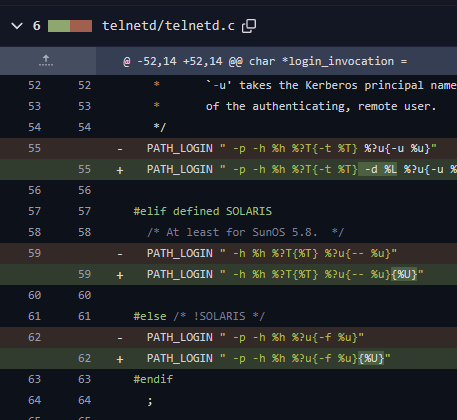 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
 dejavu666/cve-2024-4577
Proof-of-concept exploit for CVE-2024-4577, a PHP CGI argument injection vulnerability, enabling remote code execution and shell access on vulnerable…
 bfdfhdsfdd-crypto/cve-2026-22444
Exploit for Apache Solr CVE-2026-22444, leveraging UNC path injection and SMB server to achieve remote code execution via malicious configset and…