
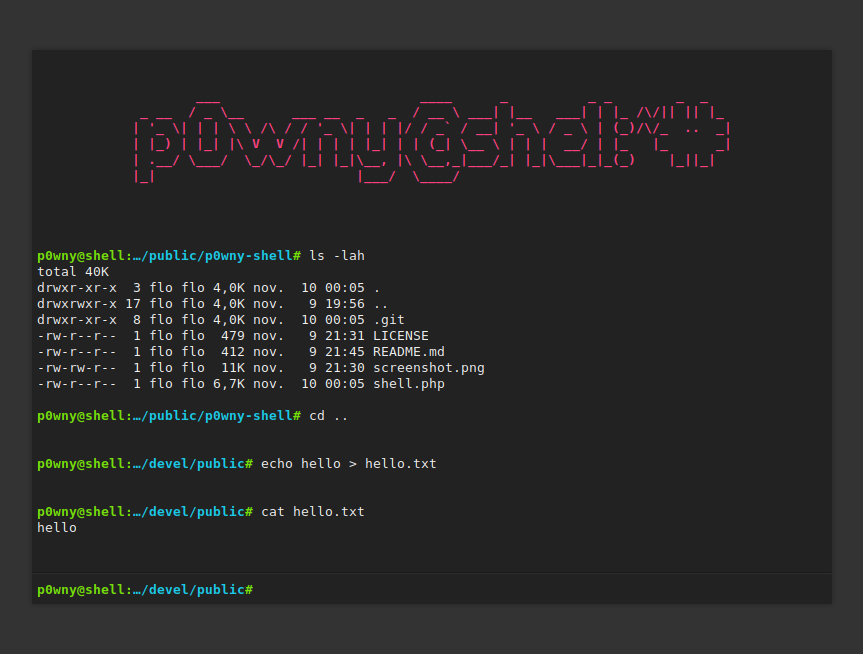
p0wny-shell
 flozz/p0wny-shell
Single-file PHP shell
penetration-testingremote-access-toolweb-application-exploitation
flozz/p0wny-shellSingle-file PHP shell
 note0577/cve-2019-12840-nodejs-exploit
Authenticated Remote Command Execution - Webmin <= 1.910
 mouadk/parquet-rce-poc-cve-2025-30065
Proof-of-concept exploit for CVE-2025-30065 demonstrating remote class instantiation and SSRF via malicious Parquet files in Java applications.
 unknowndevice64/exploits_cve-2019-19781
Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…
 goultarde/remotemouse-3.008-rce
POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601
 machine-farmer/punchingbag-for-react2shell
Intentionally vulnerable Next.js app for CVE-2025-55182 security research and CTF challenges
 xl337x/cve-2023-31902
Pre-auth RCE exploit for Mobile Mouse 3.6.0.4 via TCP (port 9099) and WebSocket (port 35913) with Python scripts for unauthenticated command…
 purpleteam-ru/cve-2021-38163
CVE-2021-38163 - SAP NetWeaver AS Java Desynchronization Vulnerability
 mekhalleh/citrix_dir_traversal_rce
The exploitation module for the CVE-2019-19781 #Shitrix (Vulnerability in Citrix Application Delivery Controller and Citrix Gateway).
 jas502n/cve-2019-16278
Directory transversal to remote code execution
 cyberaguiar/cve-2016-3088
Apache ActiveMQ Remote Code Execution Exploit
 chipik/sap_eem_cve-2020-6207
PoC for CVE-2020-6207 (Missing Authentication Check in SAP Solution Manager)
 sharphack/cve-2019-19781
Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781) that executes arbitrary commands on vulnerable…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
 alisster00/cve-2026-23744-rce
This utility was created during research involving MCPJam v1.4.2. The application exposes an API endpoint that accepts a server configuration object.…
 jagg3rsec/cve-2014-6287
Exploit implementation for CVE-2014-6287, targeting a remote code execution vulnerability in a web application. Provides a proof-of-concept for…
 alteredsecurity/cve-2021-38647
CVE-2021-38647 - POC to exploit unauthenticated RCE #OMIGOD
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.