

CVE-2024-6387
 p4x1s/cve-2024-6387
SSH RCE PoC CVE-2024-6387
exploitationpayload-developmentpenetration-testing+3
p4x1s/cve-2024-6387SSH RCE PoC CVE-2024-6387
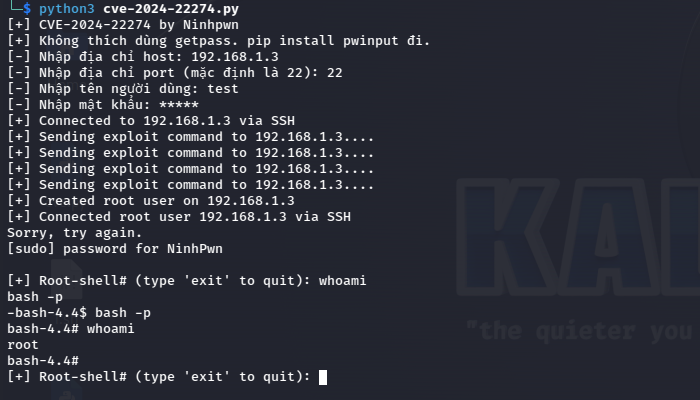 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 gill-singh-a/vsftp-2.3.4-remote-root-shell-exploit
A Simple Python Program that uses gets a Remote Root Shell on the Target Device by exploiting a Vulnerability (CVE-2011-2523) present in vsFTP 2.3.4
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 lemieone/cve-2025-32433
Missing Authentication for Critical Function (CWE-306)-Exploit
 mrdreamreal/cve-2025-32433
CVE-2025-32433 Summary and Attack Overview
 robidev/cve-2020-14871-exploit
This is a basic ROP based exploit for CVE 2020-14871. CVE 2020-14871 is a vulnerability in Sun Solaris systems libpam library, and exploitable over…
 jayanaxhf/filessh
A fast and convenient TUI file browser for remote servers
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 adhikara13/cve-2022-4510-walkingpath
A Python script for generating exploits targeting CVE-2022-4510 RCE Binwalk. It supports SSH, command execution, and reverse shell options. Exploits…
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 tenebrae93/cve-2025-3243
A proof-of-concept exploit for CVE-2025-32433, a critical vulnerability in Erlang's SSH library that allows pre-authenticated code execution via…
 symbolexe/cve-2024-6387
SSH Exploit for CVE-2024-6387 : RCE in OpenSSH's server, on glibc-based Linux systems
 carlosalbertotuma/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
 4lxprime/regresshive
rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
 0xpthree/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang OTP SSH server. Sends crafted SSH packets to open a reverse shell and gain root access.
 0dinox/cve-2024-415770-ssrf-rce
Automated exploit for CVE-2024-415770: leverages SSRF to achieve RCE, registers an agent on the teamserver, opens a socket, and injects an SSH key…