Weblogic_CVE-2020-14645

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

A professional Python tool designed for educational penetration testing, demonstrating SSH vulnerabilities (CVE-2008-0166 / CVE-2008-1657) with…

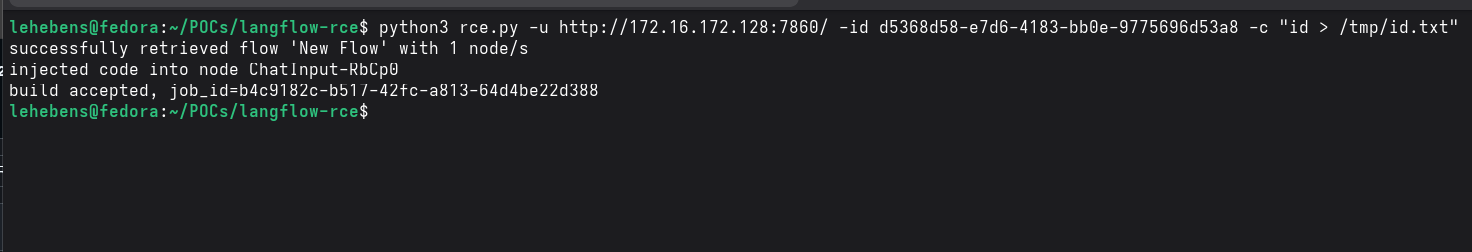
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…

PoC for CVE-2026-33439, a pre-auth RCE in OpenAM via unsafe Java deserialization.

Python proof-of-concept for CVE-2026-39987, exploiting an unauthenticated WebSocket terminal endpoint to achieve remote command execution and reverse…

Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.

Python exploit for CVE-2023-42793 that achieves remote code execution on TeamCity Linux servers by encoding a payload in a URL and sending it to the…

Proof-of-concept exploit for CVE-2026-78159, an unauthenticated RCE in The Events Calendar WordPress plugin via the parse_array widget classes sink.

Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…

CVE-2026-63030 & CVE-2026-60137 RCE chain proof-of-concept

Proof-of-concept exploit for CVE-2026-32604, a command injection RCE in Spinnaker's GitRepo artifact handling via the version field.

Proof-of-concept exploit for CVE-2026-86218, an unauthenticated RCE in N-able N-central via Struts BeanUtils, with version detection and command…

PoC for Zip Slip in MarkUs Assignment Configuration Uploads

Python PoC for CVE-2026-33439, an OpenAM pre-authentication RCE via jato.clientSession deserialization

Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…

Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated

Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…