
CVE-2026-87902
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
exploitationpayload-developmentpenetration-testing+6
bhideki/cve-2026-87902Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 hhesenjan/cve-2023-422-chamilo-lms-rce
Python exploit for CVE-2023-4220 in Chamilo LMS that uploads a file and delivers an unauthenticated reverse shell to a netcat listener.
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
 ustr/cve-2026-25057
PoC for Zip Slip in MarkUs Assignment Configuration Uploads
 threatexpert/gonc
Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
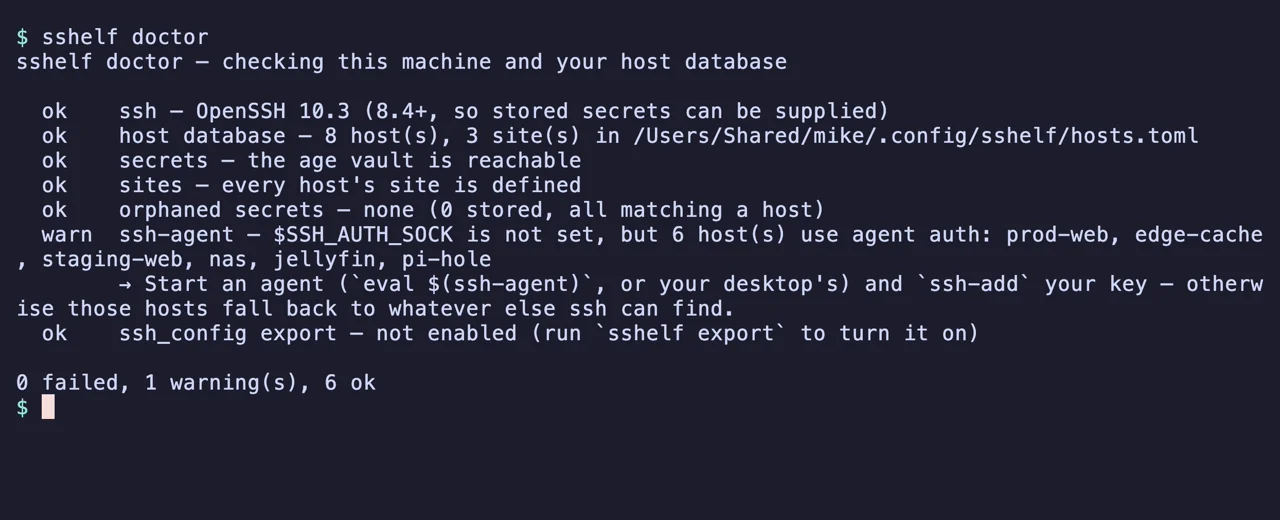 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 tibbersv6/cve-2026-21440-poc-exp
Proof-of-concept exploit for CVE-2026-21440, enabling file upload and remote command execution on Windows web servers with built-in sensitive path…
 0xgh057r3c0n/cve-2026-22812
Python exploit tool for OpenCode RCE (CVE-2026-22812) providing command execution, file read/write/upload/download, and interactive shell for…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 openssh/openssh-portable
Portable OpenSSH
 richlegrand/bitbang-cli
Establish secure remote access to a machine with interactive shell, file transfer, and web proxy over end-to-end encrypted peer-to-peer WebRTC, using…