
cve-2025-3248
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
command-and-controlexploitationpenetration-testing+3
1
bambooqj/cve-2025-3248Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 pol-ruiz/poc-cve-2019-12840
Esto es una prueba de concepto propia i basica de la vulneravilidad CVE-2019-12840 la qual te da un RCE en root
 nu11secur1ty/sh1mazu
Meterpreter auto exploit program
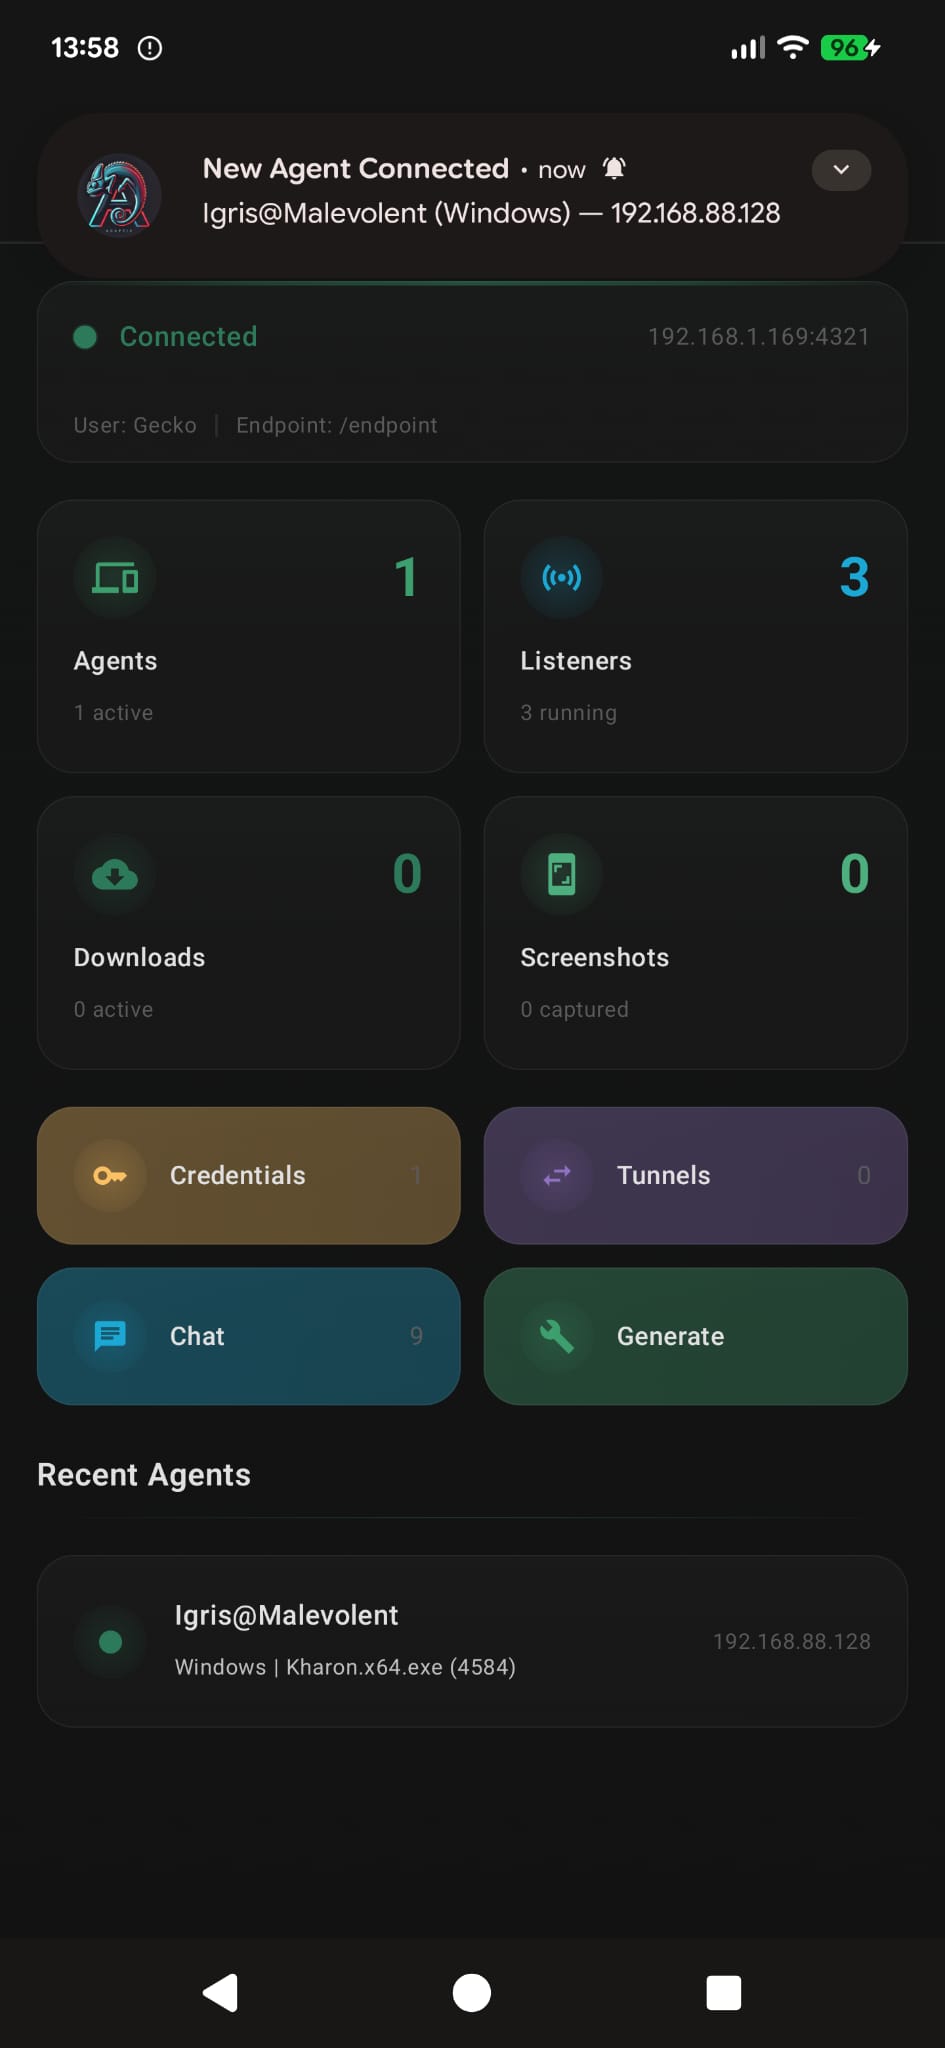 blacksnufkin/geckodroid
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…
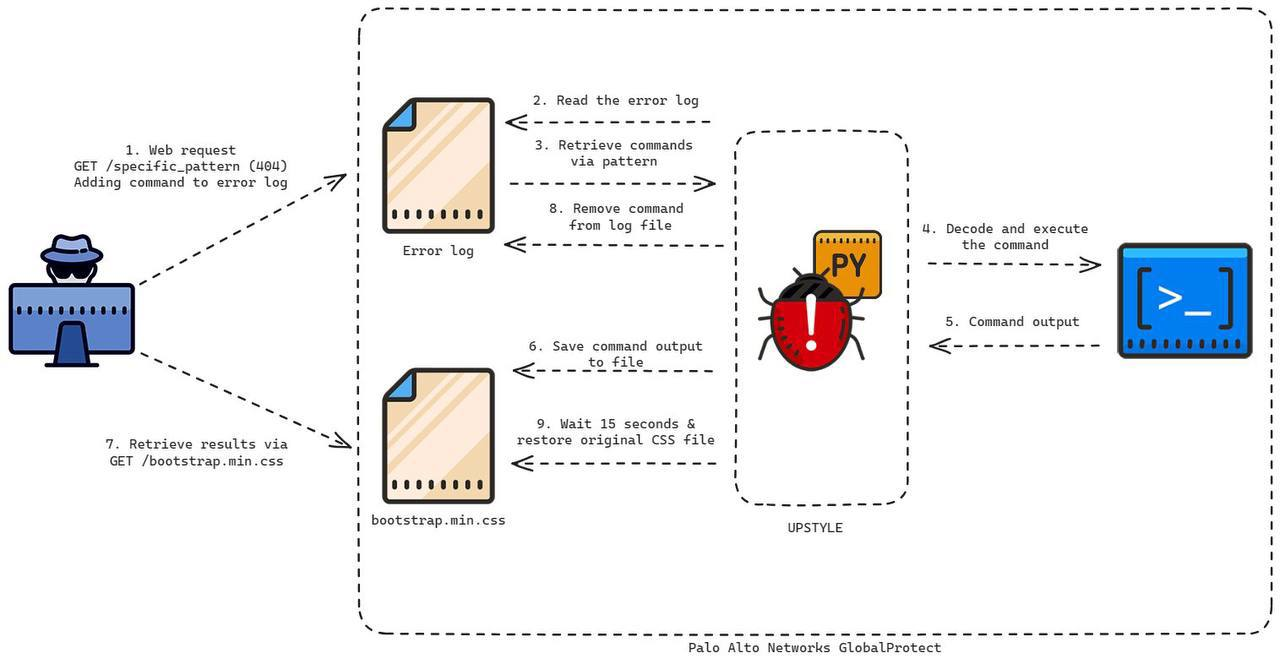 mrr0b0t19/cve-2024-3400
Vulnerabilidad de palo alto
 nxploited/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 xxnbyy/cve-2017-15944-poc
CVE-2017-15944 Palo Alto Networks firewalls remote root code execution POC
 regent8sh/panosexploitmultitool
Exploitation and Post-Exploitation Multitool for Palo Alto PAN-OS Systems affected by vulnerabilities CVE-2024-0012 and CVE-2024-9474
 9aylas/backdooring-zmm100-fingerprint-devices
AuthBypass & Auto Backdooring Devices
 behzadmagzer/auto-postxploit
Windows Auto Post Exploitation - For ReD Team