
Antecursor
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
command-and-controlexploitationhardware-iot-security+5
5
antecursor/antecursorAutonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
 arvanaghi/sessiongopher
SessionGopher is a PowerShell tool that uses WMI to extract saved session information for remote access tools such as WinSCP, PuTTY, SuperPuTTY,…
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 mverschu/adwsdomaindump
Active Directory information dumper via ADWS for evasion purposes.
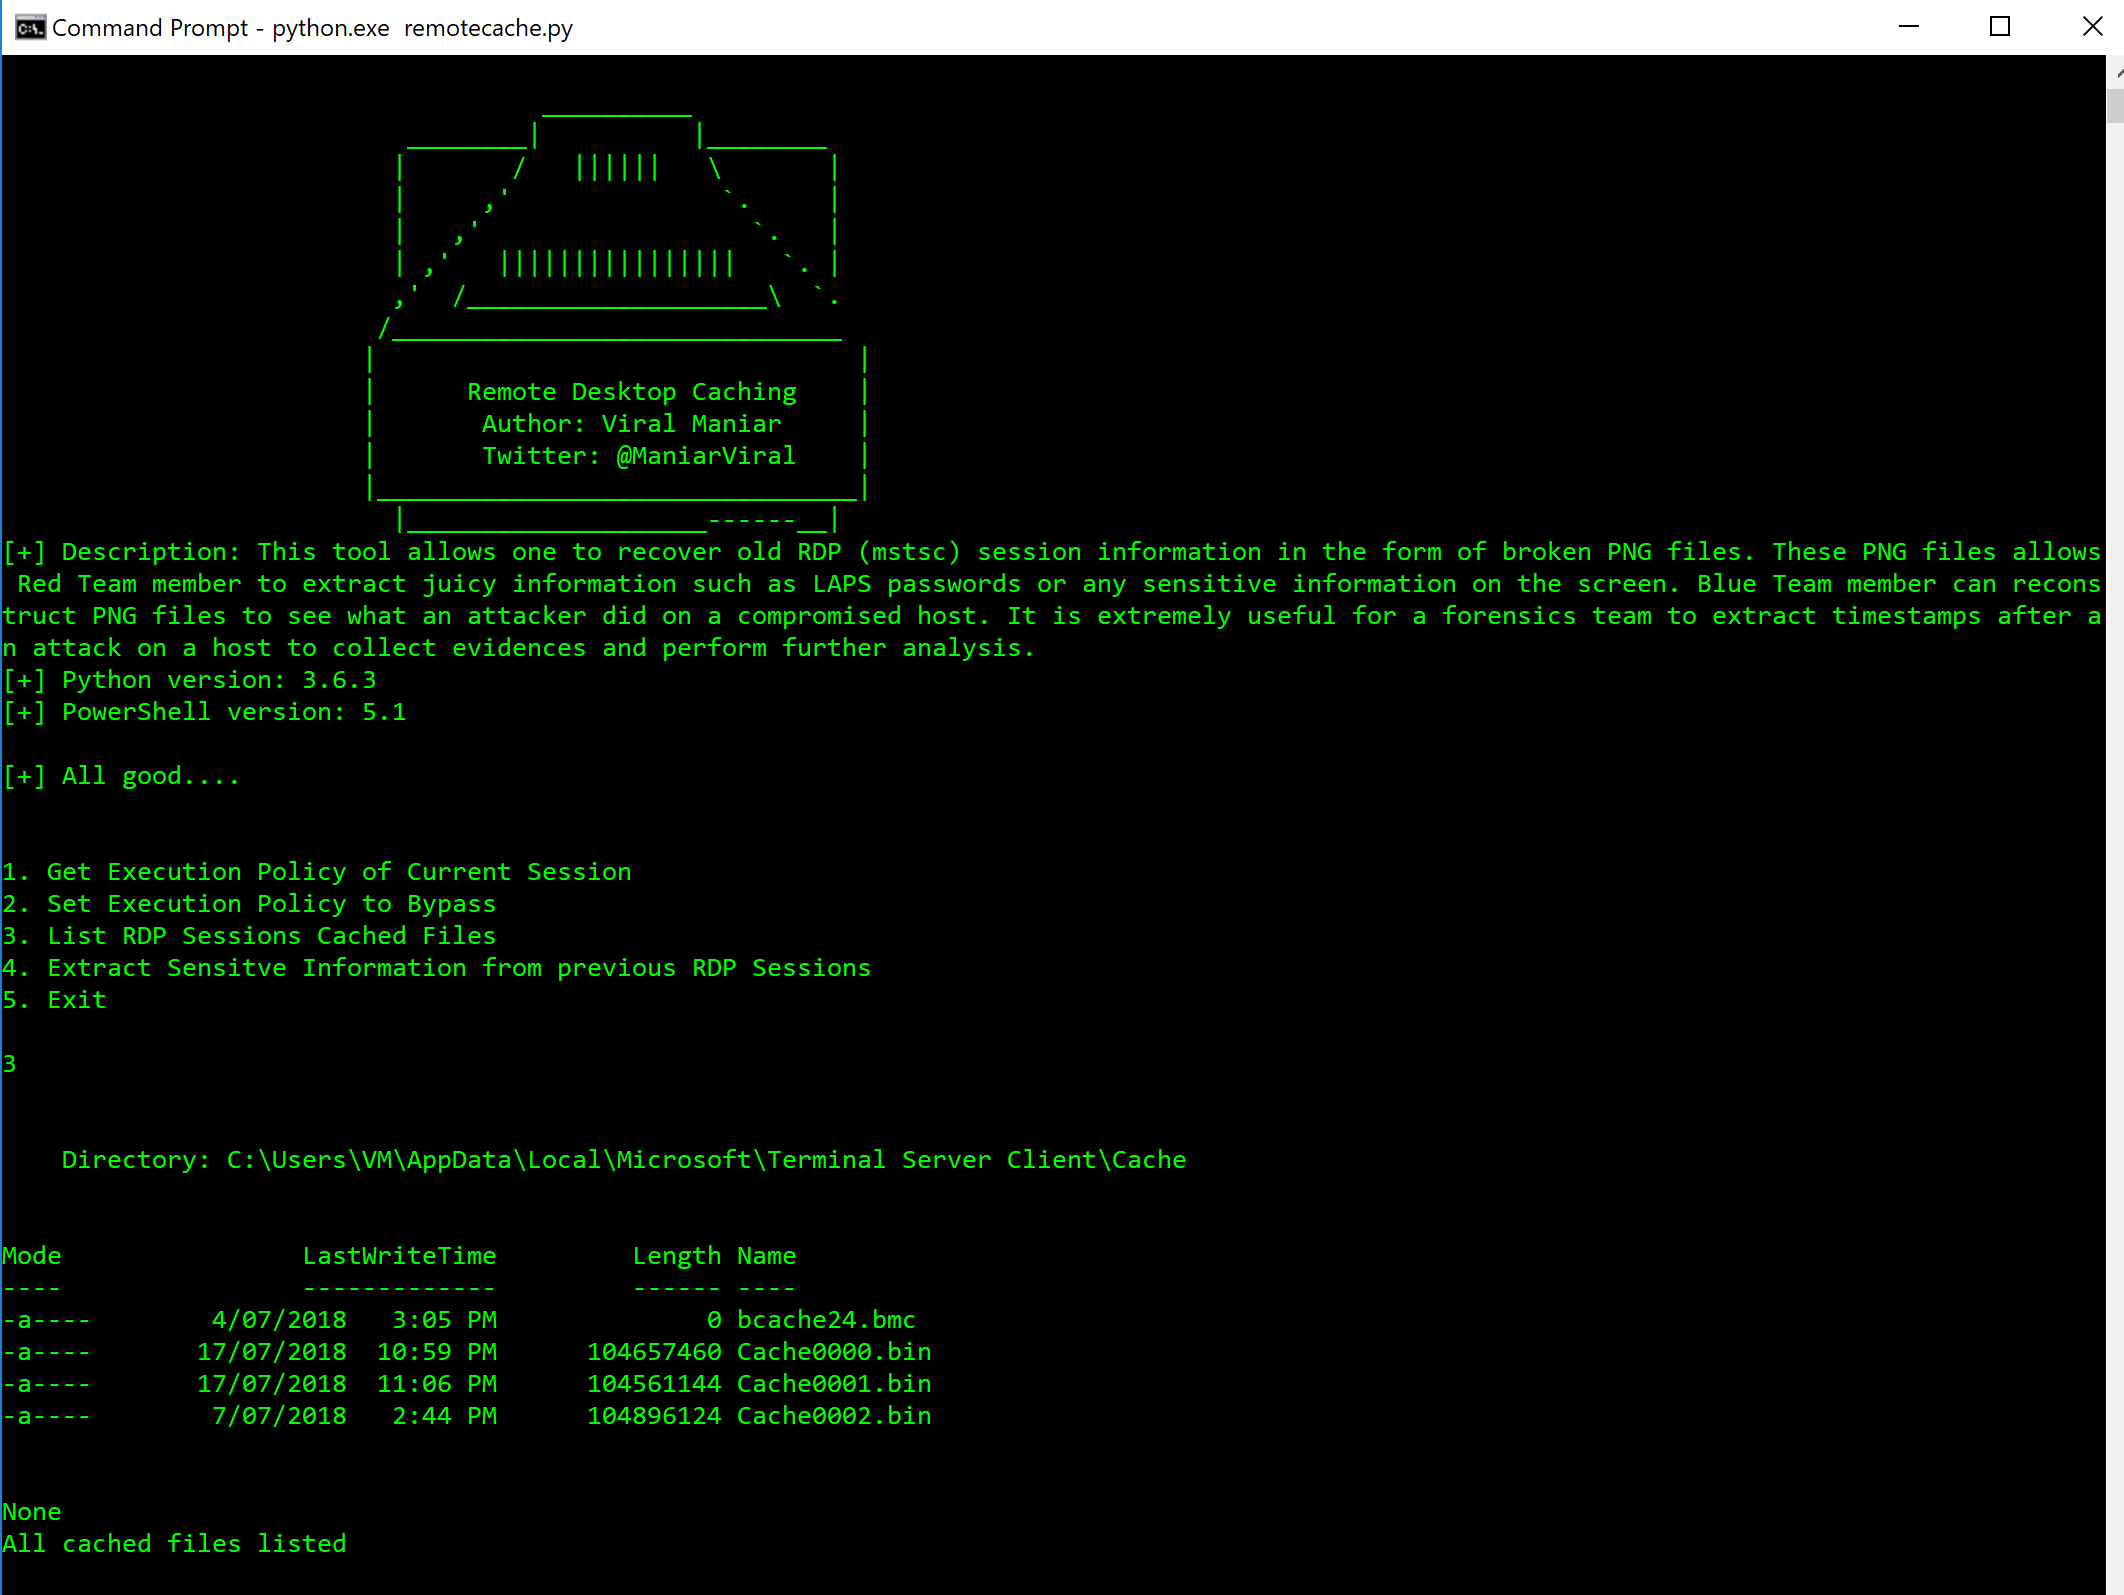 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
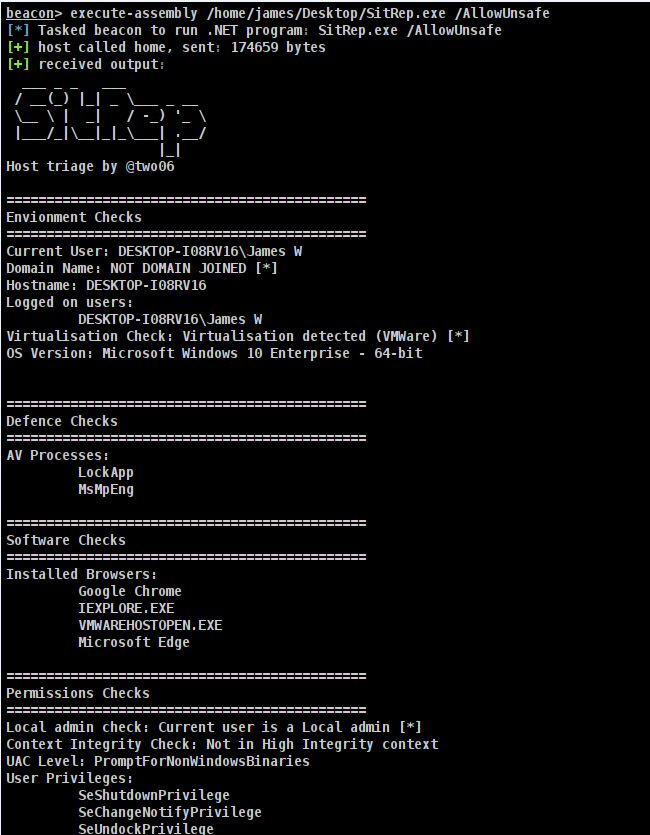 mdsecactivebreach/sitrep
Extensible host triage tool for red teams, dynamically loading OpSec-aware checks to gather user, domain, privilege, and credential information from…
 brittonhayes/pillager
Pillage filesystems for sensitive information with Go 🔍
 talyx66/webfang
WEBFANG, is my first CLI, a modular OSINT & Reconnaissance toolkit curated for Ethical Hackers and Red-Teamers. Sink fangs into web targets using a…
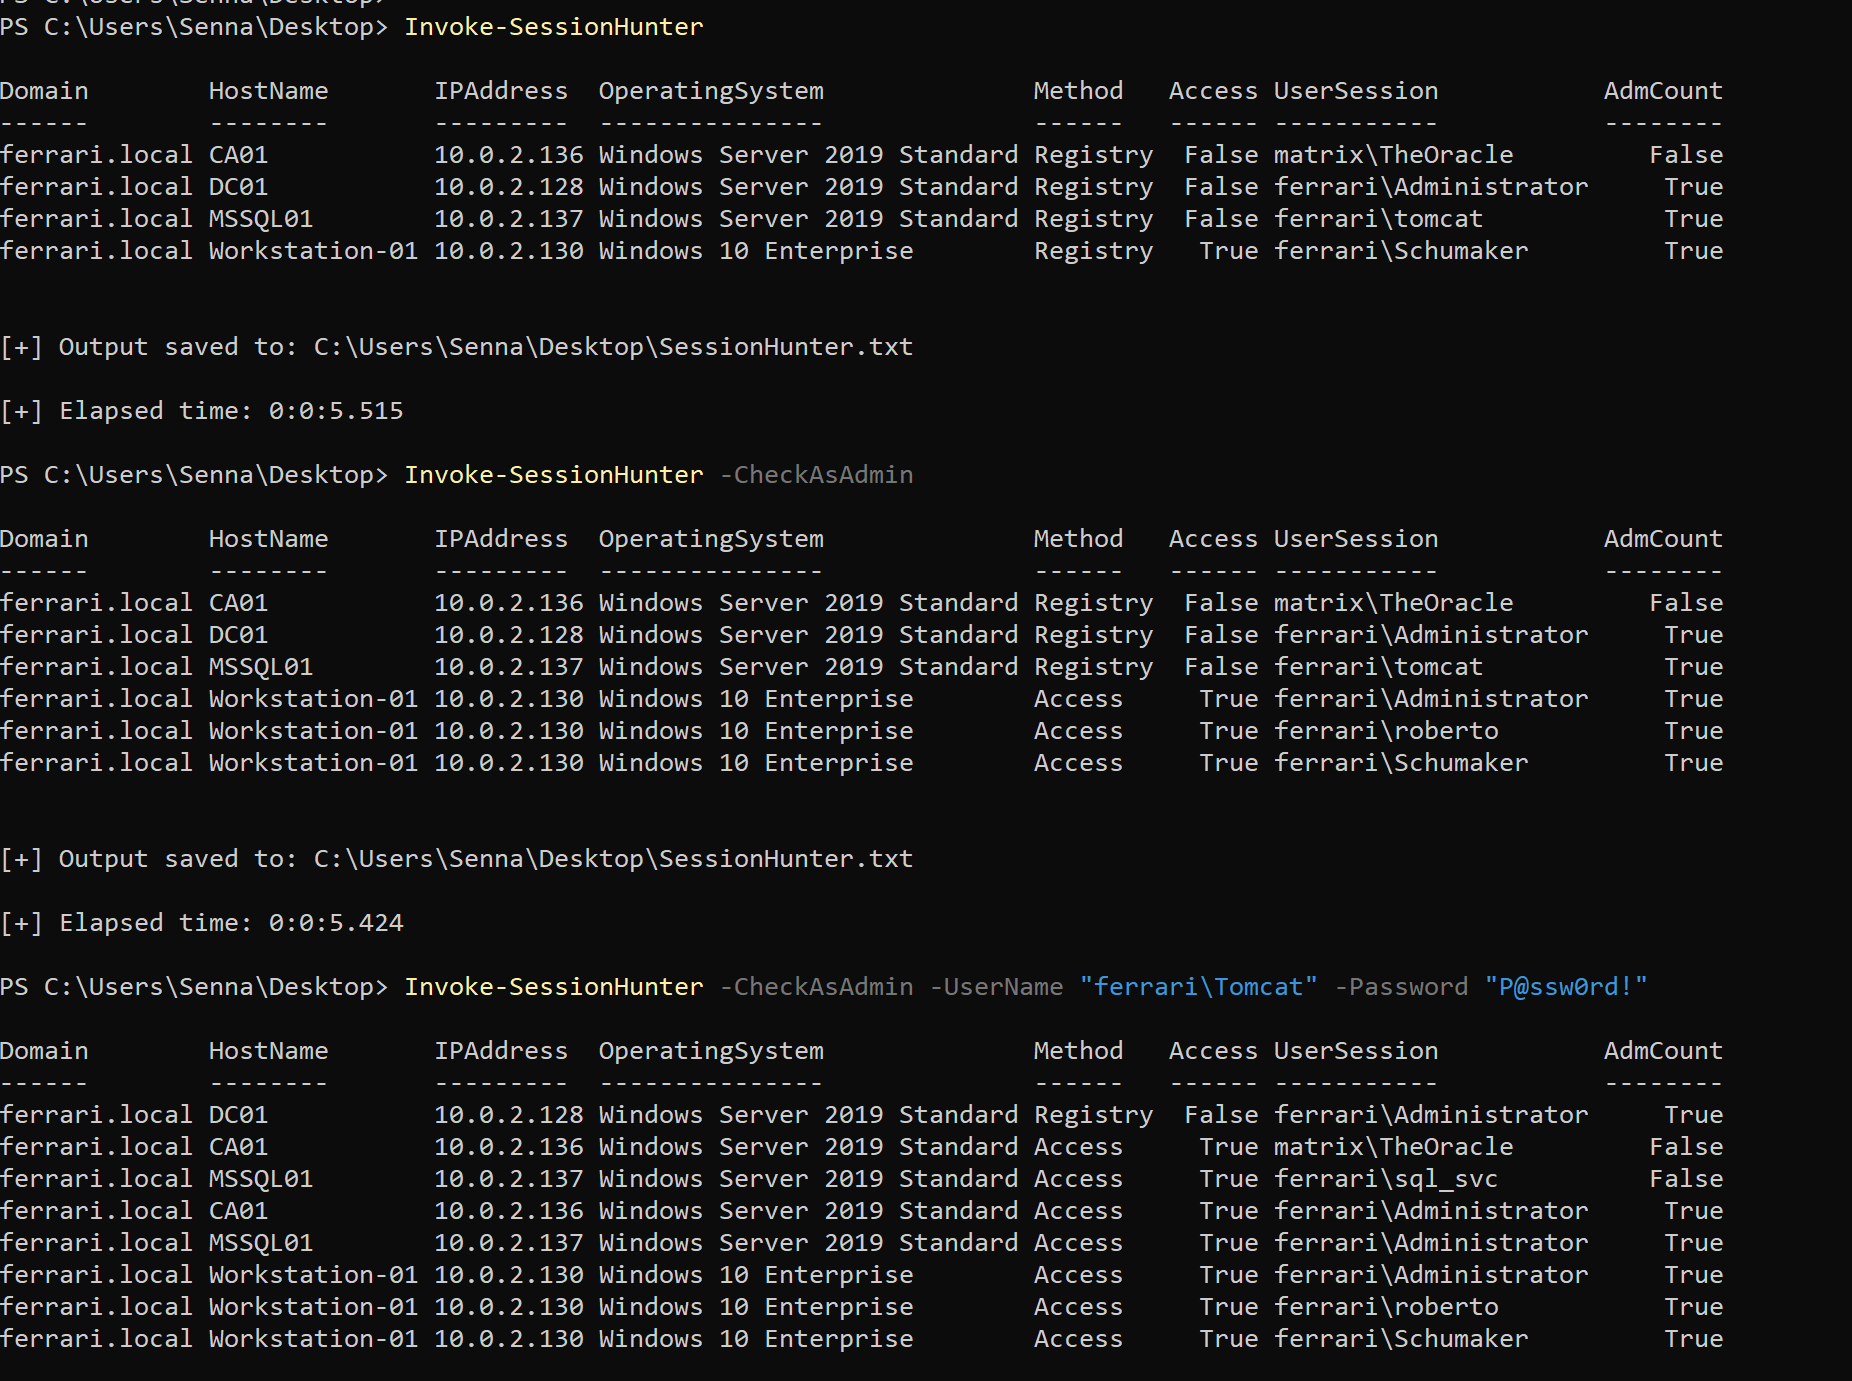 leo4j/invoke-sessionhunter
Retrieve and display information about active user sessions on remote computers. No admin privileges required.
 xaitax/totalrecall
This tool extracts and displays data from the Recall feature in Windows 11, providing an easy way to access information about your PC's activity…
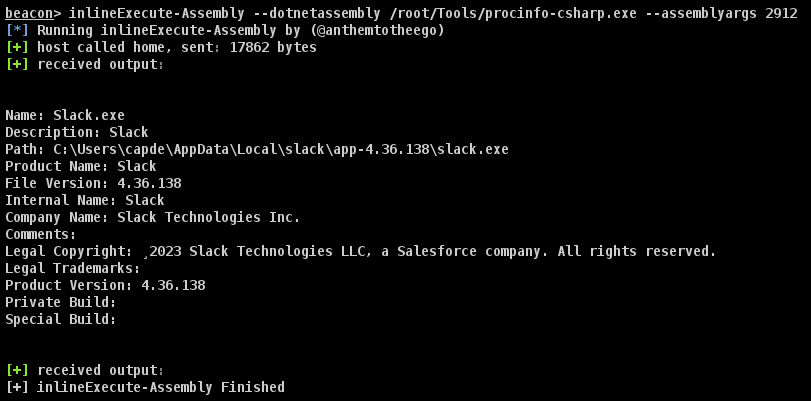 mlcsec/proctools
Small toolkit for extracting information and dumping sensitive strings from Windows processes
 stiffies/airscout
A nice tool that automates network hash capturing and has a nice GUI. Read README.md for more information and NEVER use this without explicit…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
 abdelrahman0sayed/cve-2025-24071
This is a python PoC scripts for CVE-2025-24071 which is a vulnerability in Windows File Explorer that allows unauthorized access to sensitive…
 randomrobbiebf/loot-me
Collects files and commands post-exploitation, formats them into Markdown reports, and helps find sensitive information for red team reporting.
 peewpw/invoke-wcmdump
PowerShell Script to Dump Windows Credentials from the Credential Manager
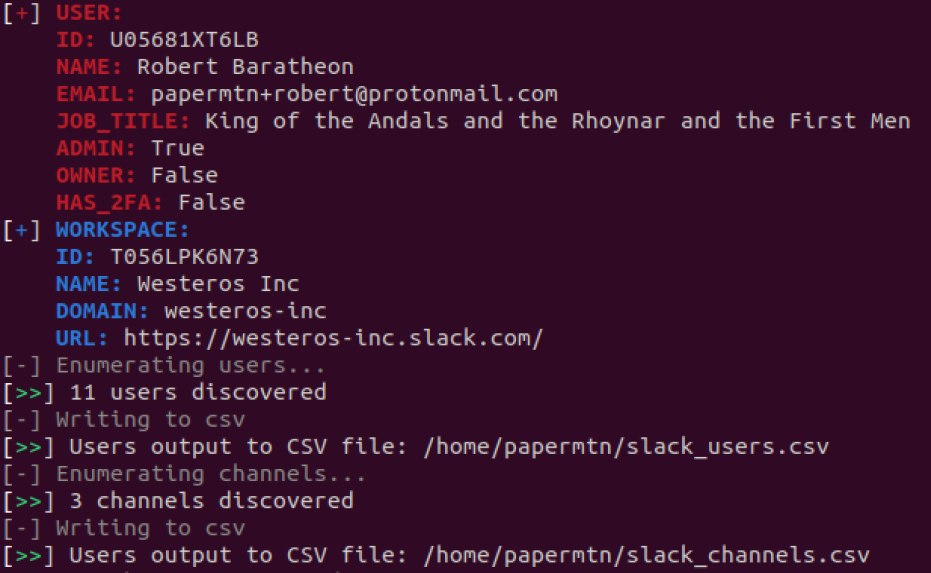 papermtn/slack-watchman
Slack enumeration and exposed secrets detection tool