
moonwalk
 mufeedvh/moonwalk
Cover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
forensicspenetration-testingpost-exploitation+2
1.5k4 years ago
mufeedvh/moonwalkCover your tracks during Linux Exploitation by leaving zero traces on system logs and filesystem timestamps.
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 beefproject/beef
The Browser Exploitation Framework Project
 bittersecurity/decepticon
Autonomous LLM red team agent that plans and executes full attack chains—recon, exploitation, privilege escalation, lateral movement and C2—inside an…
 liamg/traitor
:arrow_up: :skull_and_crossbones: :fire: Automatic Linux privesc via exploitation of low-hanging fruit e.g. gtfobins, pwnkit, dirty pipe, +w…
 secgroundzero/warberry
WarBerryPi - Tactical Exploitation
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 wh0amitz/sharpadws
Active Directory reconnaissance and exploitation for Red Teams via the Active Directory Web Services (ADWS).
 synacktiv/grouppolicybackdoor
Group Policy Objects manipulation and exploitation framework
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 matheuzsecurity/furtex
Post-exploitation and evasion research toolkit for Linux.
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
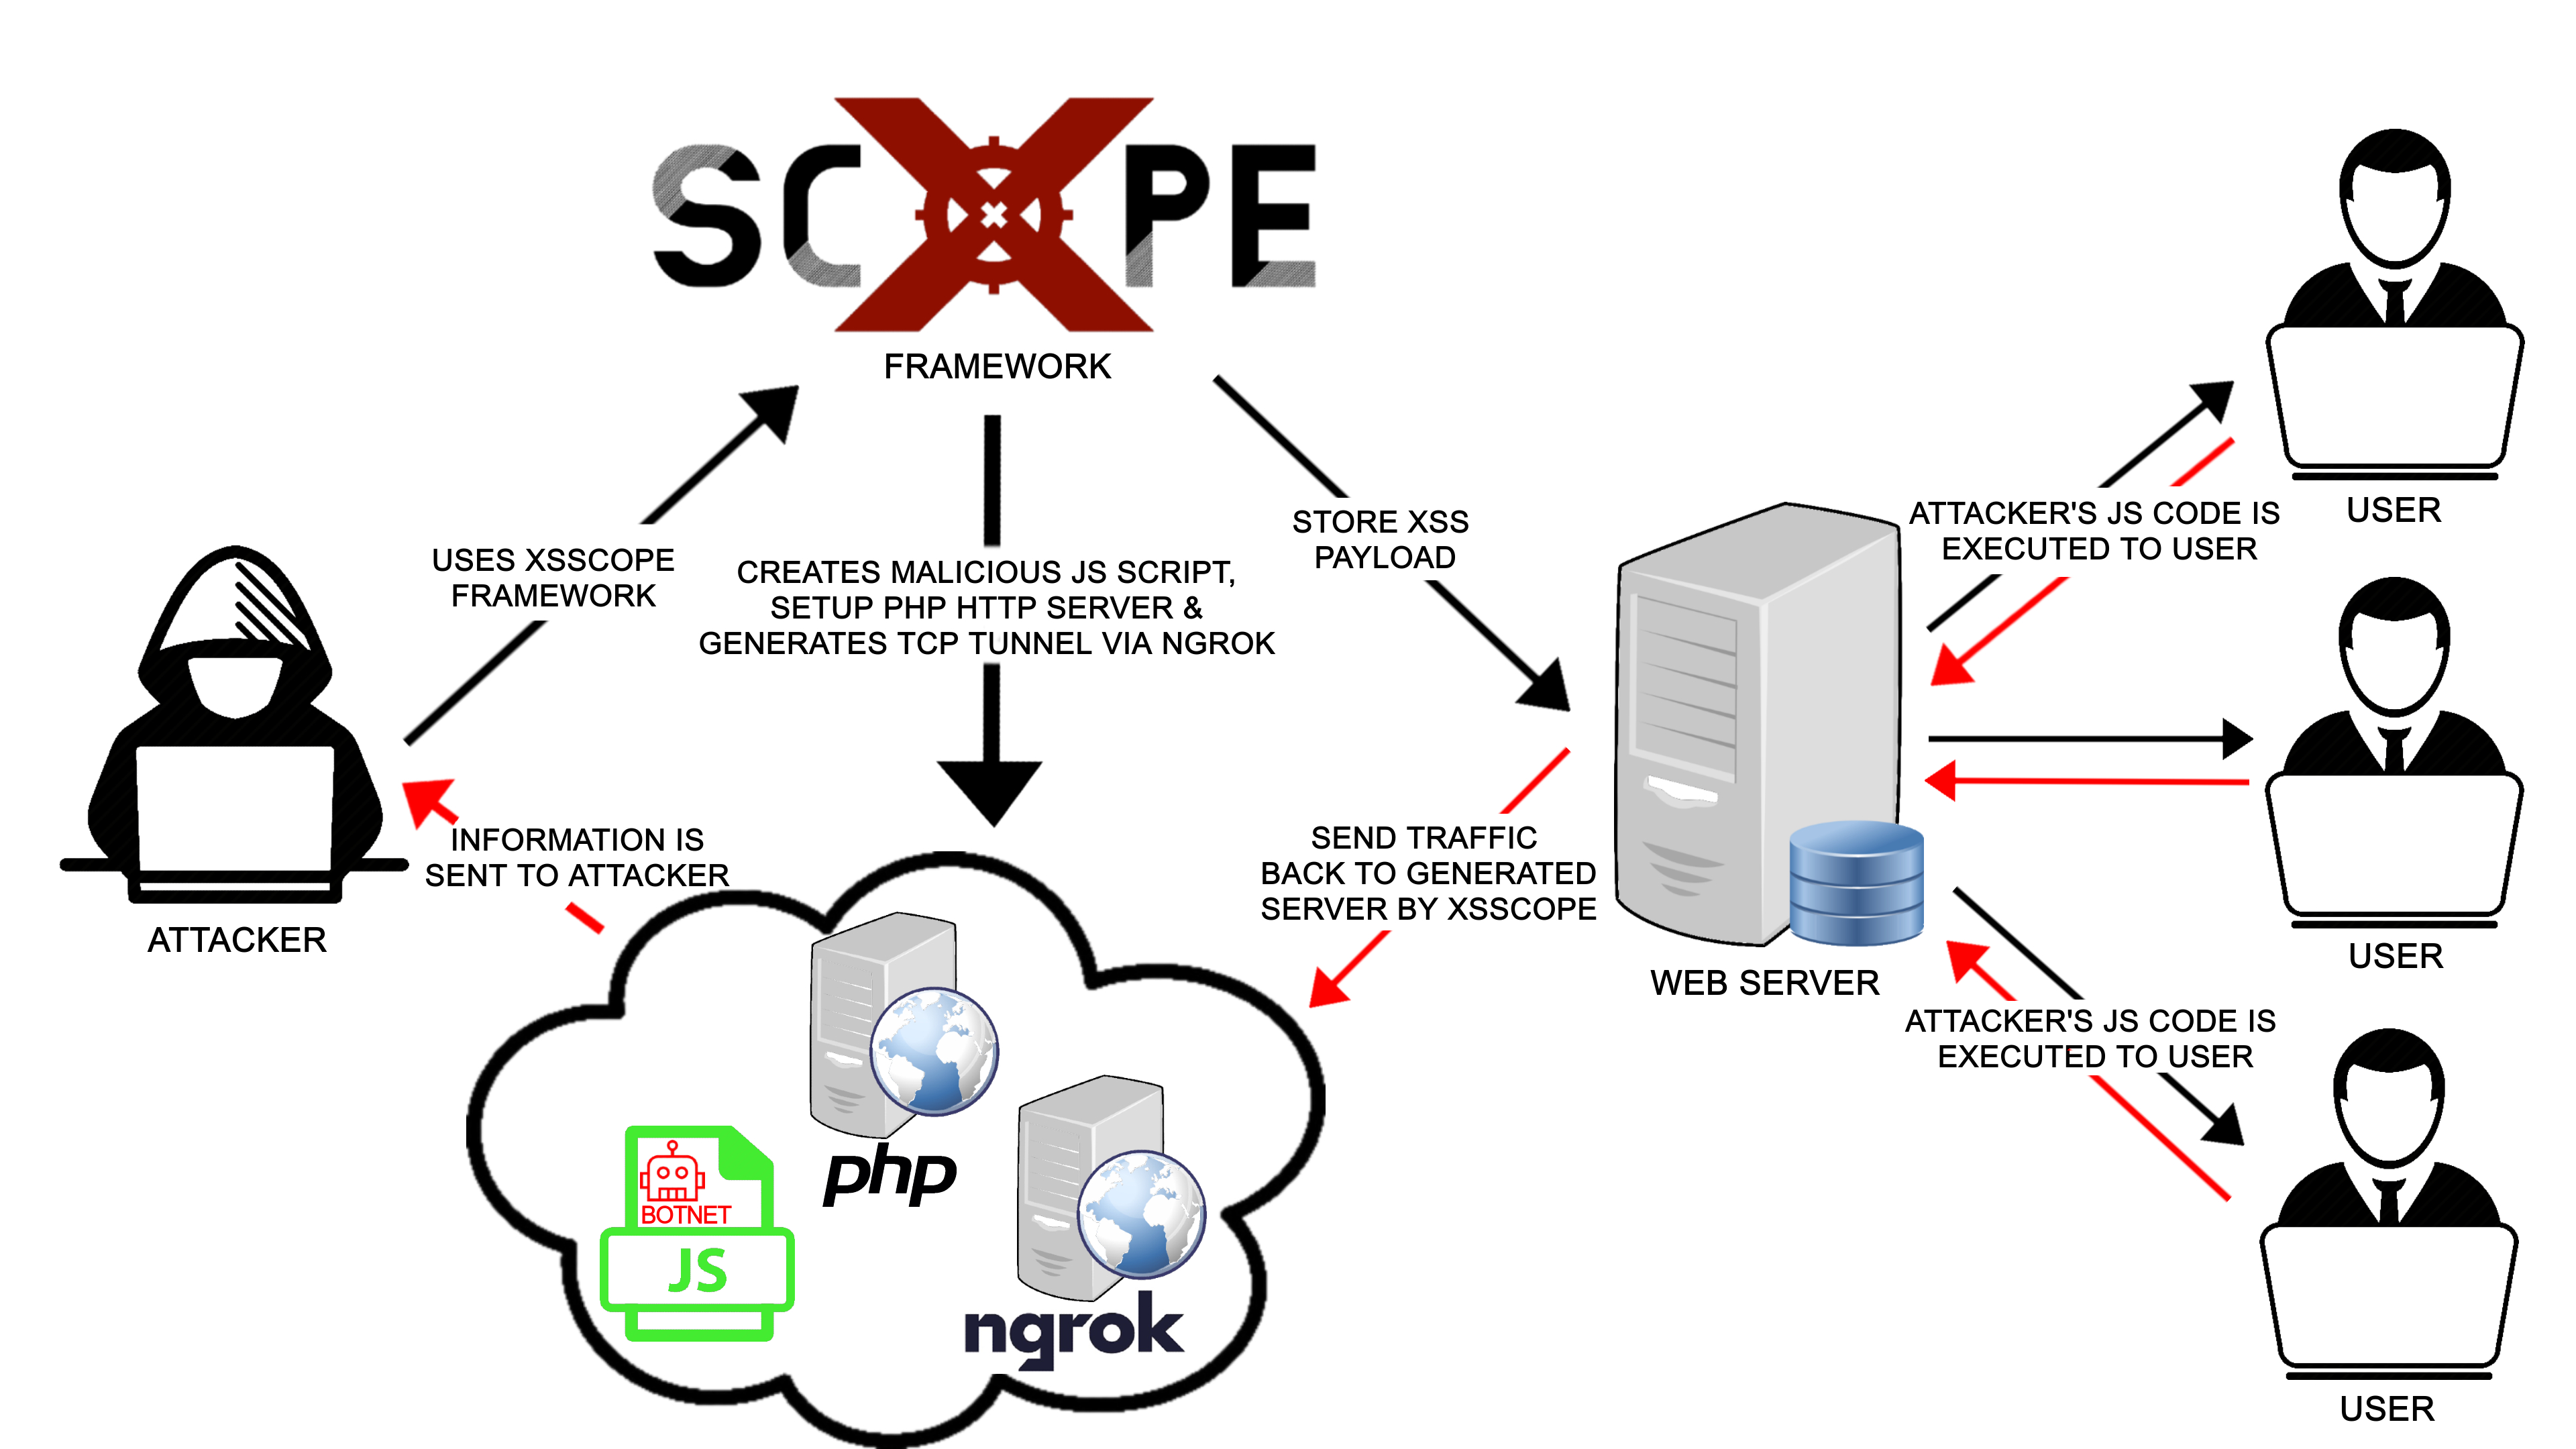 kleiton0x00/xsscope
XSScope is one of the most powerful and advanced GUI Framework for Modern Browser exploitation via XSS.