
CVE-2022-46169
 k4pxd/cve-2022-46169
Cacti 1.2.22 unauthenticated command injection
educationexploitationpenetration-testing+3
k4pxd/cve-2022-46169Cacti 1.2.22 unauthenticated command injection
 bgarz929/ashwesker-cve-2026-21858
Exploit for CVE-2026-21858, a critical unauthenticated content-type parsing flaw in n8n allowing arbitrary file read, credential theft, and remote…
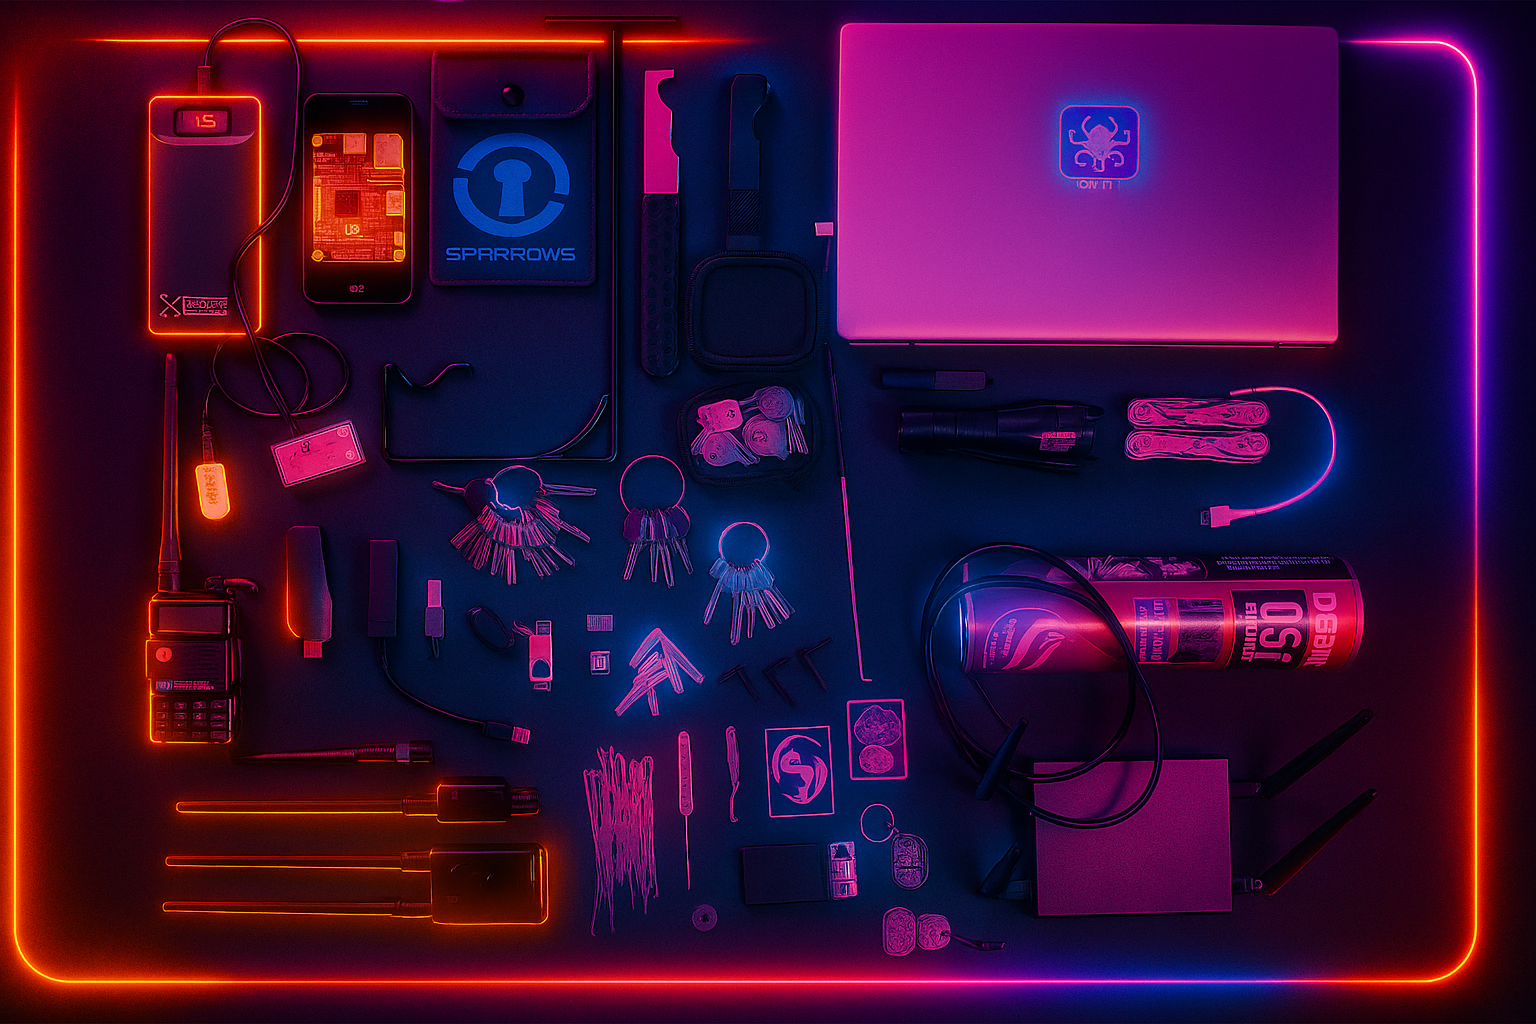 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
 mdsecactivebreach/farmer
Harvests NetNTLM hashes in Windows domains via a local WebDAV server, with LNK file poisoning and Office document field code injection for lateral…
 d3vn0mi/cve-2026-23744-poc
Python PoC for CVE-2026-23744, unauthenticated RCE in MCP servers via the /api/mcp/connect serverConfig command field (default port 6274)
 exploitwritter/cve-2022-25063
This script exploits a vulnerability (XSS) in the TPLink WR840N router, using a field for injecting javascript code.
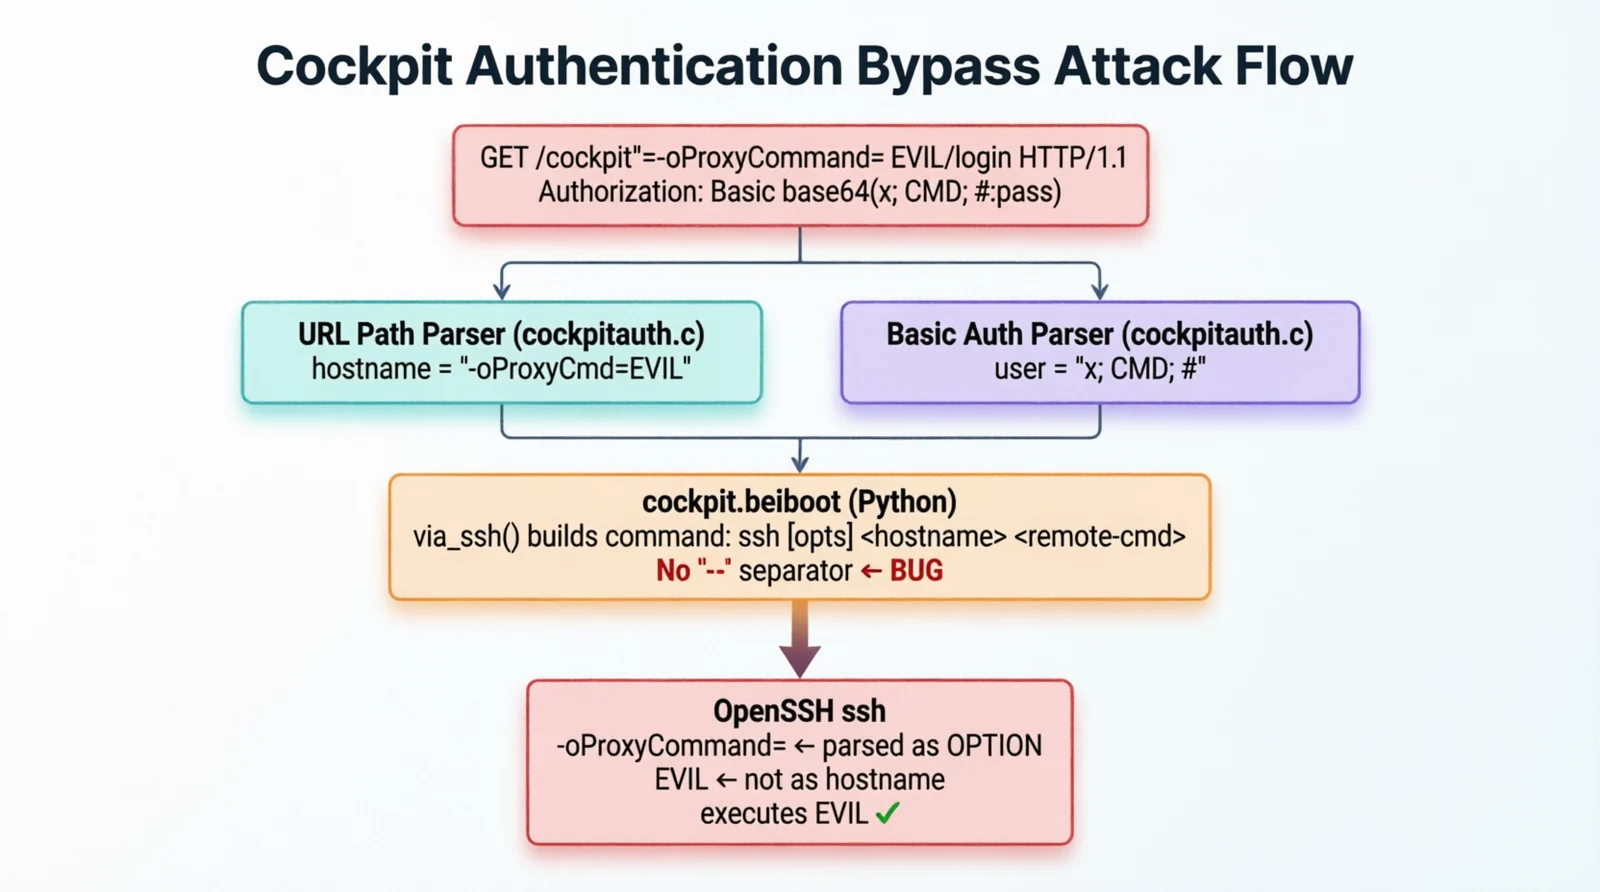 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
 shinthink/cve-2026-65883
Aimy Captcha-Less Form Guard Joomla Component PHP Object Injection RCE. clfgd XOR keystream recovery + unserialize(). CVSS 10.0 | CWE-502 |…
 jhurtadomi/cve-2024-36991-splunk
Path traversal exploit for Splunk Enterprise on Windows (CVE-2024-36991) — interactive file harvester
 shiva108/ai-llm-red-team-handbook
AI / LLM Red Team Field Manual & Consultant’s Handbook
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 cobalt-strike/beacon_health_check
This aggressor script uses a beacon's note field to indicate the health status of a beacon.
 ubaydev/cve-2026-15748
Forminator Forms <= 1.56.1 - Unauthenticated Arbitrary File Upload via Forged Upload Field Configuration
 lil0xplorer/cve-2025-60787_poc
Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…
 hyunchiya/cve-2025-14736
Unauthenticated Privilege Escalation to Administrator via Role Form Field
 eerykitty/cve-2020-0796-poc
PoC for triggering buffer overflow via CVE-2020-0796
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3