
threadfire
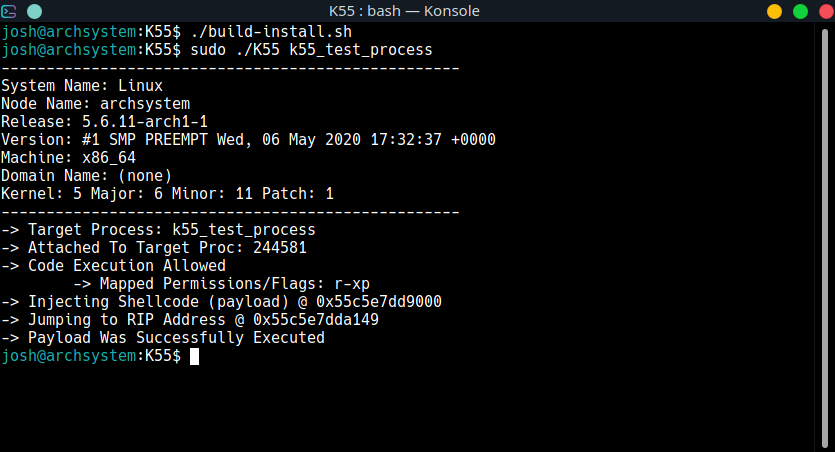
 josh0xa/threadfire
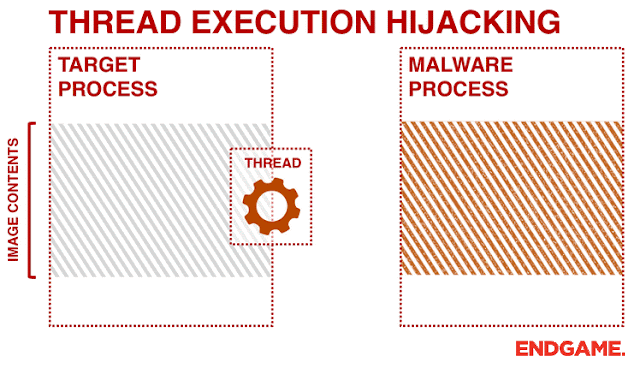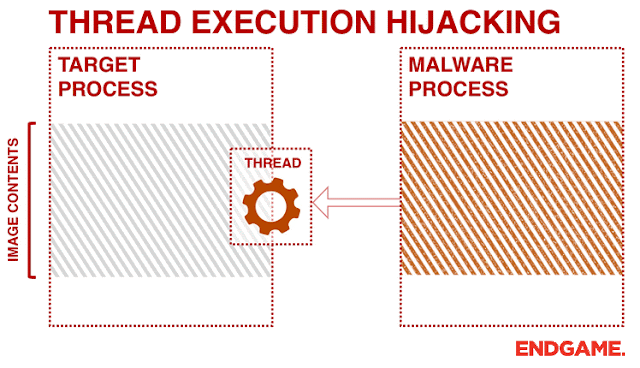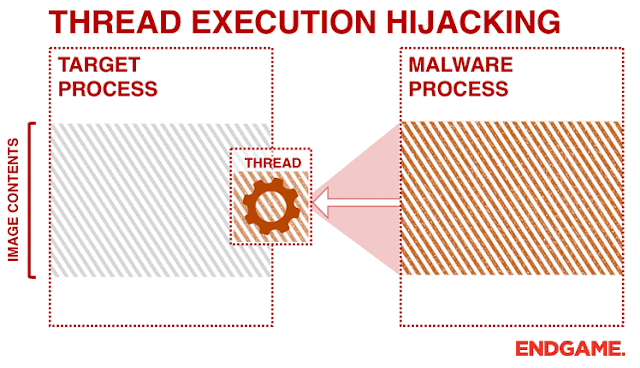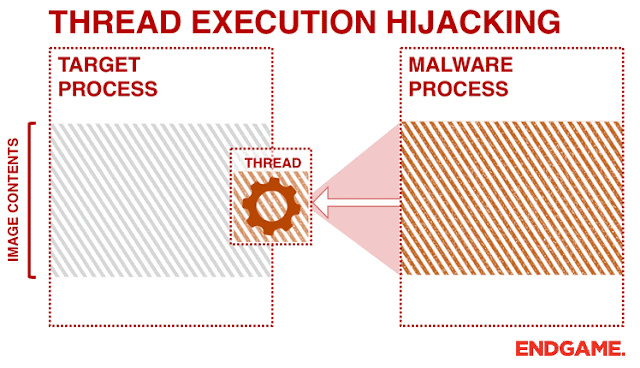
PoC Thread Execution Hijacking for Win32 Code Injection
payload-developmentpenetration-testingred-teaming+1
josh0xa/threadfirePoC Thread Execution Hijacking for Win32 Code Injection
 sh4den/cve-2022-31814
Proof of concept for CVE-2022-31814
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 davidbuchanan314/dlinject
Inject a shared library (i.e. arbitrary code) into a live linux process, without ptrace
 dec0ne/dllnotificationinjection
A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
 boogipop/cve-2023-22527-godzilla-memshell
CVE-2023-22527 内存马注入工具