
SneakyEXE
 hackernese/sneakyexe
Automatic UAC-Bypassing for custom payloads during privilege escalation testing
exploitationpayload-developmentprivilege-escalation+1
974 years ago
hackernese/sneakyexeAutomatic UAC-Bypassing for custom payloads during privilege escalation testing
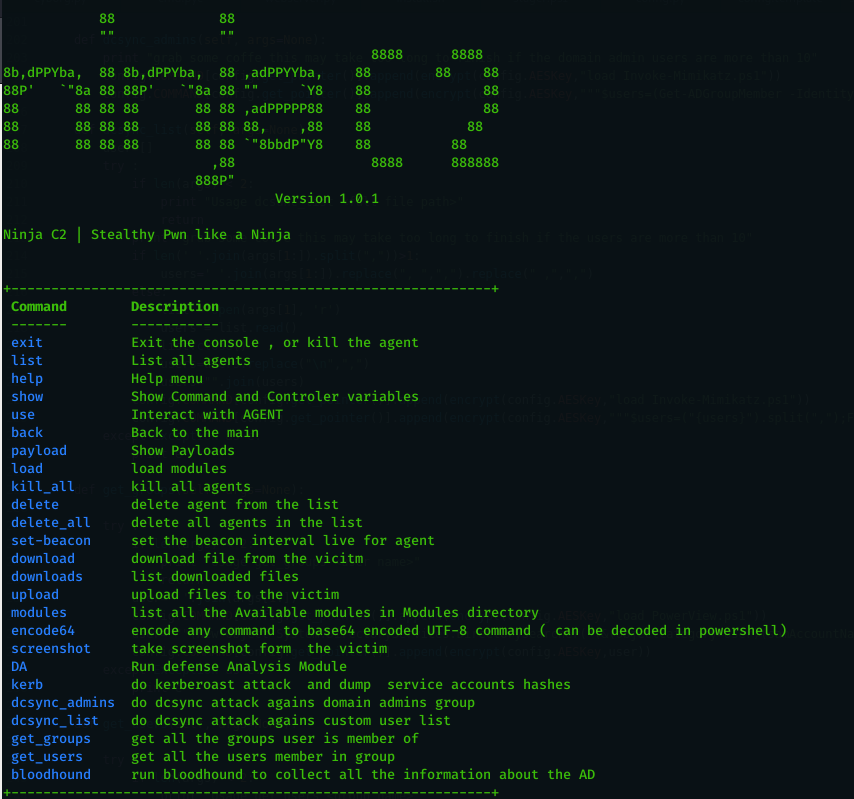 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
 mhaskar/octopus
Open source pre-operation C2 server based on python and powershell
 thestingr/cve-2025-68613-poc
Public PoC + Scanner and research for CVE-2025-68613: Critical RCE in n8n Workflow Automation via Expression Injection (CVSS 10.0). Includes…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 r41n3rzuf477/ps-ppl-bypass
Process Explorer vulnerable driver PPL Bypass
 ch4120n/cve-2026-55579
CVE-2026-55579 – Unauthenticated RCE in Pheditor via hardcoded default password "admin". Full Python exploit with file upload & terminal execution.…
 safelineman/agentic-soc-simulation
AI 驱动的 SOC 仿真平台
 samyk/skyjack
A drone engineered to autonomously seek out, hack, and wirelessly take full control over any other Parrot or 3DR drones within wireless or flying…
 chvancooten/follina.py
POC to replicate the full 'Follina' Office RCE vulnerability for testing purposes
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 v4bel/januscape
KVM/x86 guest-to-host escape exploit (CVE-2026-53359) leveraging a use-after-free in shadow MMU emulation. Includes PoC for triggering host kernel…
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
 nccgroup/nccfsas
Information released publicly by NCC Group's Full Spectrum Attack Simulation (FSAS) team.
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 yardenshafir/ioringreadwriteprimitive
Post exploitation technique to turn arbitrary kernel write / increment into full read/write primitive on Windows 11 22H2
 forefy/reburp
A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
 csenox/semanagevolumeexploit
Windows local privilege escalation exploit abusing SeManageVolumePrivilege to grant full C:\ drive access and gain a SYSTEM shell via PrintConfig.dll…