

Burp2Malleable
 codextf2/burp2malleable
Quick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
command-and-controlids-ips-evasionpayload-development+2
418
codextf2/burp2malleableQuick python utility I wrote to turn HTTP requests from burp suite into Cobalt Strike Malleable C2 profiles
 blackhillsinfosec/skyhook
A round-trip obfuscated HTTP file transfer setup built to bypass IDS detections.
 lsecqt/portforwarder
TCP Port Forwarding Utility on C
 kkevsterrr/backdoorme
powerful auto-backdooring utility
 alphasoc/flightsim
A utility to safely generate malicious network traffic patterns and evaluate controls.
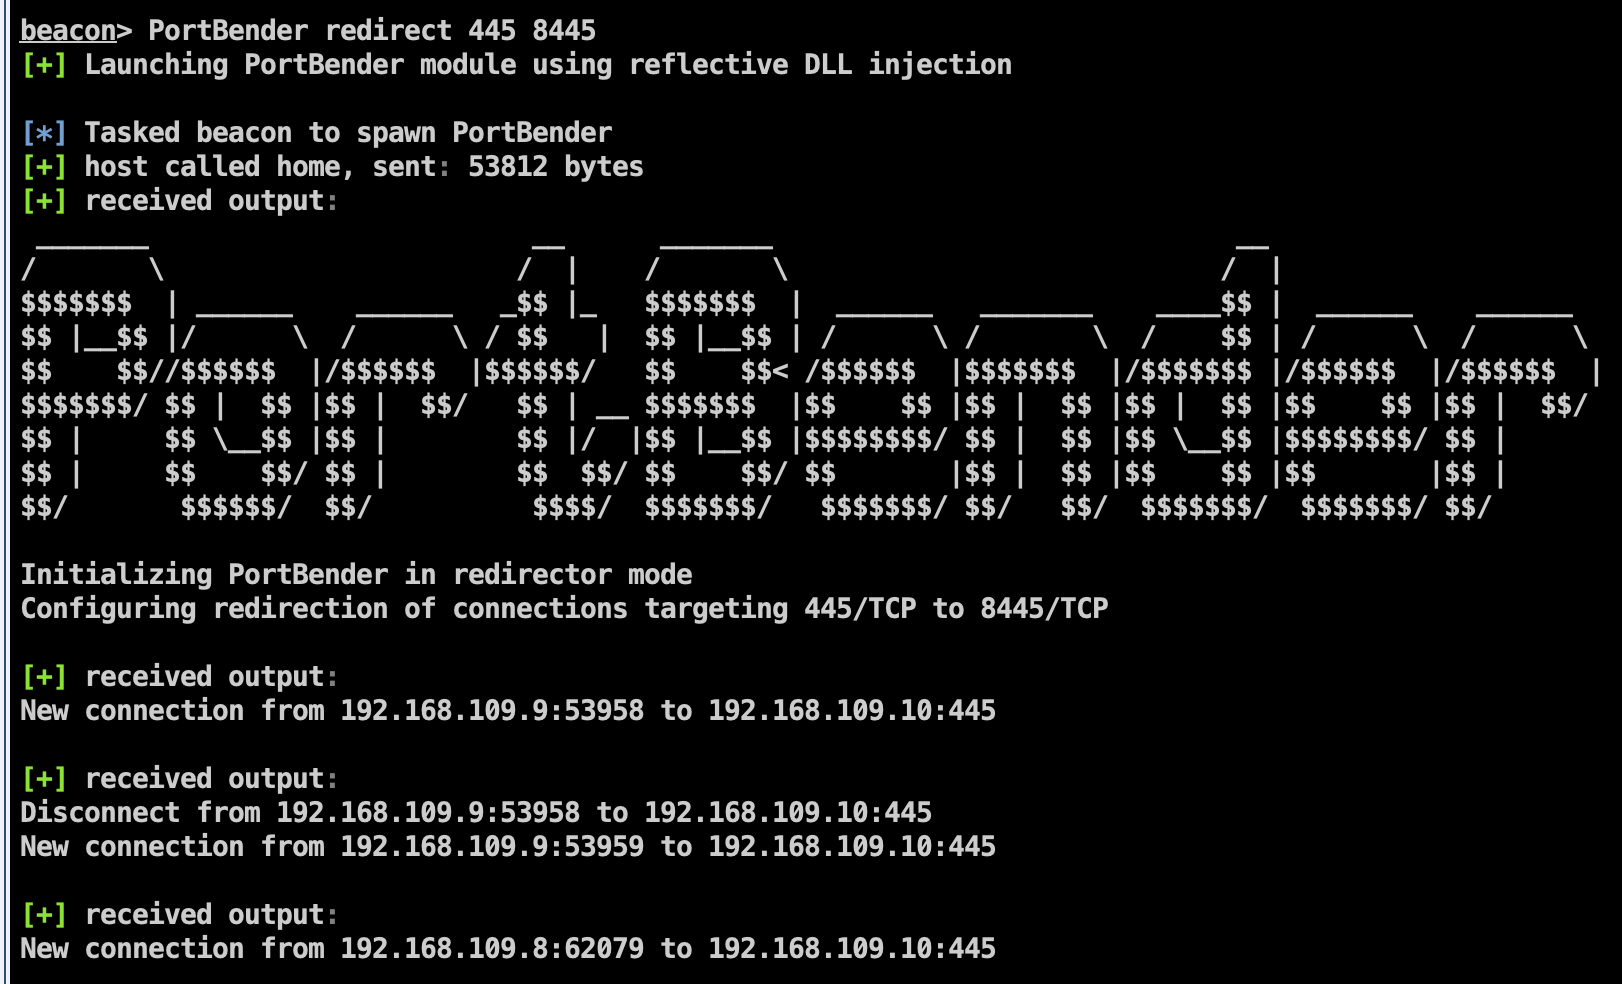 praetorian-inc/portbender
TCP Port Redirection Utility
 shell-company/qrexfil
This tool is a command line utility that allows you to convert any binary file into a QRcode movie. The data can then be reassembled visually…
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
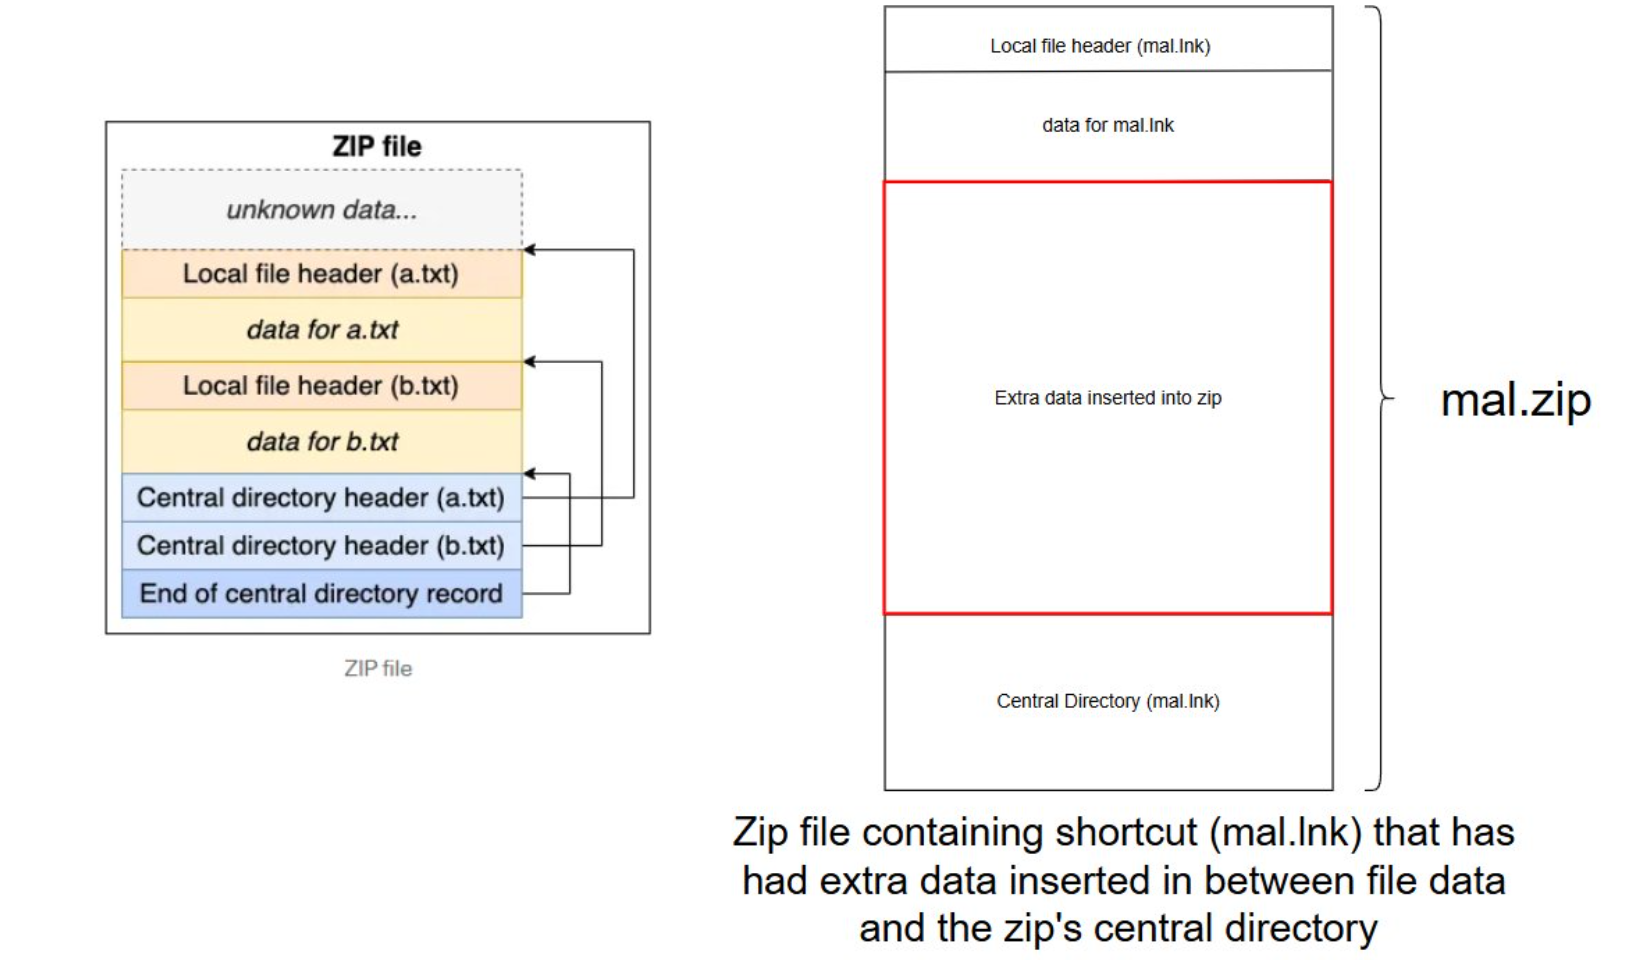 octoberfest7/zip_smuggling
Python3 utility for creating zip files that smuggle additional data for later extraction
 darkspacesecurity/runas-stealer
RunAs Utility Credential Stealer implementing 3 techniques : Hooking CreateProcessWithLogonW, Smart Keylogging, Remote Debugging
 infosecn1nja/veiltransfer
VeilTransfer is a data exfiltration utility designed to test and enhance the detection capabilities. This tool simulates real-world data exfiltration…
 withsecurelabs/doublepulsar-usermode-injector
A utility to use the usermode shellcode from the DOUBLEPULSAR payload to reflectively load an arbitrary DLL into another process, for use in testing…
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
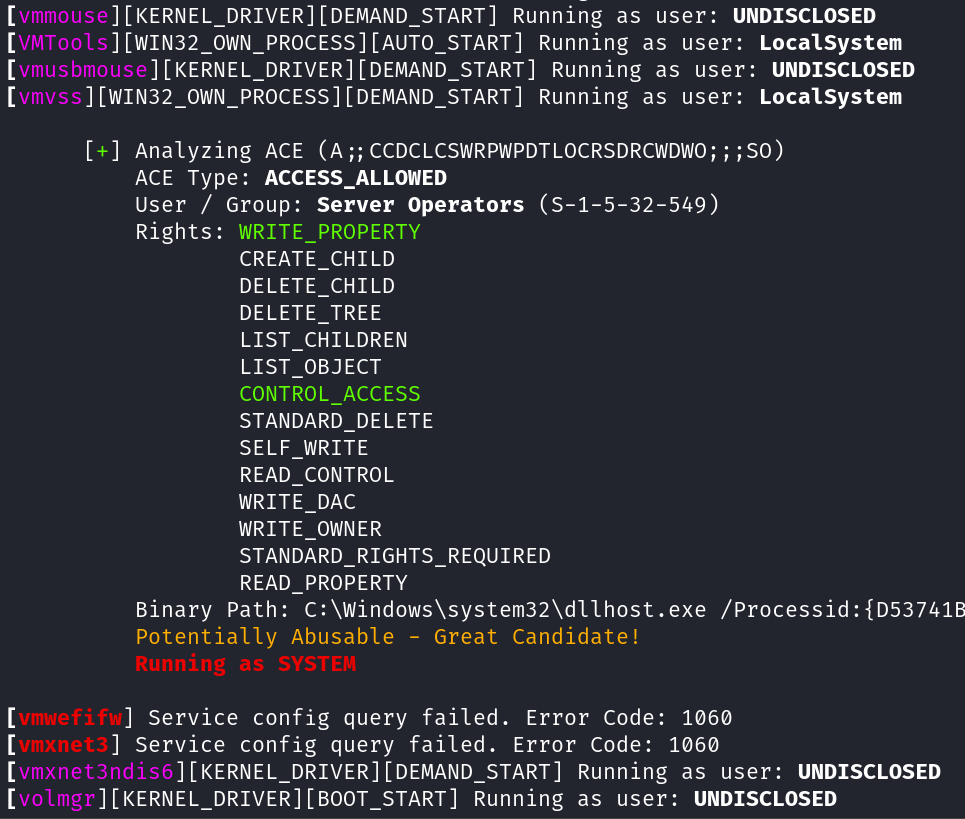 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 tasooshi/exfilkit
Data exfiltration utility for testing detection capabilities
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
 nccgroup/ncloader
A session-0 capable dll injection utility
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…