
PyRIT
 microsoft/pyrit
Open-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
adversarial-attackai-securitymachine-learning+2
4.7k
microsoft/pyritOpen-source framework for red-teaming generative AI systems: automate attack prompts, score model responses, and audit behavior to identify security…
 iknowjason/purplecloud
A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
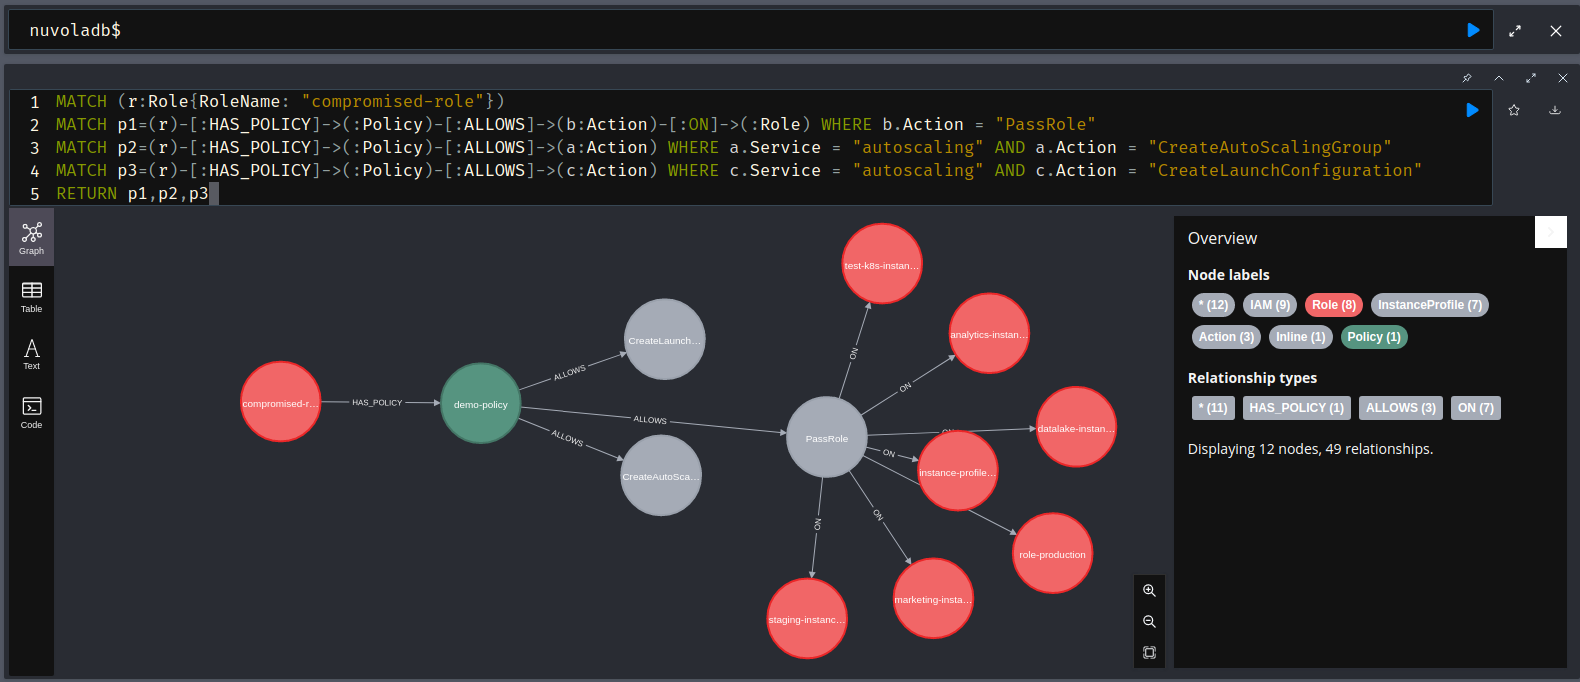 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication
 synacktiv/gpoparser
gpoParser is a tool designed to extract and analyze configurations applied through Group Policy Objects (GPOs) in an Active Directory environment.
 artemcyberlab/project-exploiting-a-vulnerability-in-fuel-cms-cve-2018-16763-
The goal of this project was to conduct a security audit of a blog recently launched by Ackme Support Incorporated, identifying any critical…
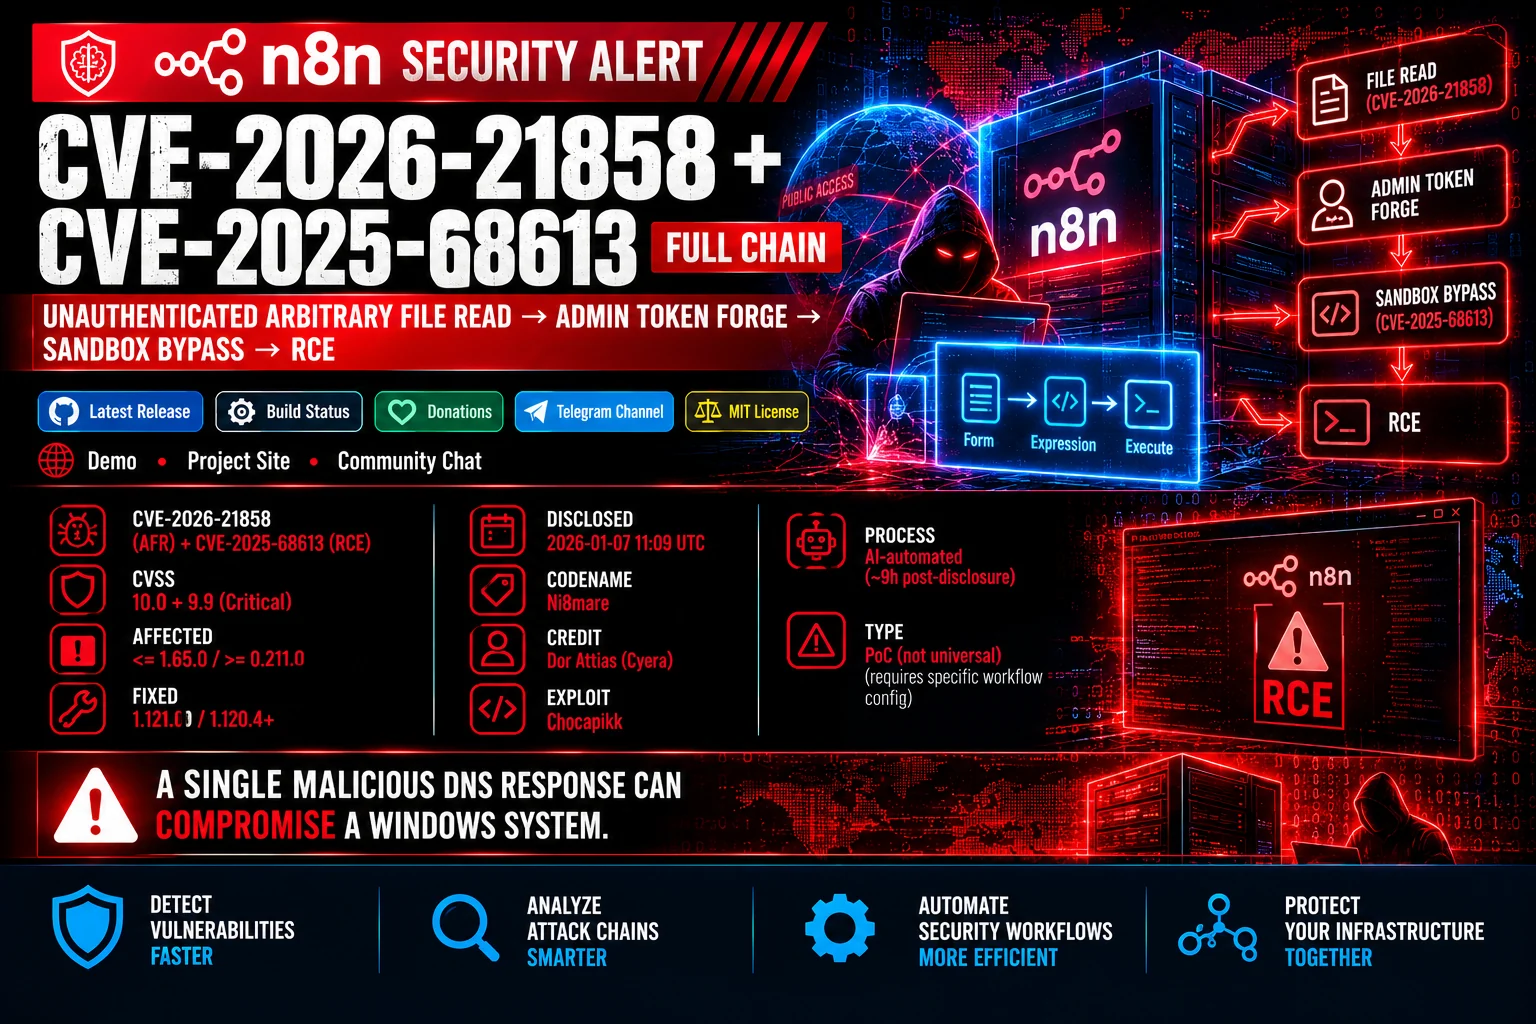 zerodayevil/cve-2026-21858-n8n-fullchain
🛡️ Official AI Security Tool module for CVE-2026-21858 + CVE-2025-68613 (n8n "Ni8mare" Unauthenticated Arbitrary File Read & Expression Injection…
 dylandavis1/dscourier
Proof-of-concept tool leveraging WinGet Configuration COM API to apply DSC configurations through Microsoft-signed binaries, enabling EDR bypass for…
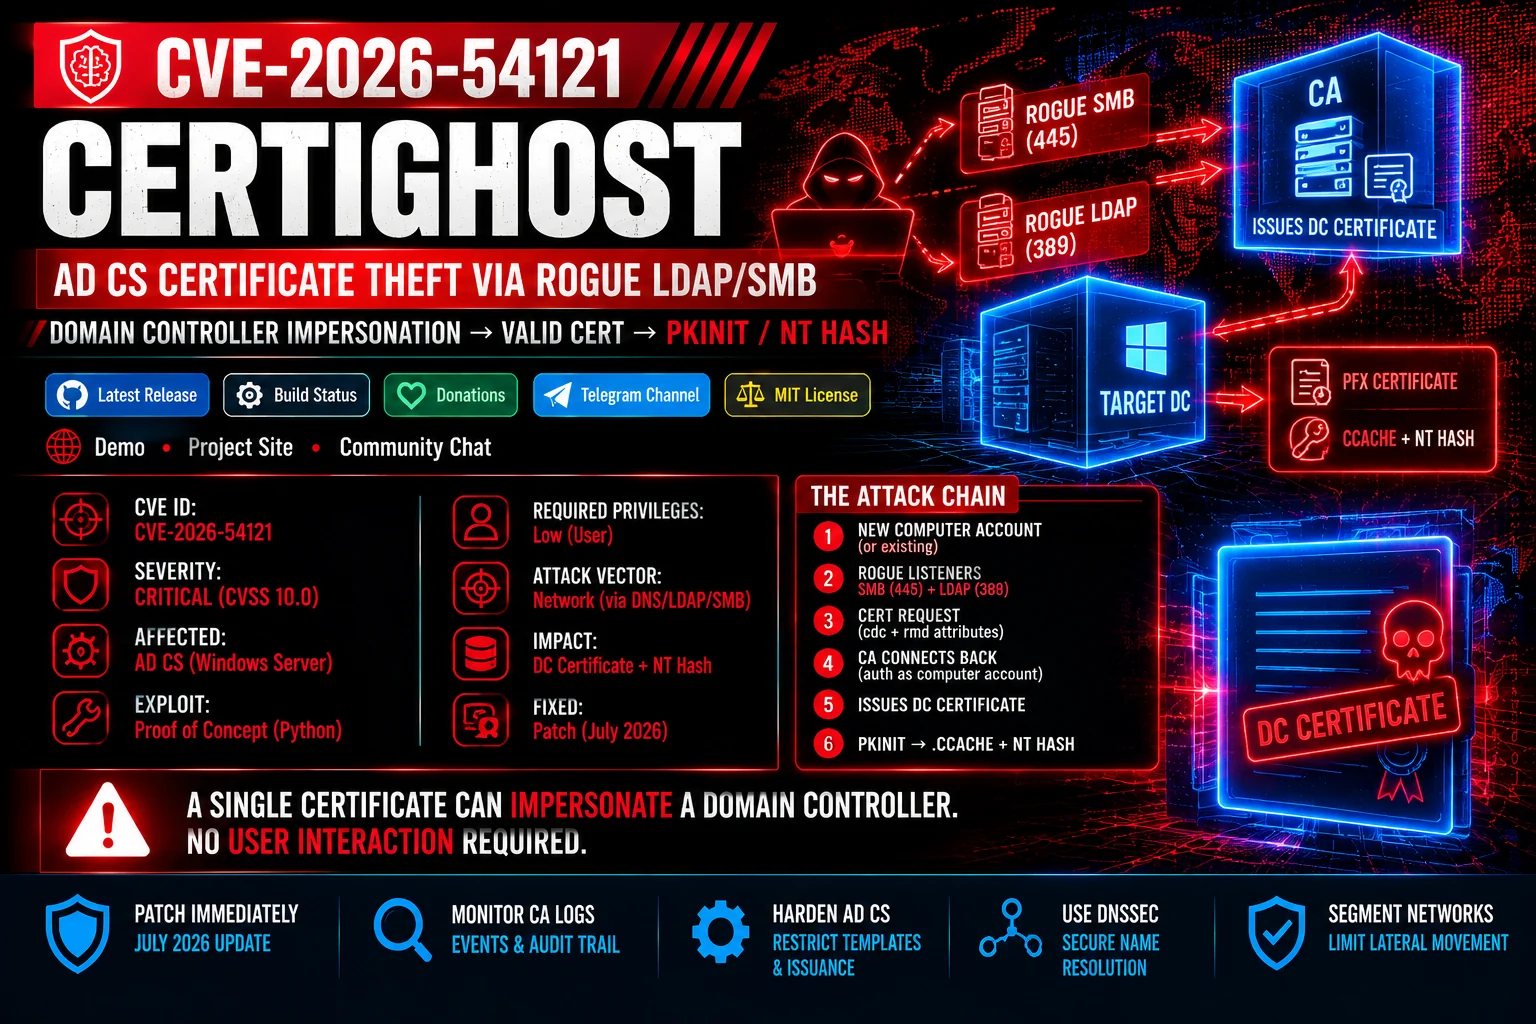 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data